
hdmi-sniff
 adamlaurie/hdmi-sniff
sniff HDMI DDC (I2C) traffic
cryptographyembedded-systems-securityhardware-hacking+4
adamlaurie/hdmi-sniffsniff HDMI DDC (I2C) traffic
 marcnewlin/presentation-clickers
Keystroke injection vulnerabilities in wireless presentation clickers
 ffri/shadebios
PoC code of Shade BIOS (stripped) presented at Black Hat USA 2025
 nccgroup/proxmark3-amiimicyou
Proxmark3 Amiibo simulator as shown at Recon Montreal 2018
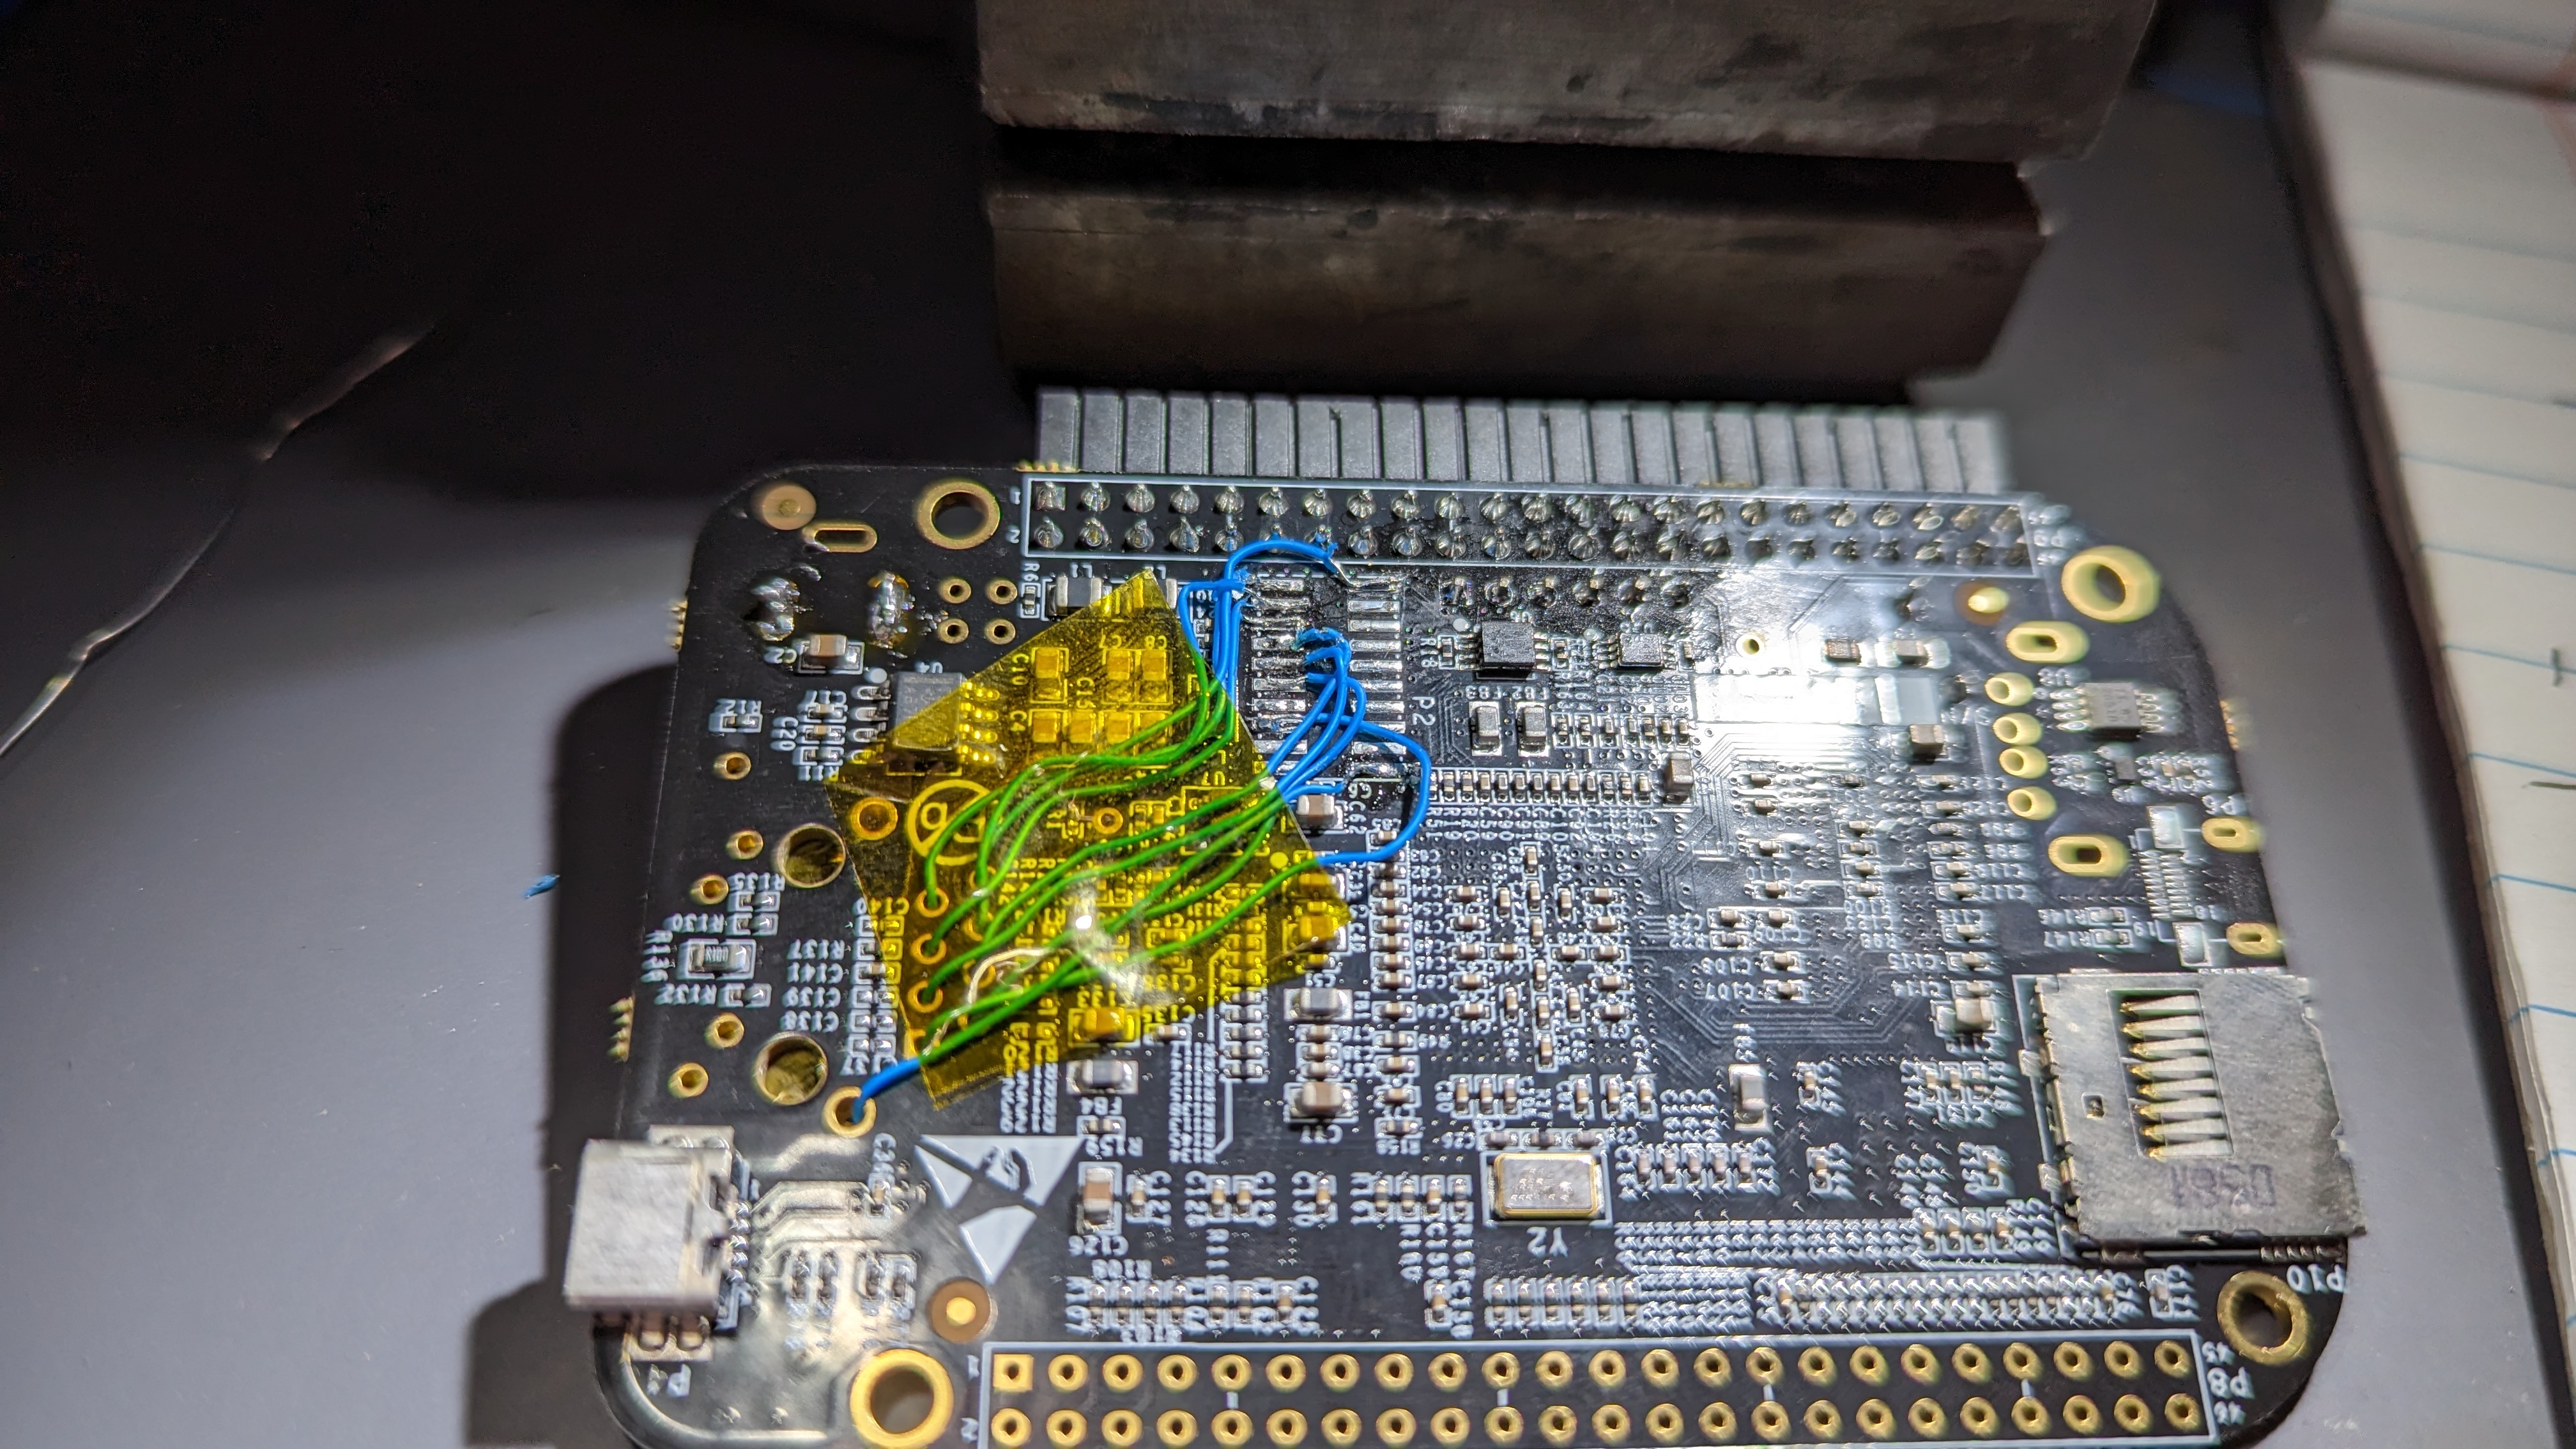 sjgallagher2/am335xbootrom
Reverse engineering the TI AM3358 boot ROM
 mikem64/exploit-writeups
Exploit writeups I've authored
 badmonkey7/cve-2021-34730
Cisco RV110w UPnP stack overflow
 saimanish1/logitech-ipc-protocol
Reverse-engineered Logi Options+ agent IPC protocol. Switch Logitech multi-host devices programmatically via Unix socket (macOS) or named pipe…
 c0mposer/c-game-modding-utility
A game modding utility that makes injecting C/C++ code easier.
 omgrant/ft9201-libfprint
Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…
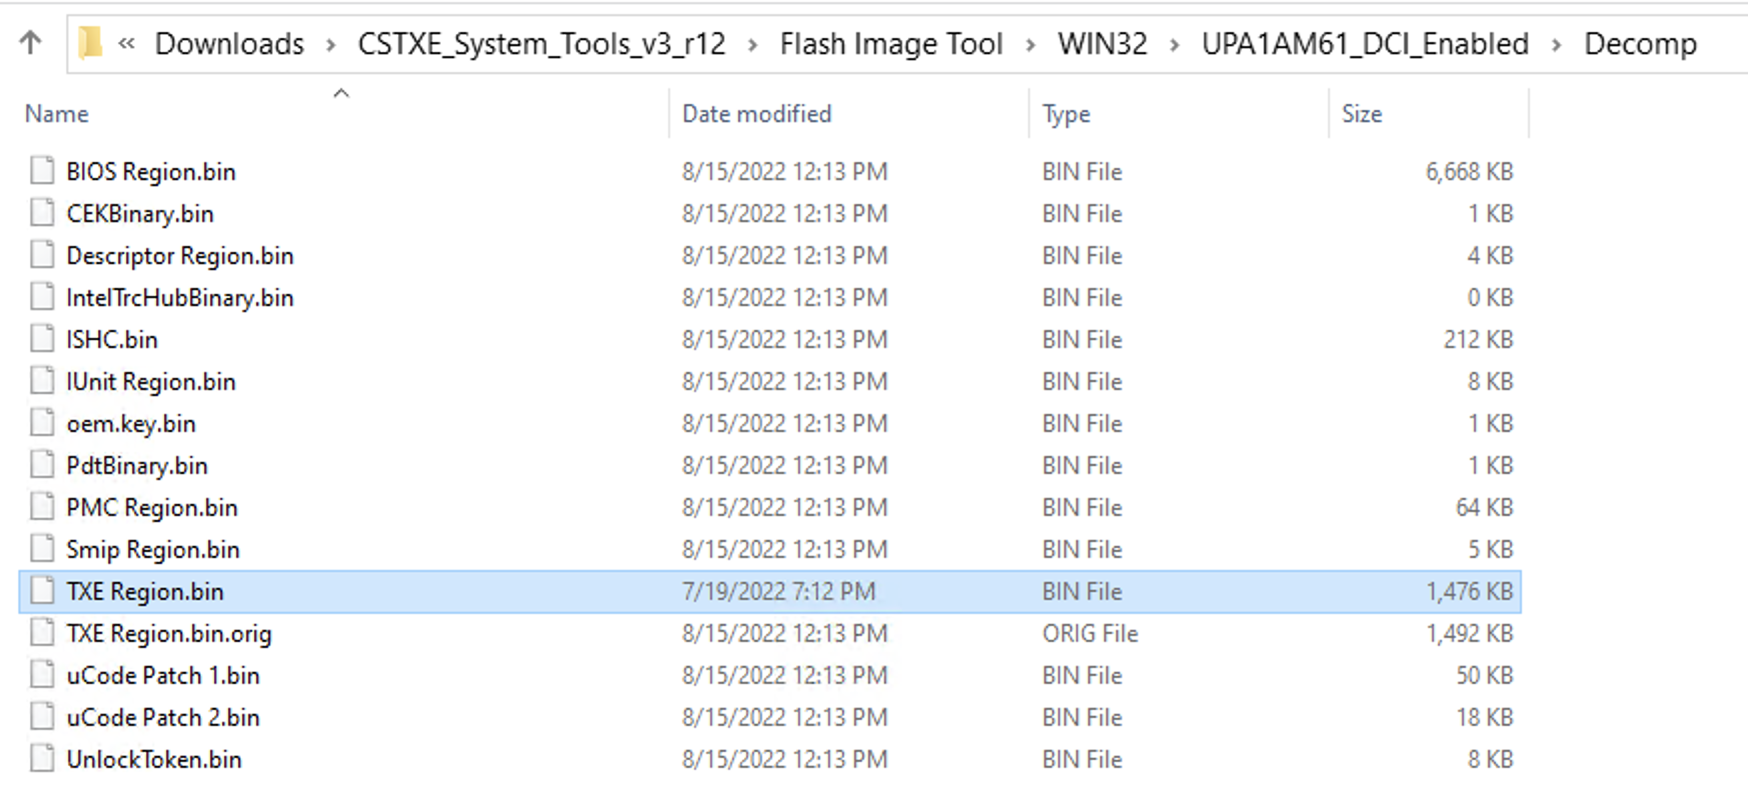 xenokovah/inteltxe-poc
Intel Management Engine JTAG Proof of Concept - 2022 Instructions
 nickdaria/wyze-bulb-color-pwned
No-open firmware exploit for the Wyze WLPA19CV2 color bulb
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
 finngineering/ch55x_firmware_extractor
Firmware extractor for CH55x microprocessors
 gadorach/vankyo-s30-bootloader-unlock
Vankyo MatrixPad S30 (Unisoc SC9863A) — Bootloader unlock via CVE-2022-38694 FDL1 method
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 victorique-123/cve-2023-38829-netis-wf2409e_report
对NETIS WF2409E路由器进行的一次完整硬件安全分析研究。通过对设备进行拆解分析、调试接口识别、固件提取等工作,记录了硬件分析的全过程、漏洞细节以及相应的安全建议,希望能帮助提高物联网设备的安全性。
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device