

doggie
 infobyte/doggie
Welcome to the Doggie and EvilDoggie repository by Faraday Security! Doggie is a modular DIY CAN Bus to serial adapter (USB, BLE, UART) using the…
embedded-systems-securityexploitationhardware-hacking+2
81
infobyte/doggieWelcome to the Doggie and EvilDoggie repository by Faraday Security! Doggie is a modular DIY CAN Bus to serial adapter (USB, BLE, UART) using the…
 iotsrg/iot-pentest-devices-and-purpose
Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…
 blasty/sonos
Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…
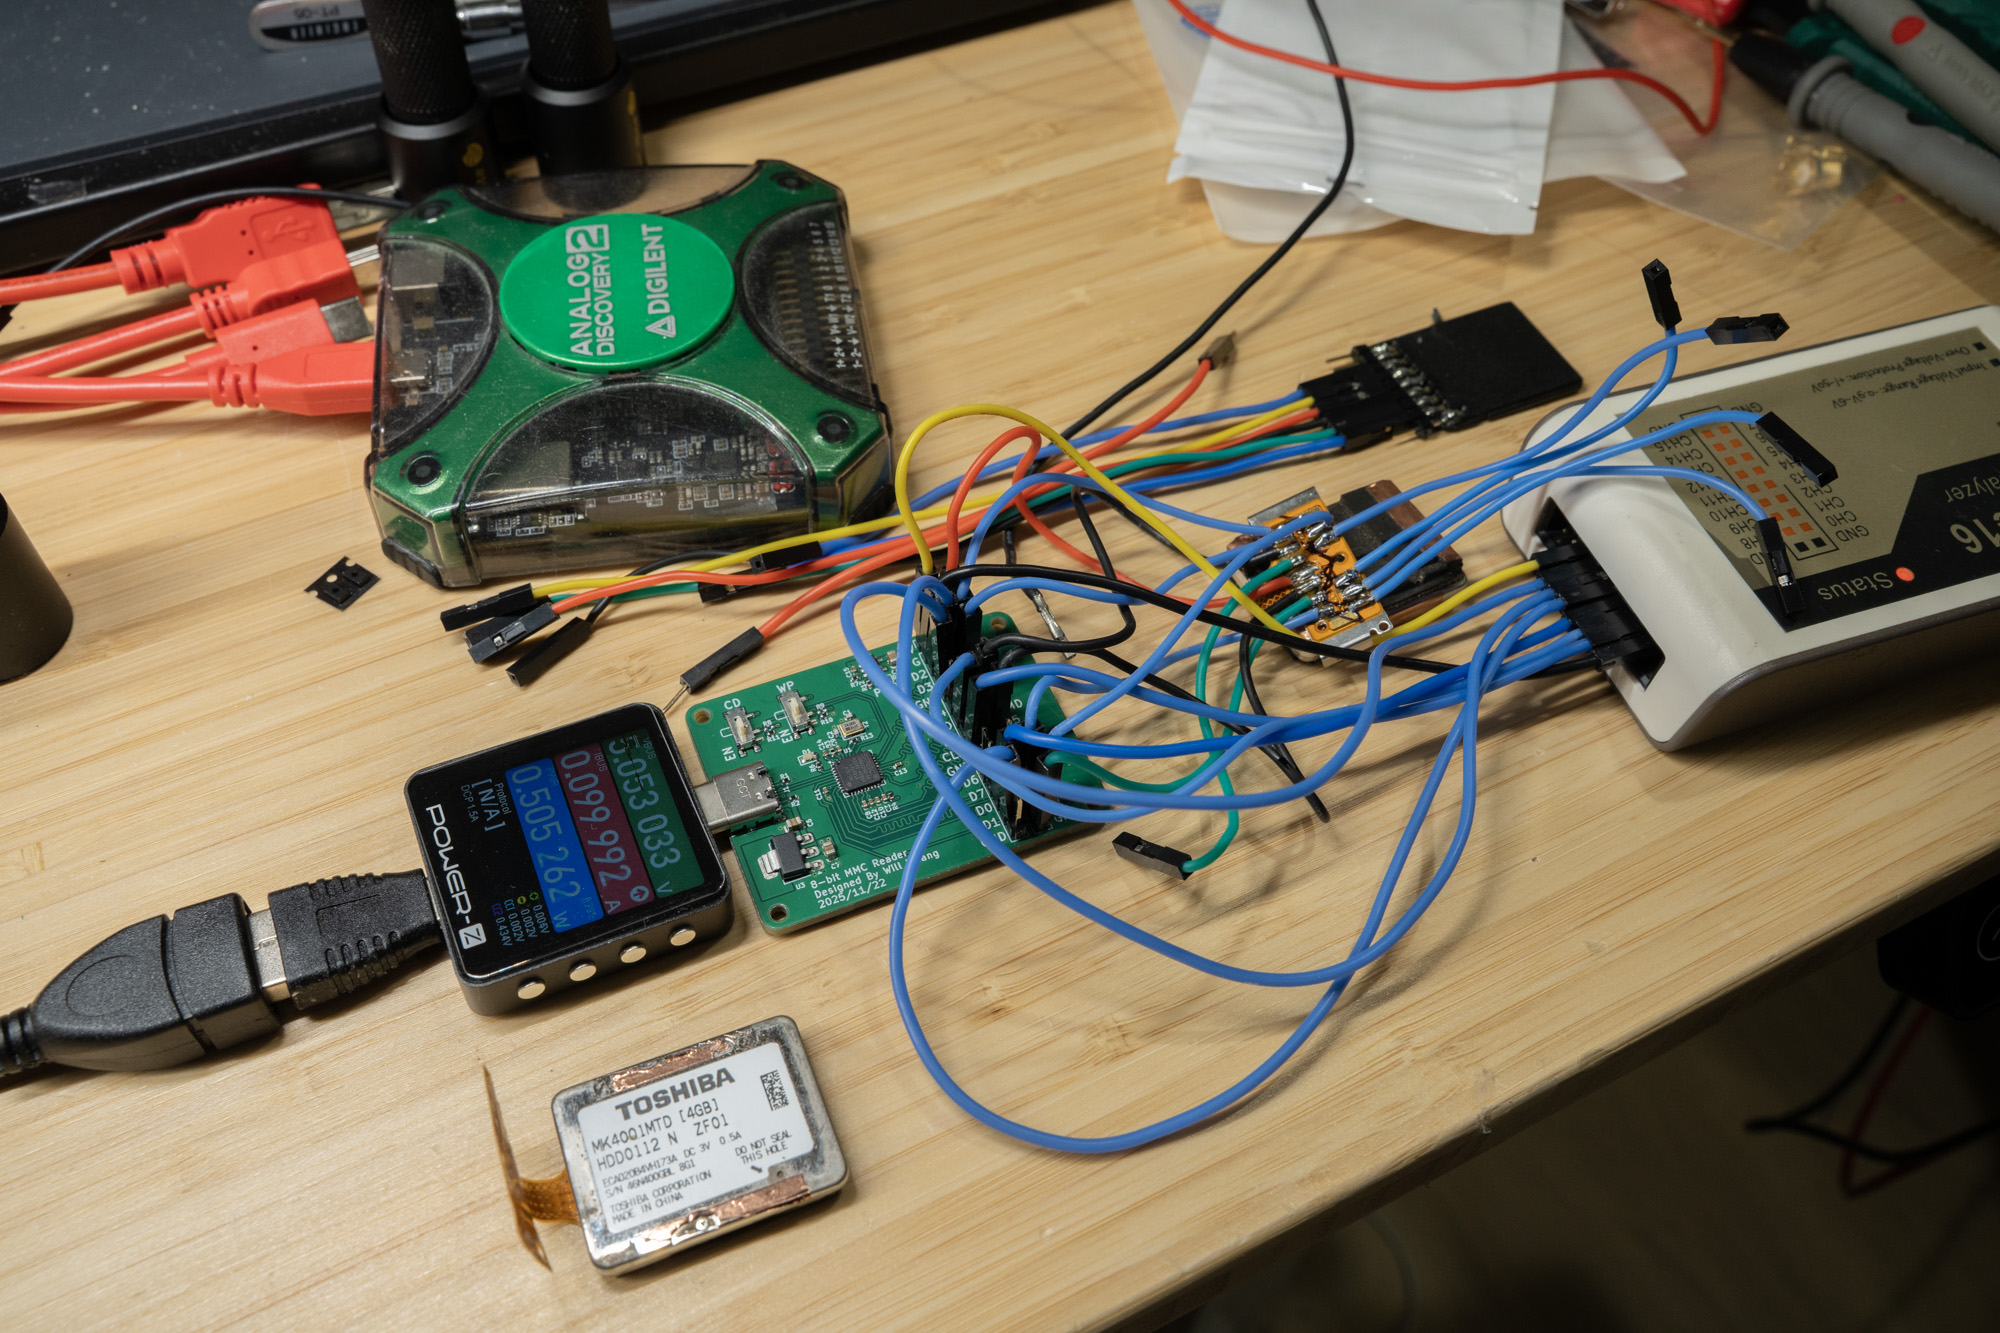 will127534/mk4001mtd-usb-bridge
RP2040 firmware that bridges a Toshiba MK4001MTD 0.85" SDIO microdrive as a USB mass storage device, implementing the full SDIO-ATA protocol stack…
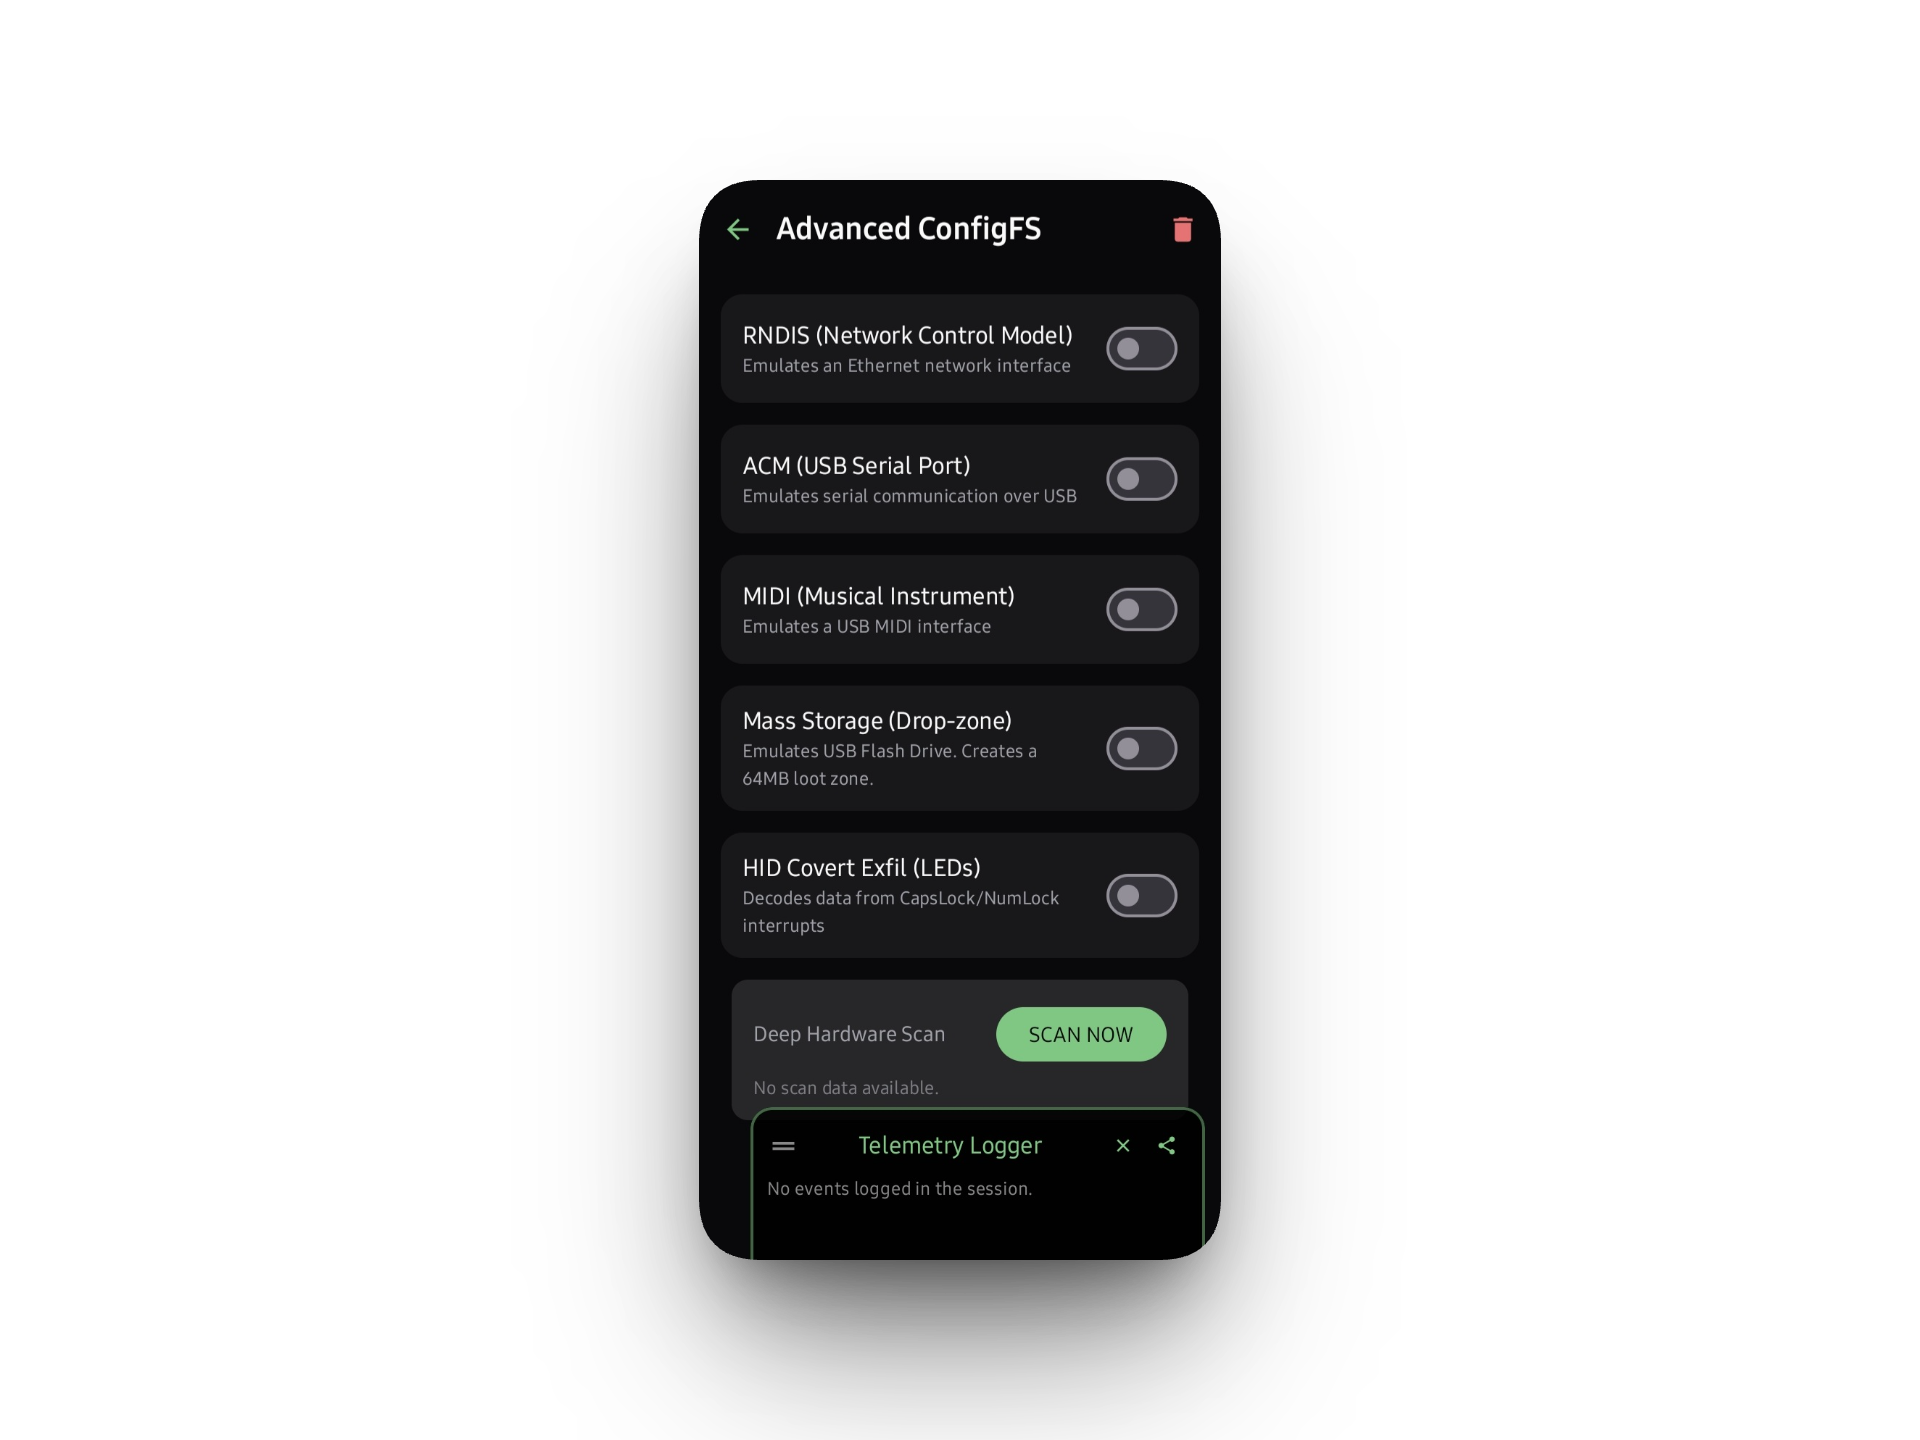 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 smillier/hydralincan
Hydrabus Shield for LIN and CAN Buses
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 badchemical/iot-vulnerability-research-public
Independent IoT security research, vulnerability disclosures, and PoCs focusing on firmware analysis, hardware interfaces, and cryptographic flaws.
 fahreddinaykut/sparkaltbatteryboard
Reverse-engineered I2C/SMBus battery interface board for DJI Spark, replacing OEM smart battery with standard 3S LiPo. Includes protocol analysis,…
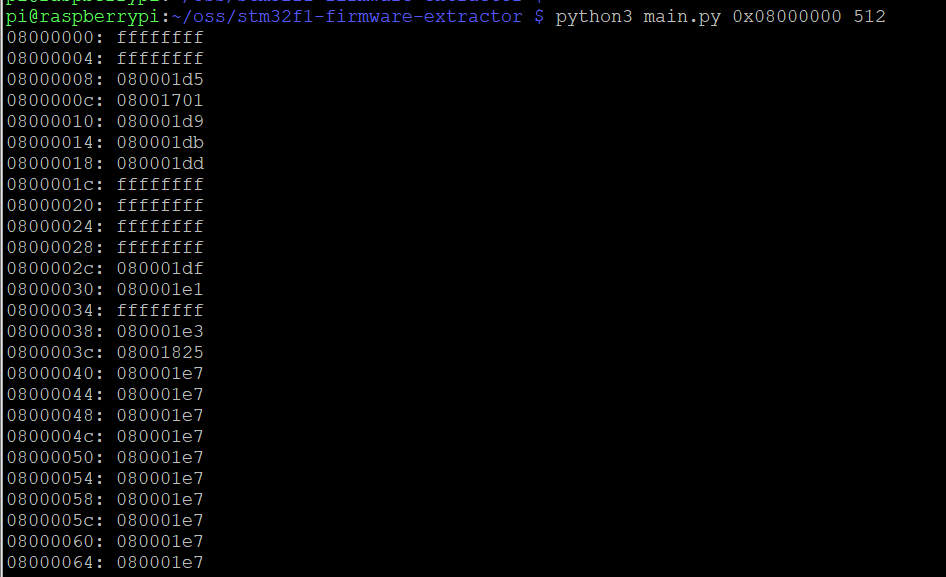 wuxx/cve-2020-8004
Exploit tool for CVE-2020-8004 targeting STM32F1 microcontrollers, enabling firmware extraction via OpenOCD and Python scripts to bypass readout…
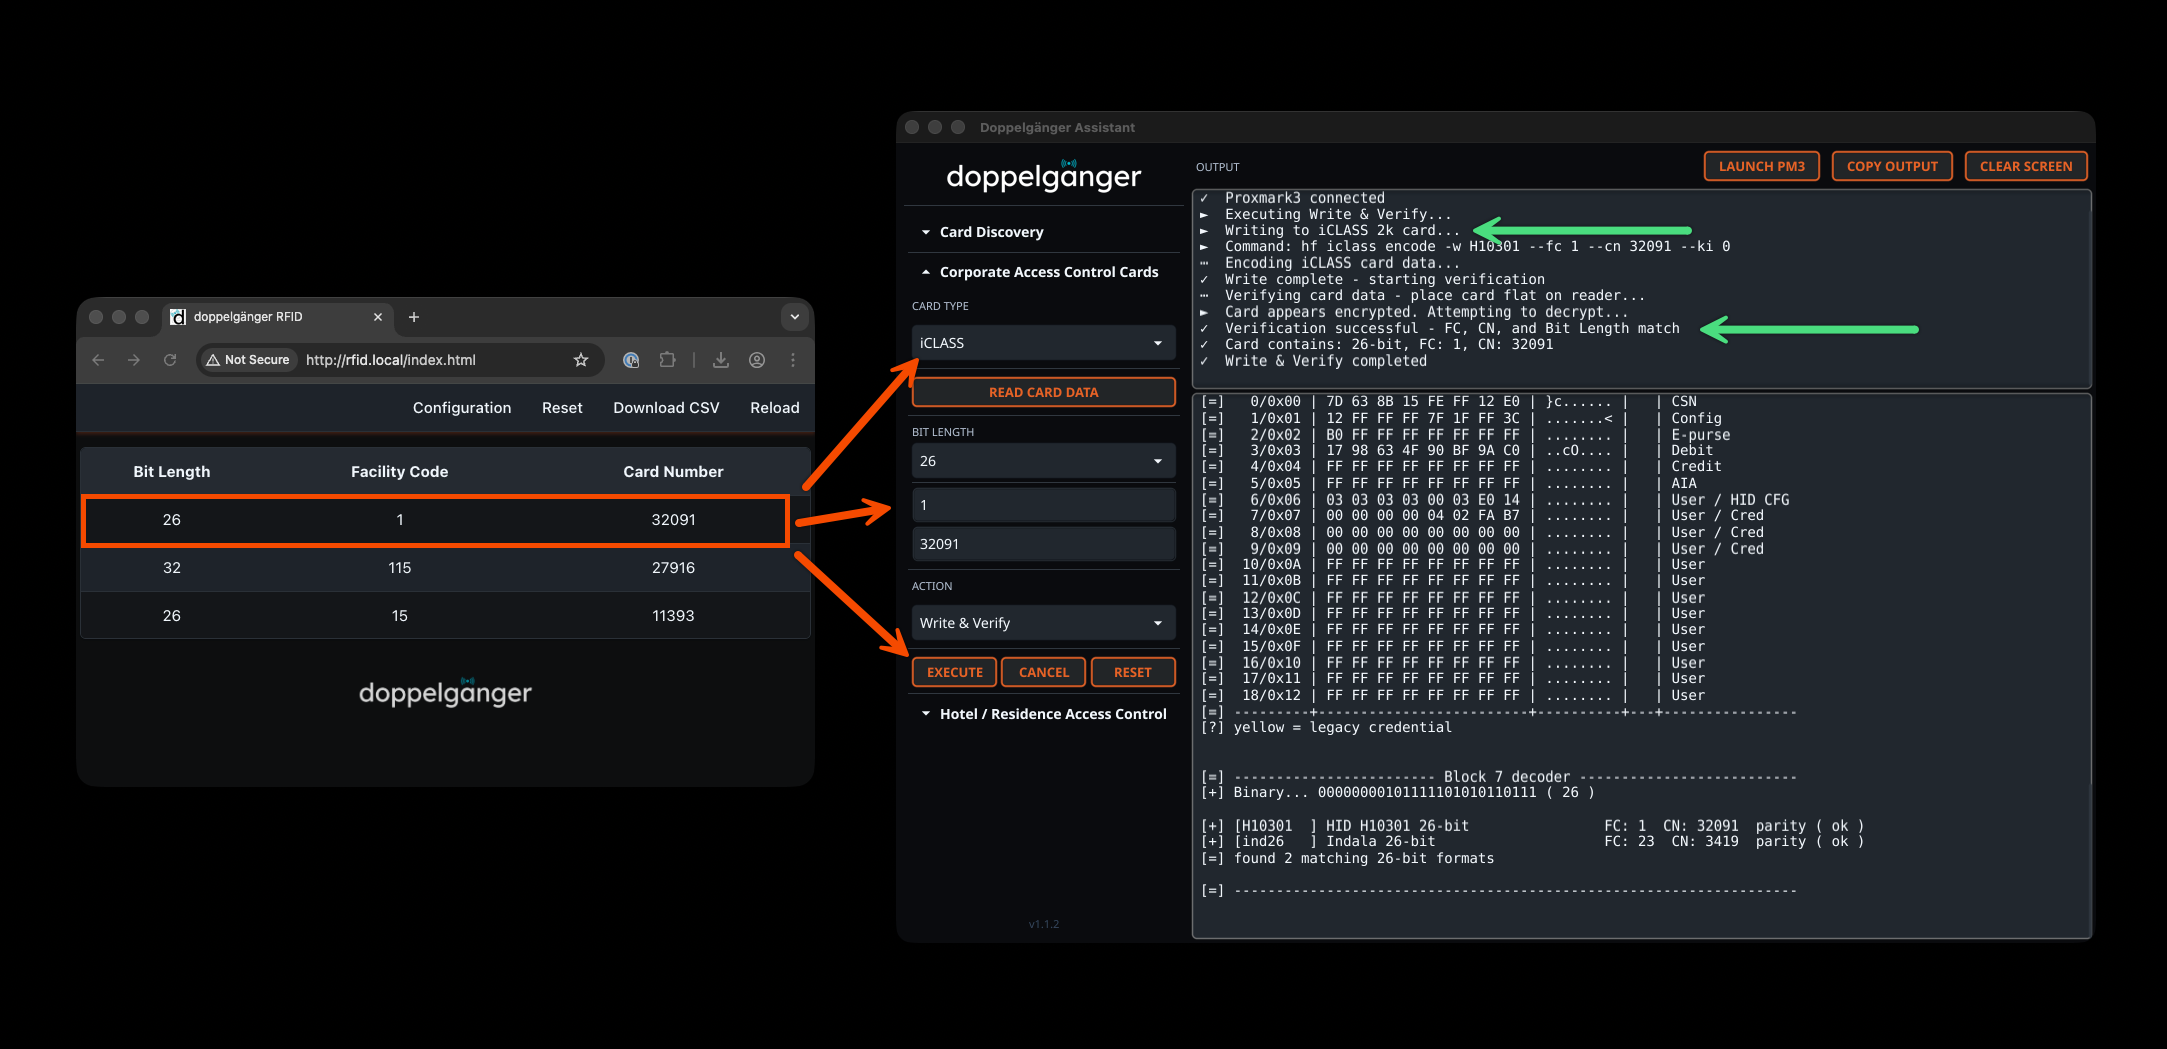 tweathers-sec/doppelganger_assistant
Card calculator and Proxmark3 Plugin for writing and/or simulating every card type that Doppelgänger Community, Pro, Stealth, and MFAS support.
 breaktoprotect/cve-2017-16778-intercom-dtmf-injection
A coordinated disclosure and security advisory on Fermax Intercom DTML Injection vulneraiblity. Special thanks to Fermax International for prompt…
 fxrstor/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 xswxm/nrf24-injection
A tool set for sniffing devices and launching attacks with Crazyradio
 hydrausb3/wch-ch56x-lib
Library for WCH CH56x-based boards with tested USB3/USB2/HSPI/SerDes drivers, logging and deferred interrupts
 vl4dr/cve-2024-42642
Proof-of-concept exploits for three vulnerabilities in Crucial MX500 SSD firmware update mechanism, enabling buffer overflows and potential code…
 ggfuchsi-oss/lg-webos-kexec
Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…
 drapl0n/pwnkit
USB Rubber Ducky payload that exploits CVE-2021-4034 to escalate privileges and spawn a root shell on Unix-like systems in under 10 seconds.