

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 whad-team/whad-client
Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…
 jarrettgohxz/cve-research
A repository that contains all the working PoC I have crafted for known CVEs, and details on any ongoing research I am currently doing (mostly Iot…
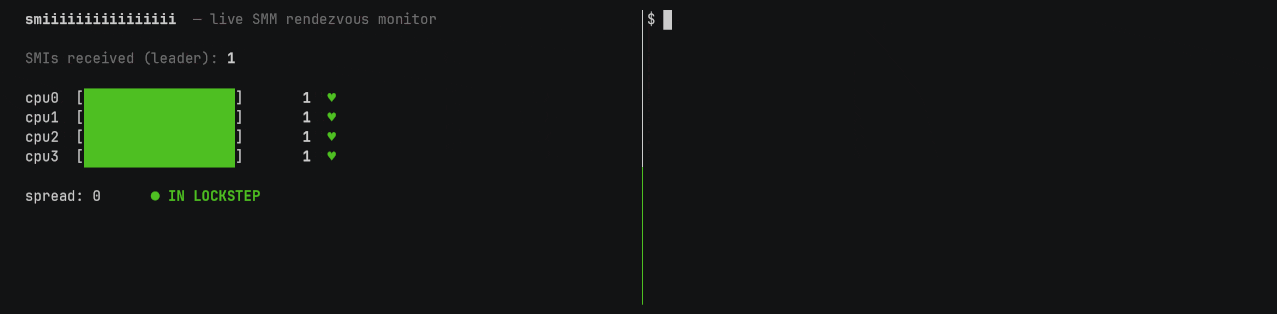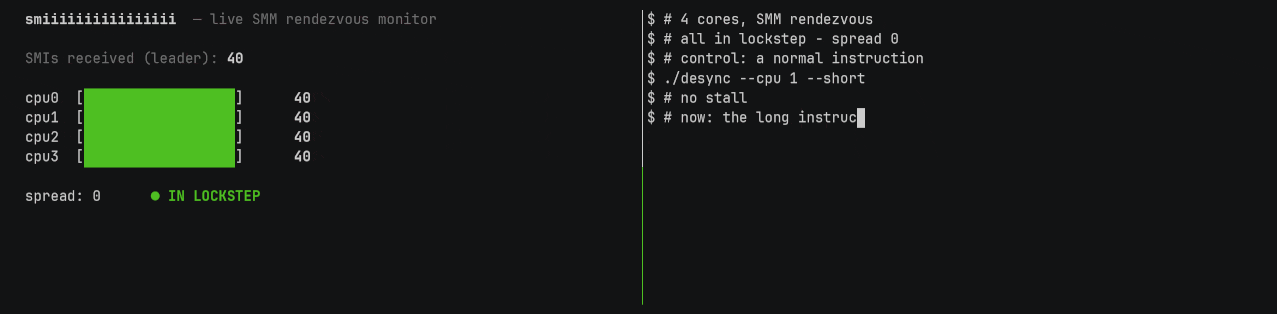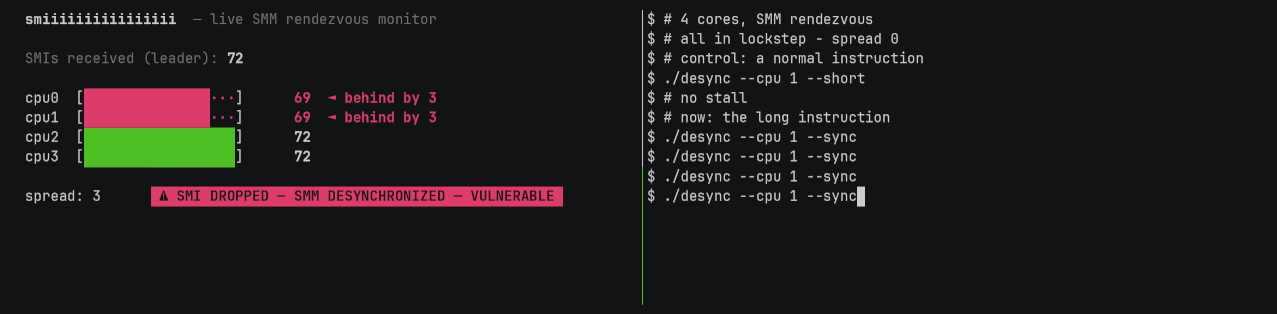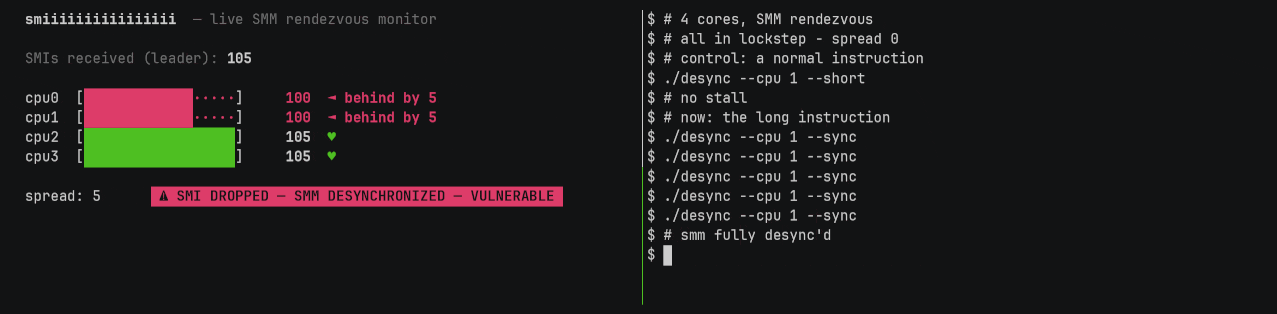 xoreaxeaxeax/smiiiiiiiiiiiiiiii
A very very very very very very very long interrupt
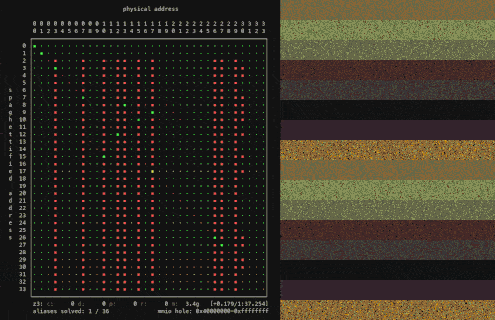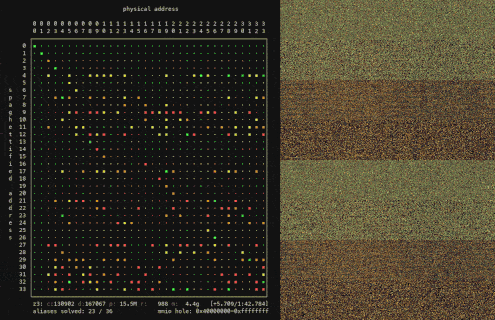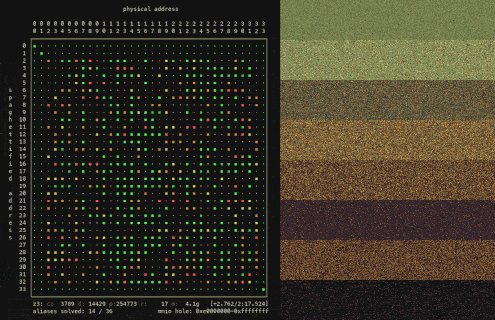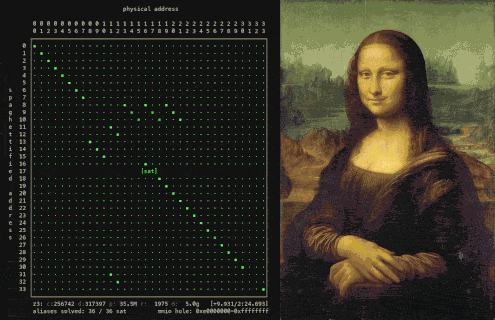 xoreaxeaxeax/skitter-creek-bath-salts
Unlocking _everything_ on the CPU with DRAM scrambling
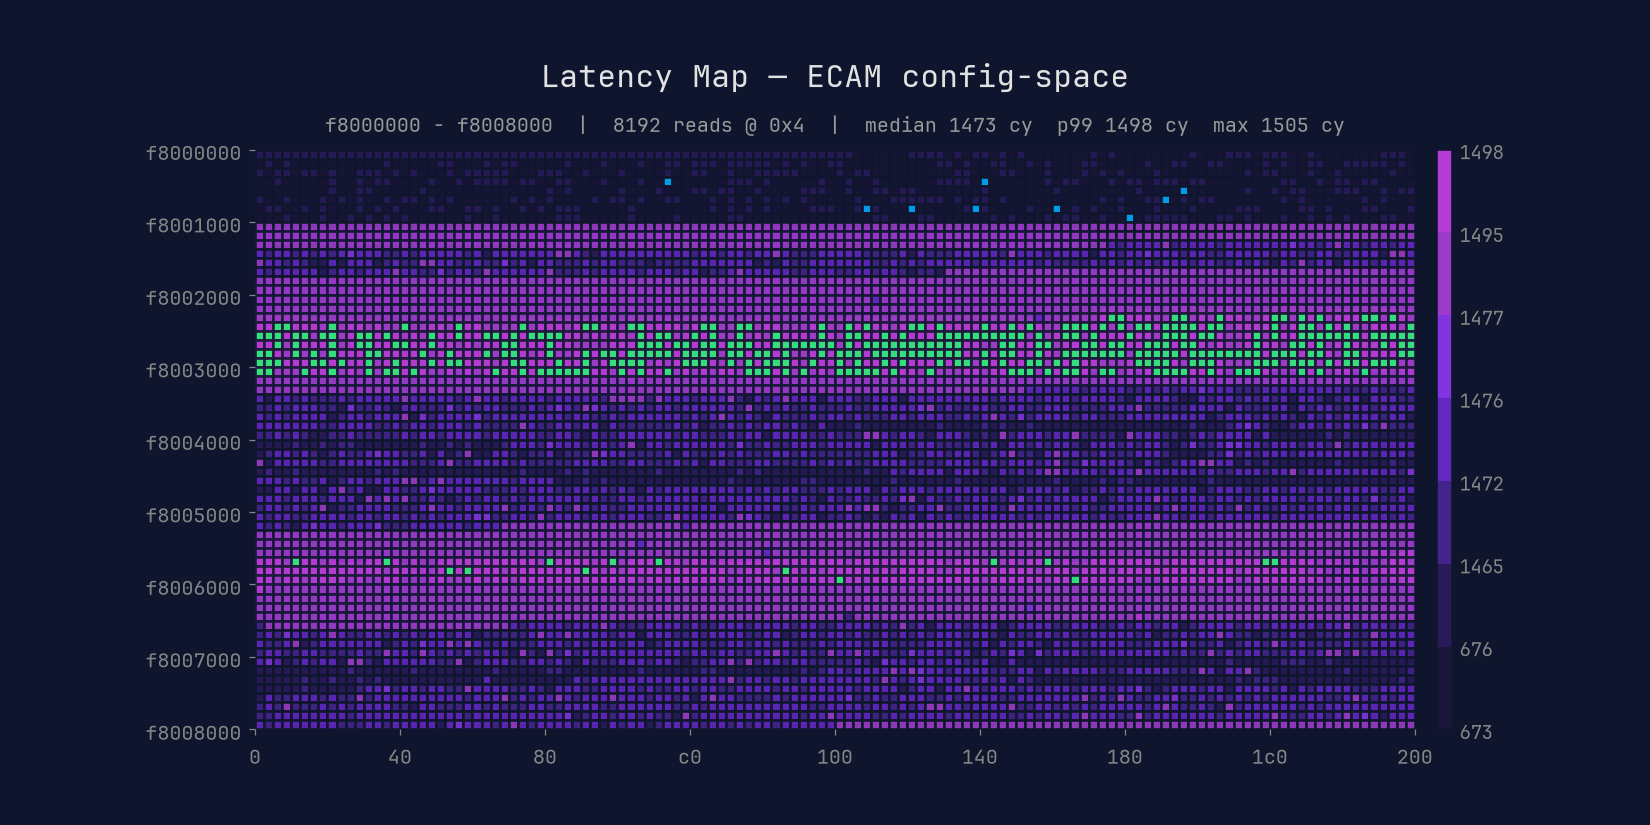 xoreaxeaxeax/mmiotic
Latency x-ray for undocumented hardware
 george0papasotiriou/cve-2026-22013-hardware-wallet-usb-descriptor-buffer-overflow
Stack buffer overflow PoC for a hardware wallet USB descriptor parser (CVE-2026-22013), showing return-address overwrite and code execution via…
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
 wh00hw/pyflipper
Flipper Zero Python CLI Wrapper
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
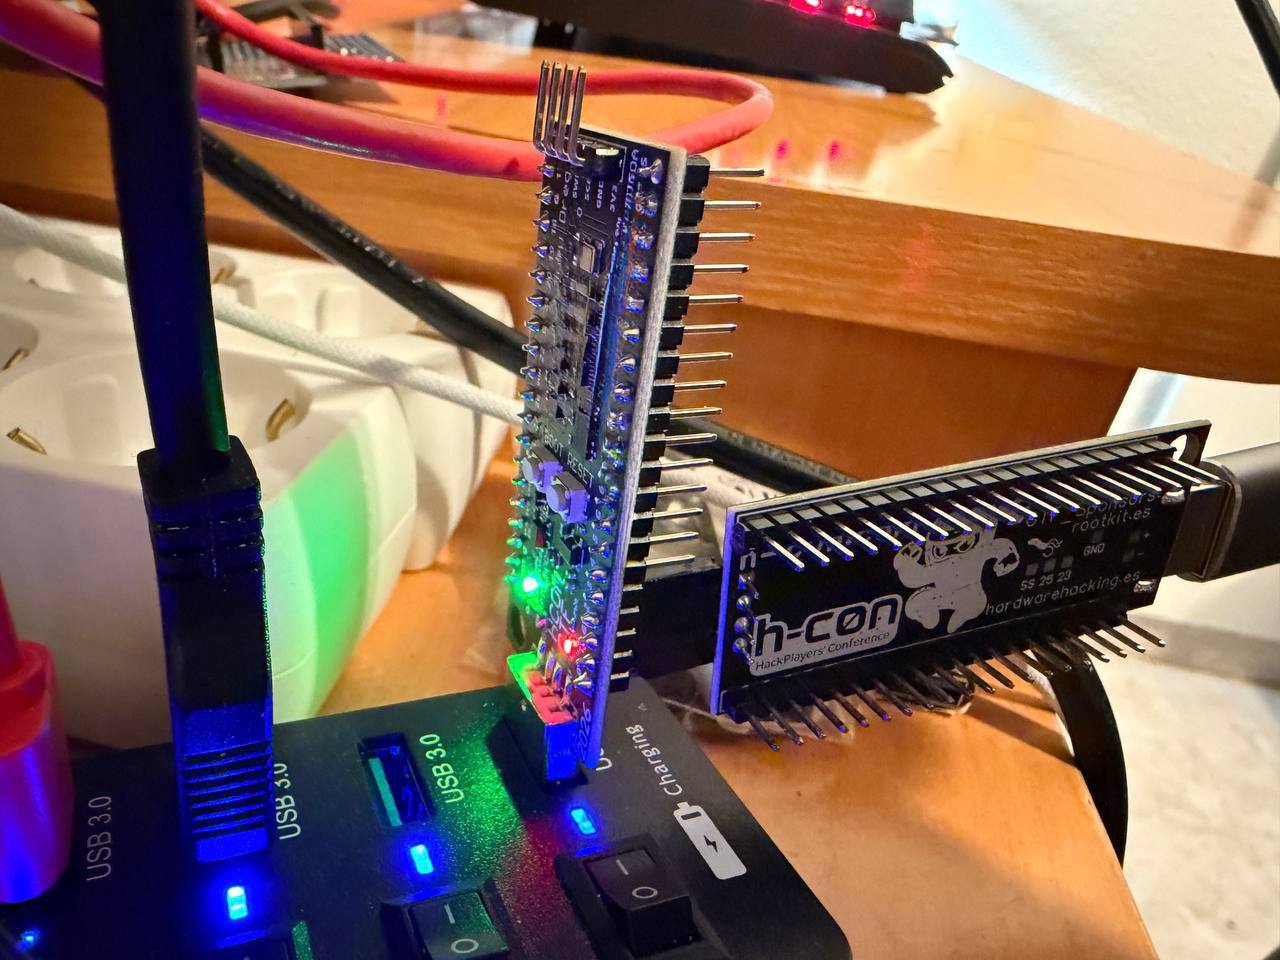 therealdreg/hcon2026hwctf
Hardware Hacking CTF hcon2026hwctf - RISCV Hazard3 (@Wren6991) Exploiting by @b1n4ri0 @antoniovazquezblanco & @therealdreg
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
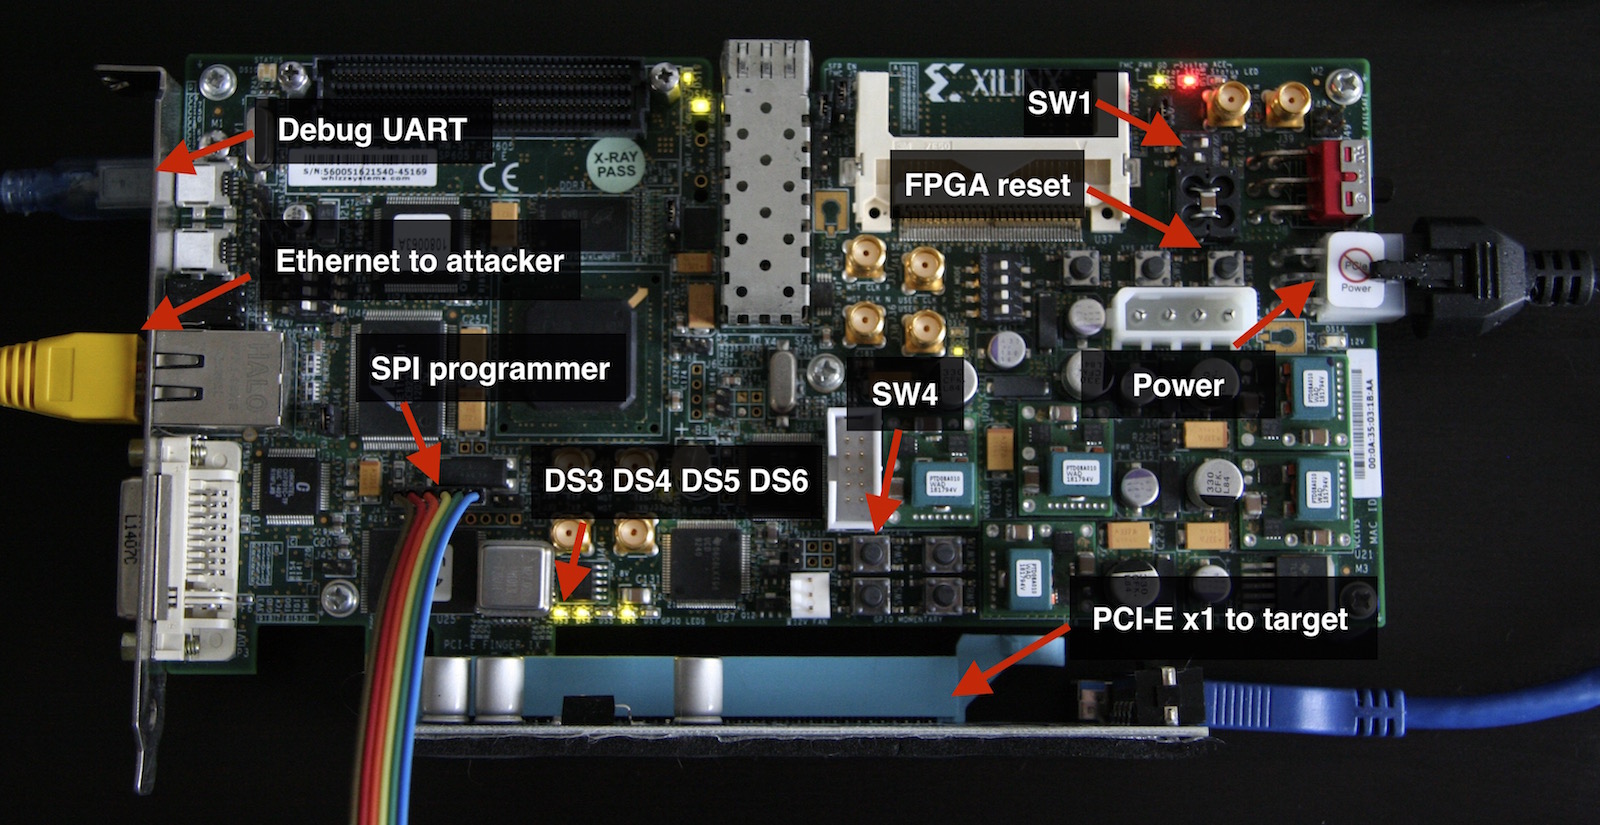 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 imnot-ye/cve-2019-17147
Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…
 rupeshsurve04/cve-2025-67399
Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…
 fxrstor/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 m-gsch/s5late
iPod Nano 7G bootrom exploit a bit too late
 nfc-tools/libnfc
Platform independent Near Field Communication (NFC) library