
Fault-Injection-Finder
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
binary-analysisembedded-systems-securityexploitation+5
14
geeoon/fault-injection-finderAutomatically find and execute fault injection attacks
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 mister-devel/main_mister
FPGA-based hardware emulation platform main binary and documentation for retro system development, firmware compilation, and hardware security…
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
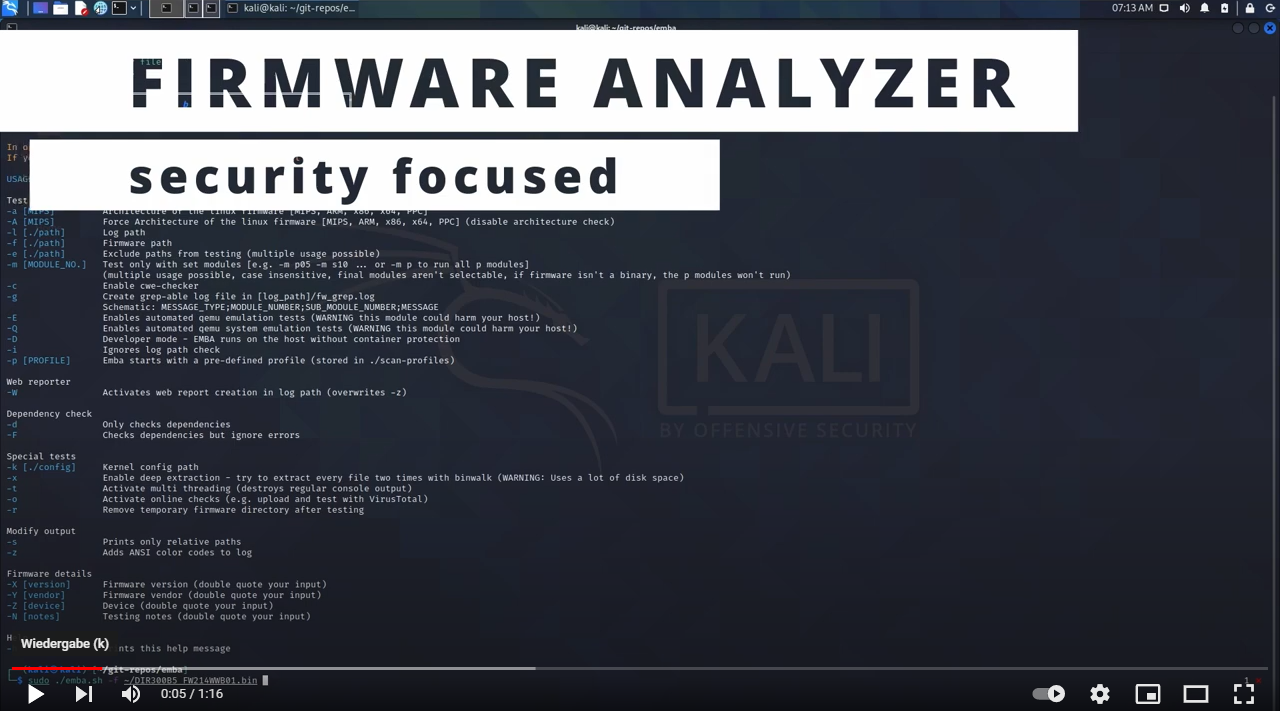 e-m-b-a/emba
EMBA - The firmware security analyzer
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
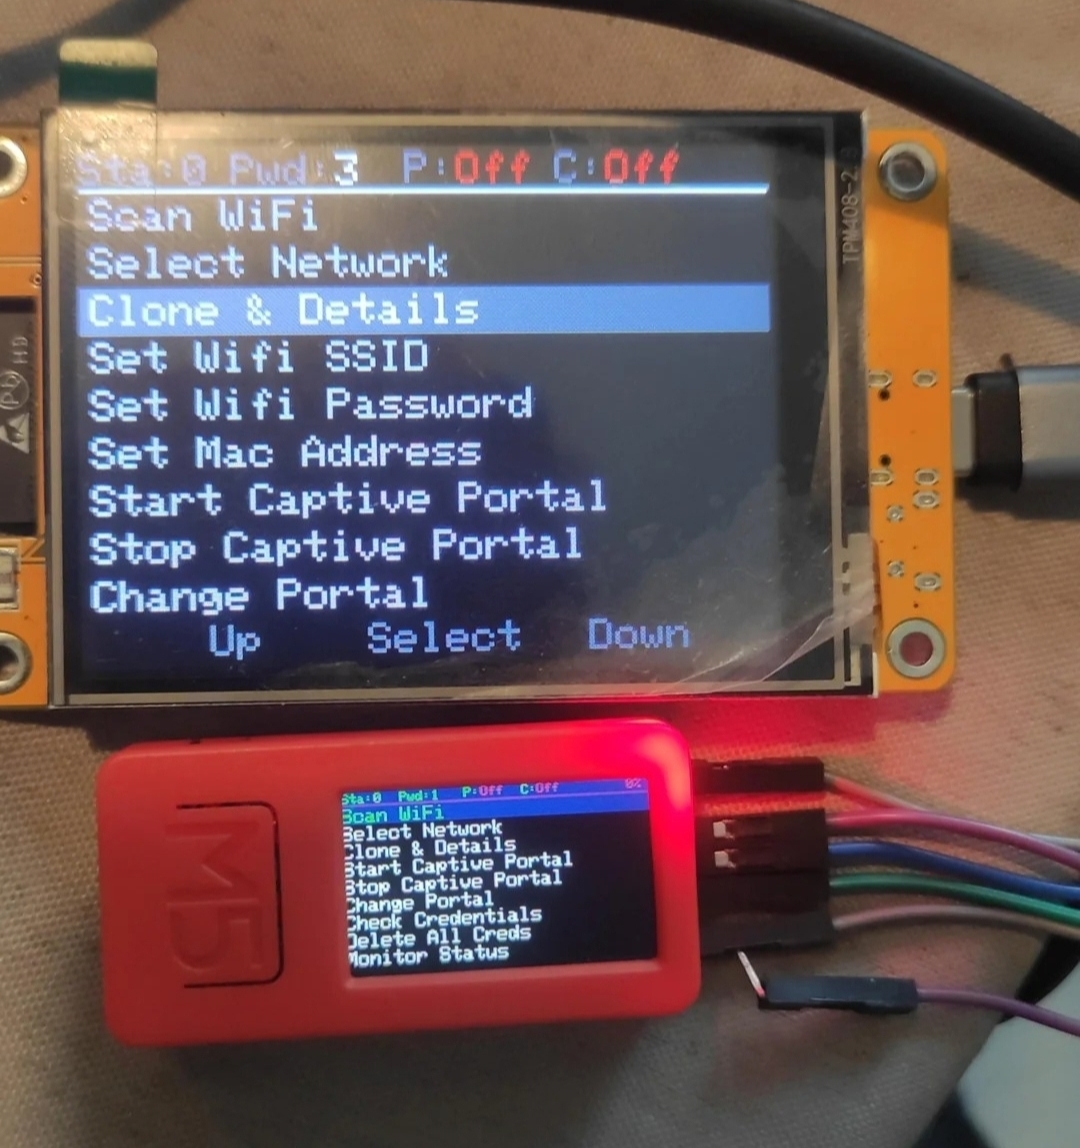 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 newaetech/chipwhisperer
Open-source hardware security toolchain for power trace capture, side-channel analysis, and glitching/fault-injection attacks on embedded devices and…
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…
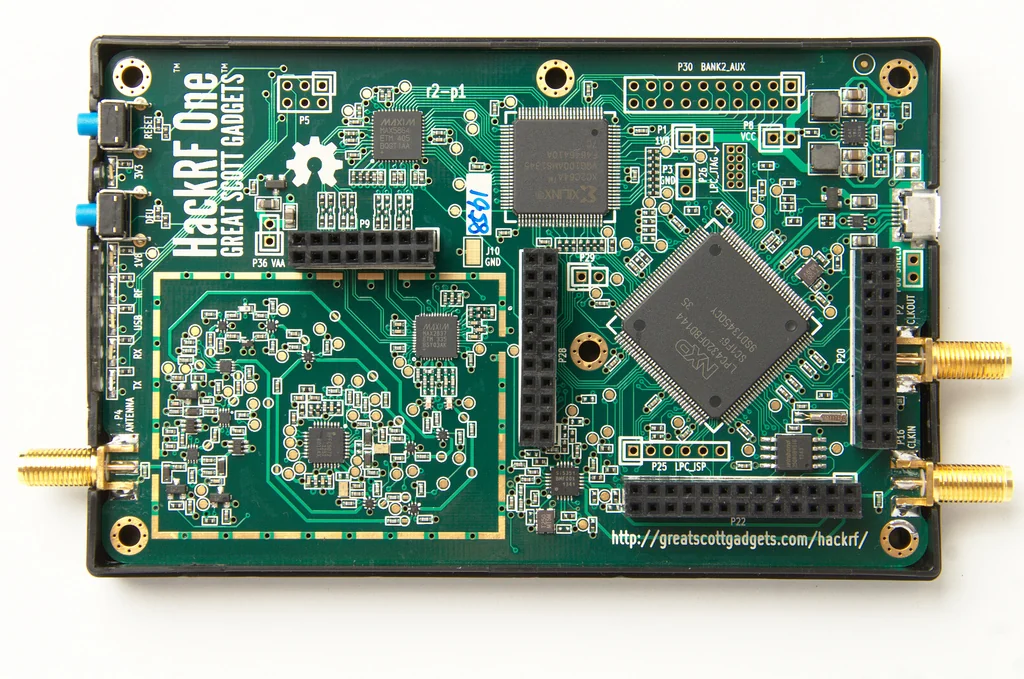 greatscottgadgets/hackrf
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…