IoT-Vulnerability-Research-Public

Independent IoT security research, vulnerability disclosures, and PoCs focusing on firmware analysis, hardware interfaces, and cryptographic flaws.

Independent IoT security research, vulnerability disclosures, and PoCs focusing on firmware analysis, hardware interfaces, and cryptographic flaws.

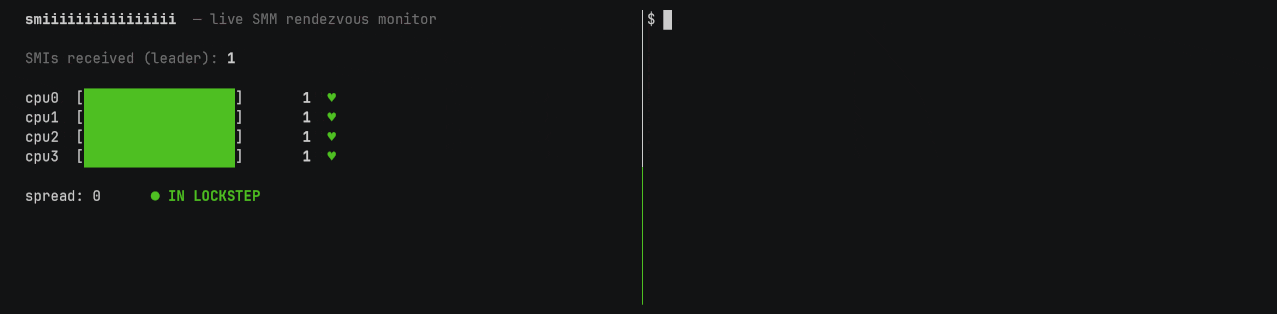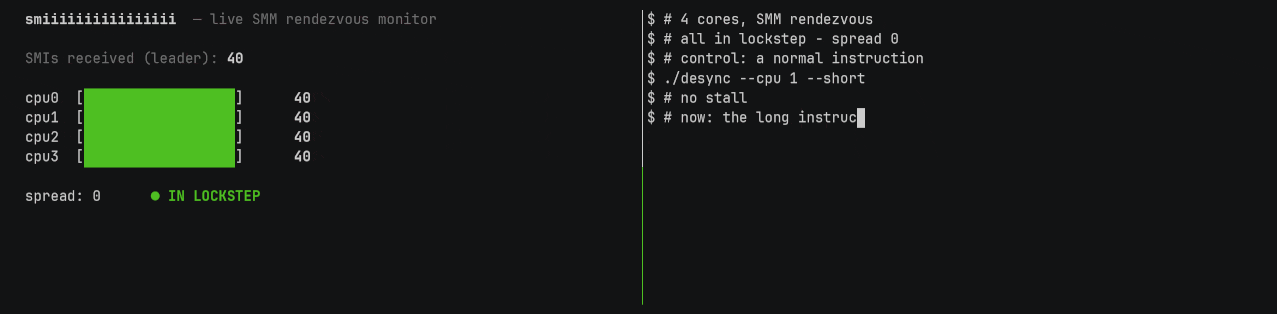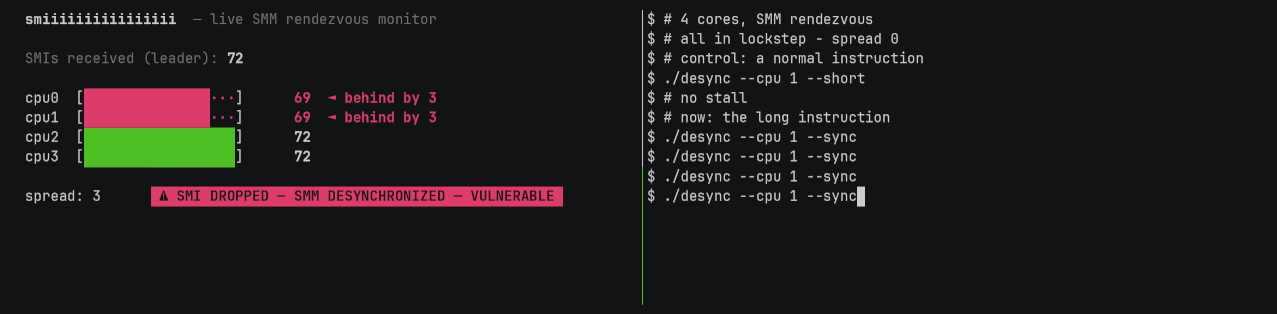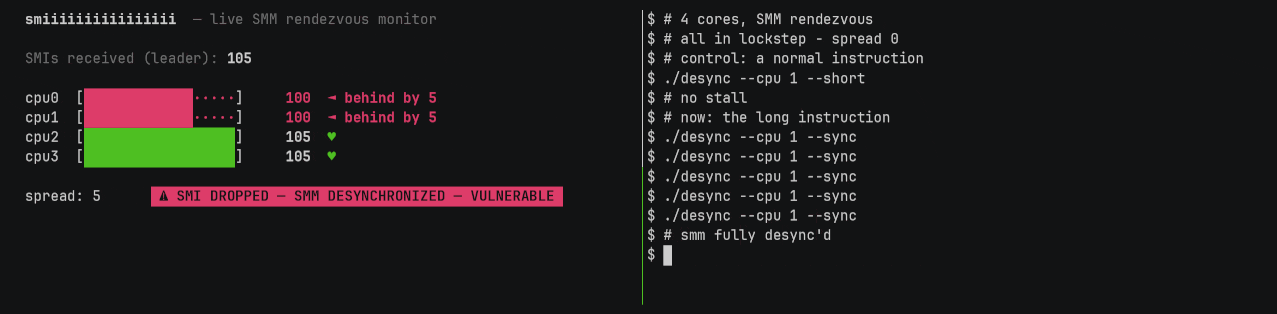
A very very very very very very very long interrupt

Proof-of-concept demonstrating a microarchitectural data leak in Loongson LA464/LA664 processors via undefined upper bits of LASX vector registers,…

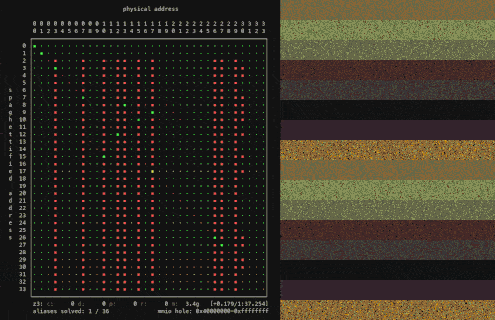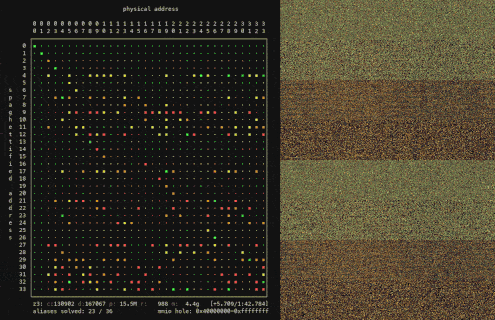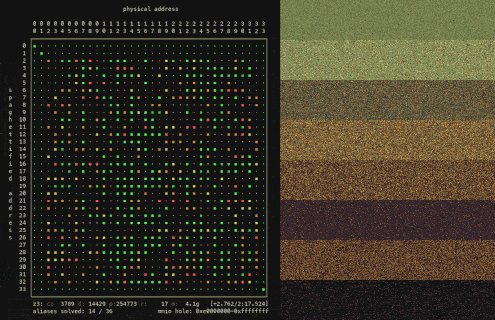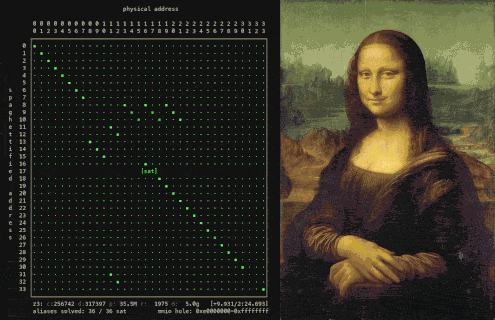
Unlocking _everything_ on the CPU with DRAM scrambling

CVE-2022-38694 Hardened Exploit - RP2350 USB Host Auto Flasher for Unisoc devices

A list of public attacks on BitLocker

Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…

Advisory for CVE-2025-65731

An app that enables payload injection into a Switch console from an Android device by exploiting the CVE-2018-6242 vulnerability

Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…

CVE-2025-50777: Root Access and Plaintext Credential Exposure in AZIOT Smart CCTV

First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…

Proof-of-concept exploit for CVE-2021-34600, demonstrating a key generation vulnerability in Telenot access control systems using Proxmark3 RFID…

TPM Genie is an I2C bus interposer for discrete Trusted Platform Modules

Collection of "modchip" designs for launching payloads via the Tegra RCM bug (CVE-2018-6242)