
ns2jb
 pepsipu/ns2jb
Console jailbreak demo that executes native functions inside the Switch 2 filesystem process via SmileBASIC, verifies results, and restores original…
embedded-systems-securityexploitationhardware-hacking+4
27
pepsipu/ns2jbConsole jailbreak demo that executes native functions inside the Switch 2 filesystem process via SmileBASIC, verifies results, and restores original…

 gmh5225/memtools
Windows Linux DMA、Dump 、Direct、inject 内存读取、写入工具
 greatscottgadgets/facedancer
Implement your own USB device in Python, supported by a hardware peripheral such as Cynthion or GreatFET
 emenstanougat/esp32-bluejammer
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
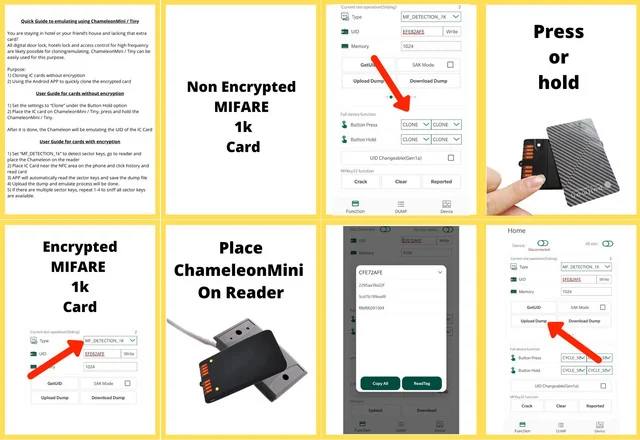 rfidresearchgroup/chameleonmini
Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
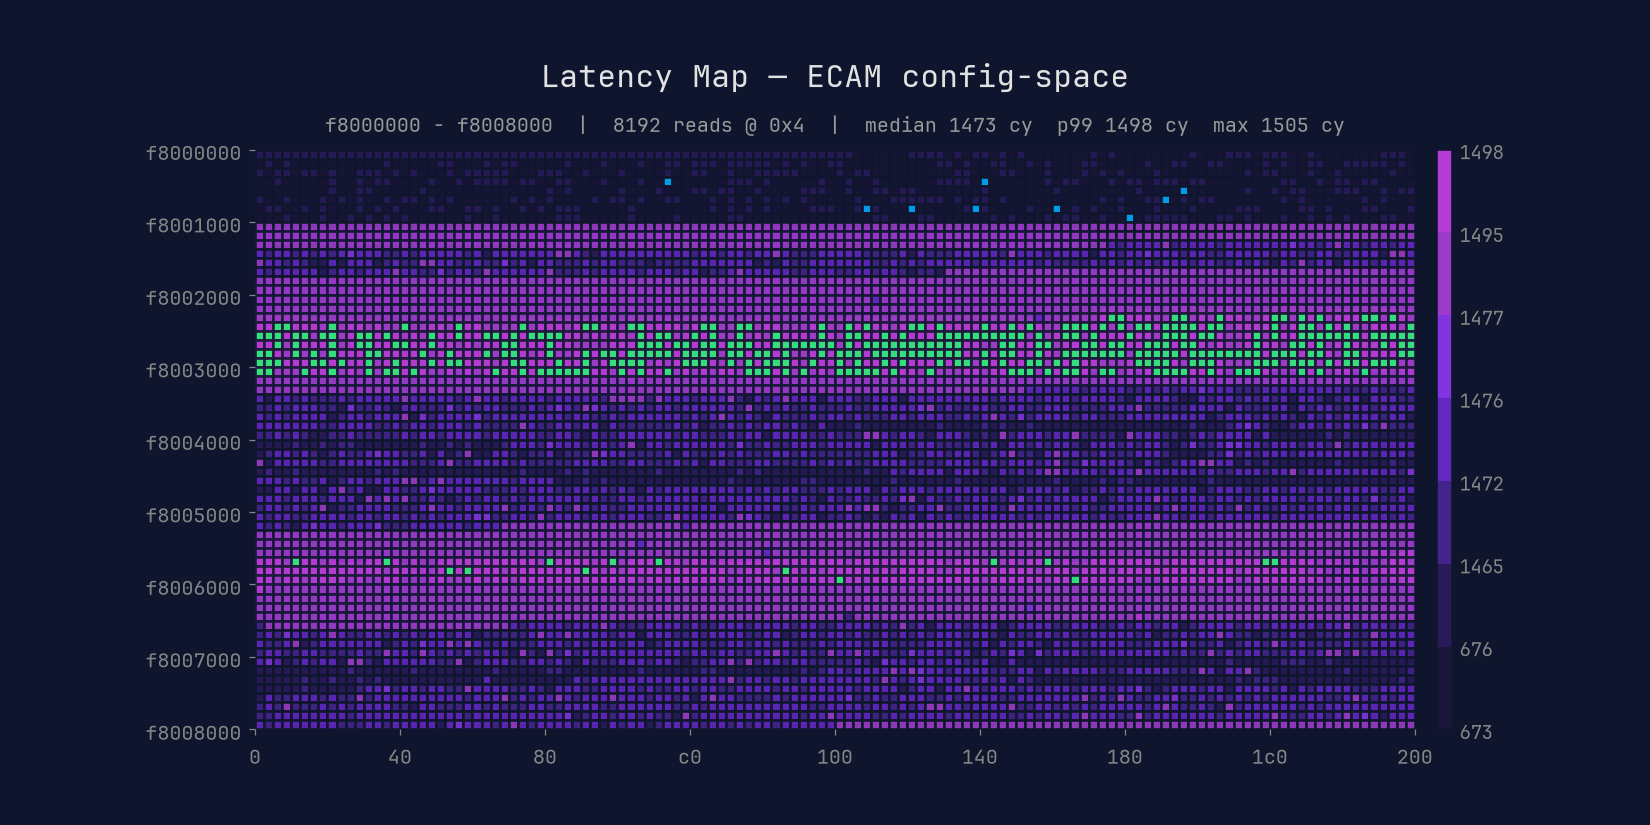 xoreaxeaxeax/mmiotic
Latency x-ray for undocumented hardware
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 jimilinuxguy/lrs-pager-systems-bruteforce
Long Range Pager Systems pagers and coasters URH and YS1 (yardstick one / cc11xx) information and brute force tool
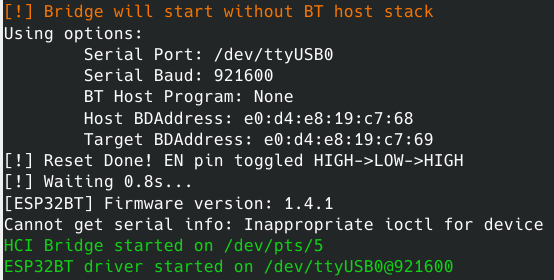 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 i-am-jakoby/powershell-for-hackers
This repository is a collection of powershell functions every hacker should know
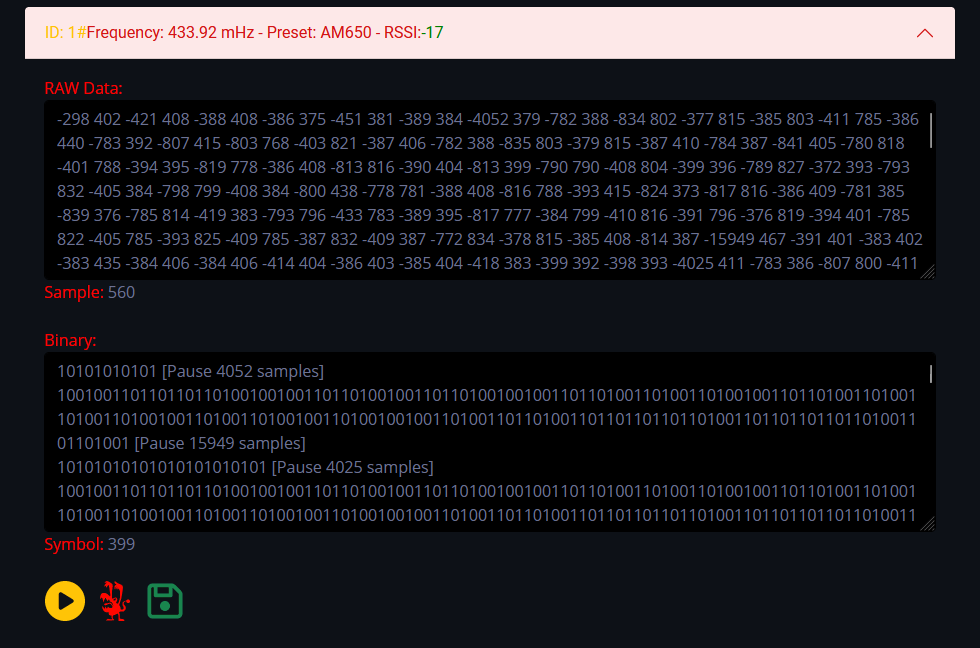 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.