Android-PIN-Bruteforce

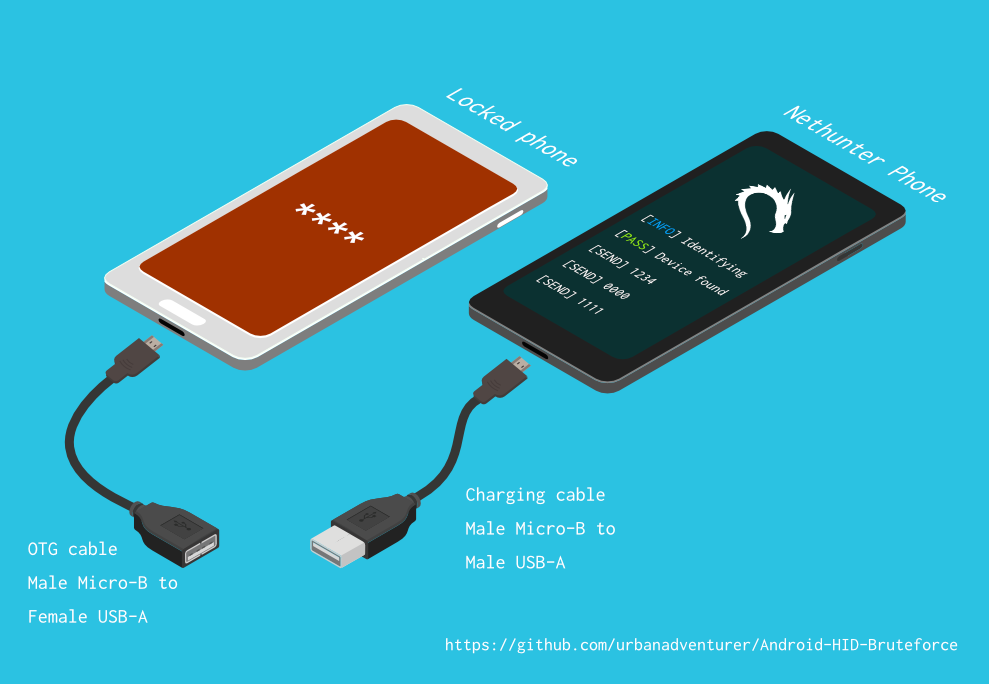
Unlock an Android phone (or device) by bruteforcing the lockscreen PIN. Turn your Kali Nethunter phone into a bruteforce PIN cracker for Android…

Unlock an Android phone (or device) by bruteforcing the lockscreen PIN. Turn your Kali Nethunter phone into a bruteforce PIN cracker for Android…

Python-Based Pentesting Framework

Firmware Analysis and Comparison Tool

:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…

The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more

EMBA - The firmware security analyzer

Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…

Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…

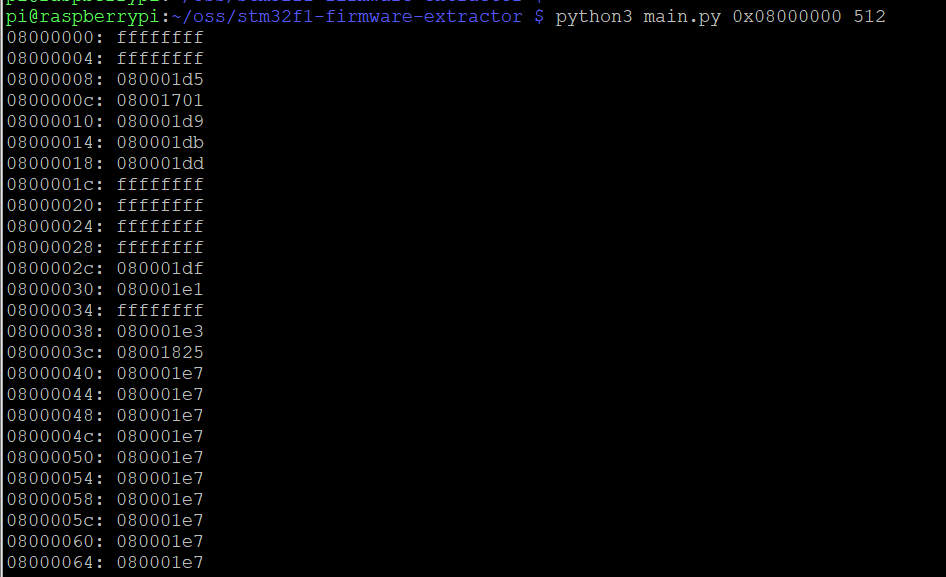
Exploit tool for CVE-2020-8004 targeting STM32F1 microcontrollers, enabling firmware extraction via OpenOCD and Python scripts to bypass readout…

This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…

Vankyo MatrixPad S30 (Unisoc SC9863A) — Bootloader unlock via CVE-2022-38694 FDL1 method

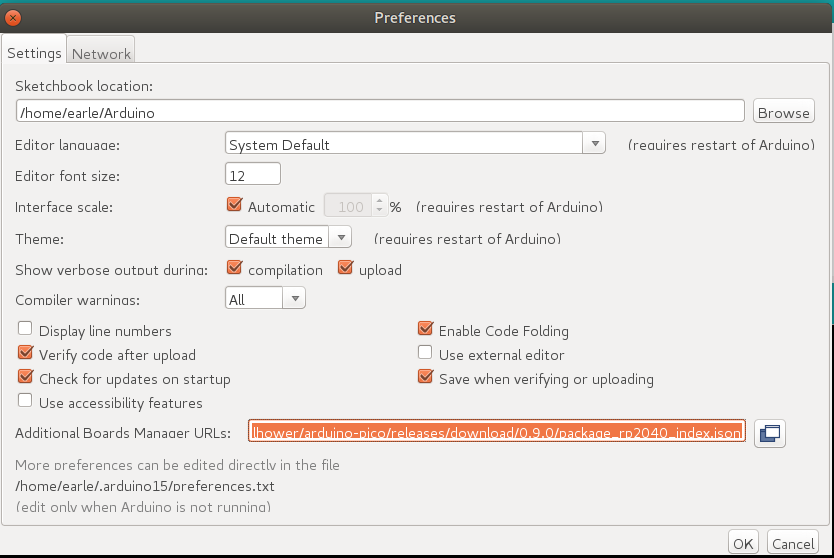
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards

uhubctl - USB hub per-port power control

Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).

Research tooling to boot Linux on iPad mini 1 via checkm8, patched iBSS/iBEC, and custom bare-metal payloads, including device tree port, kernel…

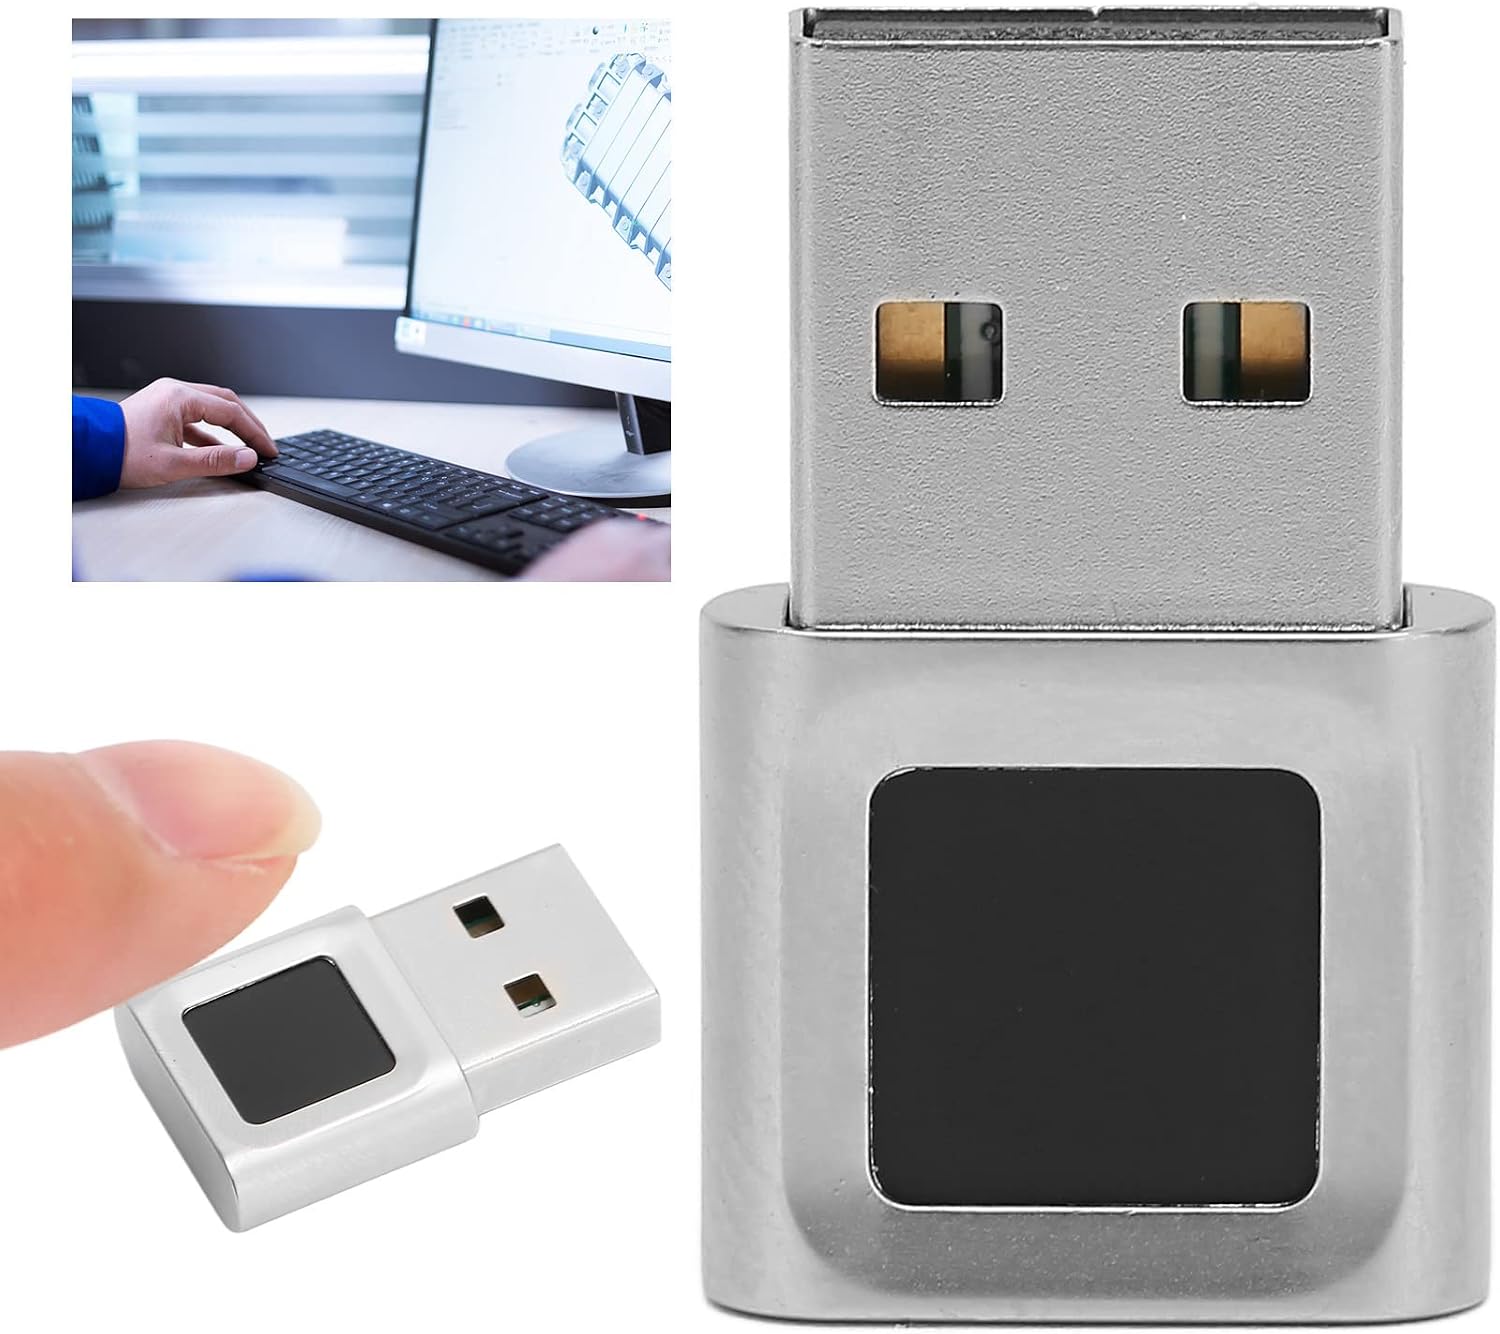
Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…

Bluetooth experimentation framework for Broadcom and Cypress chips.

Official OpenOCD Read-Only Mirror (no pull requests)