

ESP32Marauder
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
bluetooth-securitydefensive-toolsembedded-systems-security+6
12.6k
justcallmekoko/esp32marauderA suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 nccgroup/sniffle
Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 cisc0-gif/kitt
Python-Based Pentesting Framework
 spacehuhntech/esp8266_deauther
Affordable WiFi hacking platform for testing and learning
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 fahreddinaykut/sparkaltbatteryboard
Reverse-engineered I2C/SMBus battery interface board for DJI Spark, replacing OEM smart battery with standard 3S LiPo. Includes protocol analysis,…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
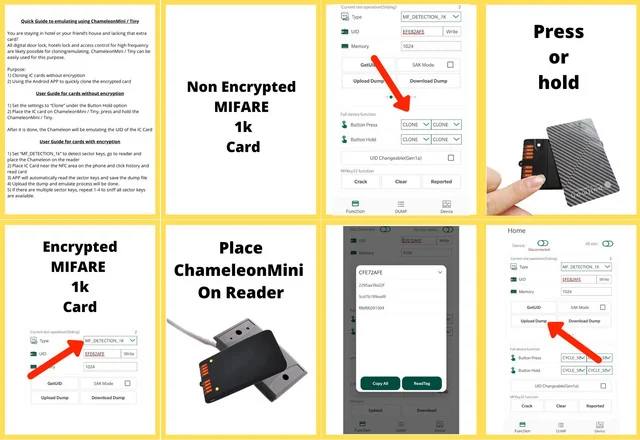 rfidresearchgroup/chameleonmini
Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.
 skickar/digitrack
Attacks for $5 or less using Arduino
 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…
 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…