ESP32-BlueJammer
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.

ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.

A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32

The open-source wireless research platform for ESP32.

Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…

Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.

Python-Based Pentesting Framework

The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.

Implement your own USB device in Python, supported by a hardware peripheral such as Cynthion or GreatFET

:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…

The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more

A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol

BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.

🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…

Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…

Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…

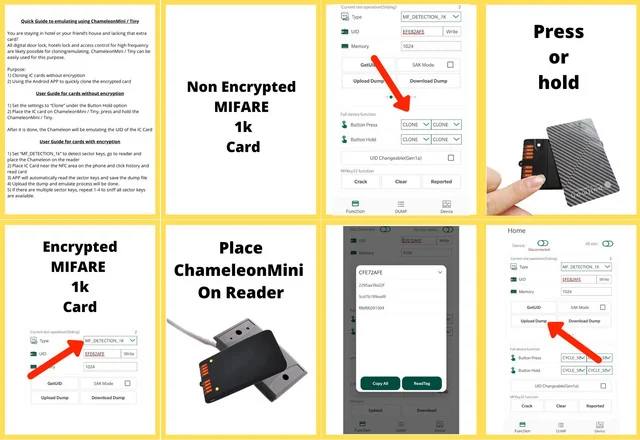
Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.