
cheat-engine
 cheat-engine/cheat-engine
Cheat Engine. A development environment focused on modding
binary-analysisdebuggersexploitation+3
19.2k
cheat-engine/cheat-engineCheat Engine. A development environment focused on modding
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 rathole-org/rathole
A lightweight and high-performance reverse proxy for NAT traversal, written in Rust. An alternative to frp and ngrok.
 umputun/reproxy
Lightweight edge HTTP(S) server and reverse proxy with automatic SSL, Docker/Consul discovery, per-route authentication, rate limiting, and…
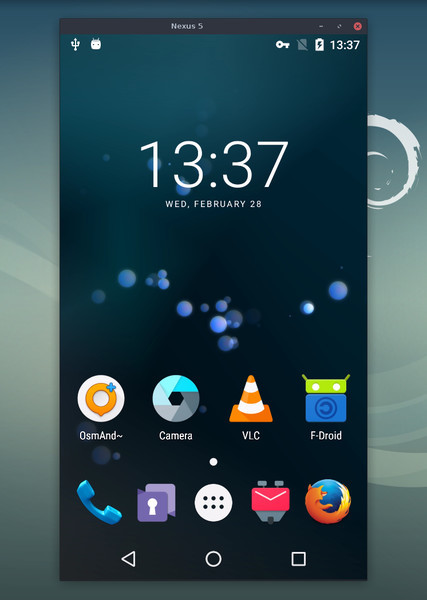 genymobile/scrcpy
Display and control your Android device
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 upx/upx
UPX - the Ultimate Packer for eXecutables
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 auroraoss/aurorastore
Open-source Android client for browsing and downloading apps from Google Play with anonymous login, device/locale spoofing, and tracker detection.
 zodiacon/alltools
All reasonably stable tools
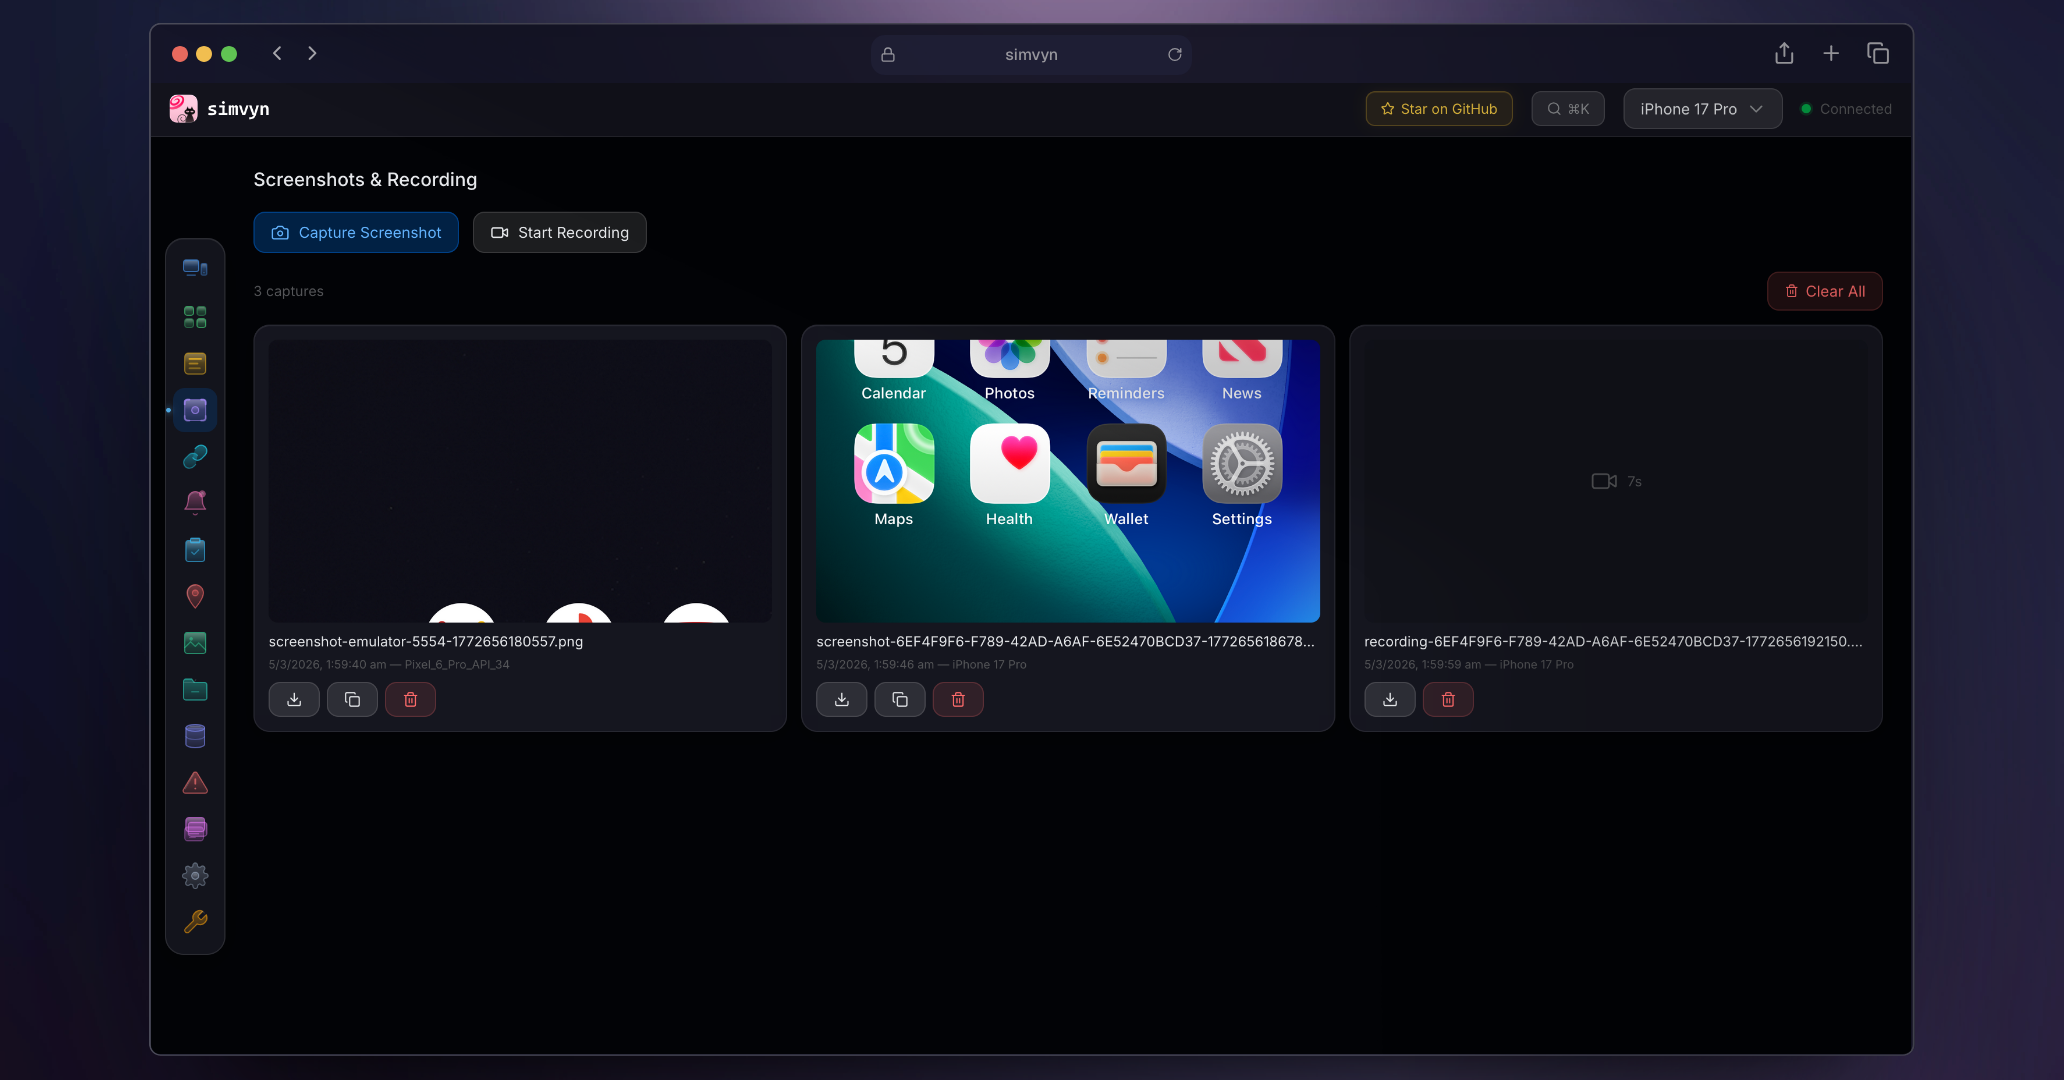 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
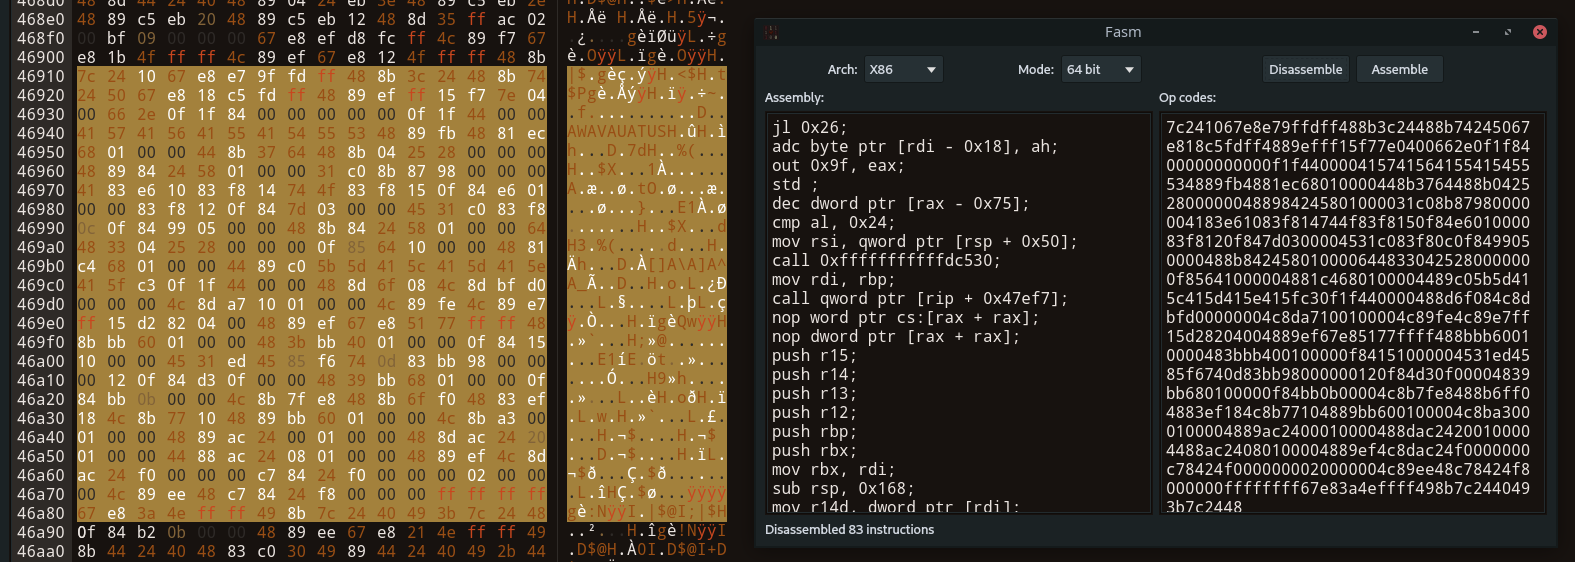 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 makelinux/cve-2015-0235-workaround
A shared library wrapper with additional checks for vulnerable functions gethostbyname2_r gethostbyname_r (GHOST vulnerability)
 dreamsmasher/inetutils-cve-2019-0053-patched-pkgbuild
A patched Arch Linux PKGBUILD to address CVE-2019-0053 (buffer overflow). Downloads and applies a (currently) unreleased patch from upstream.
 leorivass/jq-els-backport-cve-2025-48060
Backported the upstream fix for CVE-2025-48060 (heap buffer overflow in jv_string_empty) to jq 1.6.