

hacker-scripts
 narkoz/hacker-scripts
Collection of humorous shell scripts automating personal tasks: texting late-work alerts, scanning emails for keywords, faking sick days, and brewing…
general-purpose-utilitiesscripting-automation
narkoz/hacker-scriptsCollection of humorous shell scripts automating personal tasks: texting late-work alerts, scanning emails for keywords, faking sick days, and brewing…
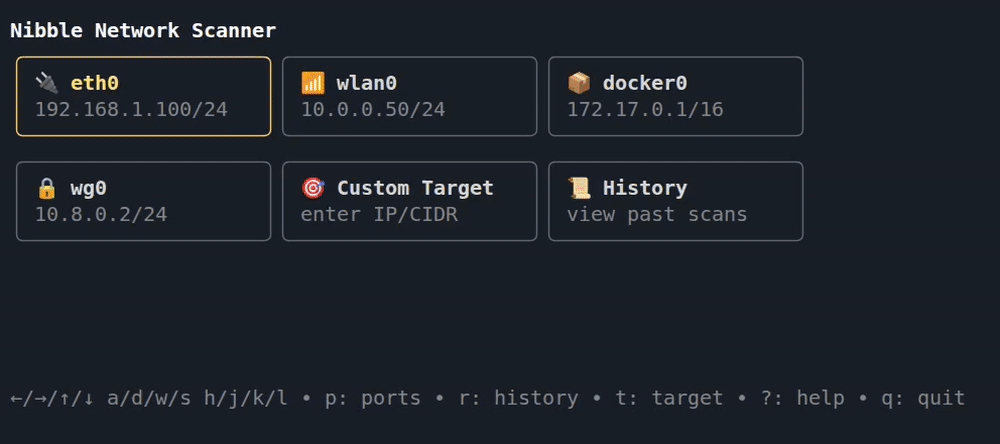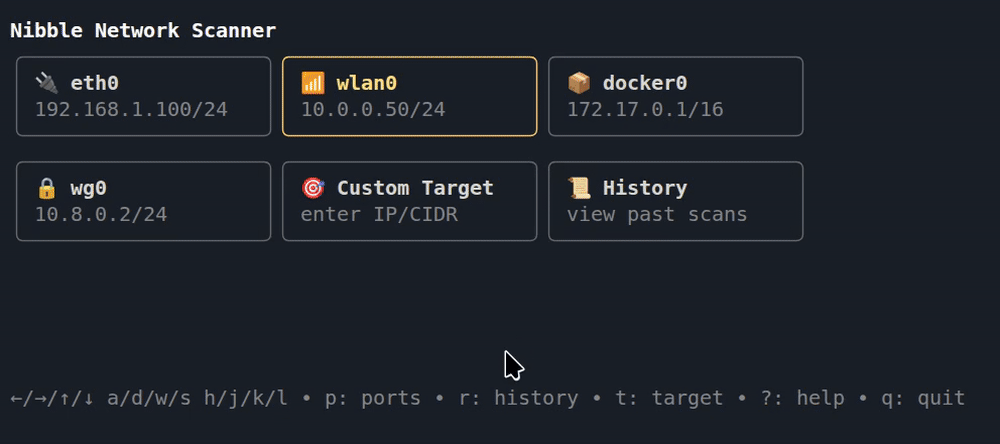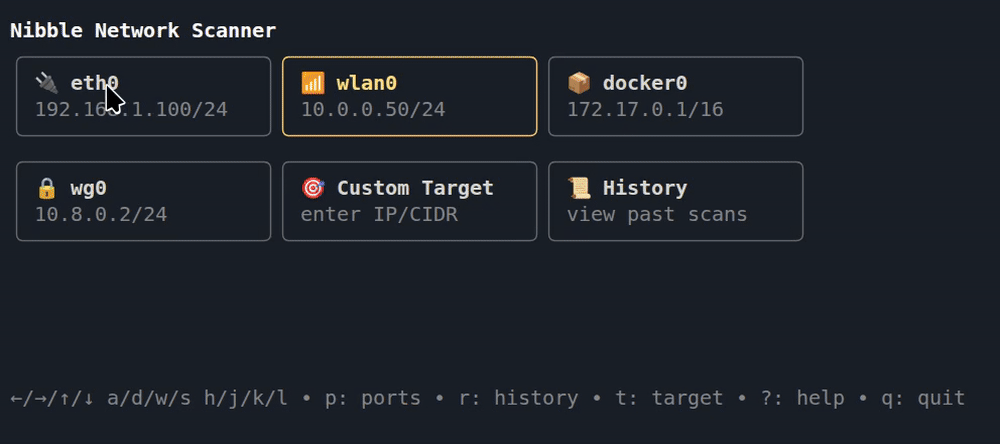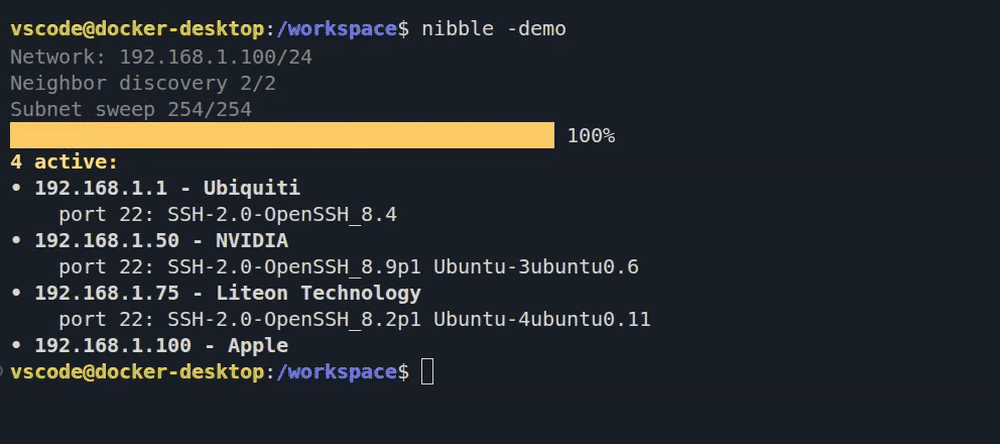 backendsystems/nibble
easy to use network scanner, with a clickable tui interface
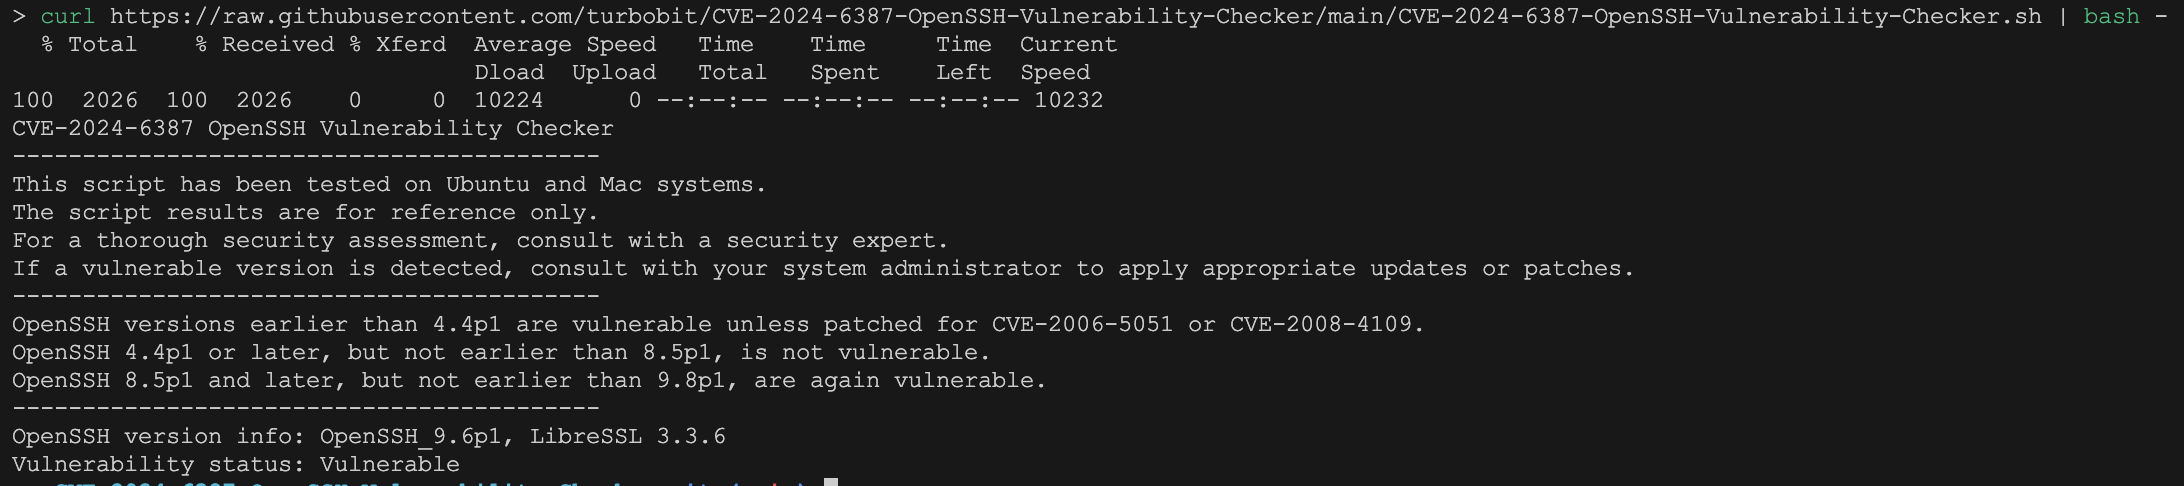 turbobit/cve-2024-6387-openssh-vulnerability-checker
Welcome to the CVE-2024-6387 OpenSSH Vulnerability Checker repository! This project offers multiple scripts to check the installed version of…
 blacksnufkin/pwnbox-kali
Bash Script to automate the process of setting up a new Kali Linux virtual machine to look a like HTB PwnBox
 rmottanet/unauthscout
UnauthScout is an OSINT (Open Source Intelligence) tool developed in Bash for passive exploration of assets on version control platforms (GitLab and…
 fractal-tess/cve-2024-3094
Bash script to detect and remediate vulnerable xz-utils versions (5.6.0/5.6.1) by replacing them with a stable, uncompromised build from source.
 sysadmin0815/fix-log4j-powershellscript
Log4Shell mitigation (CVE-2021-44228) - search and remove JNDI class from *log4j*.jar files on the system with Powershell (Windows)
 galacticquest/cve-2024-3094-detect
Bash script to detect vulnerable XZ Utils versions (CVE-2024-3094) and downgrade to a safe release, supporting multiple Linux distributions and…
 black-scorp10/url-status-checker
Async Python CLI tool for bulk URL status checking with color-coded HTTP response categorization, IP tracking, and redirect following for web service…
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
 tomnomnom/unfurl
Pull out bits of URLs provided on stdin
 tomnomnom/httprobe
Take a list of domains and probe for working HTTP and HTTPS servers
 z3apa3a/spydir
Spydir is a small utility to monitor file changes in Windows directory regardless of subdirectory and files permissions (exploits CVE-2007-0843)
 codeskipper/python-patrol
Scan for python installations on macOS, and run CVE-2015-20107.py script to report if patching is needed
 inaz2/proxy2
HTTP/HTTPS proxy in a single python script
 mustafa1986/cve-2024-3094
Python script to detect vulnerable xz-utils versions and automatically download and install a stable, patched version to mitigate CVE-2024-3094.
 sleinen/samplicator
Send copies of (UDP) datagrams to multiple receivers, with optional sampling and spoofing
 dansi/powershell-log4j-scanner
can find, analyse and patch Log4J files because of CVE-2021-44228, CVE-2021-45046