
CVE-2026-4861
 horkimhab/cve-2026-4861
CVE-2026-4861 - Draft or Todo
educationgeneral-purpose-utilitiesvulnerability-analysis
horkimhab/cve-2026-4861CVE-2026-4861 - Draft or Todo
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…
 alonisser/ralph
Ralph Wiggum plugin implementation that works after the CVE-2025-54795 security patch
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
 viruscamp/luadec
Lua Decompiler for lua 5.1 , 5.2 and 5.3
 jsonpath-plus/jsonpath
A fork of JSONPath from http://goessner.net/articles/JsonPath/
 check-spelling/check-spelling
Spelling checker action to check spelling in repositories / pull requests / commits
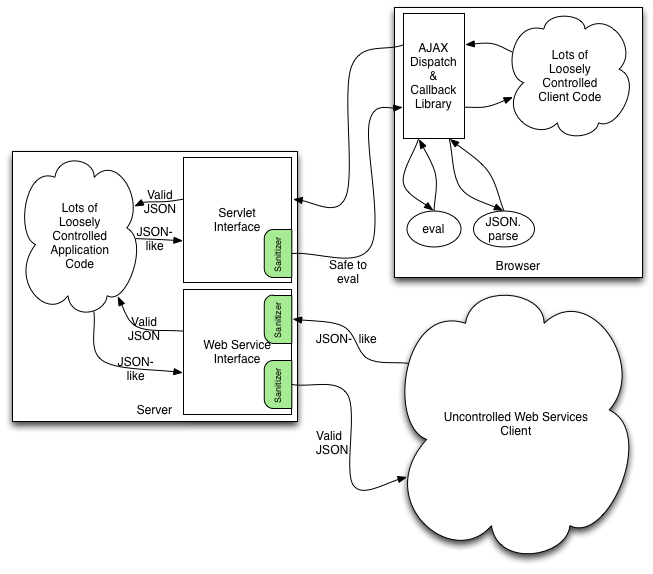 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
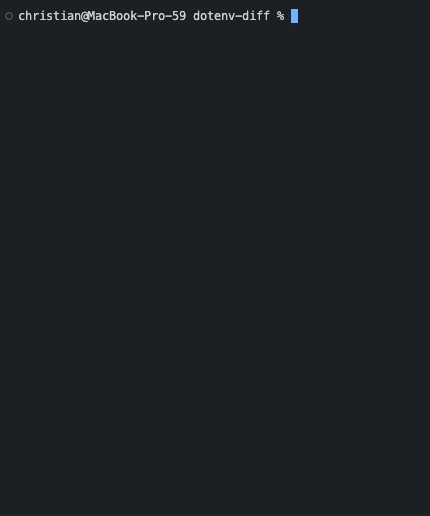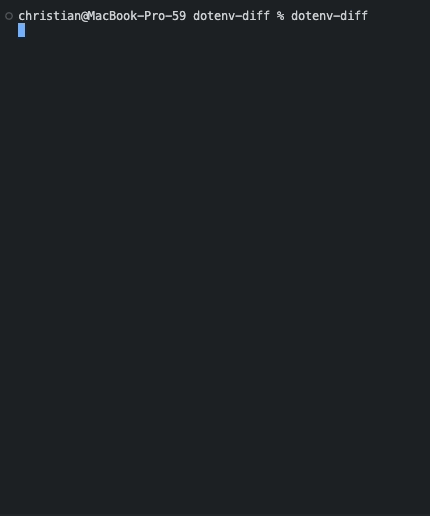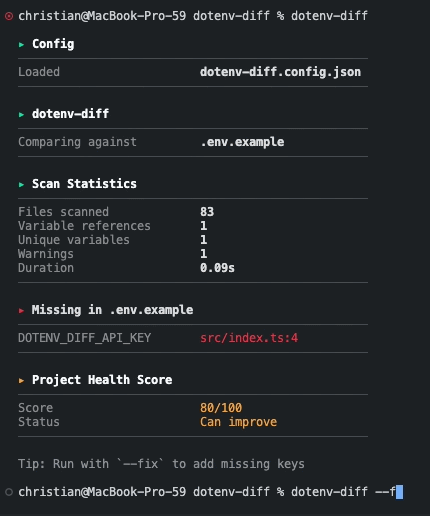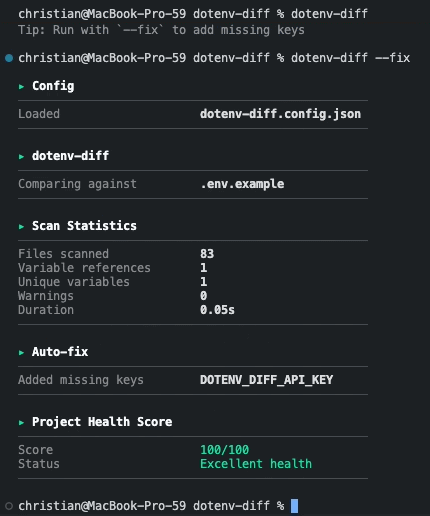 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 bio/vue-template-compiler-patched
Patched Vue 2.7.16 template compiler with fixes for CVE‑2024‑6783 and CVE-2024-9506
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…
 nzkoz/bigdecimal-segfault-fix
Provides a quick workaround for the segfault bug in Ruby (CVE-2009-1904)
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 alecasg555/safe-expr-eval
Secure expression evaluator - Drop-in replacement for expr-eval without CVE-2025-12735 vulnerability
 rmottanet/unauthscout
UnauthScout is an OSINT (Open Source Intelligence) tool developed in Bash for passive exploration of assets on version control platforms (GitLab and…
 lauxjpn/corruptqueryaccessworkaround
The latest workaround for the "Query is corrupt" error introduced with CVE-2019-1402