
ZX-DDoS
 mrgoofydev/zx-ddos
Python-based DDoS stress testing tool for educational and authorized network security evaluation, supporting configurable workers and request counts.
educationgeneral-purpose-utilitiesnetwork-security+3
51
mrgoofydev/zx-ddosPython-based DDoS stress testing tool for educational and authorized network security evaluation, supporting configurable workers and request counts.
 horkimhab/cve-2026-4861
CVE-2026-4861 - Draft or Todo
 reconinfosec/web-traffic-generator
A quick and dirty HTTP/S "organic" traffic generator.
 blacksnufkin/pwnbox-kali
Bash Script to automate the process of setting up a new Kali Linux virtual machine to look a like HTB PwnBox
 shoucheng3/jmrozanec__cron-utils_cve-2021-41269_9-1-5
Java library for parsing, validating, migrating, and describing cron expressions with support for multiple formats (Unix, Quartz, Spring) and…
 shoucheng3/jlangch__venice_cve-2022-36007_1-10-16
Sandboxed Lisp dialect for the JVM with immutable data structures, macros, and over 900 core functions. Ideal for safe scripting, automation, and…
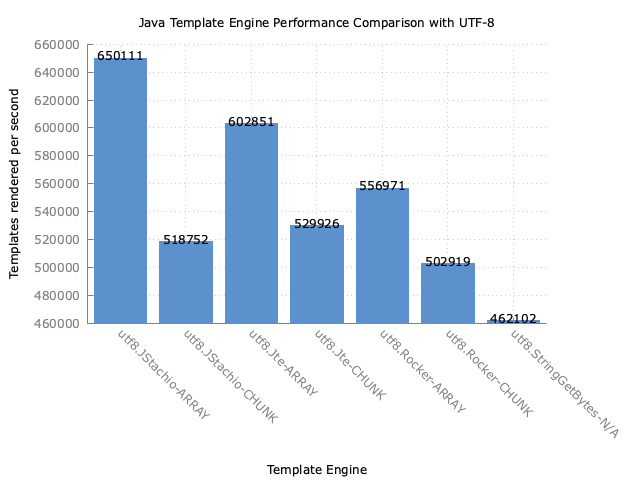 shoucheng3/jstachio__jstachio_cve-2023-33962_1-0-0
Type-safe Java Mustache templating engine with compile-time template validation, static value binding, and extensible escaping for HTML and other…
 shoucheng3/xwiki__xwiki-rendering_cve-2023-32070_14-5
Generic rendering system converting wiki syntax, HTML, and other formats into XHTML. Part of the XWiki platform, providing a flexible and extensible…
 koupah/mc-log4j-patcher
A singular file to protect as many Minecraft servers and clients as possible from the Log4j exploit (CVE-2021-44228).
 shogo82148/fix-cve-2017-1000117
Test repository for verifying Git's CVE-2017-1000117 vulnerability and upgrading Git versions. Clone with --recursive to check safety.
 ninedeadeyes/s.p.a.r.k--standard-python-ascii-rpg-kit-
Light Weight 2d Ascii RPG Python Game Engine
 loserlab/bigint-buffer-safe
Safe, pure-JS drop-in replacement for bigint-buffer. Fixes CVE-2025-3194 (CVSS 7.5). Zero dependencies, no native bindings.
 shoucheng3/apache__uima-uimaj_cve-2022-32287_3-3-0
Java SDK for building analytics pipelines that process and enrich unstructured text data with annotations, type systems, and modular analysis engines.

 notasithlord/peerd
The first AI agent harness native to the browser. A browser extension that runs a full agent loop where you already work: it drives your tabs, spins…
 homjxi0e/cve-2017-4490-
Experimental proof-of-concept demonstrating .bashrc manipulation using figlet to create terminal persistence and privilege-escalation vulnerabilities…
 hackingetico21/revisaxzutils
Script en bash para revisar si tienes la vulnerabilidad CVE-2024-3094.