
CVE-2010-1205
 mk219533/cve-2010-1205
sample exploit of buffer overflow in libpng
binary-exploitationeducationexploitation+2
mk219533/cve-2010-1205sample exploit of buffer overflow in libpng
 jgajek/killasa
Exploit tool for CVE-2016-1287 that tests Cisco ASA devices by sending crafted IKEv2 fragments with invalid lengths to trigger denial of service.
 rog3rsm1th/frelatage
Coverage-based fuzzer for python applications
 manhndd/cve-2019-19012
Integer overflow in Oniguruma
 tarantula-team/cve-2019-19012
An integer overflow in the search_in_range function in regexec.c in Oniguruma 6.x before 6.9.4_rc2 leads to an out-of-bounds read
 doyensec/regexploit
Find regular expressions which are vulnerable to ReDoS (Regular Expression Denial of Service)
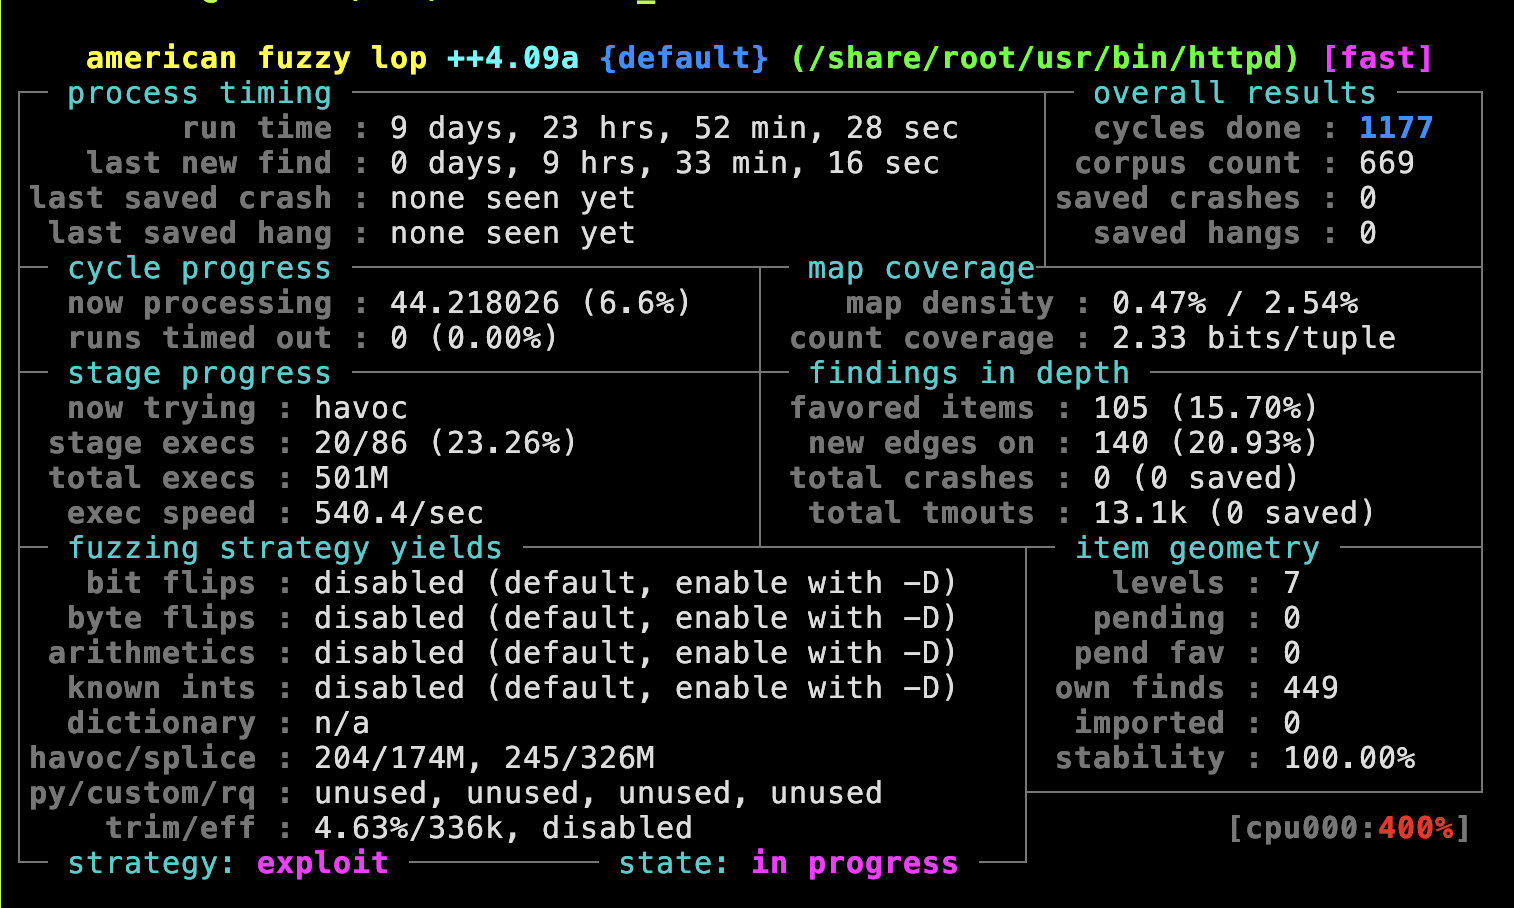 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
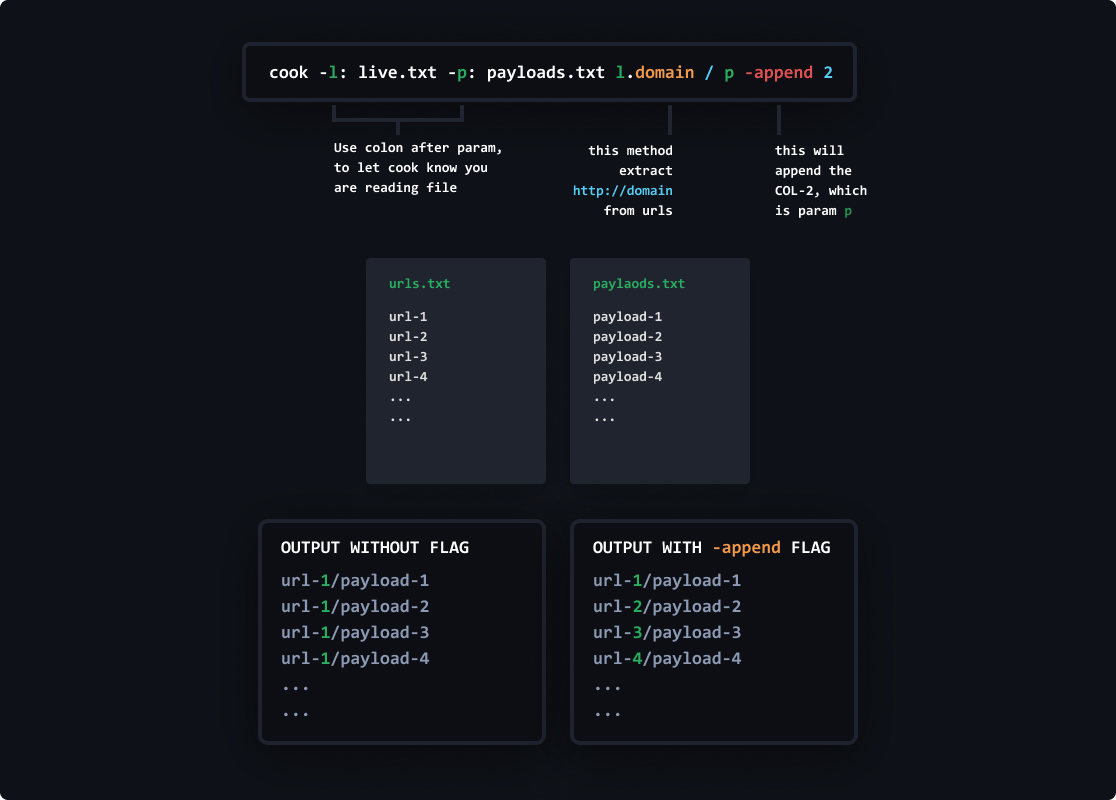 glitchedgitz/cook
A wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.
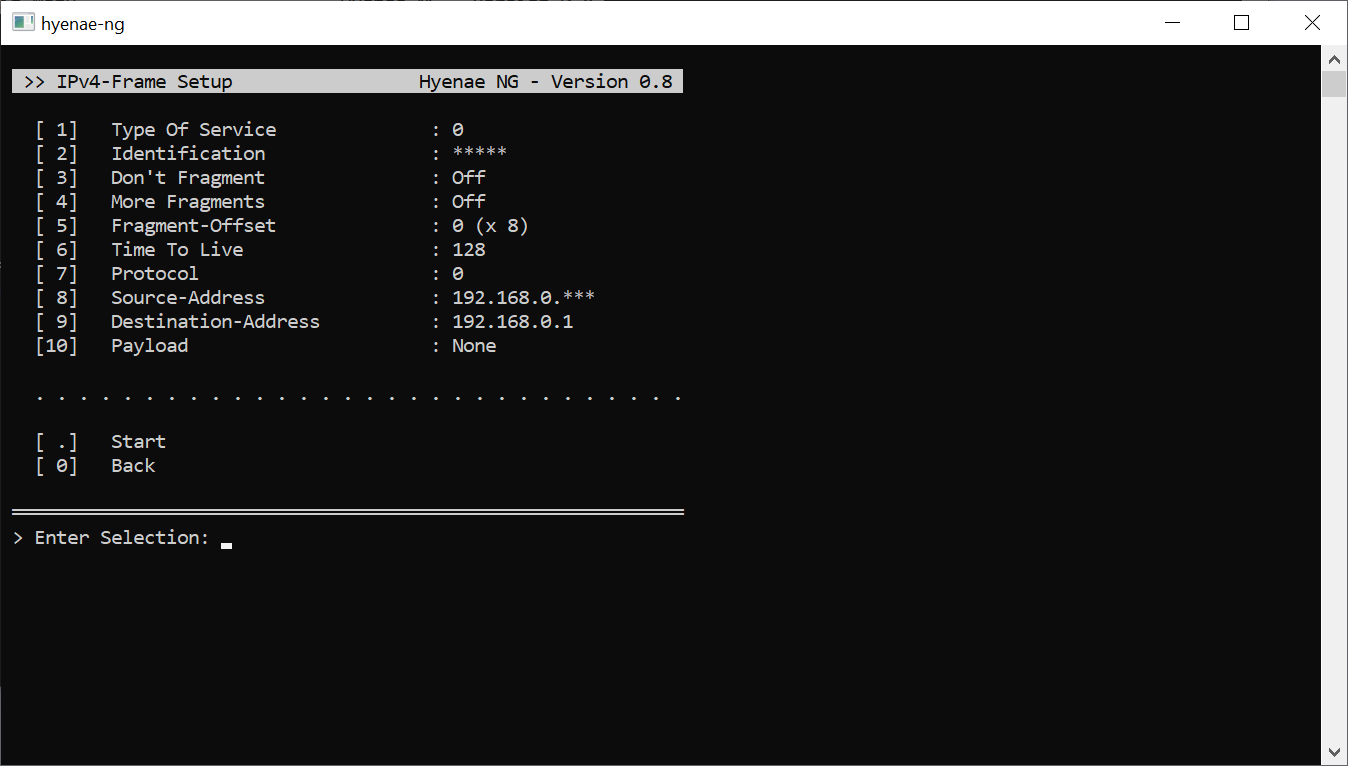 r-richter/hyenae-ng
Cross-platform network packet generator with full layer spoofing, pattern-based address randomization, and flood detection evasion for stress-testing…
 pfg666/dtls-fuzzer
dtls-fuzzer is a protocol-state-fuzzer for DTLS server implementations.
 thephykon/cve-2025-53367-poc
A simple POC of the CVE-2025-53367, creating a .djvu-file which triggers an OOB-write in the heap
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 caoweiquan322/notenough
This tool calculates tricky canonical huffman histogram for CVE-2023-4863.
 noxxi/mime-is-broken
Test cases for broken MIME and tools to generate and process these
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 dsecuredcom/ffufpostprocessing
Golang tool which helps dropping the irrelevant entries from your ffuf result file.
 gitlab-org/security-products/protocol-fuzzer-ce
This is the community edition of GitLab's protocol fuzzing framework. This framework is based on Peach Fuzzer Professional with some features removed.