
nili
 niloofarkheirkhah/nili
Nili is a Tool for Network Scan, Man in the Middle, Protocol Reverse Engineering and Fuzzing.
fuzzingnetwork-mappingpacket-sniffing-analysis+1
2198 years ago
niloofarkheirkhah/niliNili is a Tool for Network Scan, Man in the Middle, Protocol Reverse Engineering and Fuzzing.
 0xinfection/logmepwn
A fully automated, reliable, super-fast, scanning and validation toolkit for the Log4J RCE CVE-2021-44228 vulnerability.
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 phra/rustbuster
A Comprehensive Web Fuzzer and Content Discovery Tool
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 henshin/filebuster
An extremely fast and flexible web fuzzer
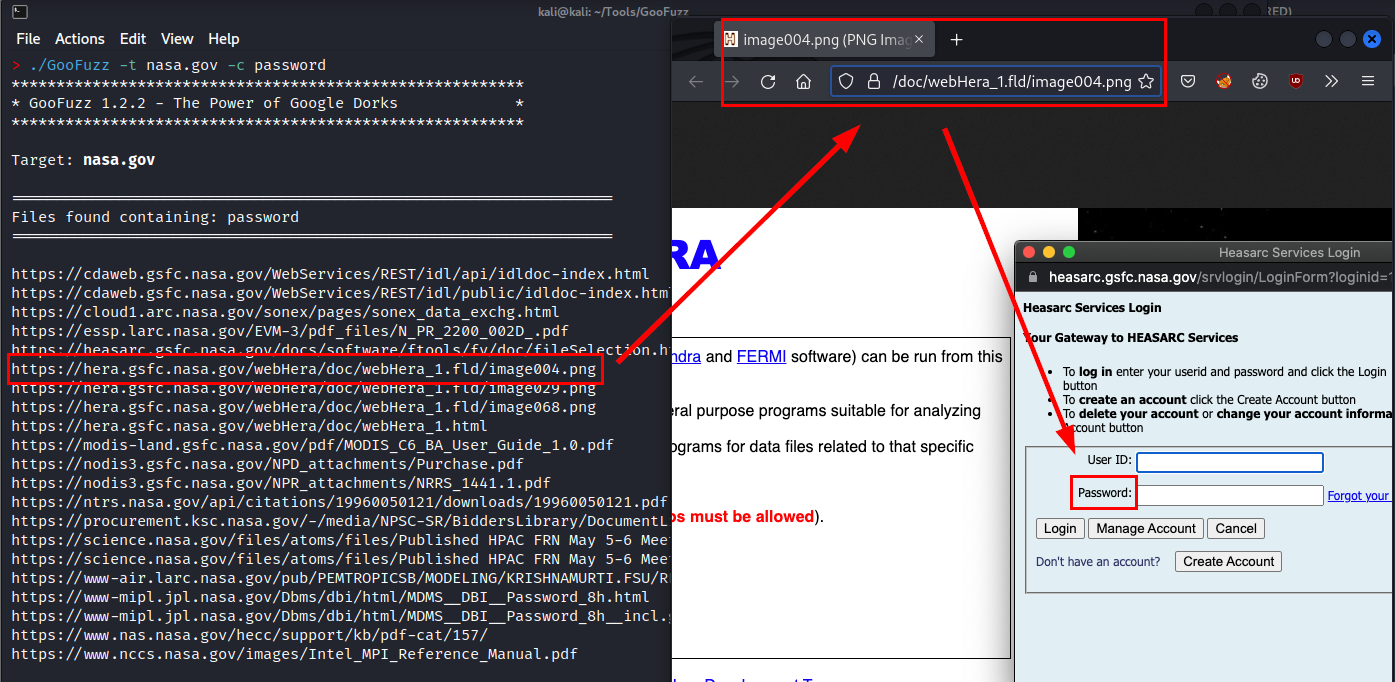 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…
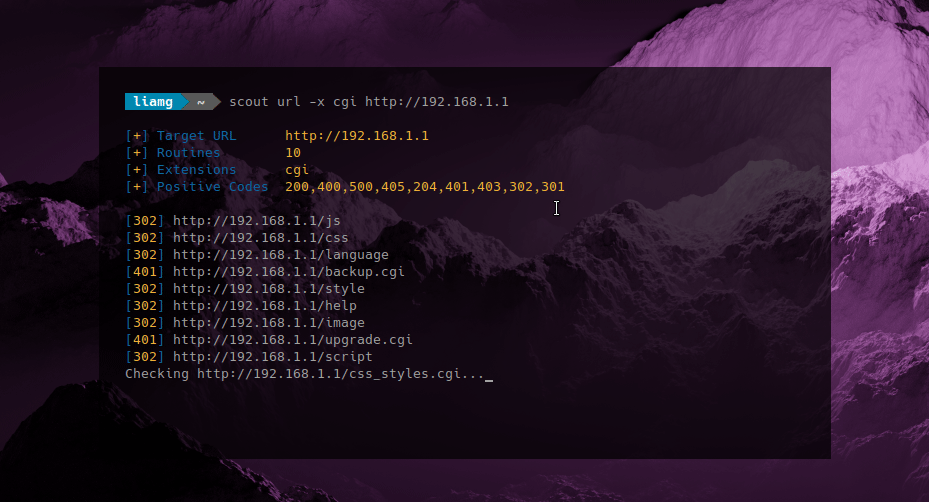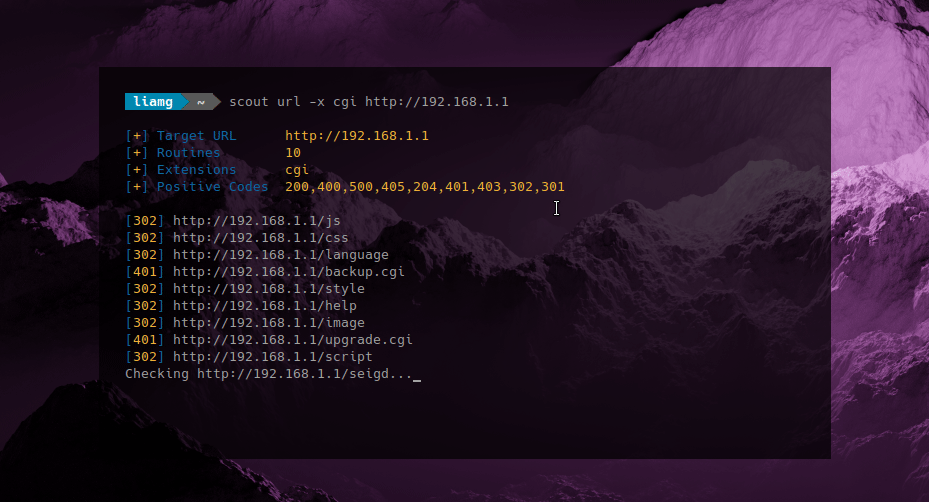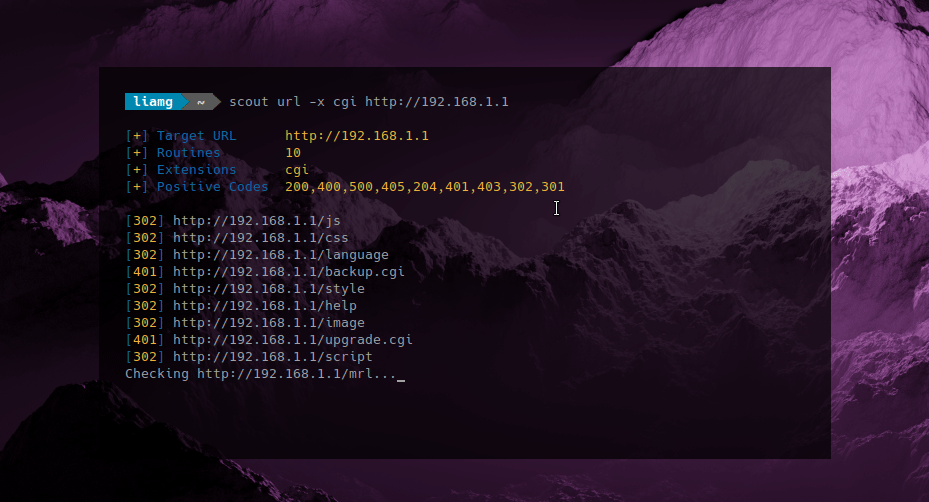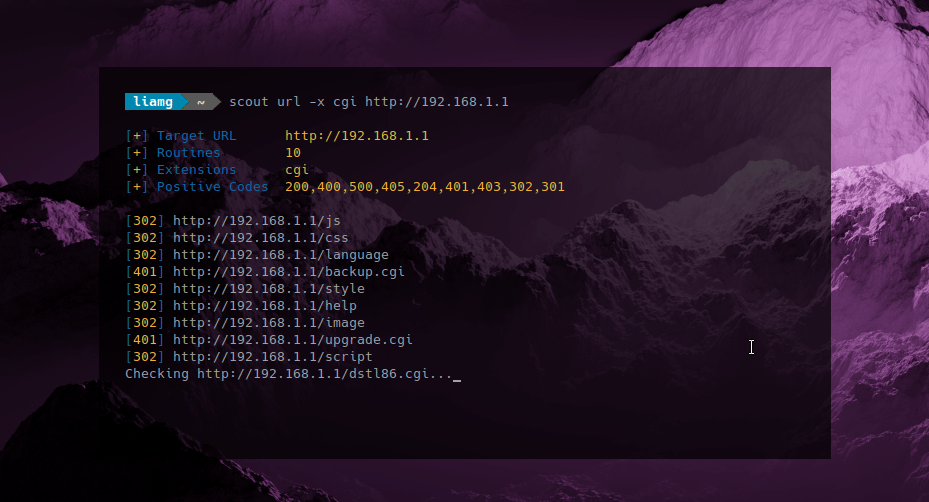 liamg/scout
🔭 Lightweight URL fuzzer and spider: Discover a web server's undisclosed files, directories and VHOSTs
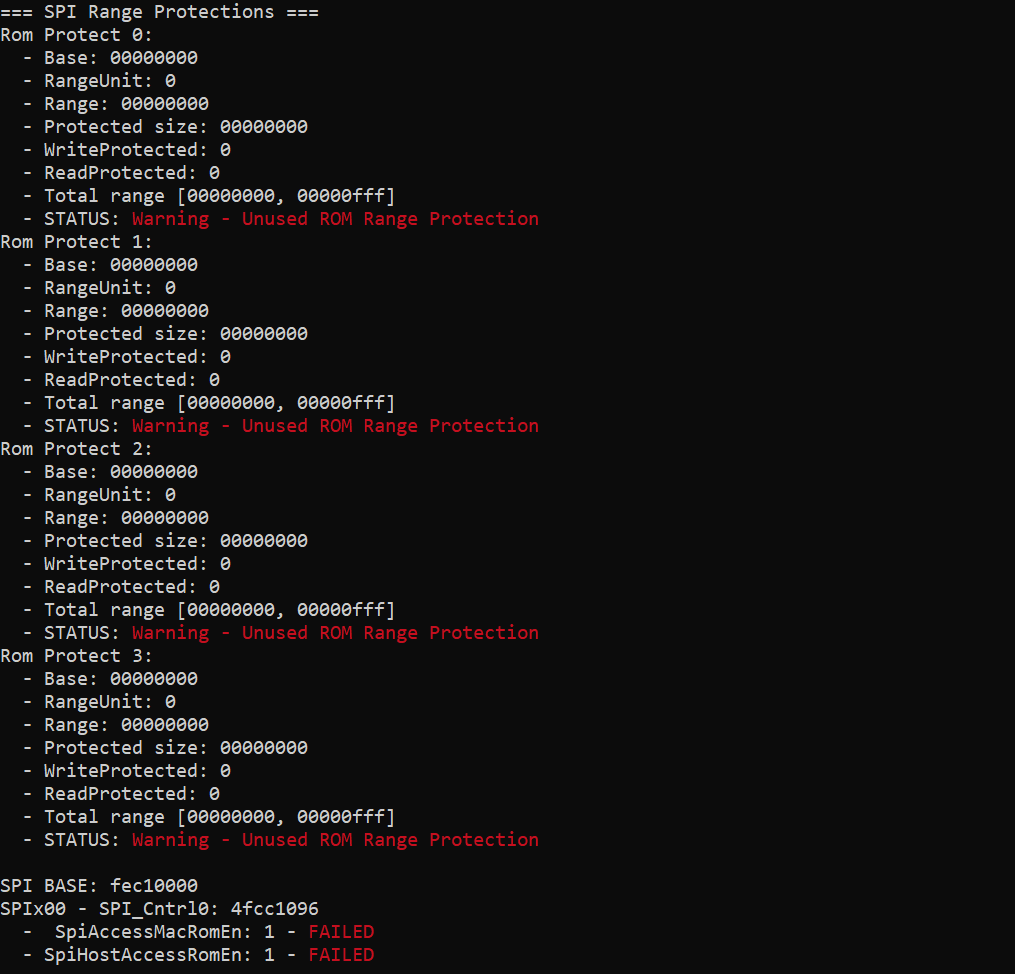 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
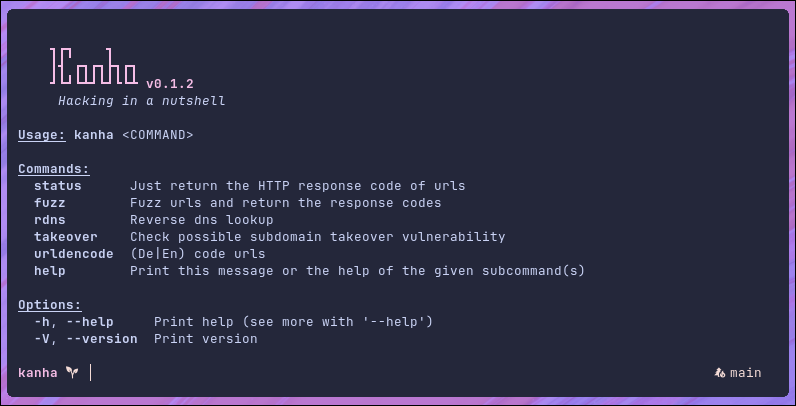 pwnwriter/kanha
🦚 A web-app pentesting suite written in rust .
 rxerium/bug-bounty-tools
A BASH Script to automate the installation of the most popular bug bounty tools
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…