
nDPI
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
dns-analysisfuzzingintrusion-detection+5
ntop/ndpiOpen Source Deep Packet Inspection Software Toolkit
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
 0xsobky/hackvault
A container repository for my public web hacks!
 phra/rustbuster
A Comprehensive Web Fuzzer and Content Discovery Tool
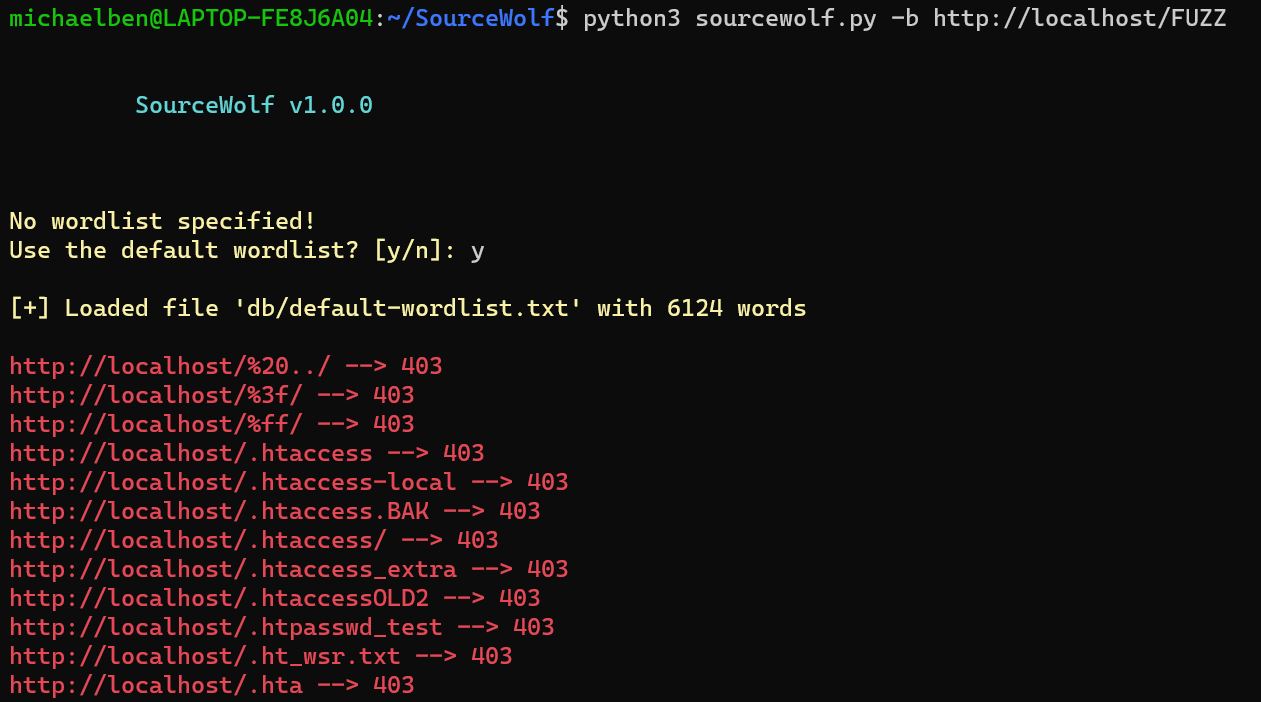 ksharinarayanan/sourcewolf
Amazingly fast response crawler to find juicy stuff in the source code! 😎🔥
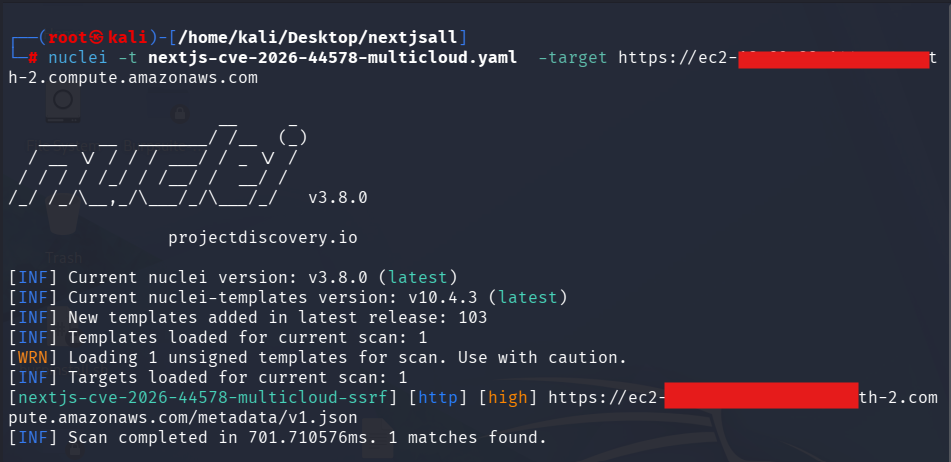 love07oj/nextjs-cve-2026-44578
Nuclei templates for detecting CVE-2026-44578 (Next.js WebSocket Upgrade SSRF) with multi-cloud metadata validation, Next.js fingerprinting, and…
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…
 syaifulandy/cve-2024-38475
CVE-2024-38475 Scanner using FFUF + Seclists
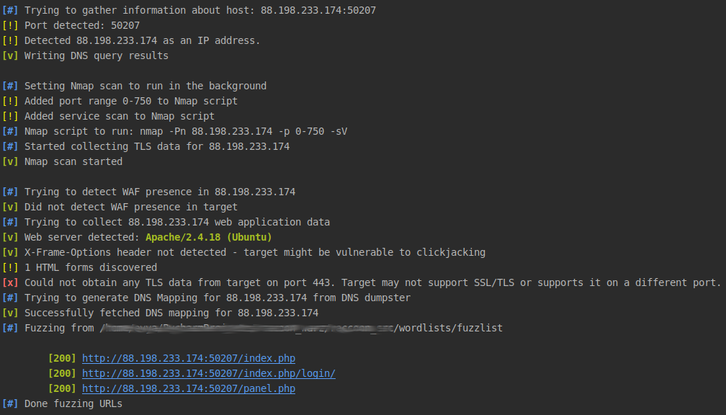 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.

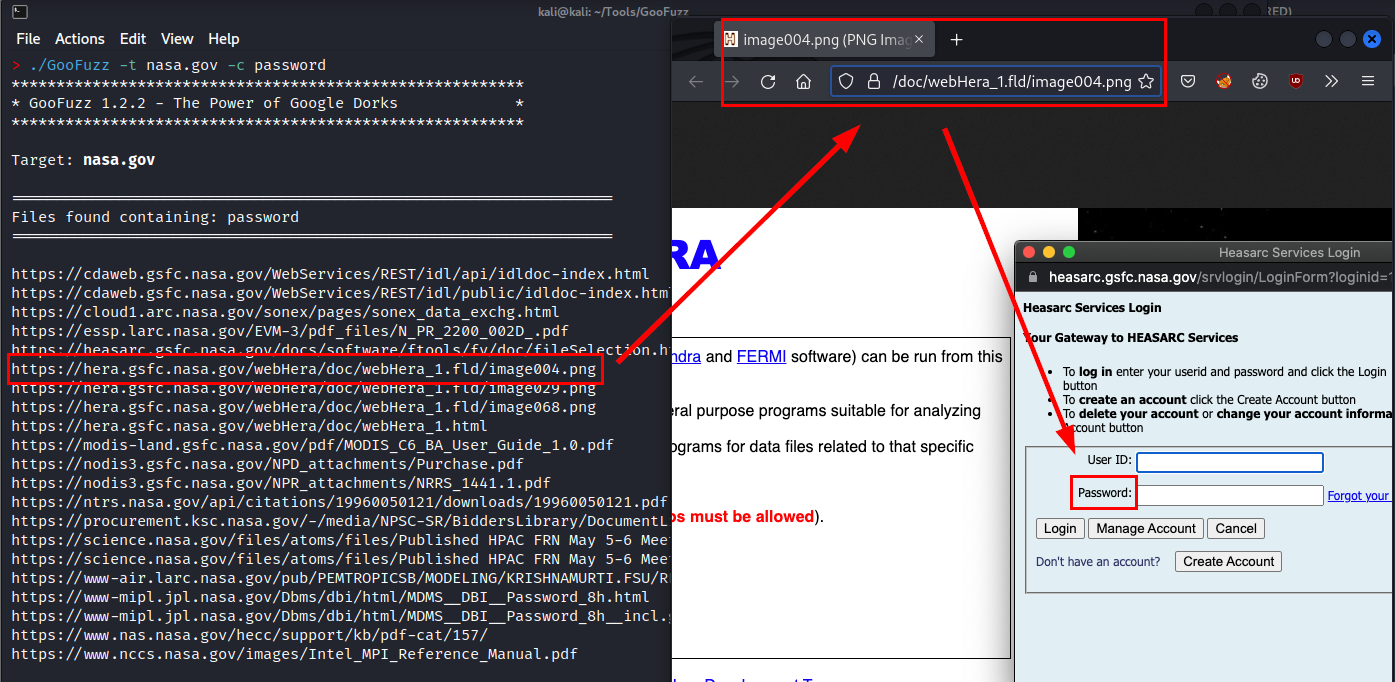 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
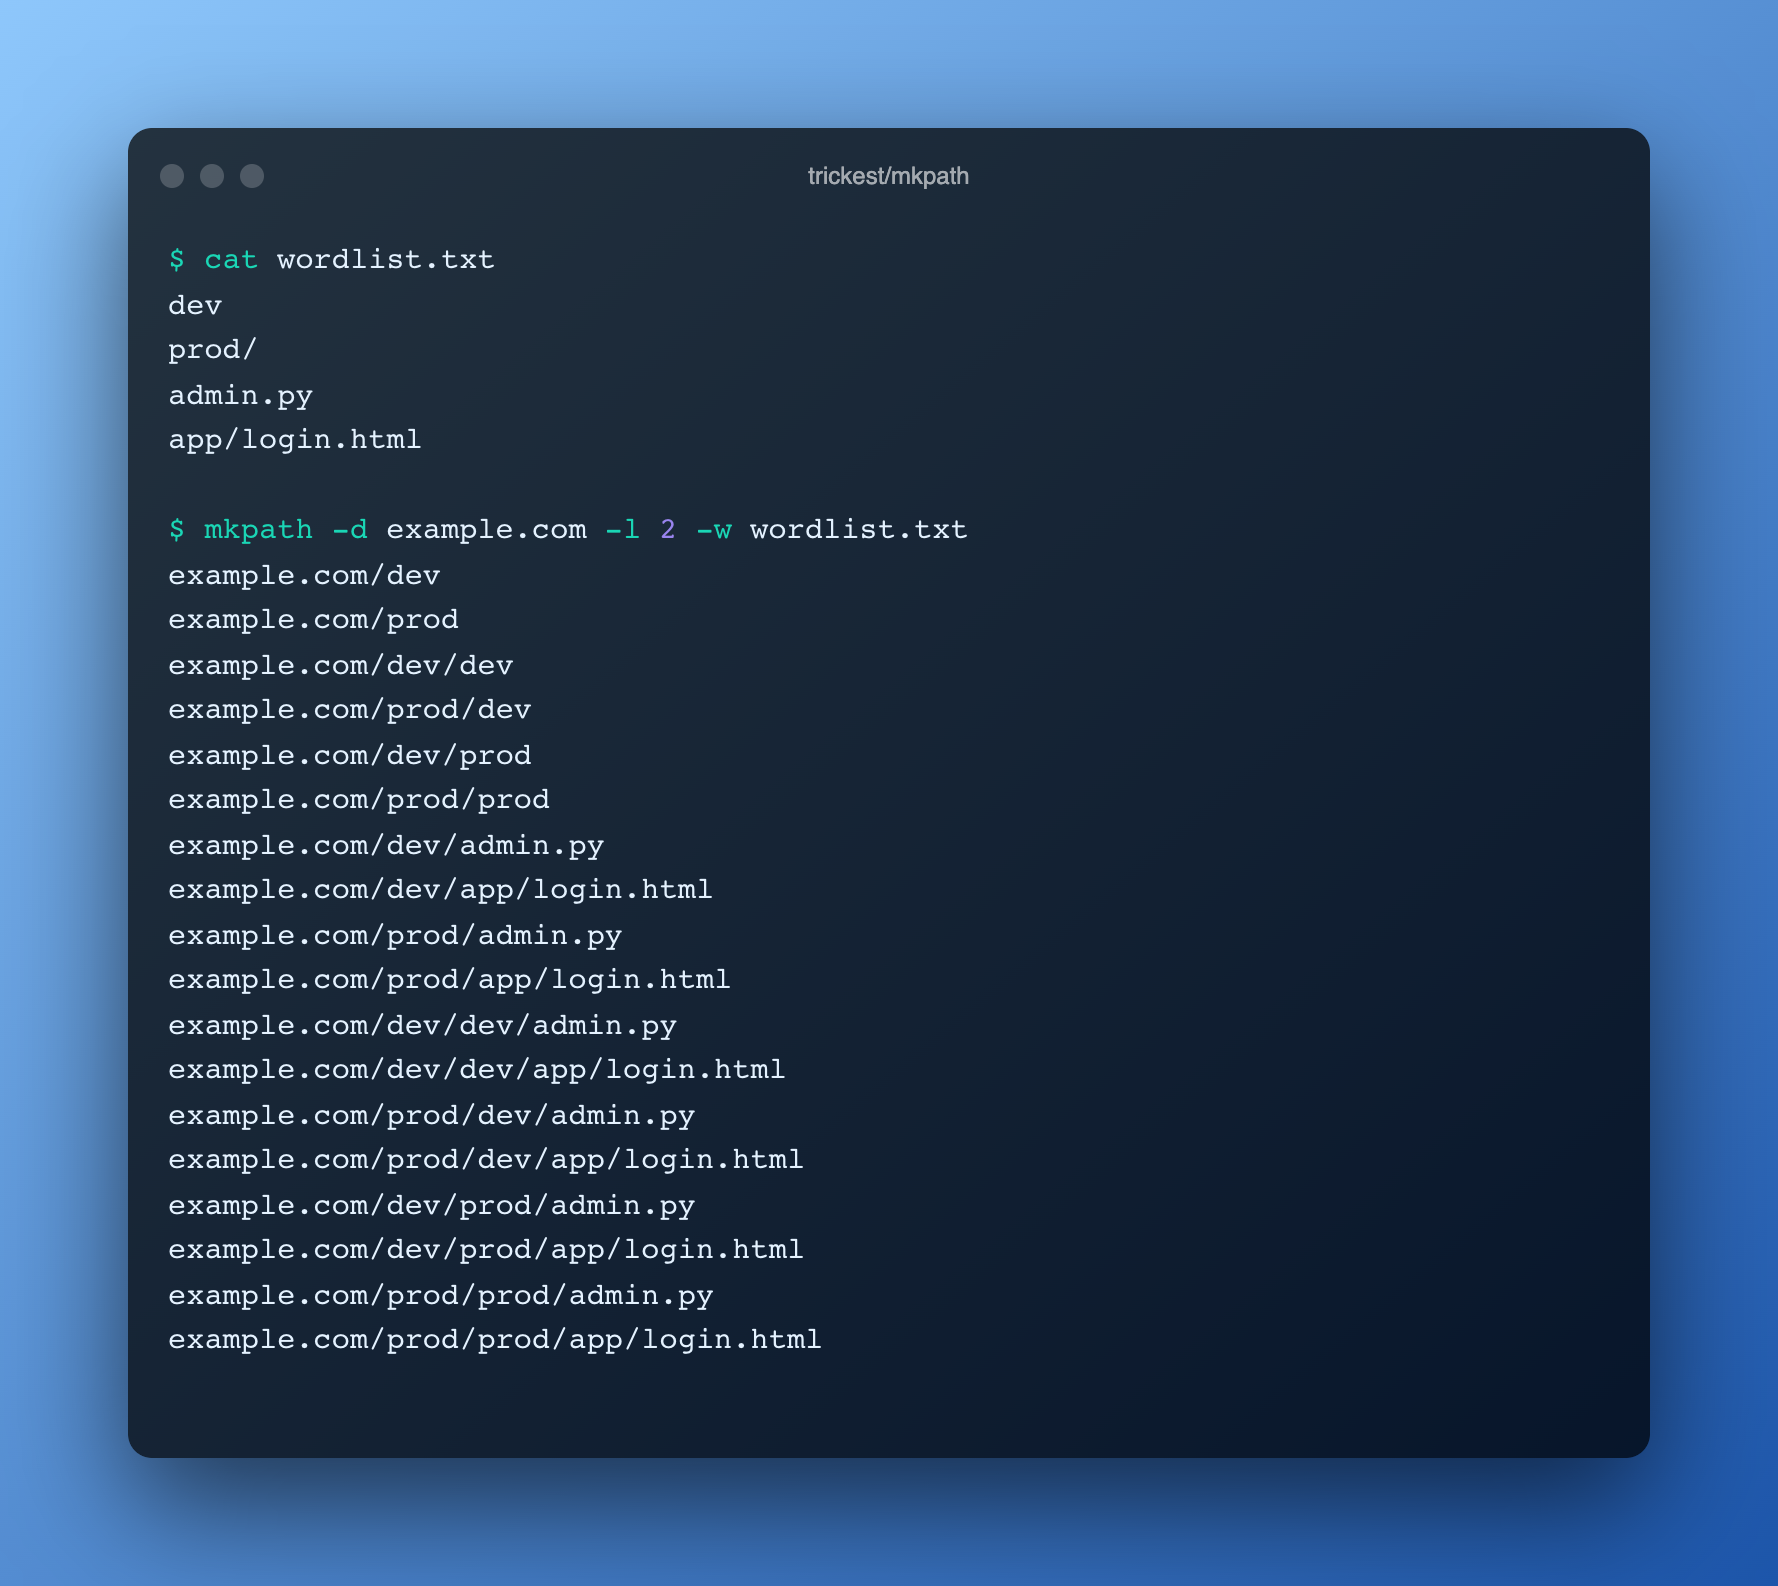 trickest/mkpath
Make URL path combinations using a wordlist
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…