


 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
 frizb/wordlistgen
Super Simple Python Word List Generator for Fuzzing and Brute Forcing in Python
 tin-z/cve-2021-20294-poc
Simple CVE-2021-20294 poc
 batchmcnulty/malbait
Simple TCP/UDP honeypot implemented in Perl
 nexxus67/cve-2010-1938
A simple Python script to test an off-by-one vulnerability in the OPIE library (CVE-2010-1938). This vulnerability affects certain FTP servers and…
 antogit-sys/cve-2018-7449
simple Python exploit using CVE-2018-7449 on embOS/IP FTP Server v3.22
 therook/audiocaptchabypass-cve-2008-2019
Exploit for CVE-2008-2019 bypassing audio captcha in Simple Machines Forum 1.1.4 using hamming distance and levenshtein distance to compare PCM audio…
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 liviuptr/cve-2014-0075_poc
This is a simple PoC written n python that demonstrates the DoS through integer overflow.
 thephykon/cve-2025-53367-poc
A simple POC of the CVE-2025-53367, creating a .djvu-file which triggers an OOB-write in the heap
 ubuntustrike/struts_rest_rce_fuzz-cve-2017-9805-
Simple python script to fuzz site for CVE-2017-9805
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
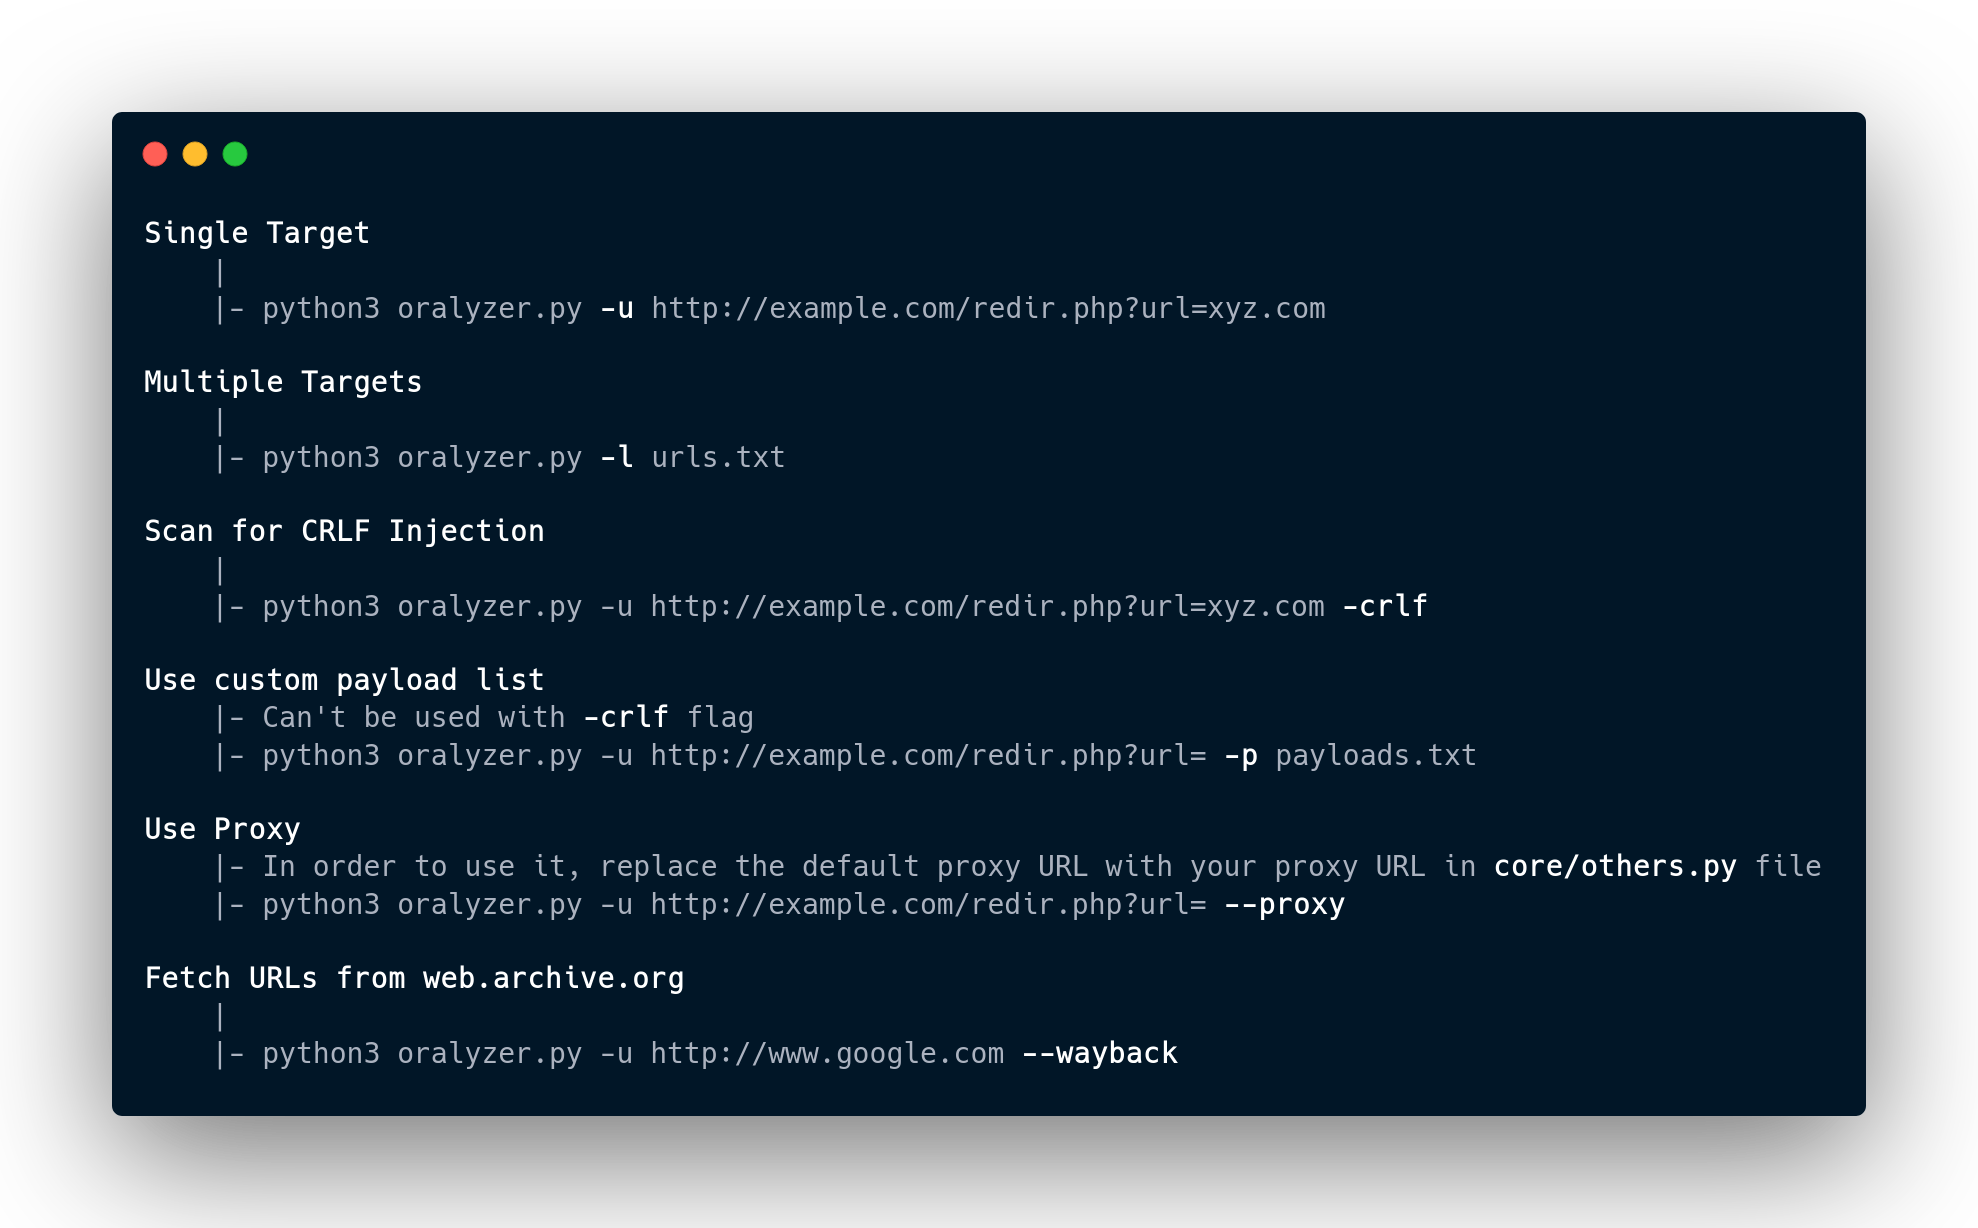 r0075h3ll/oralyzer
Python-based open redirect vulnerability scanner that fuzzes URLs to detect header, JavaScript, and meta tag-based redirects, with integrated…
 meliht/mr.sip
SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone.
 osirislab/awesome-rust-security
Curated list of awesome projects and resources related to Rust and computer security
