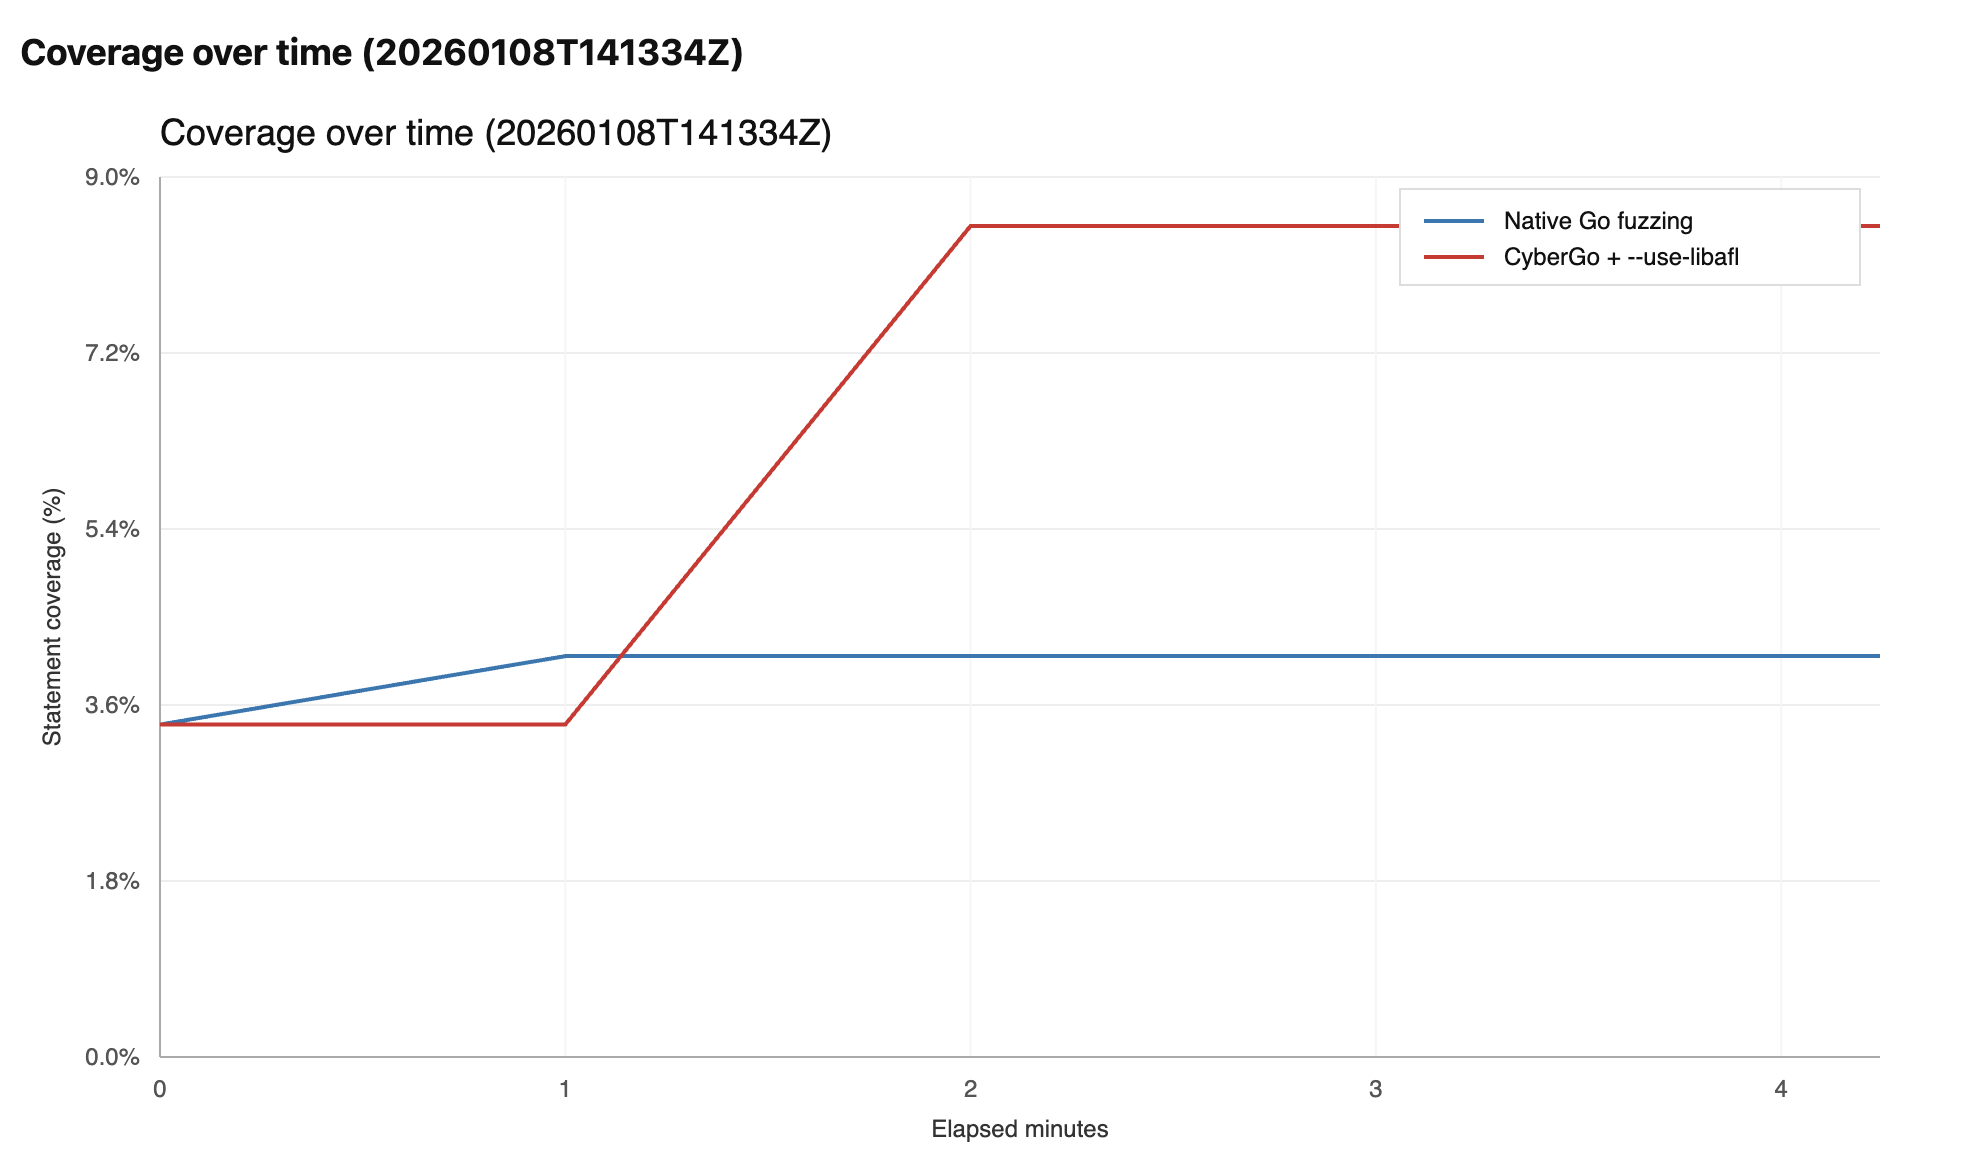
 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
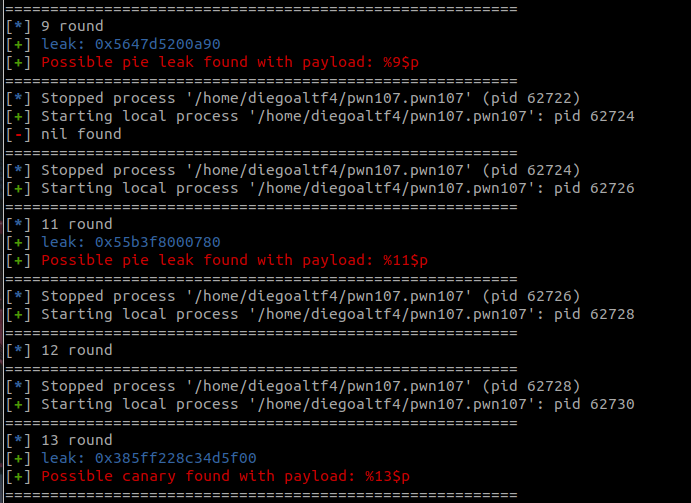 diego-altf4/glufs
Automated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…
 maherazzouzi/cve-2022-36163
Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 dwisiswant0/cve-2025-46819
Proof-of-concept exploit for CVE-2025-46819, a Redis Lua long-string delimiter out-of-bounds read, demonstrating a crash via malformed input.
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 tarantula-team/cve-2019-19203
An issue was discovered in Oniguruma 6.x before 6.9.4_rc2. In the function gb18030_mbc_enc_len in file gb18030.c, a UChar pointer is dereferenced…