

theftfuzzer
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
fuzzingmisconfigurationvulnerability-scanners+1
3197 years ago
lc/theftfuzzerTheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
 nccgroup/cecster
A GUI-based tool to perform security testing against the HDMI CEC (Consumer Electronics Control) and HEC (HDMI Ethernet Channel) protocols
 zhangzhuosjtu/web3bugs
Demystifying Exploitable Bugs in Smart Contracts
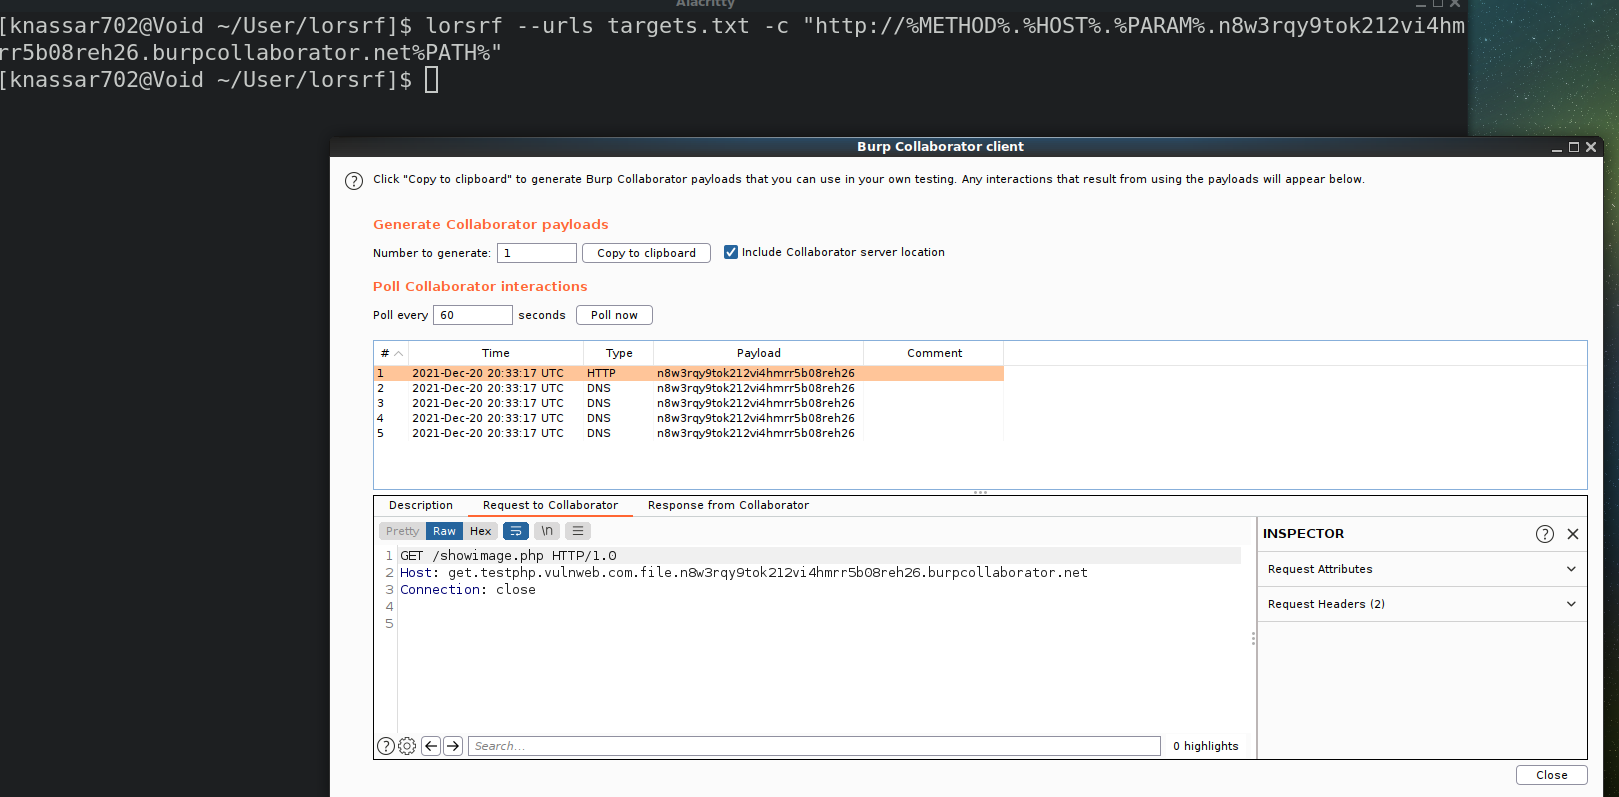 mindpatch/lorsrf
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 alphaseclab/all-my-collection-repos
All Security Resource Collections Repos That I Published.
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 aeyesec/cve-2024-27316_poc
Proof-of-concept exploit for CVE-2024-27316, an HTTP/2 CONTINUATION flood vulnerability in Apache httpd, demonstrating resource exhaustion via…
 lottiedeyan/cve20265172poc
CVE-2026-5172: buffer overflow in extract_addresses() on crafted resource record PoC
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide