

yakit
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
command-and-controlexploit-frameworksfuzzing+9
7.7k
yaklang/yakitAll-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
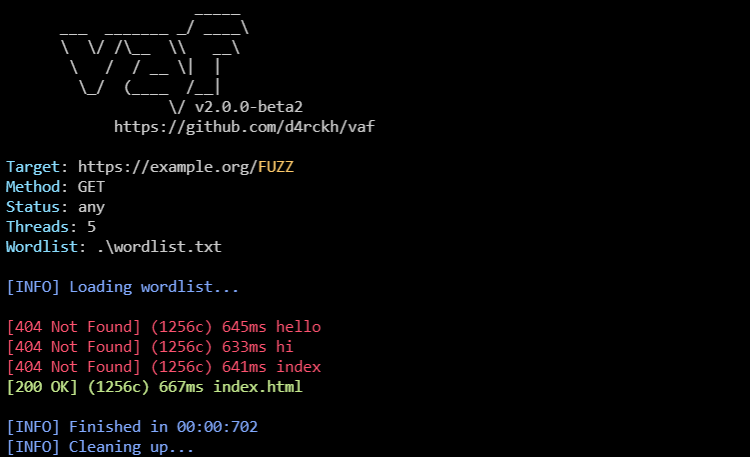 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
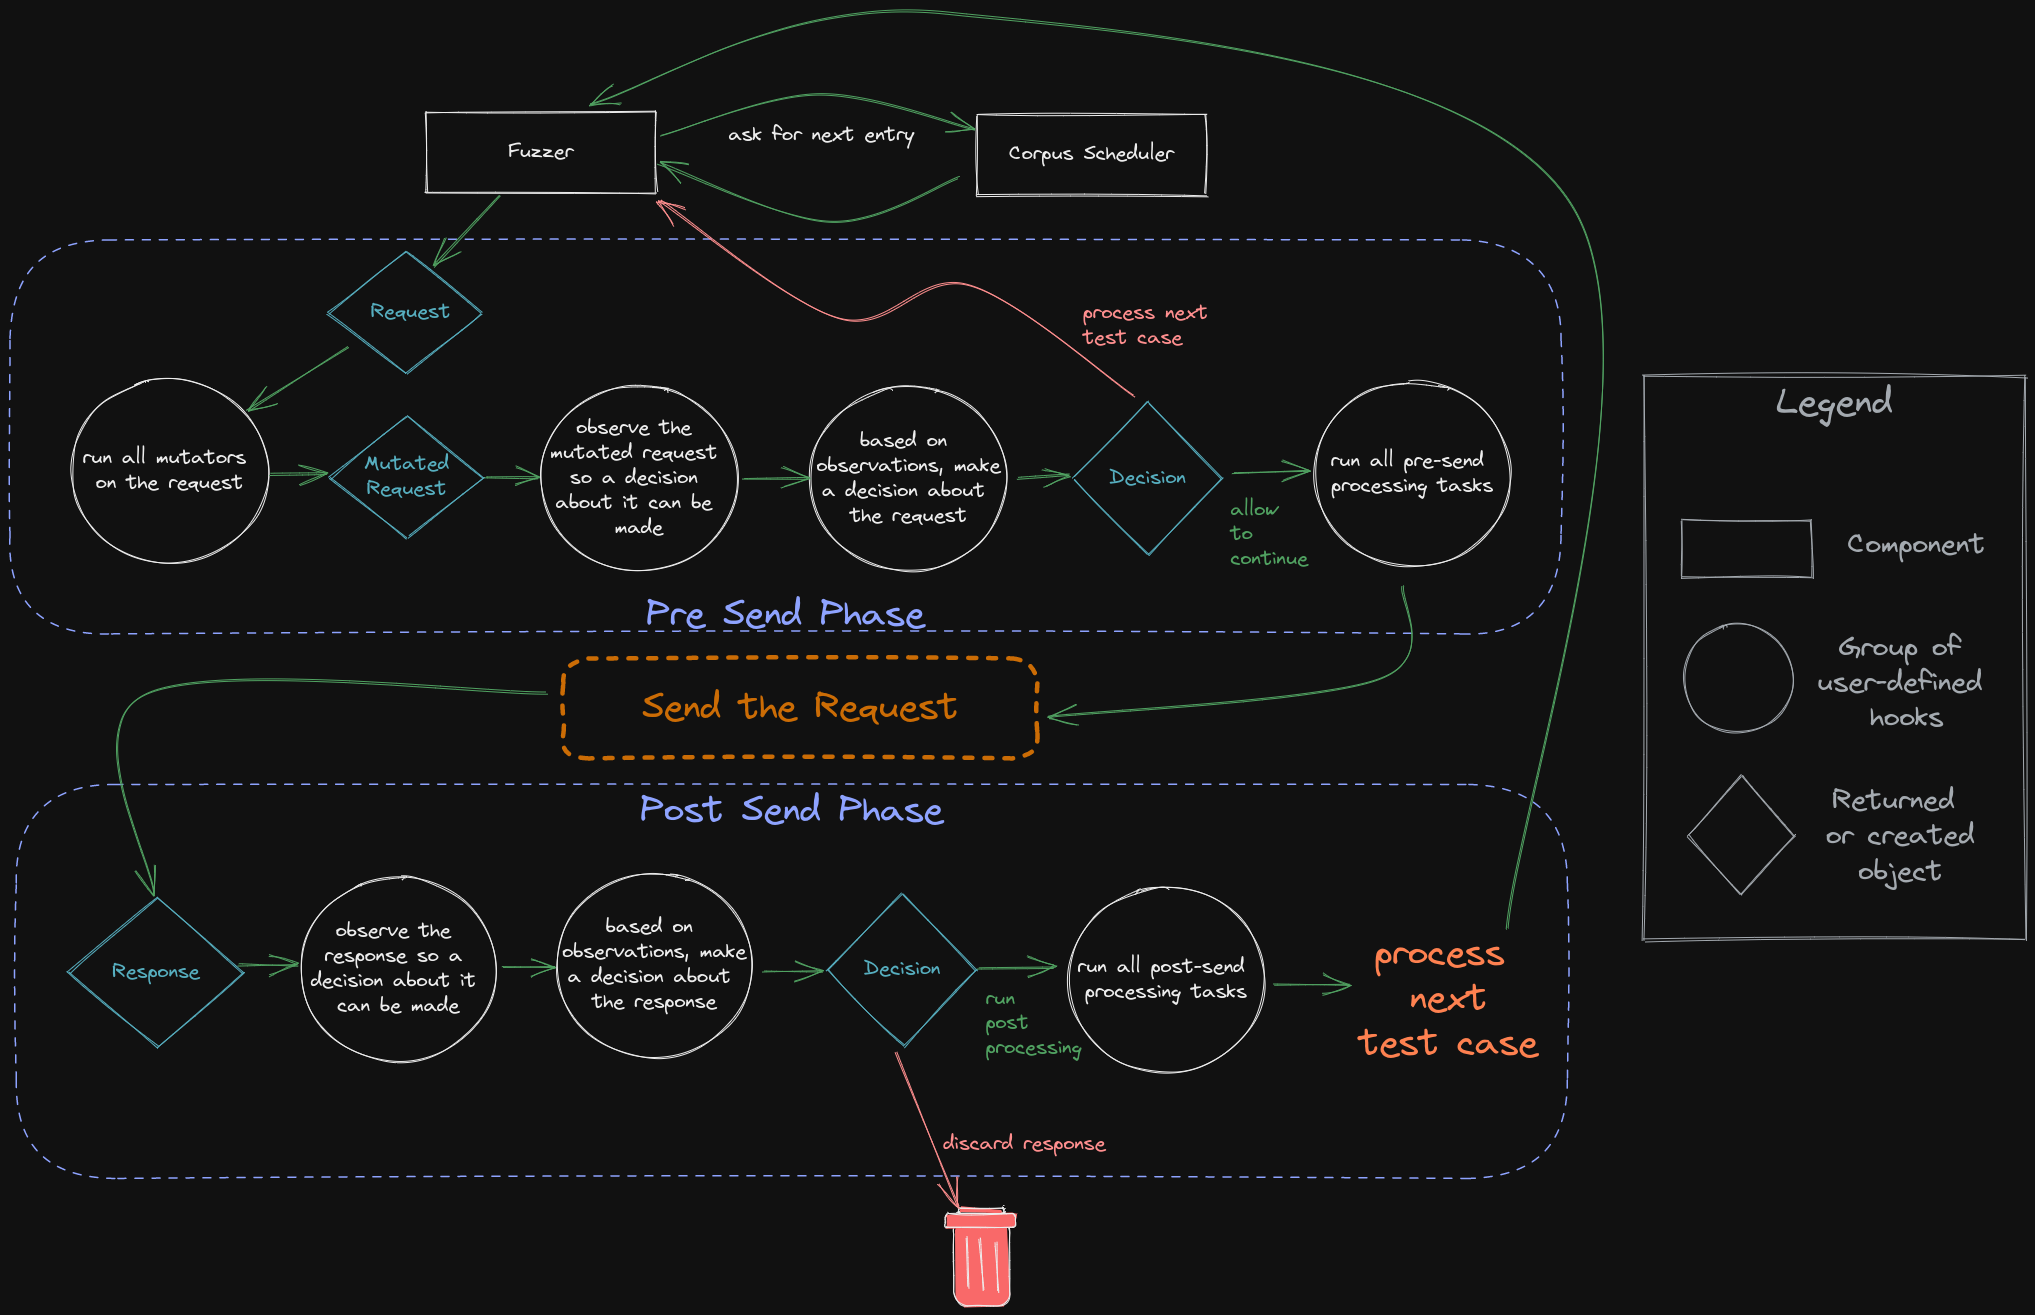 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 nccgroup/wssip
Application for capturing, modifying and sending custom WebSocket data from client to server and vice versa.
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 ttdennis/fpicker
Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 dbrugman/cve-2023-38545-poc
Proof-of-concept for CVE-2023-38545 heap buffer overflow in curl's SOCKS5 proxy handling, demonstrating exploitation via rate-limit buffer reduction.
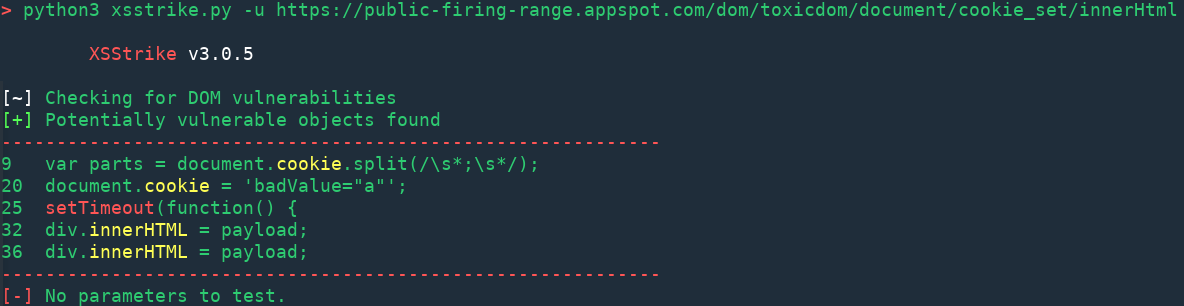
 fatmo666/cve-2023-38545-libcurl-socks5-heap-buffer-overflow
Proof-of-concept exploit for CVE-2023-38545, a heap buffer overflow in libcurl's SOCKS5 proxy handshake triggered via a malicious HTTP 301 redirect…
 yang-shun-yu/cve-2023-38545
Proof-of-concept exploit for CVE-2023-38545, a curl heap buffer overflow. Includes SOCKS5 proxy and HTTP server to trigger the vulnerability and…
 retocode/golang-cve-2023-44487
Testing resources and attacker tool for CVE-2023-44487 (HTTP/2 Rapid Reset) to evaluate server resilience across Go, gRPC, reverse proxy, and nginx…