
clif
 0x4ndy/clif
clif is a command-line interface (CLI) application fuzzer, pretty much what wfuzz or ffuf are for web. It was inspired by sudo vulnerability…
binary-exploitationdynamic-analysis-sandboxingexploitation+3
100
0x4ndy/clifclif is a command-line interface (CLI) application fuzzer, pretty much what wfuzz or ffuf are for web. It was inspired by sudo vulnerability…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 yolkfull/cve-2026-52910-poc
Race reproducer and stress toolkit for CVE-2026-52910, a Linux kernel use-after-free in reuseport cBPF selector programs, with dmesg and leak checks.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
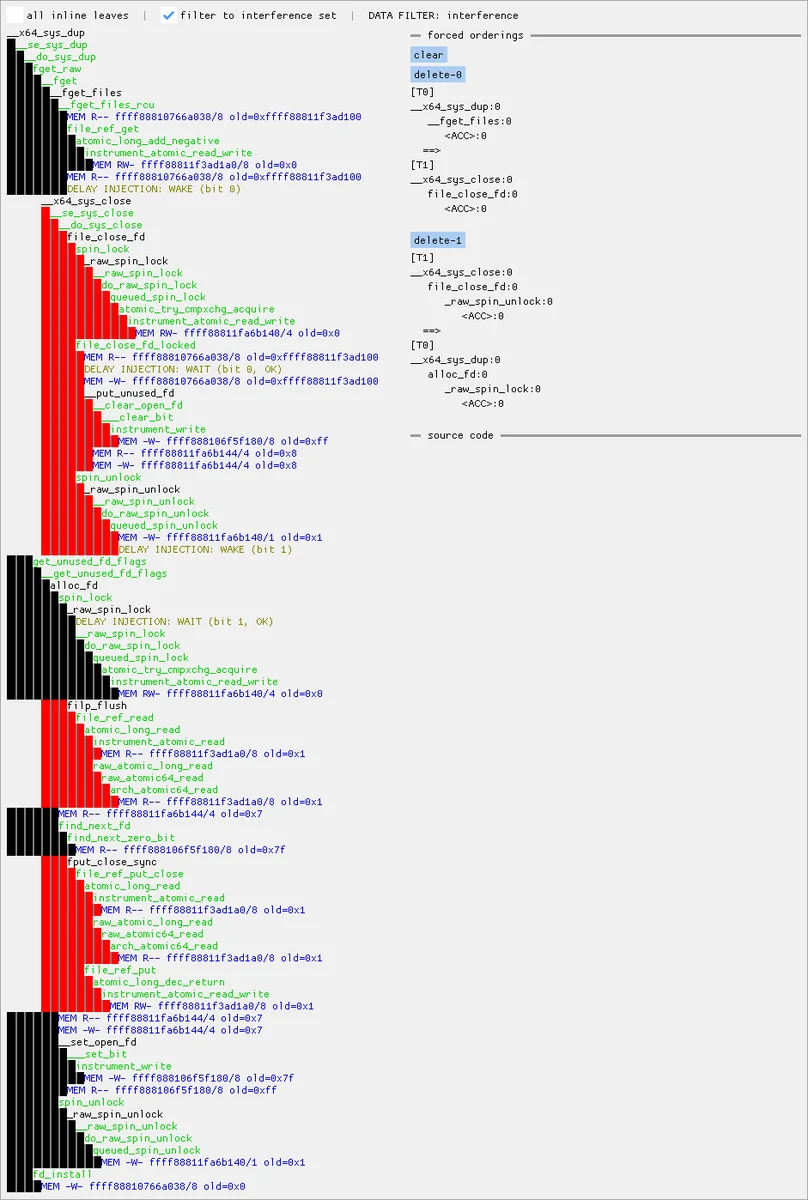 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 gao-zuin/cve-2022-46395-qemu
QEMU-based lab for reproducing CVE-2022-46395 race condition in Arm Mali r36p0 GPU driver. Includes PoC, build scripts, and initramfs packaging for…
 hantwister/fakedellom
A fake host that can be "managed" by Dell OMSA, getting you past the login screen.
 tylepr96/cve-2018-1000030
Python 2.7.14 race condition UAF proof-of-concept
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks