

TriforceOpenBSDFuzzer
 nccgroup/triforceopenbsdfuzzer
System call fuzzing of OpenBSD amd64 using TriforceAFL (i.e. AFL and QEMU)
dynamic-analysis-sandboxingfuzzingvulnerability-analysis
nccgroup/triforceopenbsdfuzzerSystem call fuzzing of OpenBSD amd64 using TriforceAFL (i.e. AFL and QEMU)
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
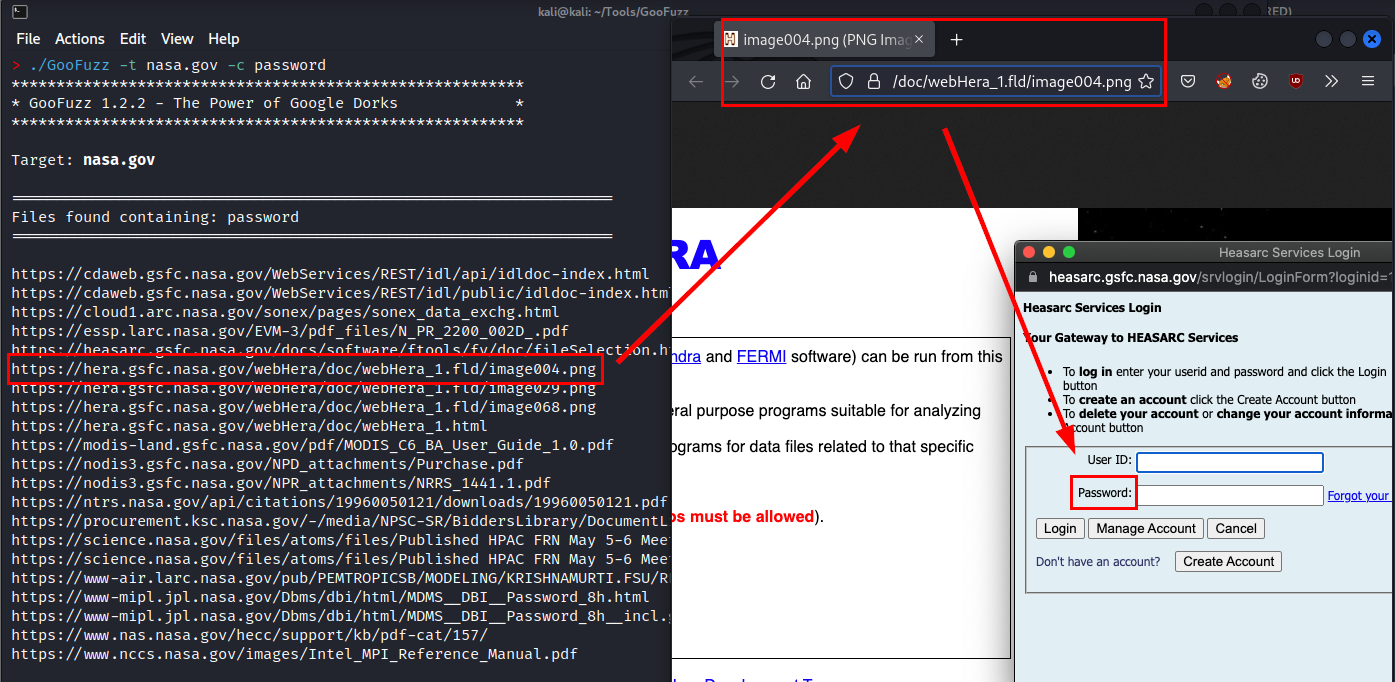 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 13m0n4de/pngcheck-vulns
A repository of proof-of-concept files demonstrating disclosed and patched vulnerabilities in pngcheck (2.4.0 - 3.0.1), including CVE-2020-27818,…
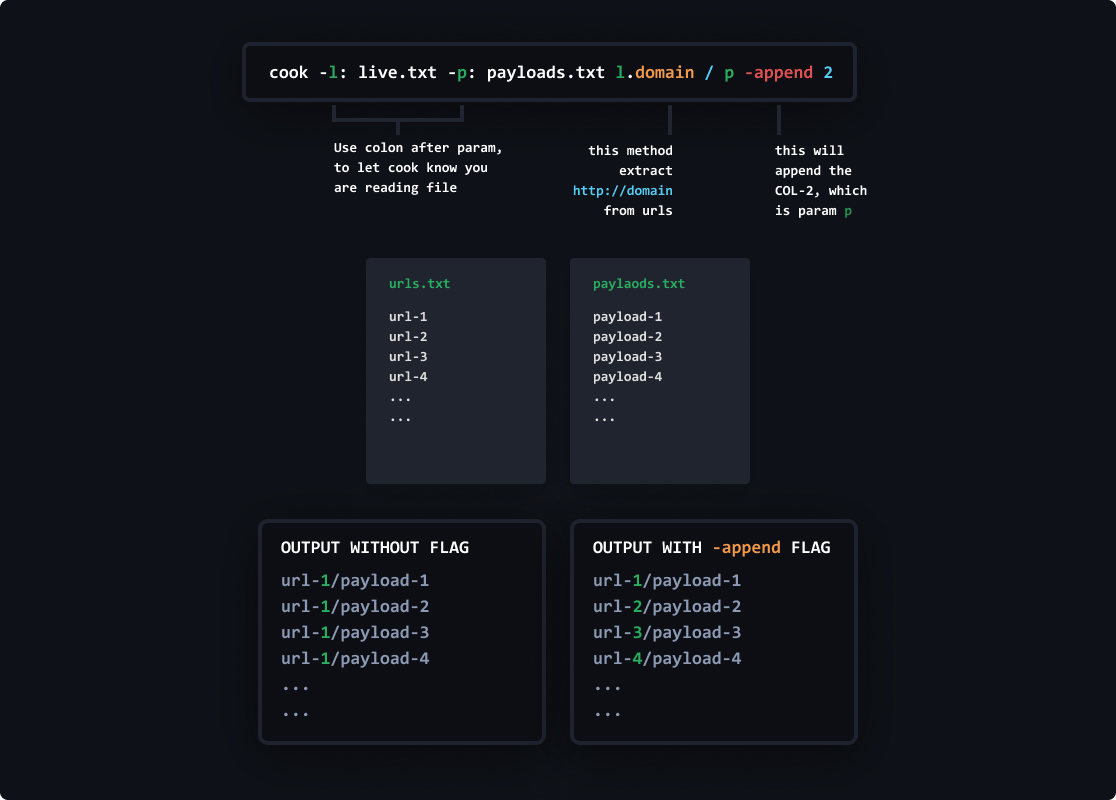 glitchedgitz/cook
A wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 zunak/cve-2024-22641
Proof-of-concept for CVE-2024-22641: ReDoS vulnerability in TCPDF <=6.7.4 triggered by crafted SVG files, demonstrating regex backtrack limit…
 abhinavagarwal07/abhinavagarwal07.github.io
RingWraith: CVE-2026-33150 and CVE-2026-33179 — Use-After-Free and NULL Dereference in libfuse io_uring
 henshin/filebuster
An extremely fast and flexible web fuzzer
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
 musana/fuzzuli
Domain-aware URL fuzzer that dynamically generates wordlists to discover exposed backup and sensitive files on web servers.
 rapiddns/afuzz
Automated web path fuzzing tool that detects hidden directories, files, and endpoints using intelligent language detection, blacklist/whitelist…
 cytopia/urlbuster
Powerful mutable web directory fuzzer to bruteforce existing and/or hidden files or directories.
 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…