

CVE-2026-42945
 liaoziqi-gzfls/cve-2026-42945
CVE-2026-42945 Nginx Rift
binary-exploitationexploitationfuzzing+6
liaoziqi-gzfls/cve-2026-42945CVE-2026-42945 Nginx Rift
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 narfindustries/http-garden
Differential testing framework for HTTP implementations
 redteampentesting/monsoon
Fast HTTP enumerator
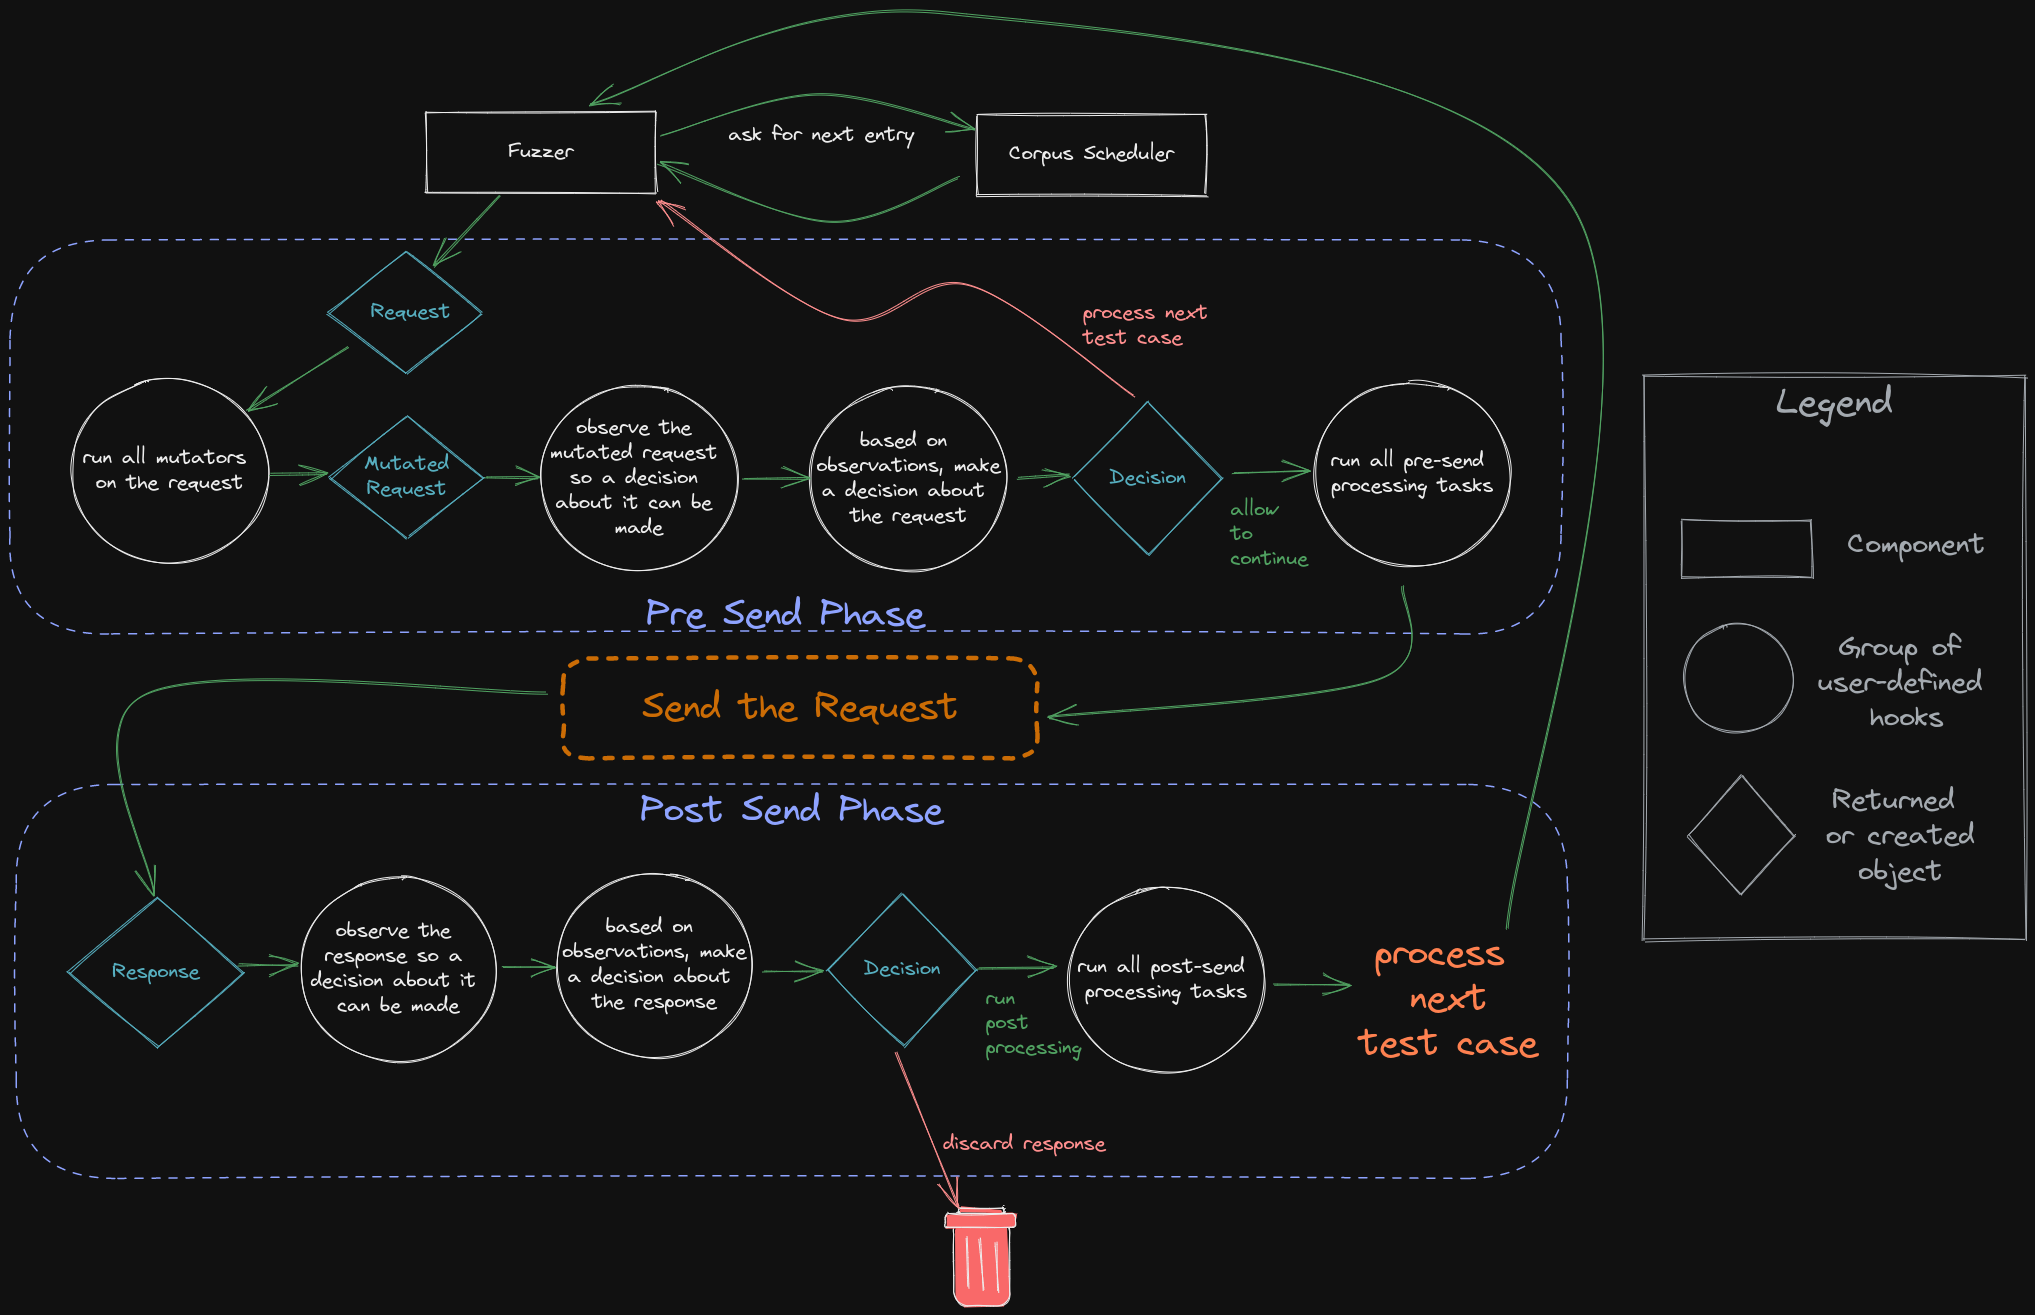 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 henshin/filebuster
An extremely fast and flexible web fuzzer
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 portswigger/turbo-intruder
High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
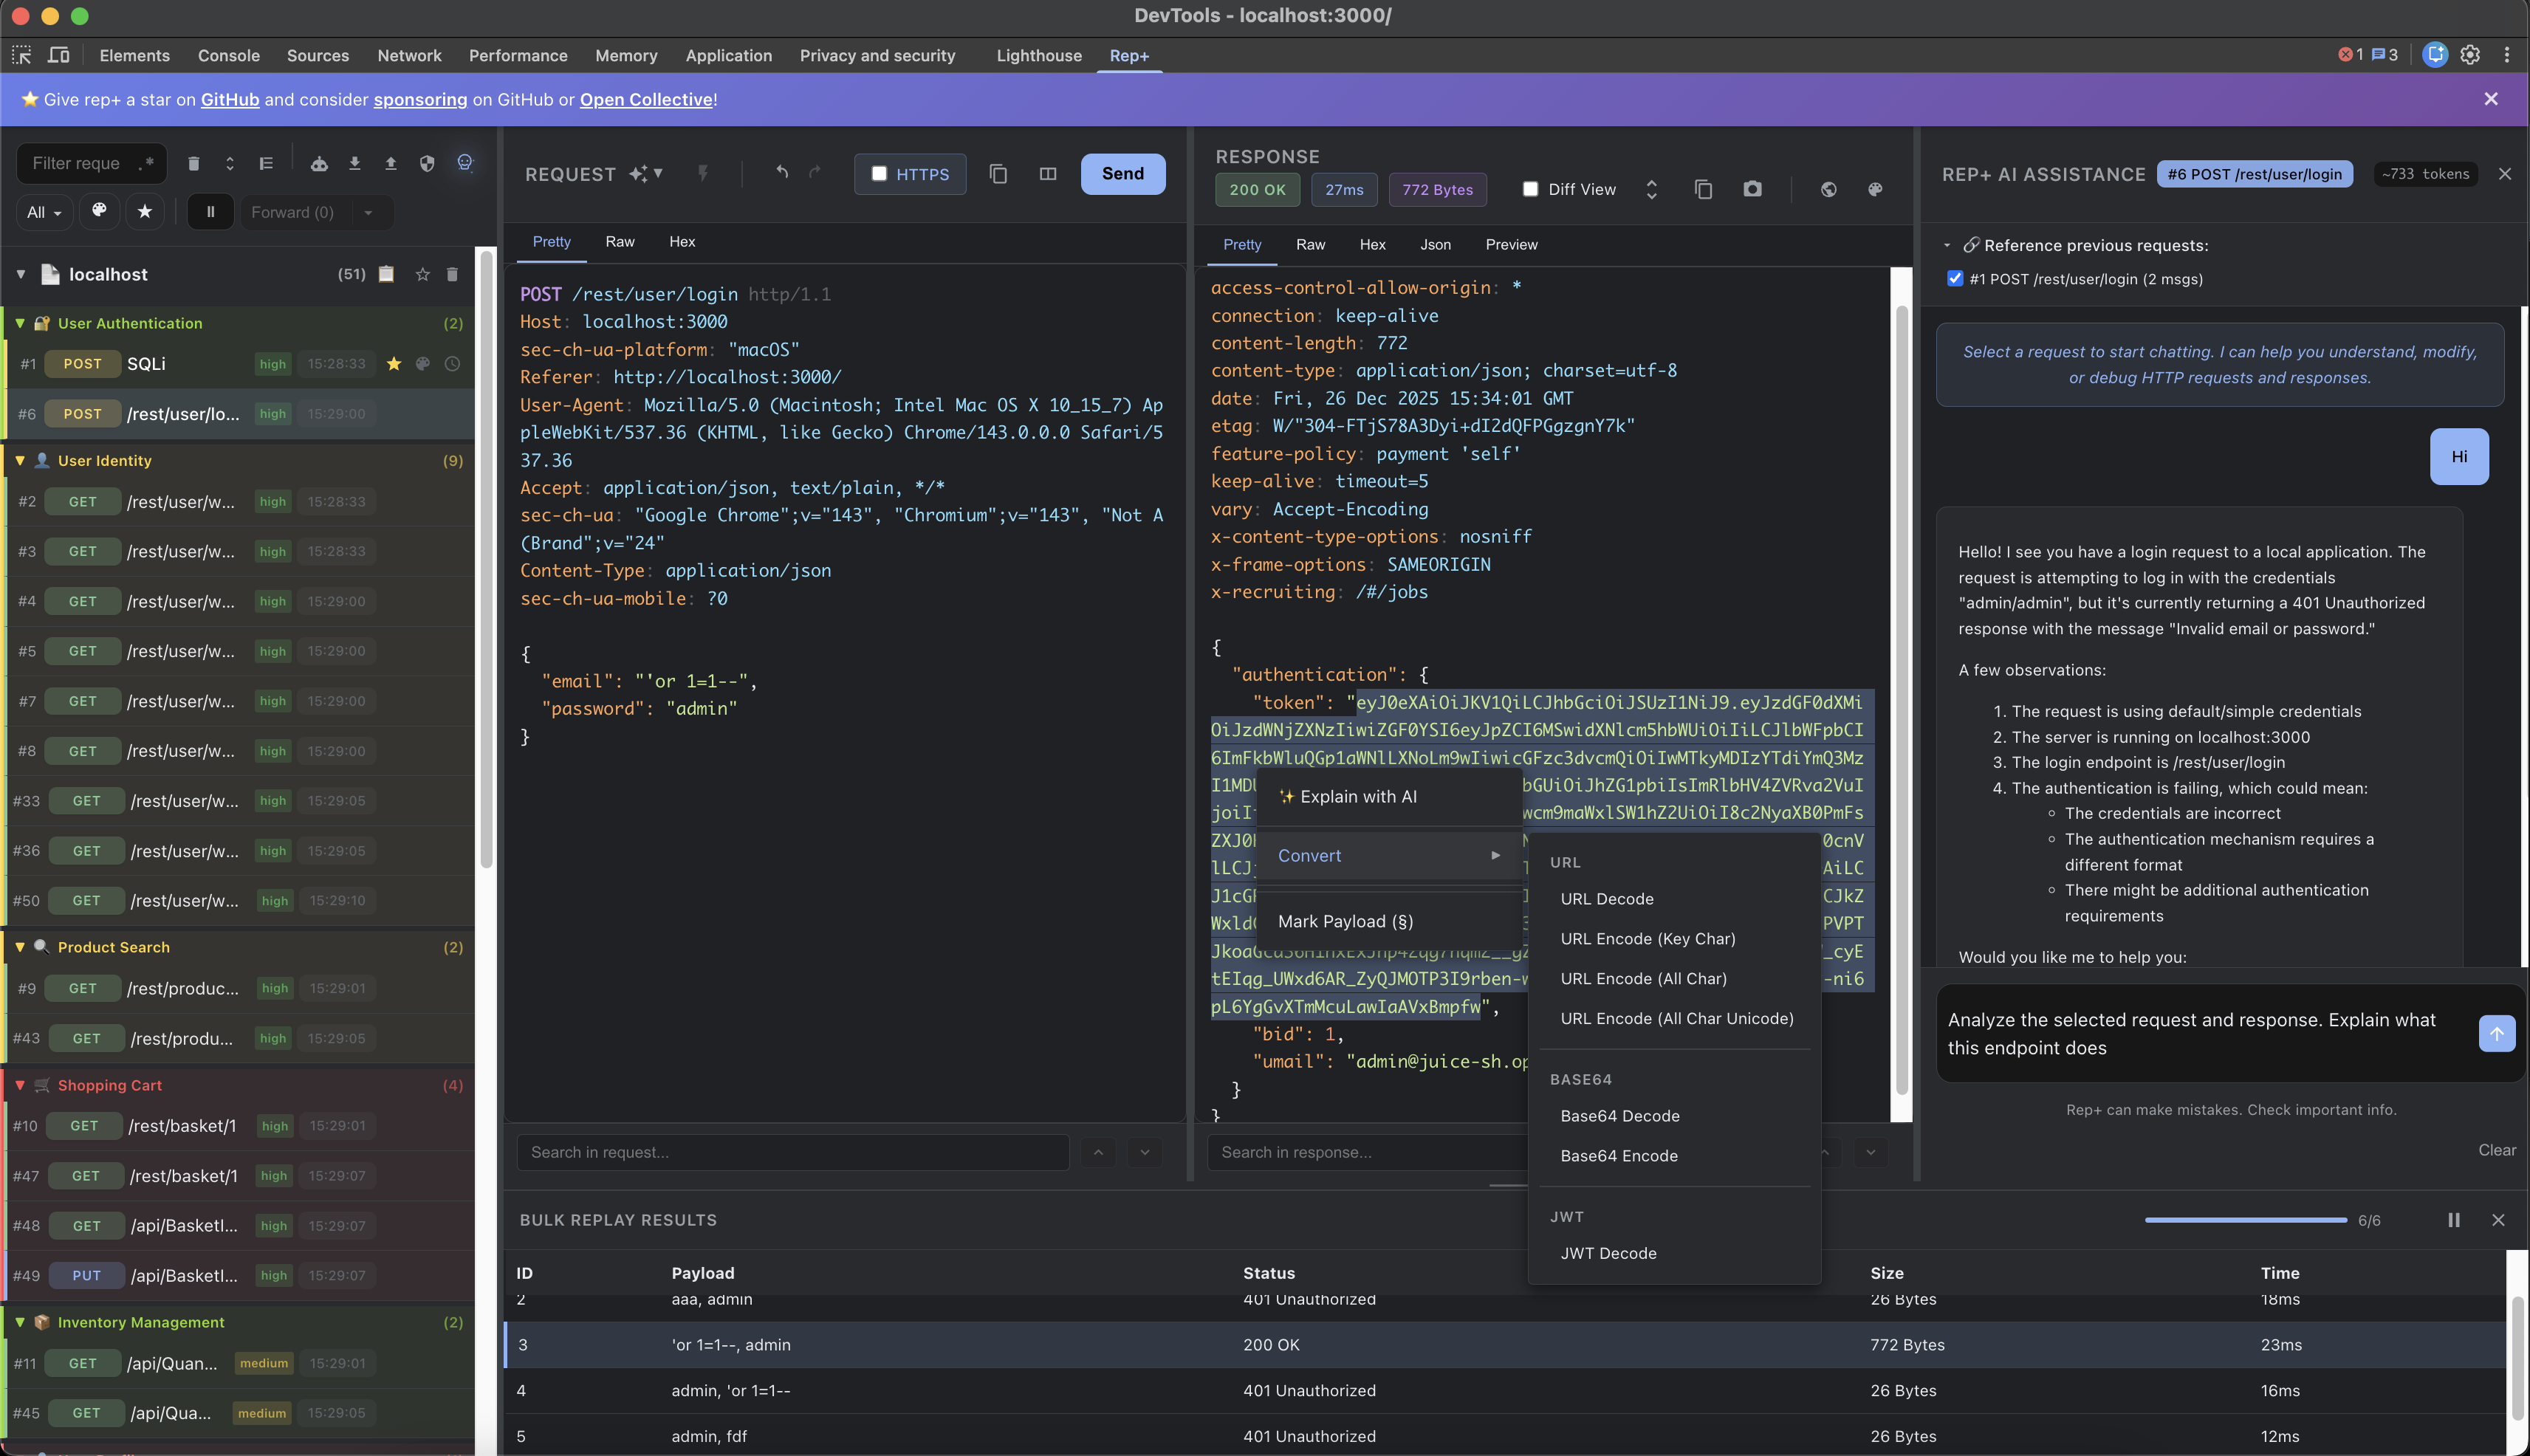 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
 overspace-labs/caa
BurpSuite plugin for HTTP packet analysis and fuzzing dictionary generation. Extracts parameters, paths, and files from requests, counts frequency,…
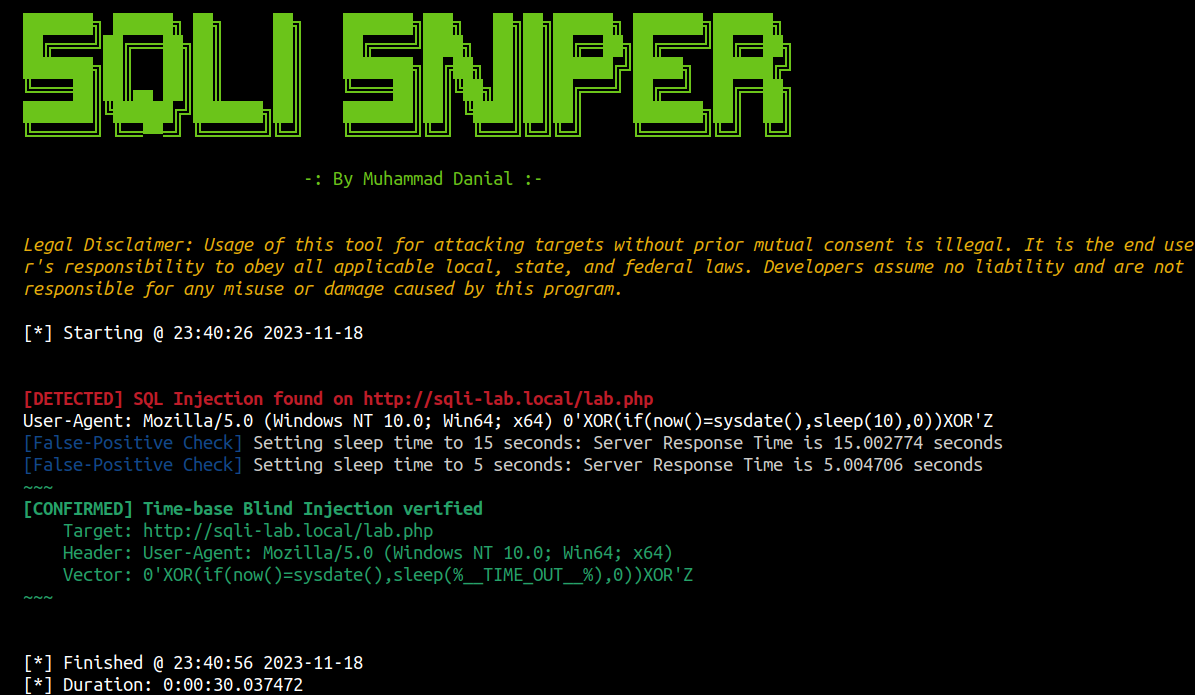 danialhalo/sqlisniper
Advanced Time-based Blind SQL Injection fuzzer for HTTP Headers
 sn1r/forbidden-buster
A tool designed to automate various techniques in order to bypass HTTP 401 and 403 response codes and gain access to unauthorized areas in the…
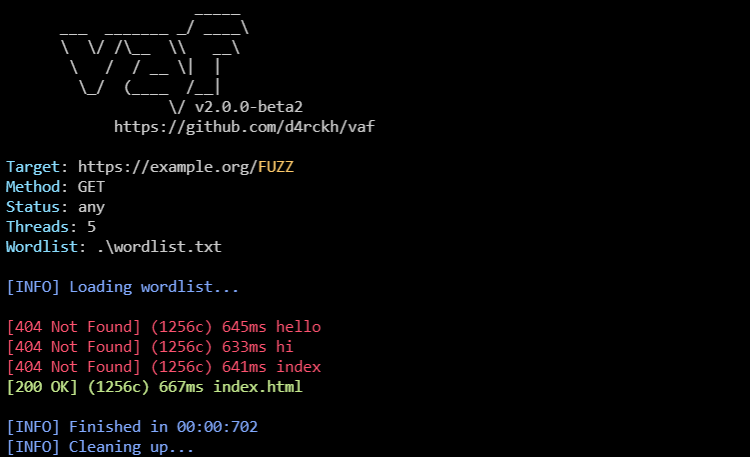 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
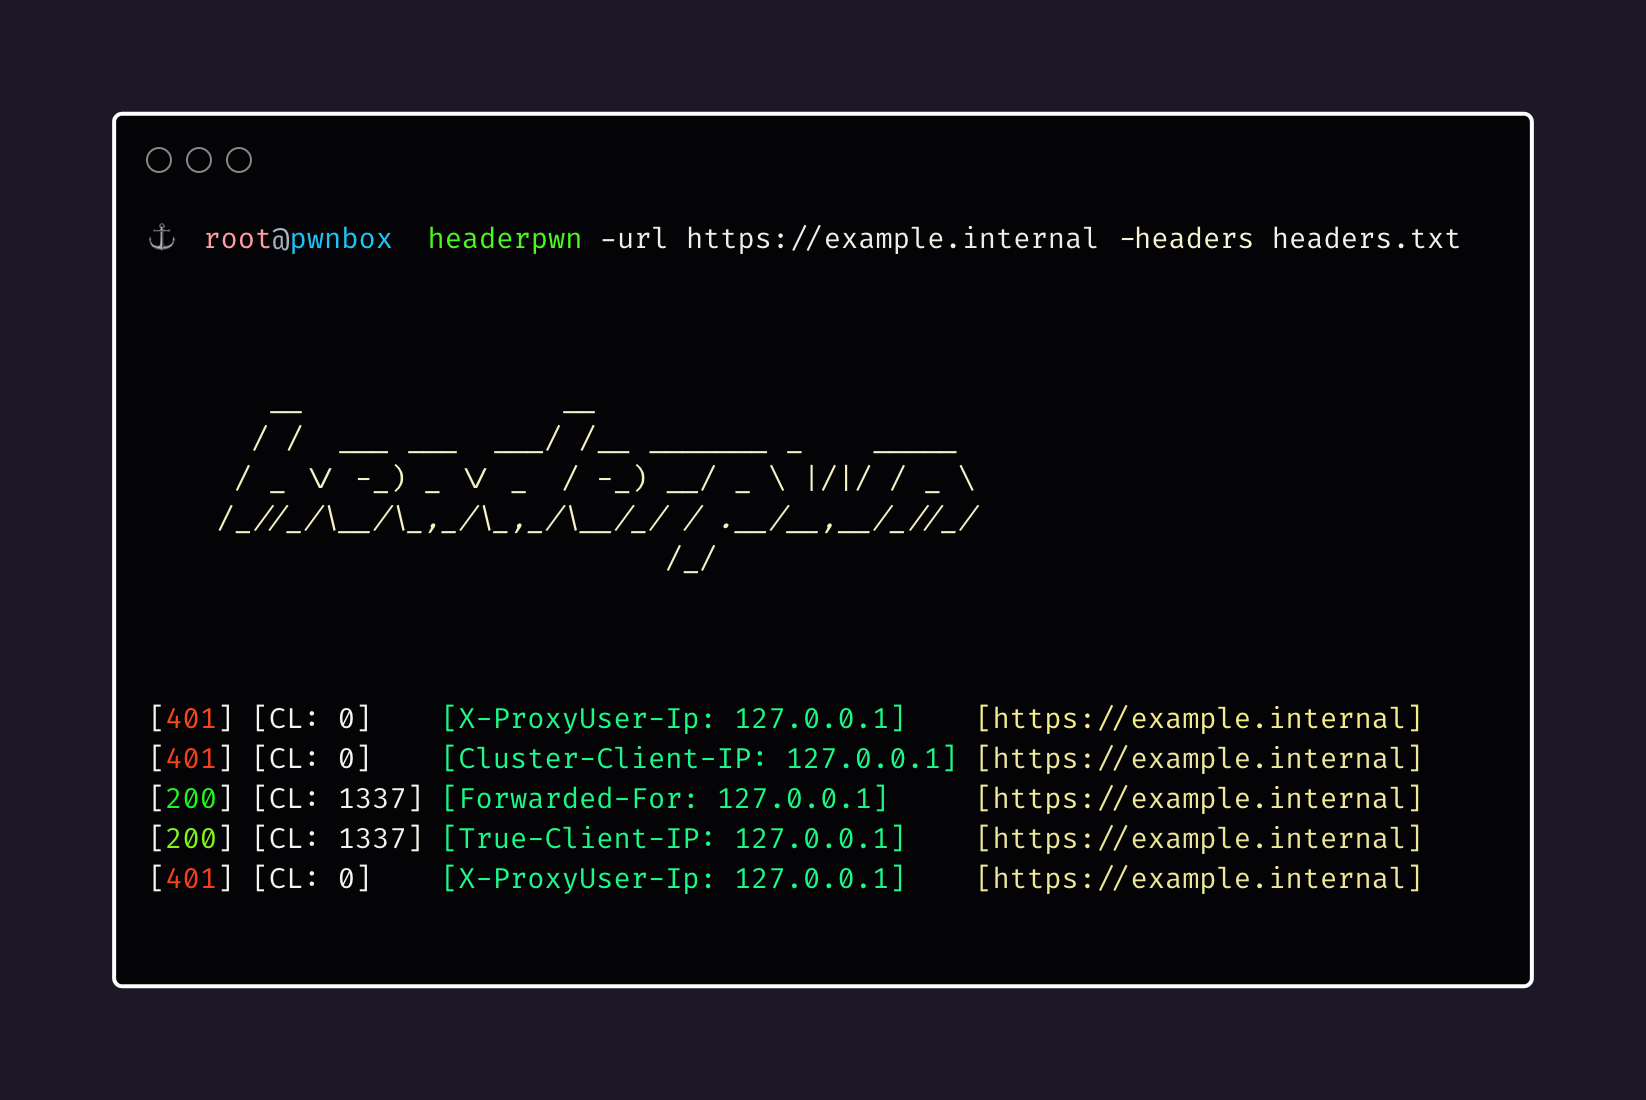 devanshbatham/headerpwn
A fuzzer for finding anomalies and analyzing how servers respond to different HTTP headers
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.