

navgix
 hakaioffsec/navgix
Multi-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
fuzzingmisconfigurationvulnerability-scanners+1
75
hakaioffsec/navgixMulti-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
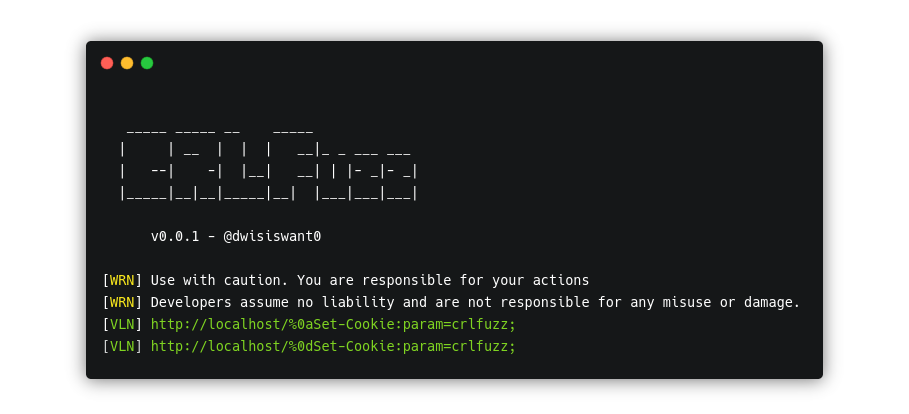 dwisiswant0/crlfuzz
A fast tool to scan CRLF vulnerability written in Go
 retocode/golang-cve-2023-44487
Testing resources and attacker tool for CVE-2023-44487 (HTTP/2 Rapid Reset) to evaluate server resilience across Go, gRPC, reverse proxy, and nginx…
 ryandamour/ssrfuzz
SSRFuzz is a tool to find Server Side Request Forgery vulnerabilities, with CRLF chaining capabilities
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 ethicalhackingplayground/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 perplext/echteeteepee
Go tool and Nuclei template for testing James Kettle's (CVE-2025-32094) HTTP/1.1 must die: the desync endgame
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
 ameenalkerdy/endsfuzzer
Fuzz a list of domains for specific endpoints
 dzonerzy/gowapt
Go Web Application Penetration Test
 dsecuredcom/ffufpostprocessing
Golang tool which helps dropping the irrelevant entries from your ffuf result file.
 doyensec/regexploit
Find regular expressions which are vulnerable to ReDoS (Regular Expression Denial of Service)
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
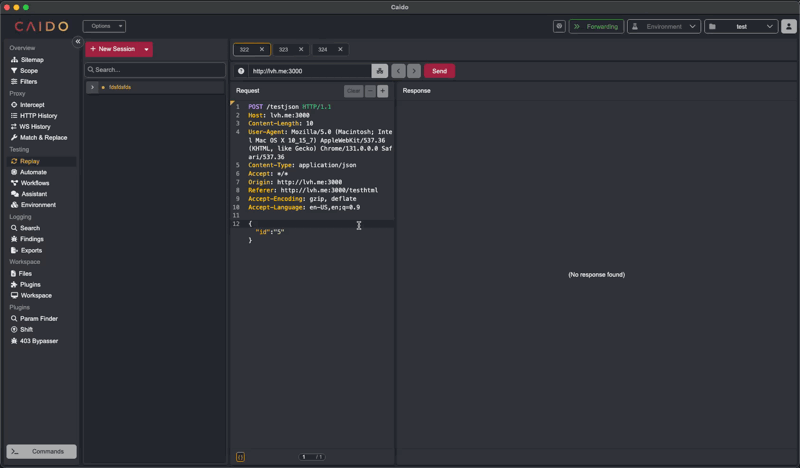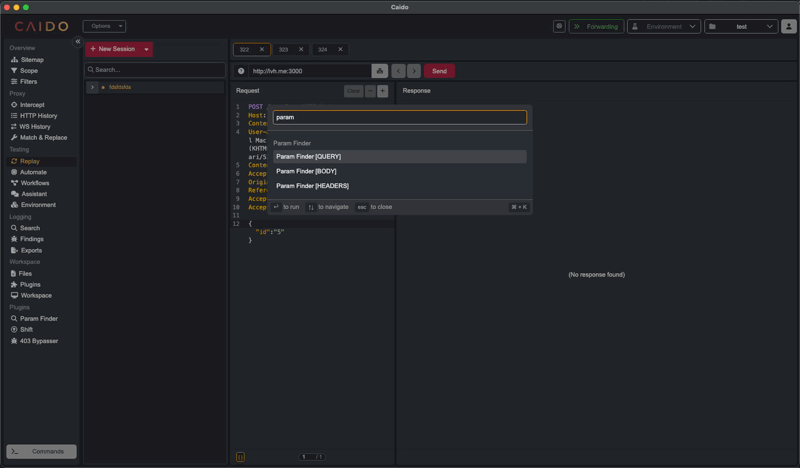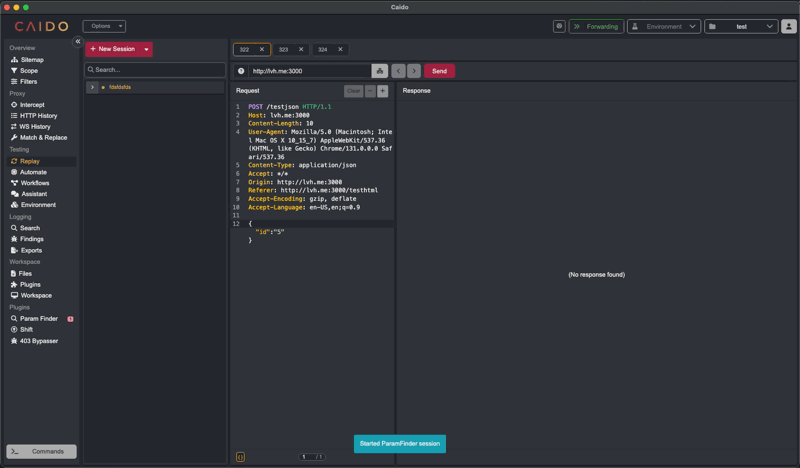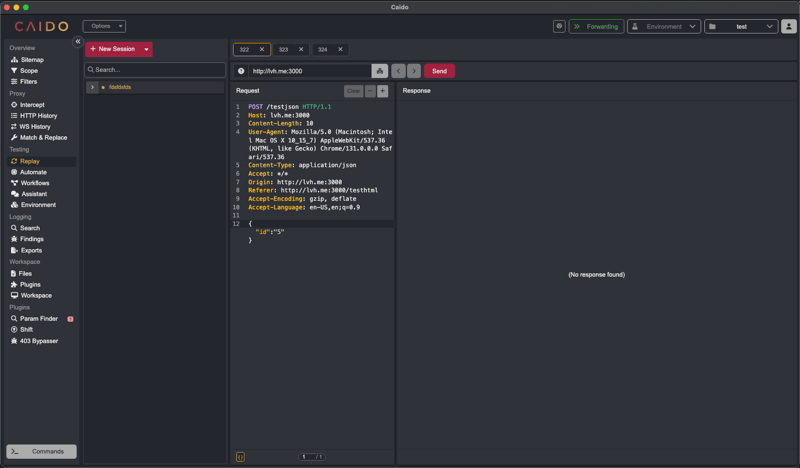 caido-community/paramfinder
Discover hidden parameters in Caido
 oj/gobuster
Directory/File, DNS and VHost busting tool written in Go
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
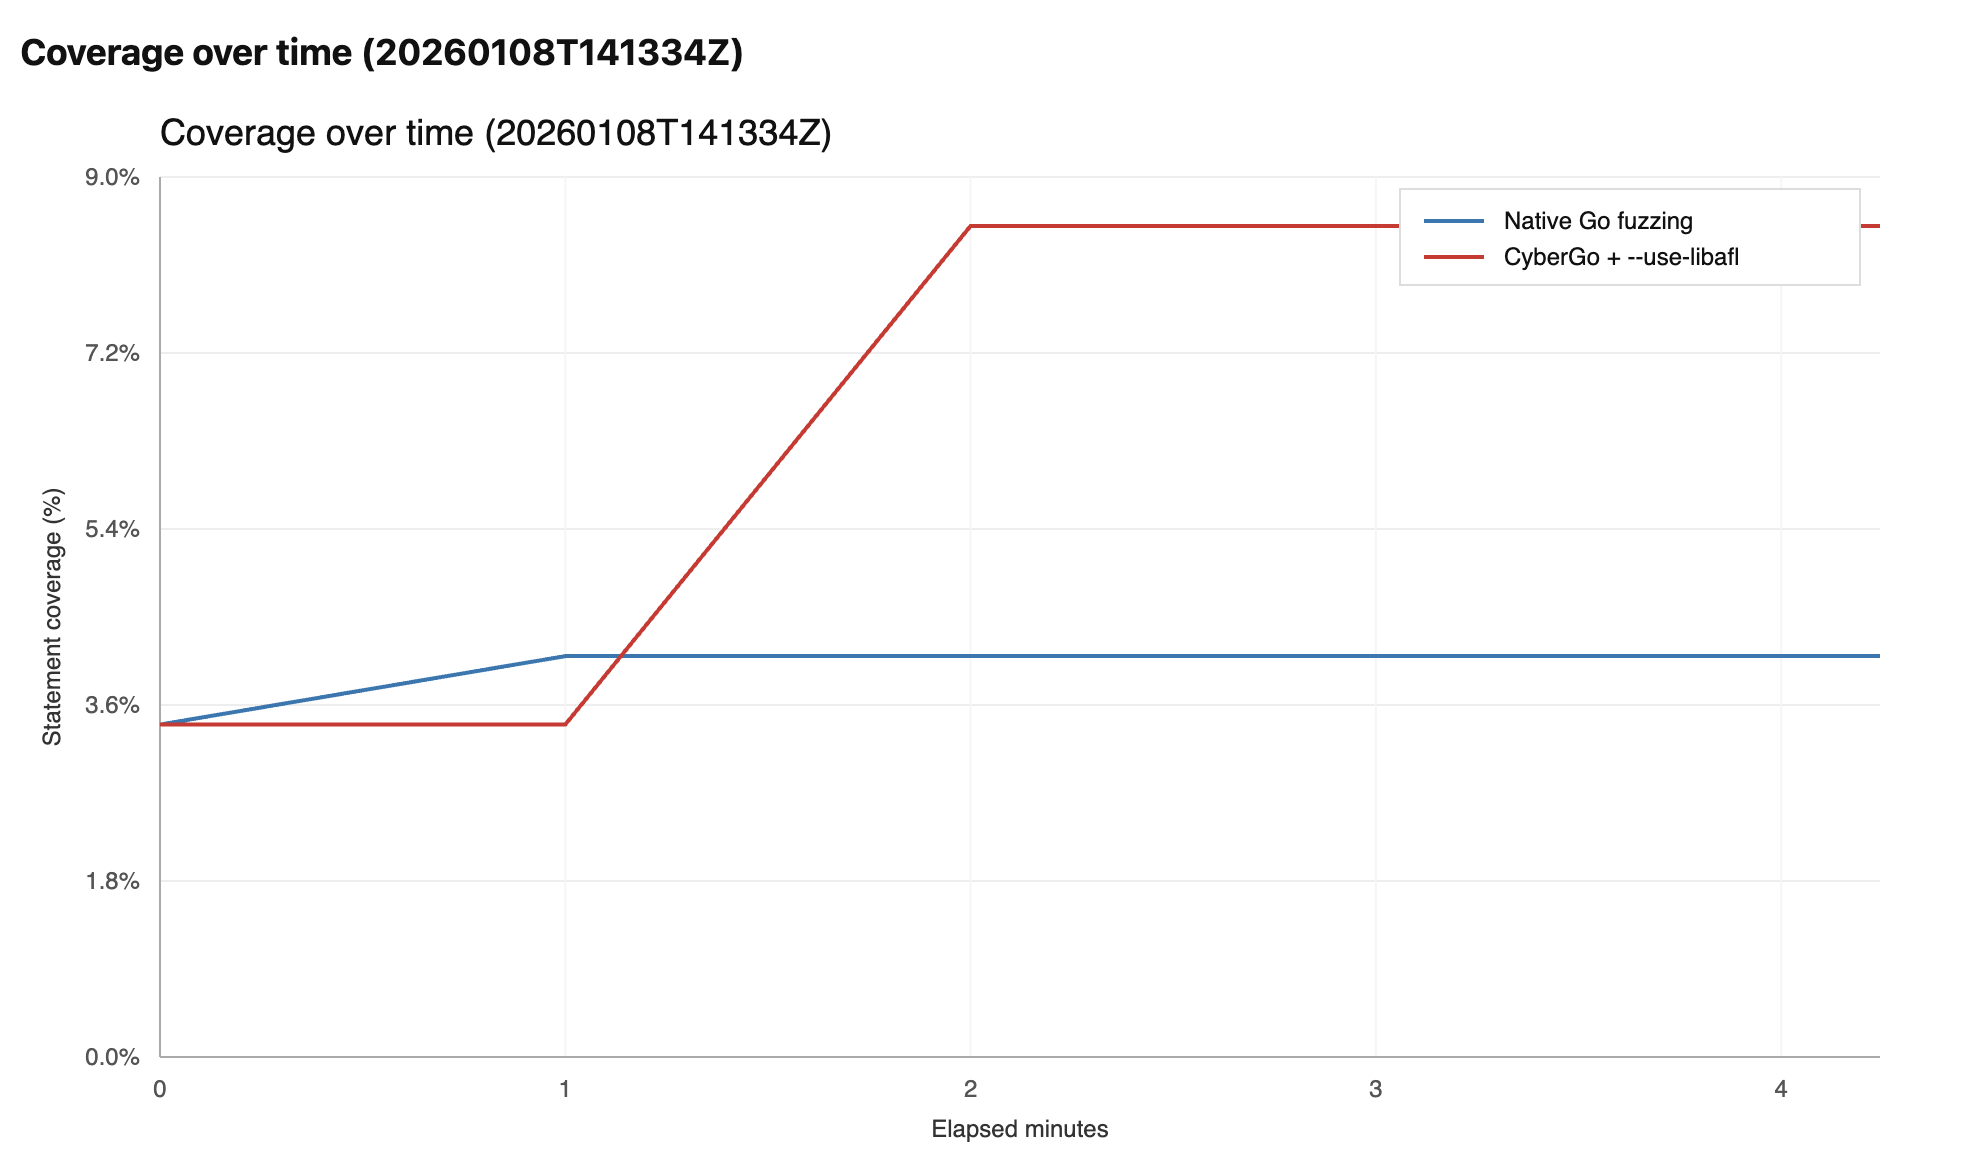 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.