
CVE-2025-55891
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
binary-exploitationexploitationfuzzing+3
terribledactyl/cve-2025-55891Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 luisfontes19/xxexploiter
Tool to help exploit XXE vulnerabilities
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 amossys/memitm
Tool to make in memory man in the middle
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
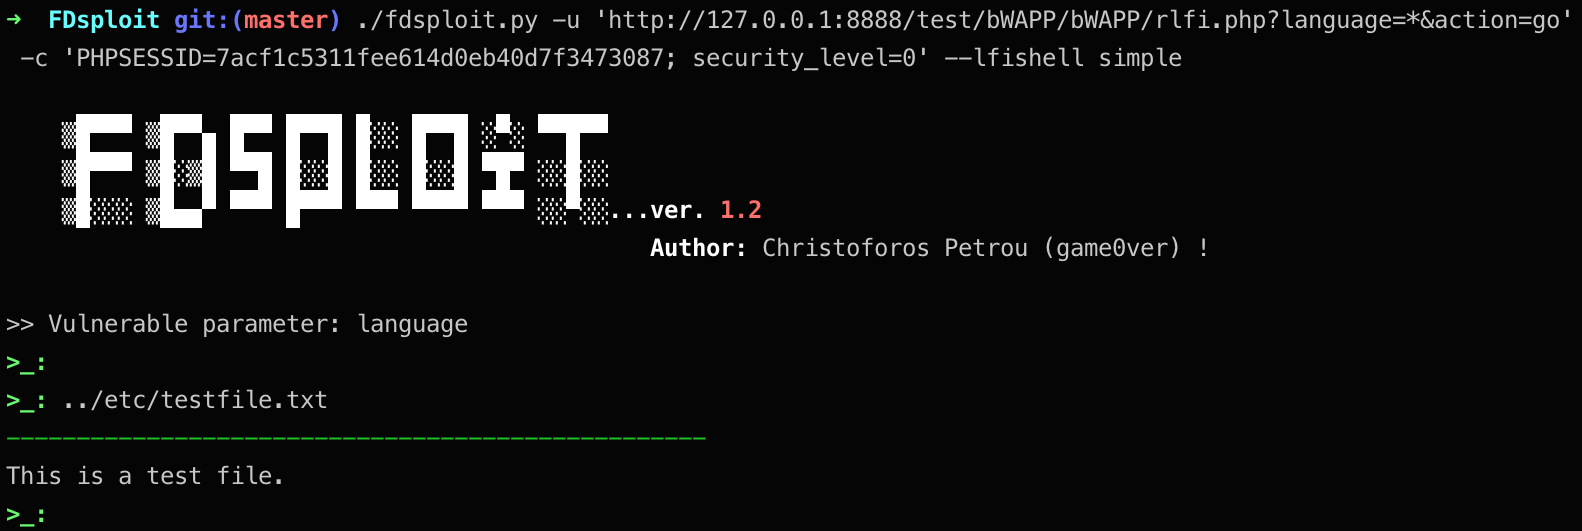 chrispetrou/fdsploit
File Inclusion & Directory Traversal fuzzing, enumeration & exploitation tool.
 tismayil/fastfuz-chrome-ext
Chrome extension for fast web fuzzing to discover hidden files and directories during penetration testing and vulnerability analysis.
 dsecuredcom/ffufpostprocessing
Golang tool which helps dropping the irrelevant entries from your ffuf result file.
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 ioactive/melkor_elf_fuzzer
Melkor is a very intuitive and easy-to-use ELF file format fuzzer to find functional and security bugs in ELF parsers.
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 mk219533/cve-2010-1205
sample exploit of buffer overflow in libpng
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 ww9210/cve-2017-7374
Proof-of-concept exploit for CVE-2017-7374, triggering a vulnerability in ext4 filesystem encryption via crafted directory operations on Linux.