yakit
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
command-and-controlexploit-frameworksfuzzing+9
7.7k
yaklang/yakitAll-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 bishopfox/joro
A collaborative web exploitation framework.
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 luisfontes19/xxexploiter
Tool to help exploit XXE vulnerabilities
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 jesusprubio/bluebox
A collection of exploits for different VoIP products.
 malqr/malqr.github.io
MalQR is a collection of malicious QR Codes and Barcodes you can use to test the security of your scanners.

 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
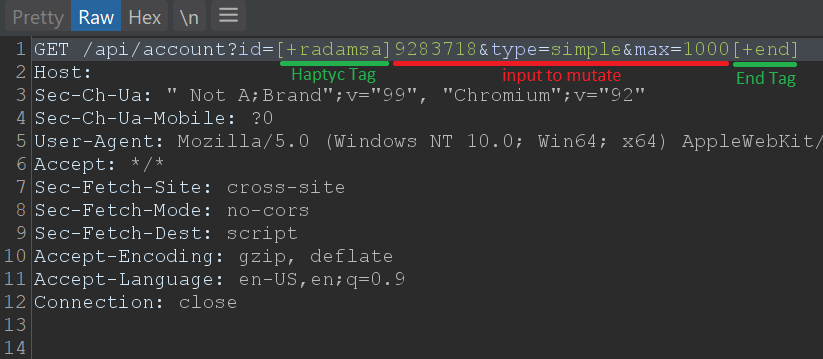 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 payatu/cve-2018-14442
PoC for Foxit Reader CVE-2018-14442
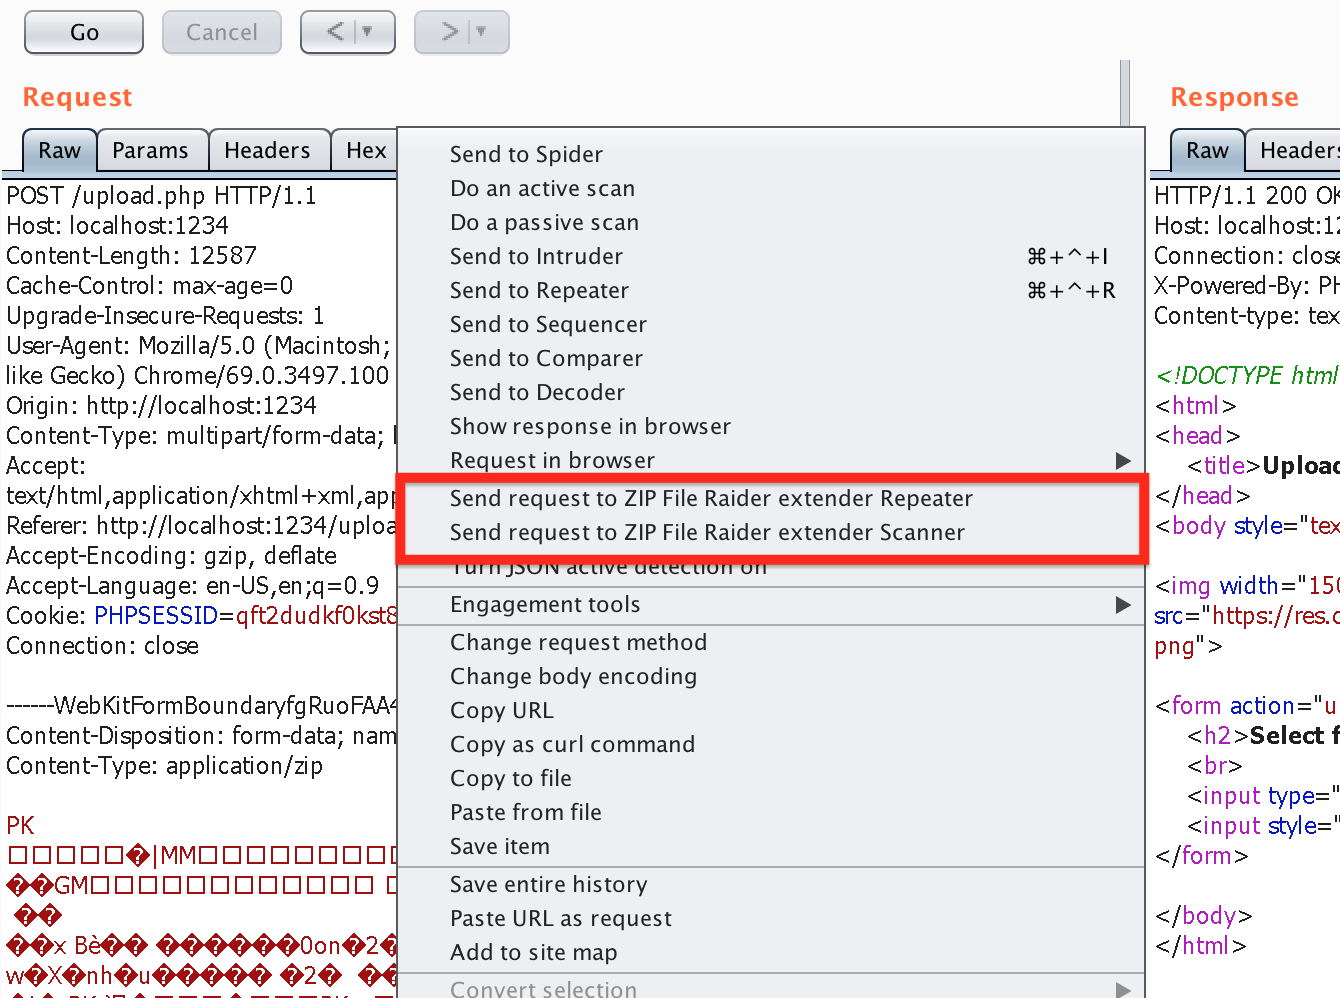 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
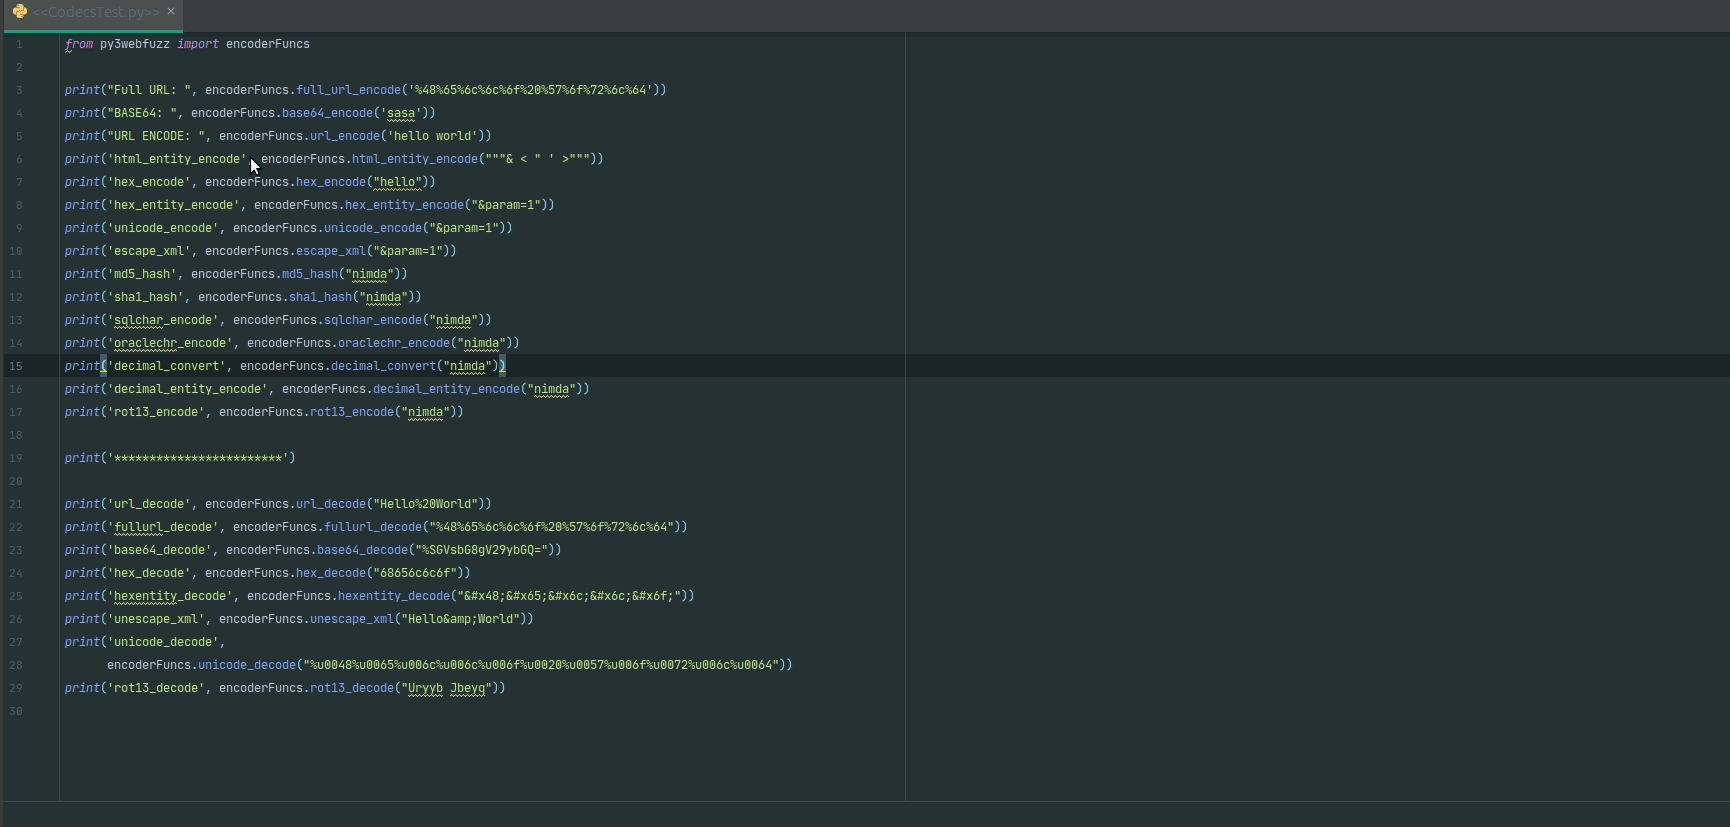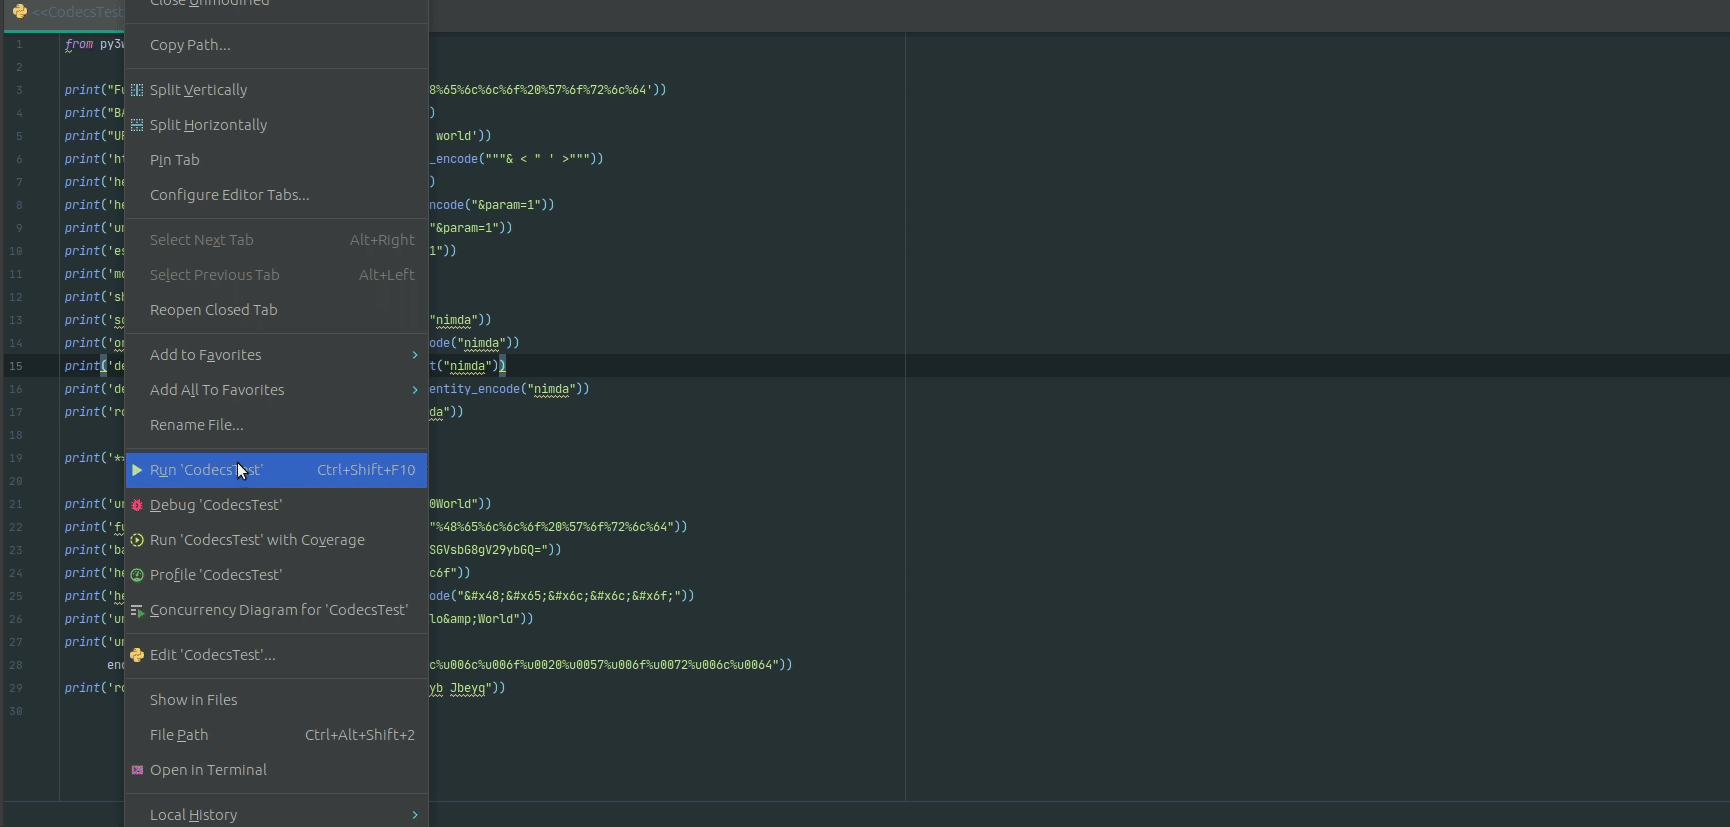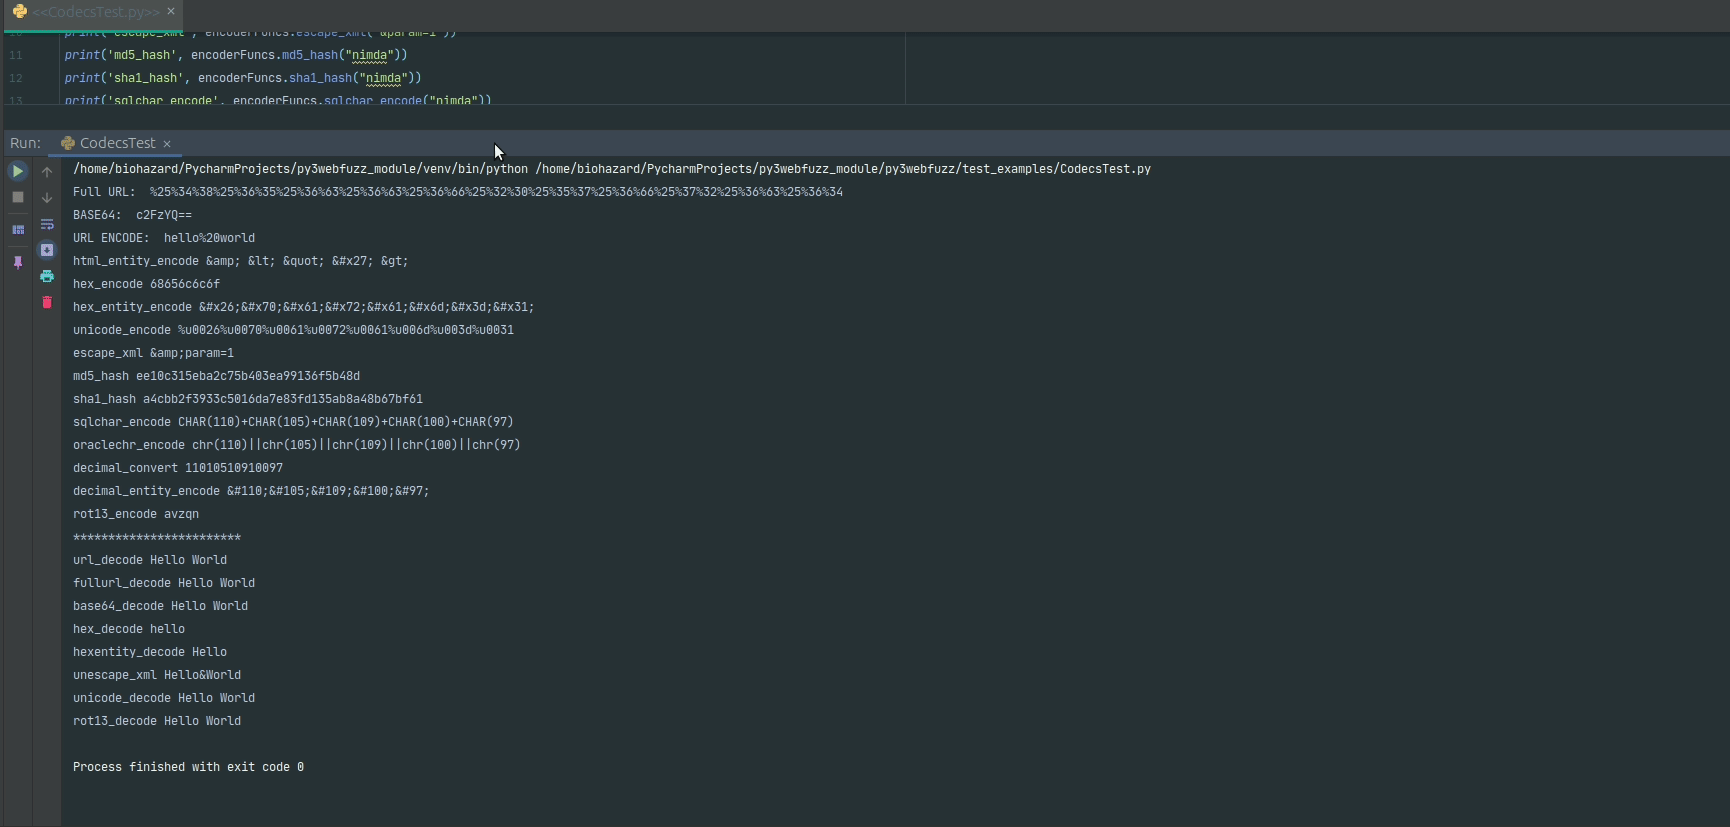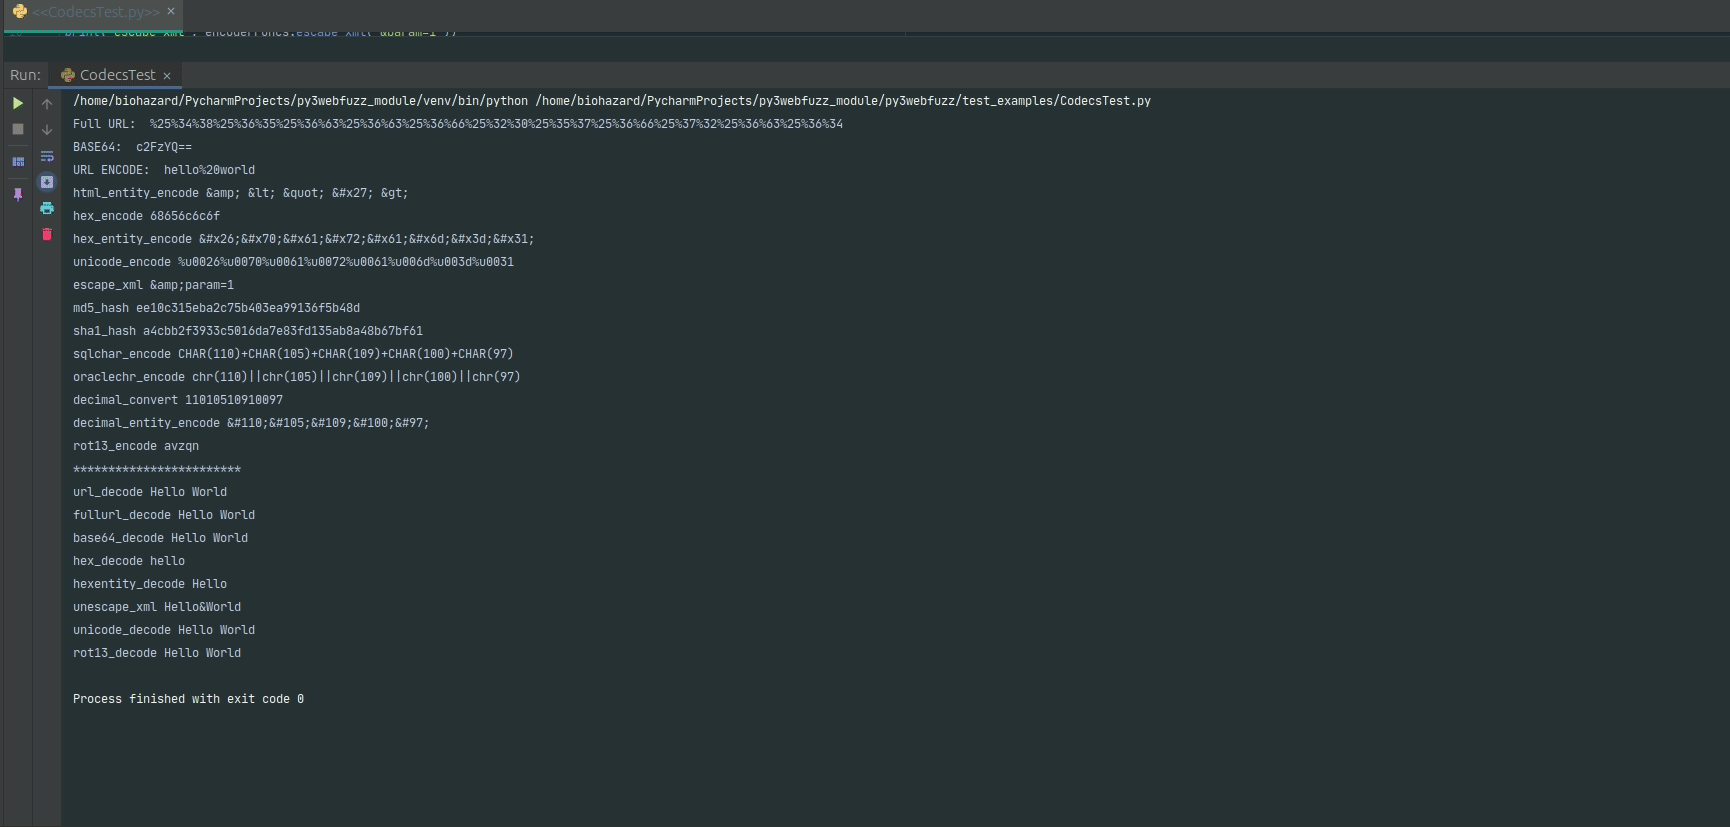 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 r00thunter/log4shell
Generic Scanner for Apache log4j RCE CVE-2021-44228
 grp-ops/react2shell
Lightweight scanner and Nuclei templates for identifying React and Next.js deserialization RCEs (CVE-2025-55182 / CVE-2025-66478).
 jvbotelho/cve-2026-69243-poc-aiohttp-smuggling
Reproduces aiohttp CWE-444 request smuggling via rejected WebSocket upgrades, with Python/Rust payloads and Docker lab demonstrating proxy…