
CVE-2025-5548
 javyan05/cve-2025-5548
Entorno y explotación de la vulnerabilidad CVE-2025-5548
binary-exploitationdebuggerseducation+6
javyan05/cve-2025-5548Entorno y explotación de la vulnerabilidad CVE-2025-5548
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 iamescri/cve-2025-5548-freefloat-ftp-buffer-overflow
Laboratorio de análisis y explotación de la vulnerabilidad CVE-2025-5548 en FreeFloat FTP Server 1.0
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
 jsantos1990/cve-2025-5548
🚀 Complete analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server 1.0 - NOOP Buffer Overflow) Full methodology: manual tool installation,…
 jackieya/vitevulscan
针对CVE-2025-30208和CVE-2025-31125的漏洞利用
 m4rc0s-s3c/cve-2025-5548-freefloat-ftp-lab
Laboratorio académico de análisis y explotación de CVE-2025-5548 en FreeFloat FTP Server 1.0.
 alvarosr/cve-2025-5548
Documented technical analysis and controlled exploitation of CVE-2025-5548 in FreeFloat FTP Server, covering lab setup, static/dynamic binary…
 gumbita/cve-2025-5548-freefloat-ftp-walkthrough
Documentación paso a paso del análisis y la explotación controlada de la CVE-2025-5548 en FreeFloat FTP Server 1.0, incluyendo preparación del…
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 ish2yu/cve-2025-55780
Null Pointer Dereference in MuPDF , First CVE discovered by me
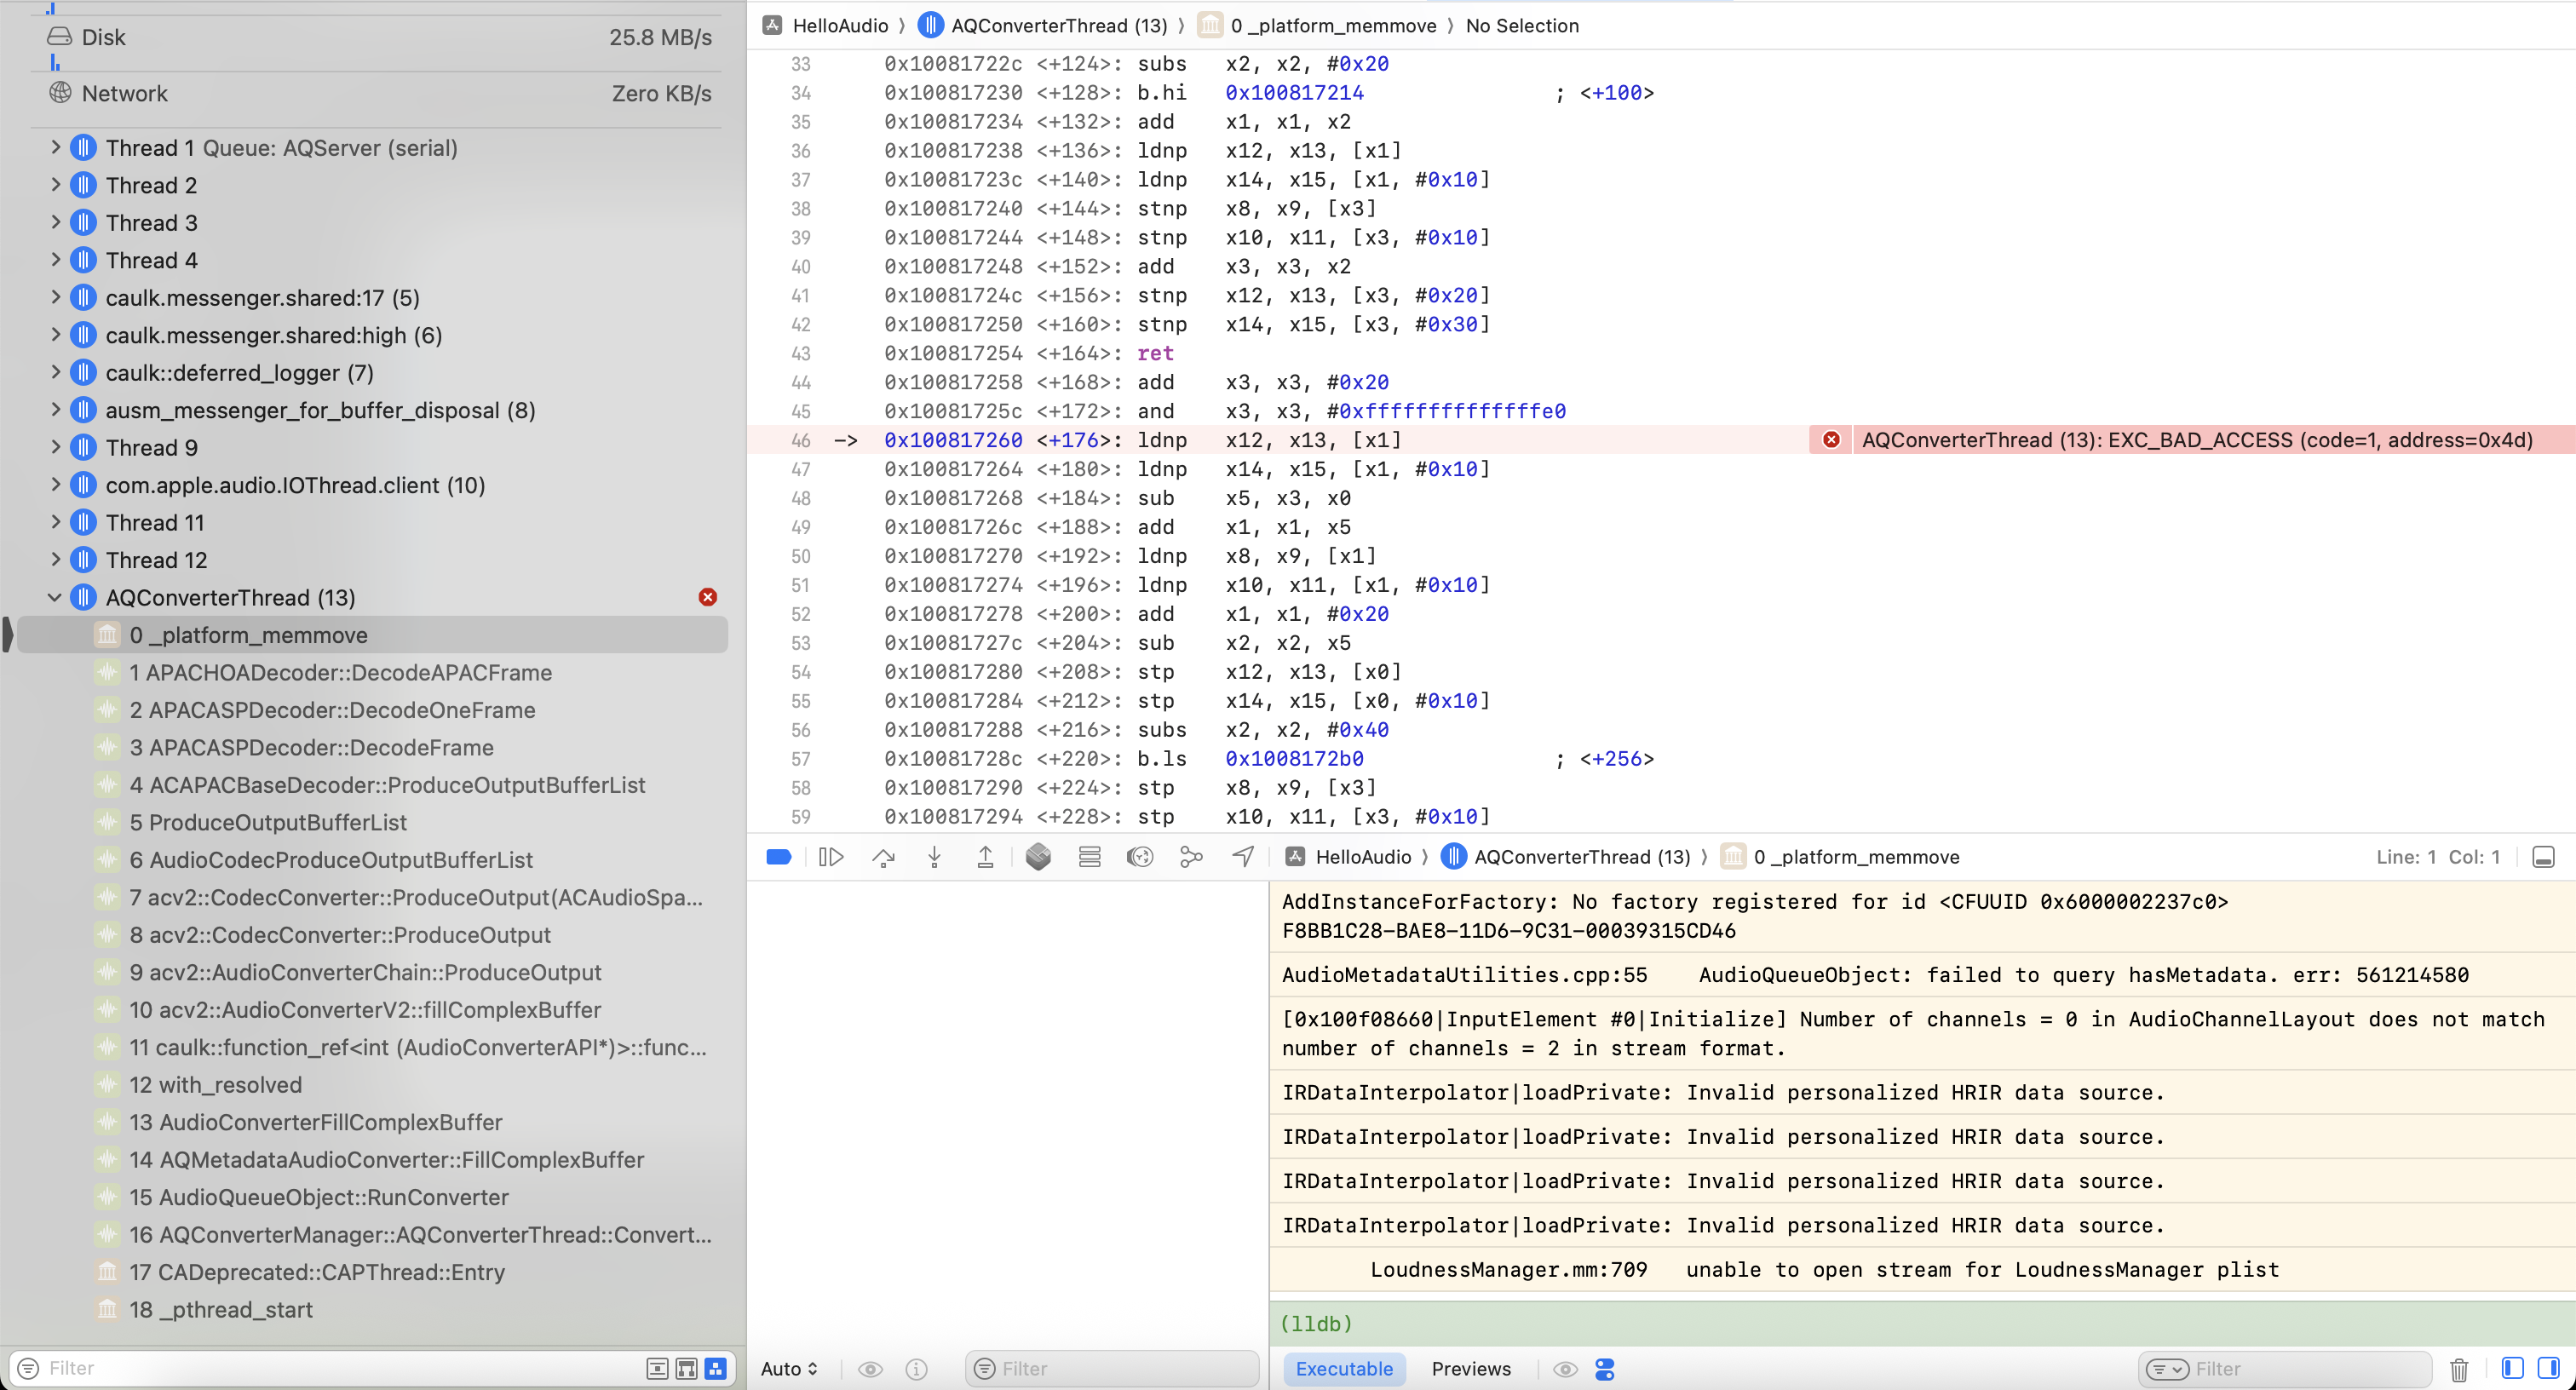 zhuowei/apple-positional-audio-codec-invalid-header
CVE-2025-31200 - @Noahhw46 figured it out
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
 zhuowei/cve-2025-27363-proof-of-concept
Proof-of-concept for CVE-2025-27363 demonstrating a heap buffer overflow in FreeType 2.13.0 via a crafted variable font, with ASAN-verified crash…
 kha-beleh/poc-cve-2025-69420
Crash-only PoC for CVE-2025-69420 demonstrating a type-confusion vulnerability in OpenSSL's TimeStamp Response verification via malformed ESS…
 kha-beleh/poc-cve-2025-69419
Minimal proof-of-concept reproducer for CVE-2025-69419, a heap buffer overflow in OpenSSL's PKCS12_get_friendlyname() triggered by a crafted…