
xxexploiter
 luisfontes19/xxexploiter
Tool to help exploit XXE vulnerabilities
exploitationfuzzingpayload-generation+2
luisfontes19/xxexploiterTool to help exploit XXE vulnerabilities
 1n3/intruderpayloads
A collection of Burpsuite Intruder payloads, BurpBounty payloads, fuzz lists, malicious file uploads and web pentesting methodologies and checklists.
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 noptrix/lulzbuster
A multithreaded, very fast and smart HTTP(S) directory and file bruteforcer written in C on top of libcurl
 ioactive/melkor_elf_fuzzer
Melkor is a very intuitive and easy-to-use ELF file format fuzzer to find functional and security bugs in ELF parsers.
 0xricksanchez/fisy-fuzz
This is the full file system fuzzing framework that I presented at the Hack in the Box 2020 Lockdown Edition conference in April.
 dsecuredcom/ffufpostprocessing
Golang tool which helps dropping the irrelevant entries from your ffuf result file.
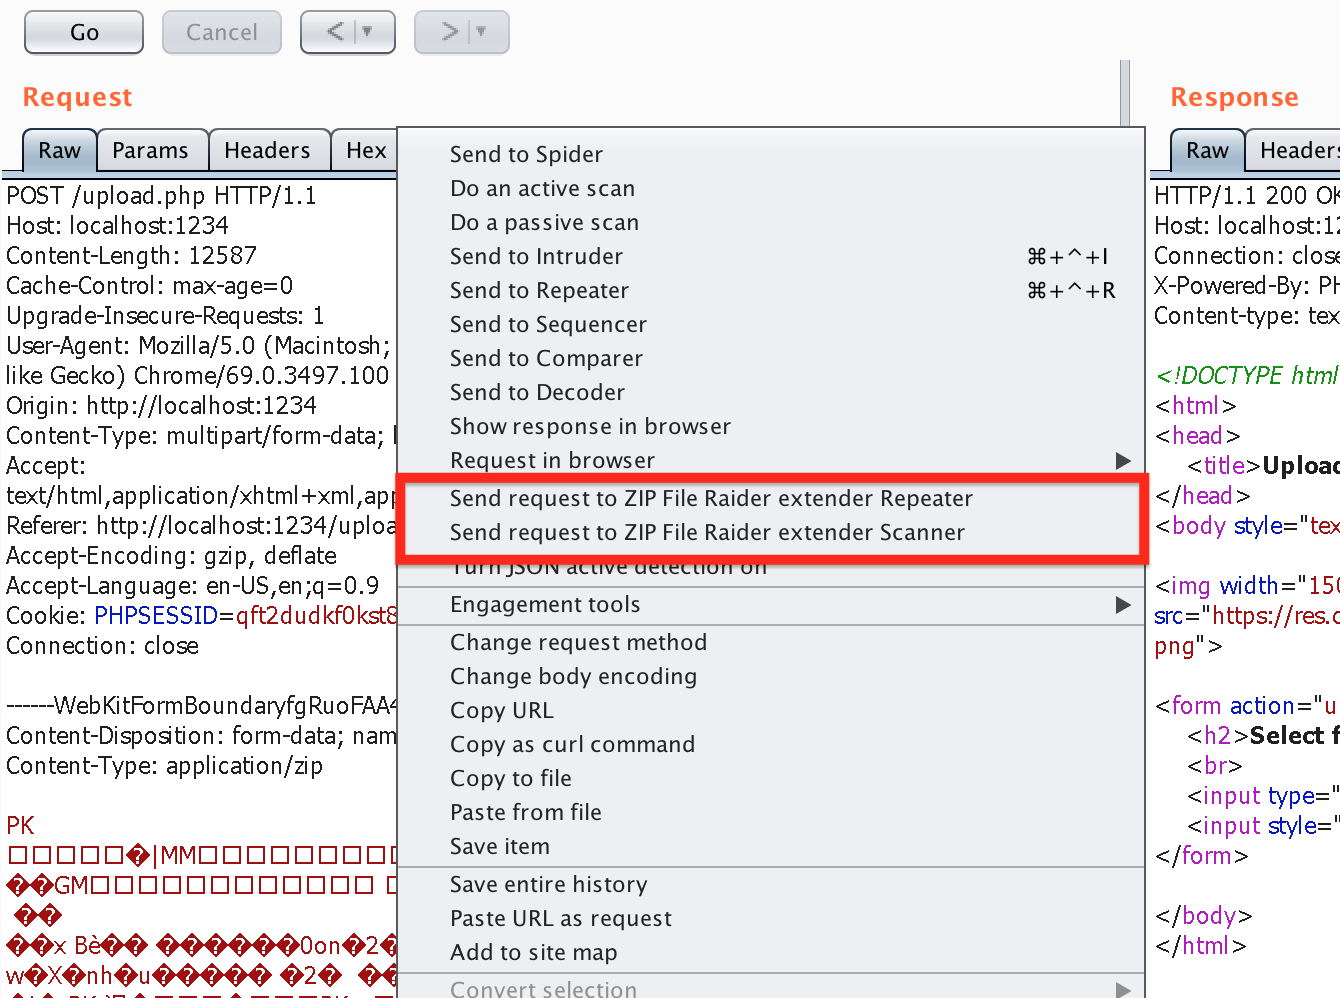 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 anyanything/cve-2026-8461-poc
Proof-of-concept exploit for CVE-2026-8461, generating a crafted AVI file that triggers a crash in unpatched ffmpeg versions.
 olafdaf/cve-2022-40363
A buffer overflow in the component nfc_device_load_mifare_ul_data of Flipper Devices Inc., Flipper Zero before v0.65.2 allows attackers to cause a…
 kha-beleh/poc-cve-2025-69421
Minimal CVE-2025-69421 reproducer demonstrating a NULL pointer dereference in OpenSSL PKCS#12 processing via a malformed PFX file with absent…
 pwndorei/cve-2024-22532
Proof-of-concept exploit for CVE-2024-22532: heap-based buffer overflow in XnView Classic 2.51.5 and NConvert 7.163 via crafted .xwd file, enabling…
 erikdervishi03/cve-2026-31024
Proof of Concept (PoC) for a stack-based buffer overflow in Steghide 0.5.1. Demonstrates how long file paths trigger a crash (DoS) and leak sensitive…
 fineas/cve-2019-13288-poc
Proof-of-concept exploit for CVE-2019-13288, demonstrating infinite recursion denial-of-service in Xpdf 4.01.01 via a crafted PDF file.