
goWAPT
 dzonerzy/gowapt
Go Web Application Penetration Test
fuzzingpenetration-testingscripting-automation+4
dzonerzy/gowaptGo Web Application Penetration Test
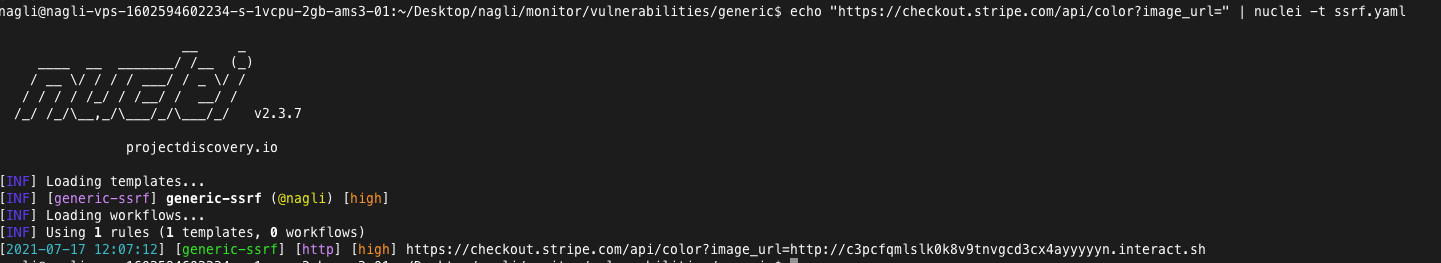 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 gokulapap/reconator
Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…
 wattocyber/bug-bounty-library
Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 bikini/exploitarium
Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
 google/clusterfuzz
Scalable fuzzing infrastructure with coverage-guided engines (libFuzzer, AFL, Honggfuzz), automated crash deduplication, bug filing, and regression…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 google/boringssl
Fork of OpenSSL implementing TLS, cryptographic primitives, and X.509 certificate handling for use in Chrome and Android, with no API/ABI…
 snort3/snort3
Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 portswigger/turbo-intruder
High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 jonathansalwan/vmprotect-devirtualization
Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.