

CVE-2024-40725
 soltanali0/cve-2024-40725
exploit CVE-2024-40725 (Apache httpd) with
exploitationfuzzingpenetration-testing+3
soltanali0/cve-2024-40725exploit CVE-2024-40725 (Apache httpd) with
 n0kovo/danish_phone_wordlist_generator
Generate wordlists of Danish phone numbers by area and/or usage (Mobile, landline etc.) Useful for password cracking or fuzzing Danish targets.
 cyber-defence-campus/netgear_r6700v3_circled
Demonstrate some functionalities of Morion by generating an exploit for CVE-2022-27646 (stack buffer overflow on Netgear R6700v3 routers).
 antogit-sys/cve-2018-7449
simple Python exploit using CVE-2018-7449 on embOS/IP FTP Server v3.22
 grp-ops/react2shell
Lightweight scanner and Nuclei templates for identifying React and Next.js deserialization RCEs (CVE-2025-55182 / CVE-2025-66478).
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
 hmrumman777-beep/netaudit-iot
Research-driven UPnP vulnerability scanner focusing on libupnp 1.6.19 and CVE-2012-5958.
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…
 pfg666/dtls-fuzzer
dtls-fuzzer is a protocol-state-fuzzer for DTLS server implementations.
 ameenalkerdy/endsfuzzer
Fuzz a list of domains for specific endpoints
 dubs3c/injectus
CRLF and open redirect fuzzer
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 google/boringssl
Fork of OpenSSL implementing TLS, cryptographic primitives, and X.509 certificate handling for use in Chrome and Android, with no API/ABI…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
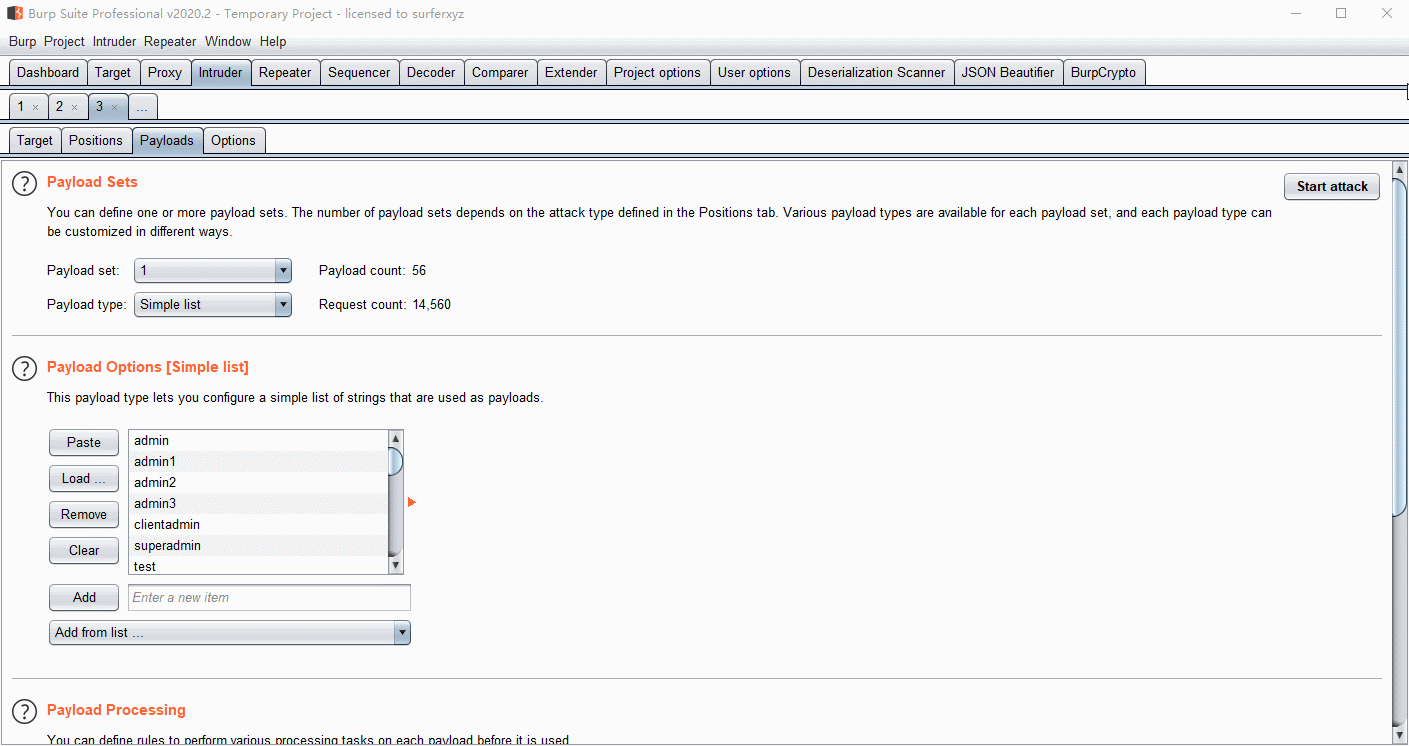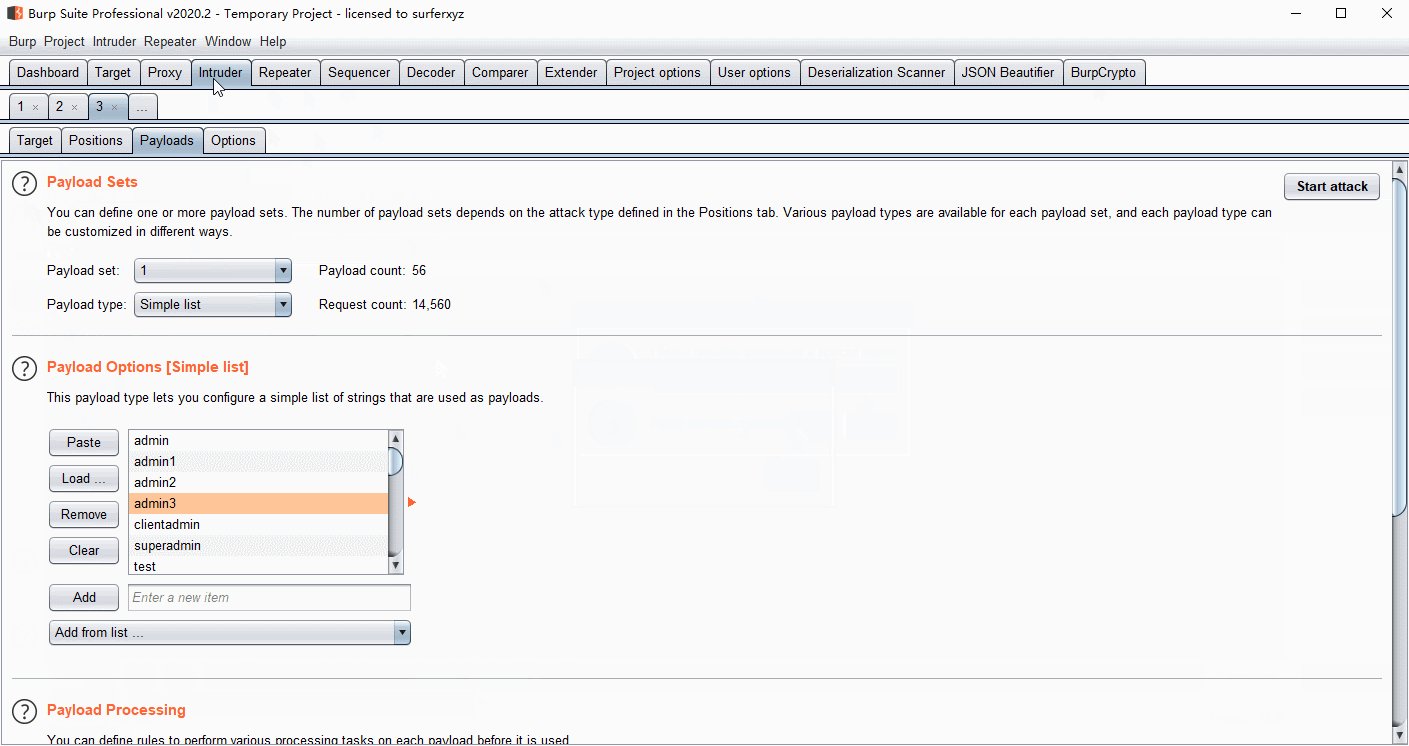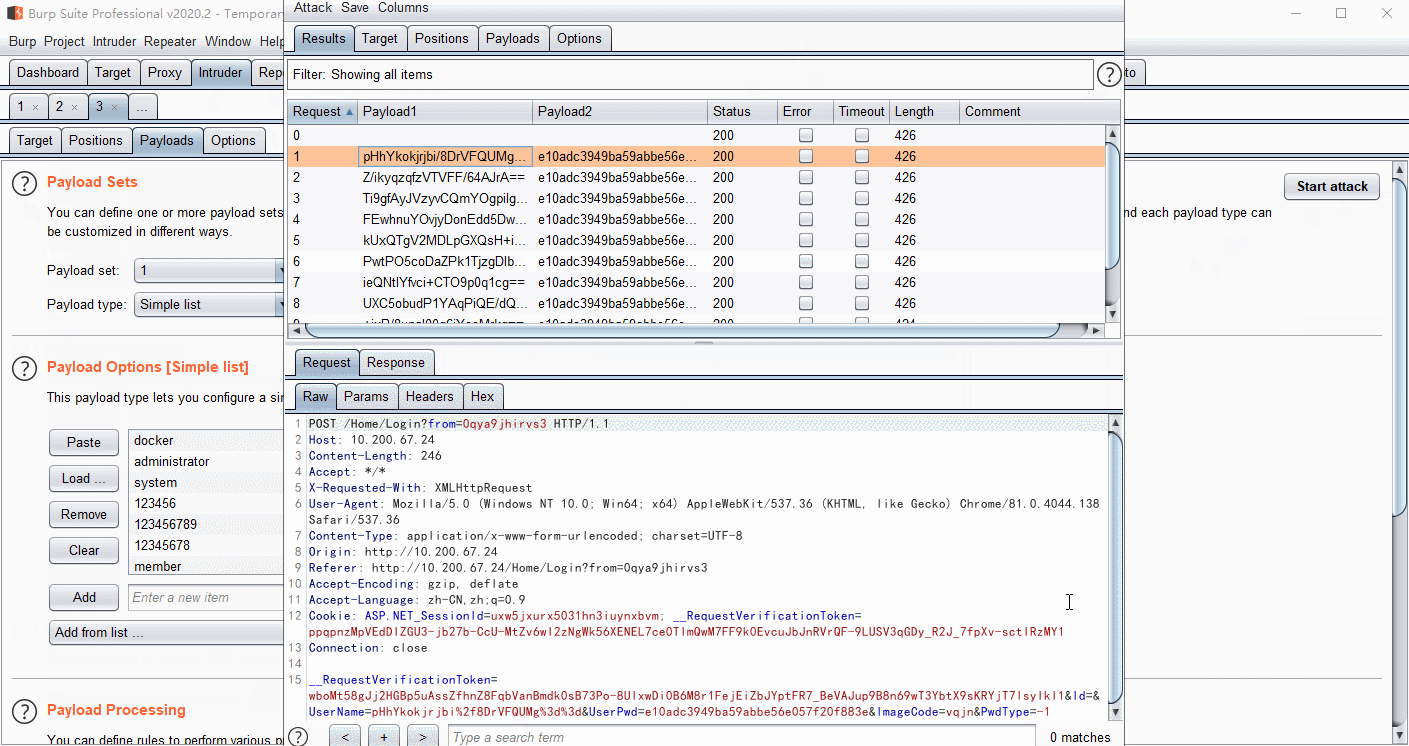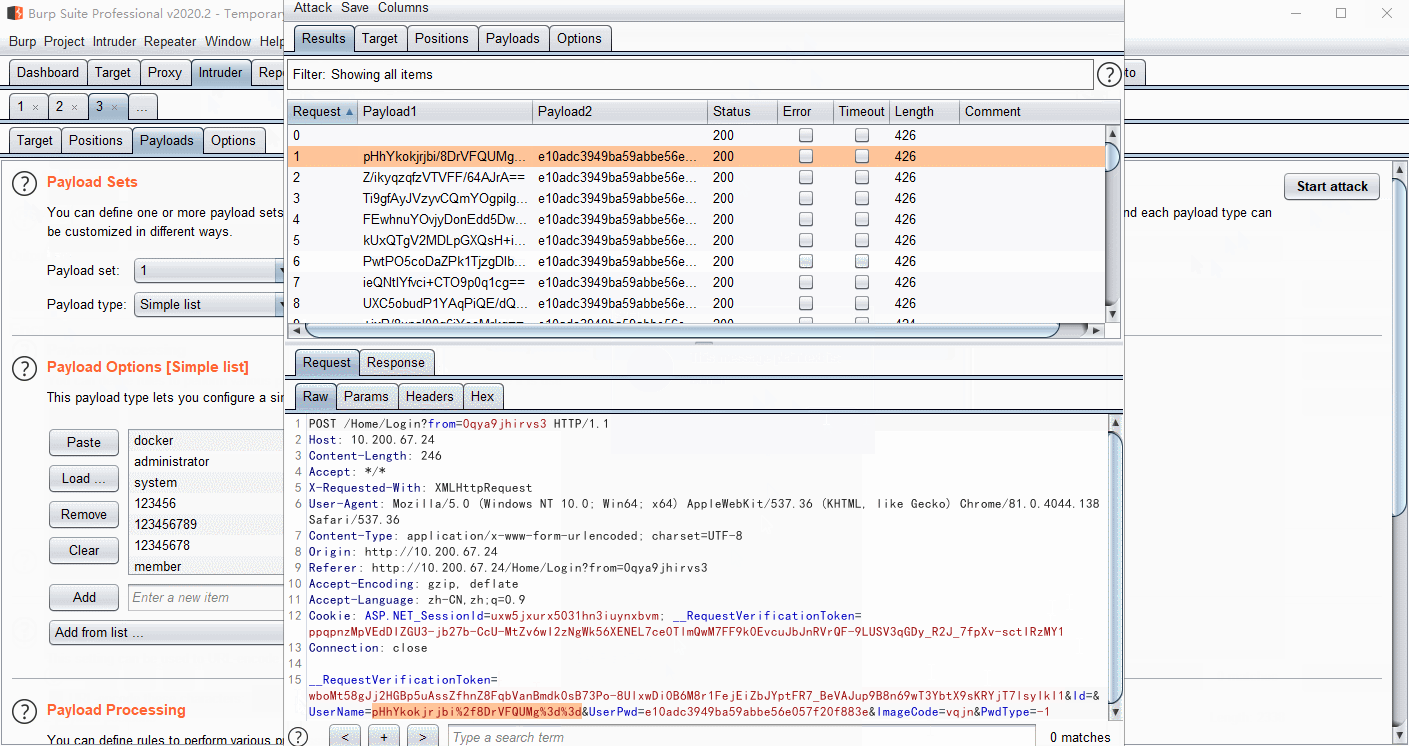 whwlsfb/burpcrypto
BurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…
 doyensec/regexploit
Find regular expressions which are vulnerable to ReDoS (Regular Expression Denial of Service)
 libssh/libssh-mirror
C library implementing the SSH protocol for secure remote access, authentication, and encrypted communication. Includes fuzzing support via OSS-Fuzz…
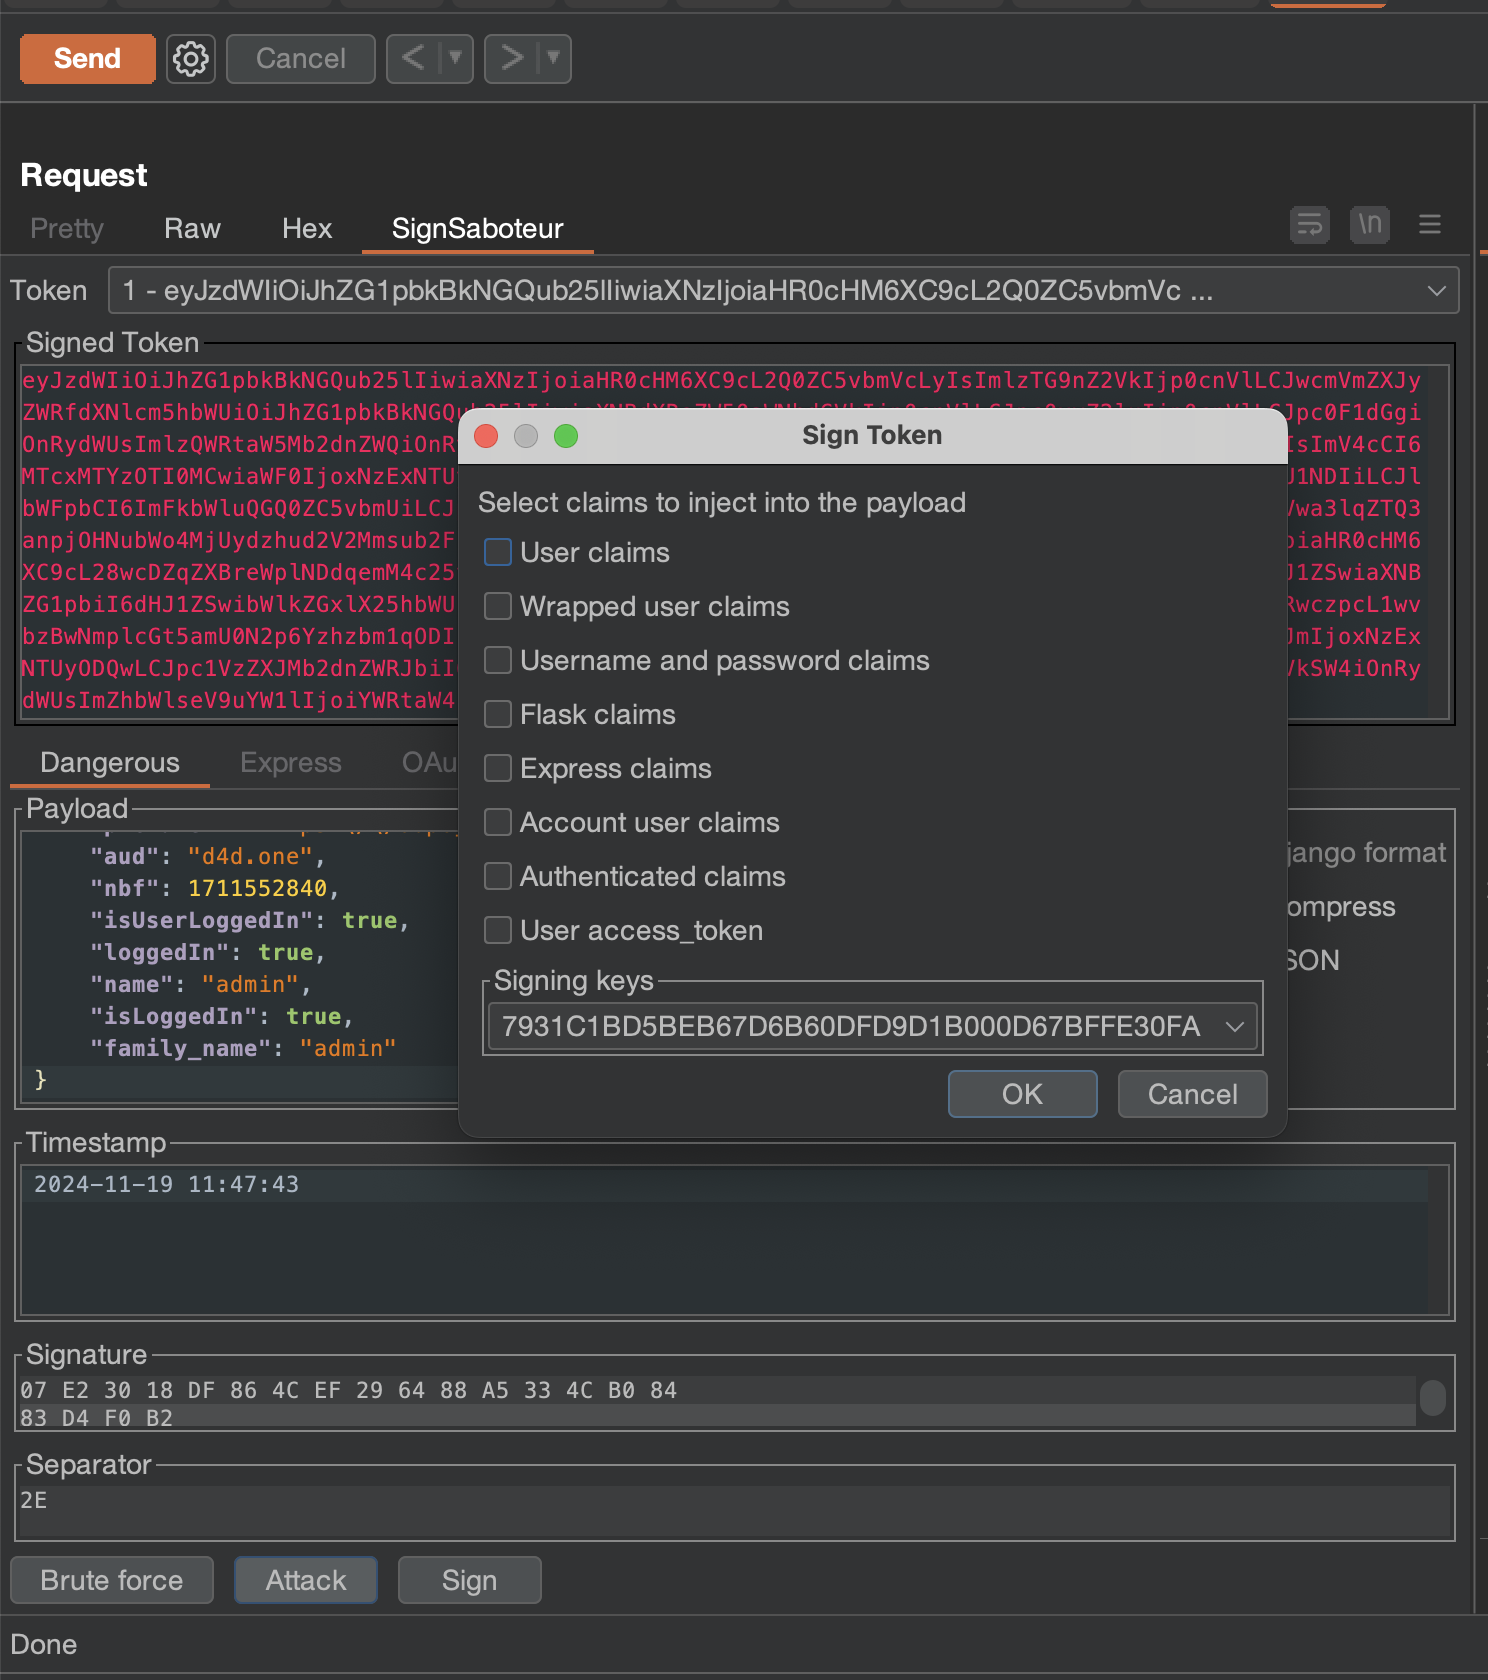 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens