
piraterf
 psyb0t/piraterf
PIrateRF transforms your Raspberry Pi Zero W into a portable RF signal generator that spawns its own WiFi hotspot. Control everything from FM…
educationembedded-systems-securityexploitation+8
274
psyb0t/piraterfPIrateRF transforms your Raspberry Pi Zero W into a portable RF signal generator that spawns its own WiFi hotspot. Control everything from FM…
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
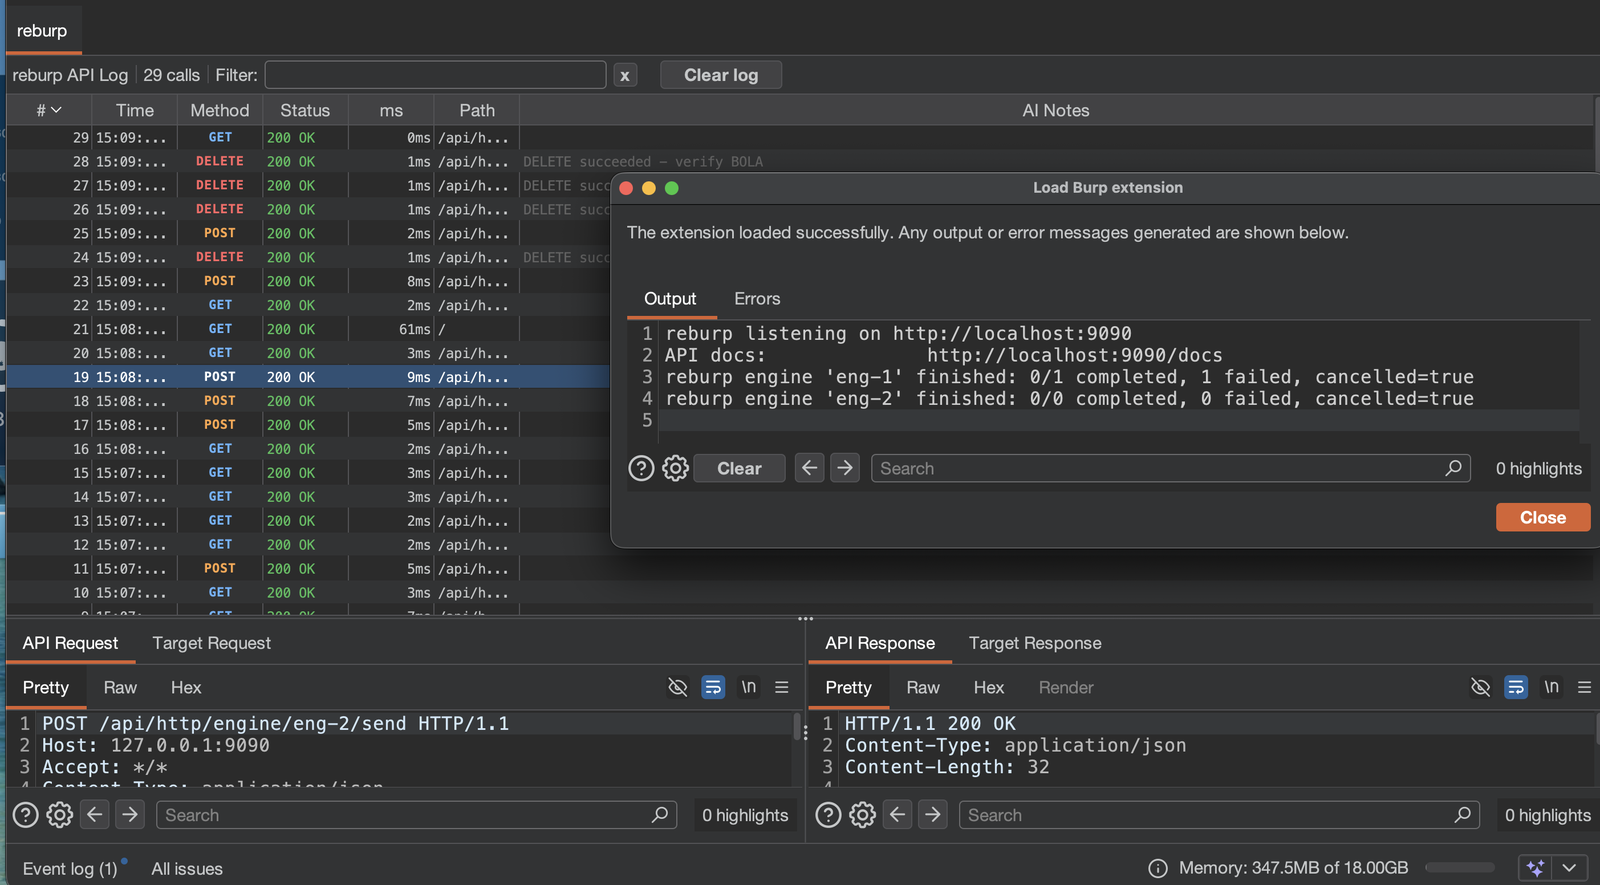 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
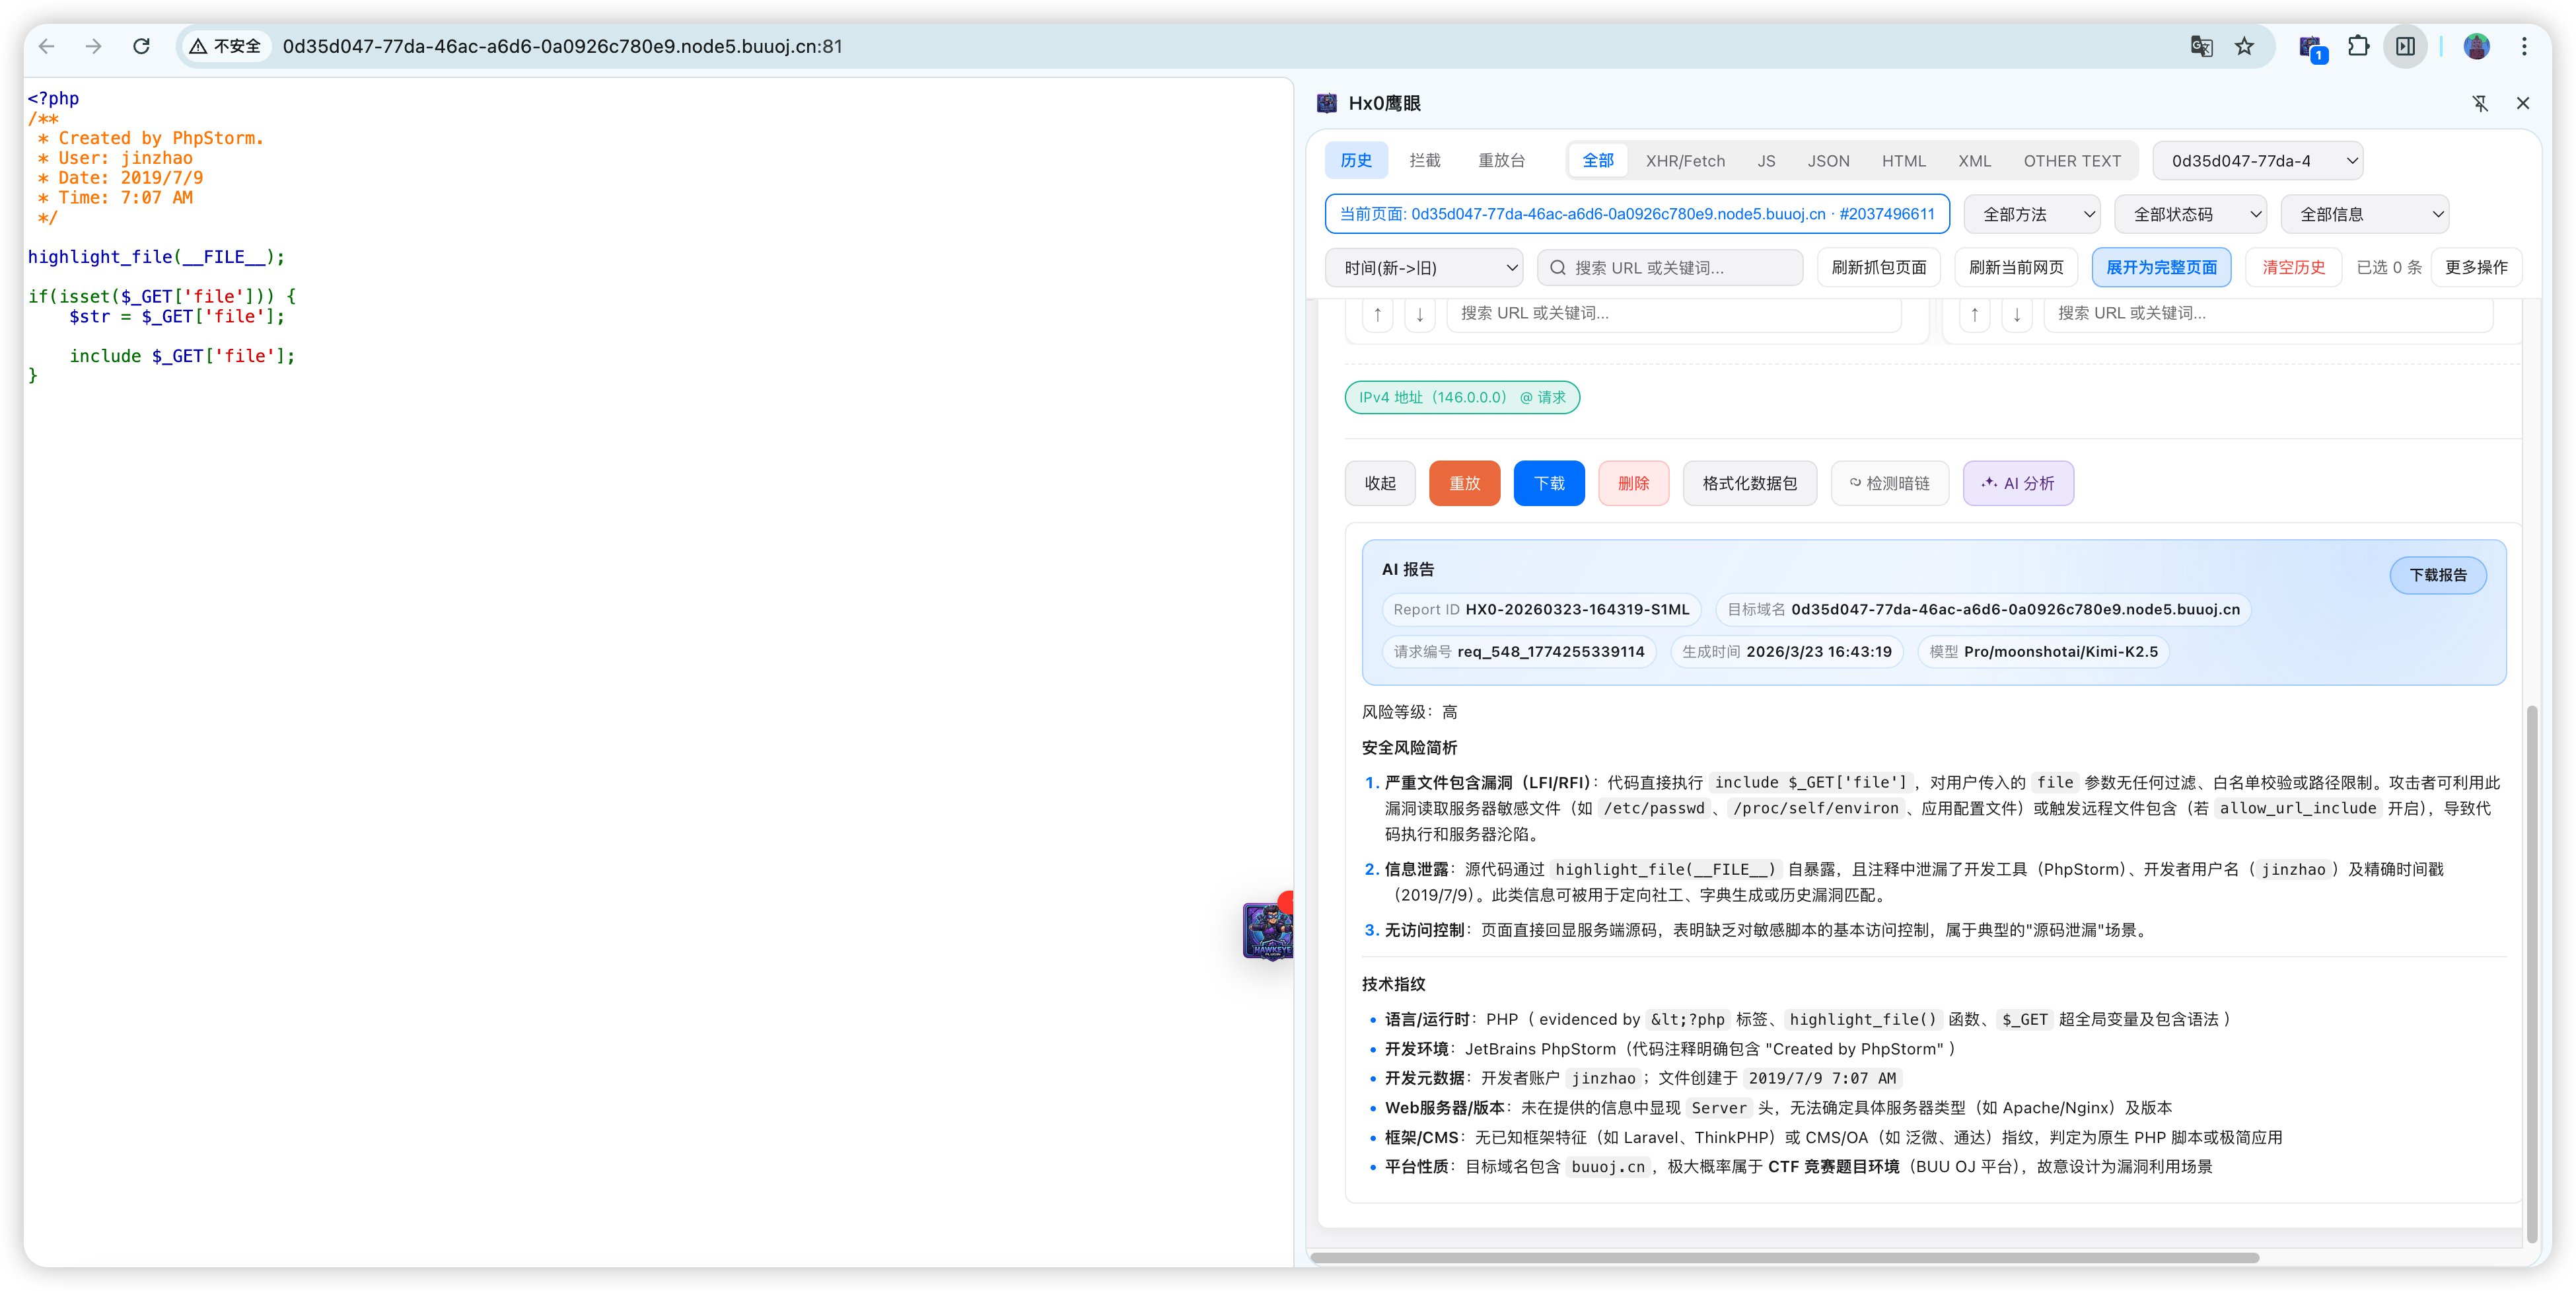 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
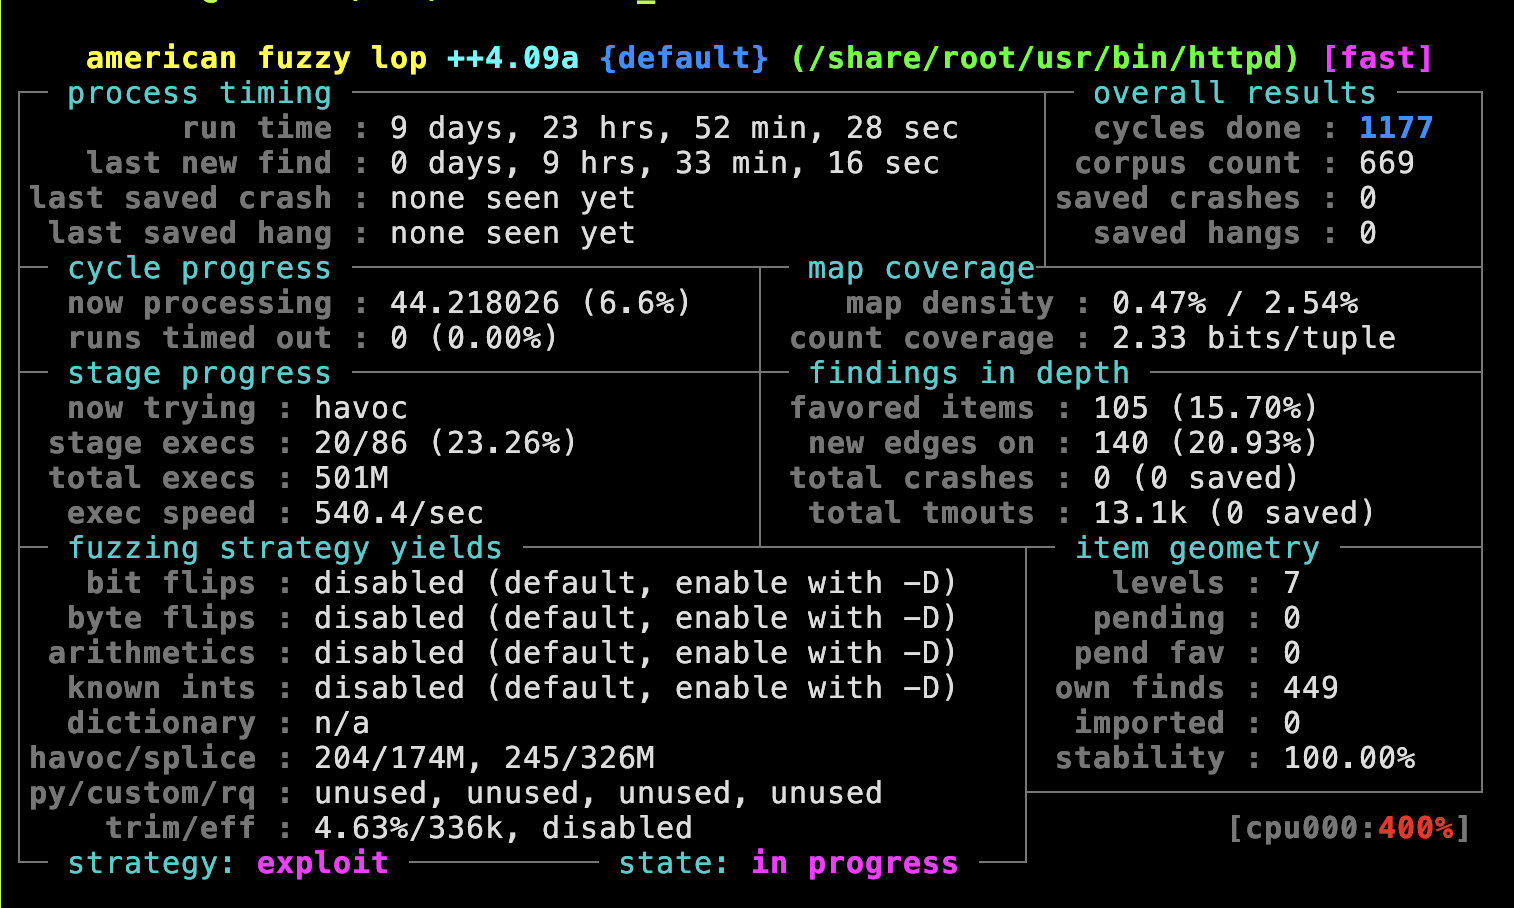 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
 gromhacks/payload-and-polyglot-lists
GromHacks Labs -- The payload lists they don't want you to have. 1,324 injection probes beamed down from the mothership to detect what's injectable…
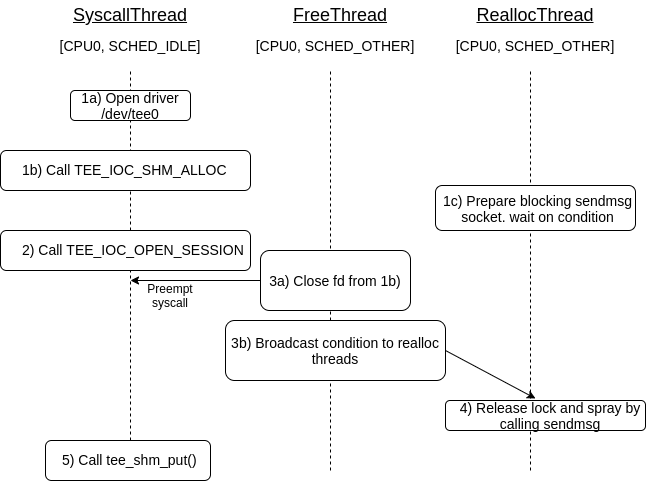 pjlantz/optee-qemu
Environment with vulnerable kernel for exploitation of the TEE driver (CVE-2021-44733)
 runzeroinc/vulns-2026-fatfs-chance
Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 0xbinder/android-kernel-exploitation-lab
This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.
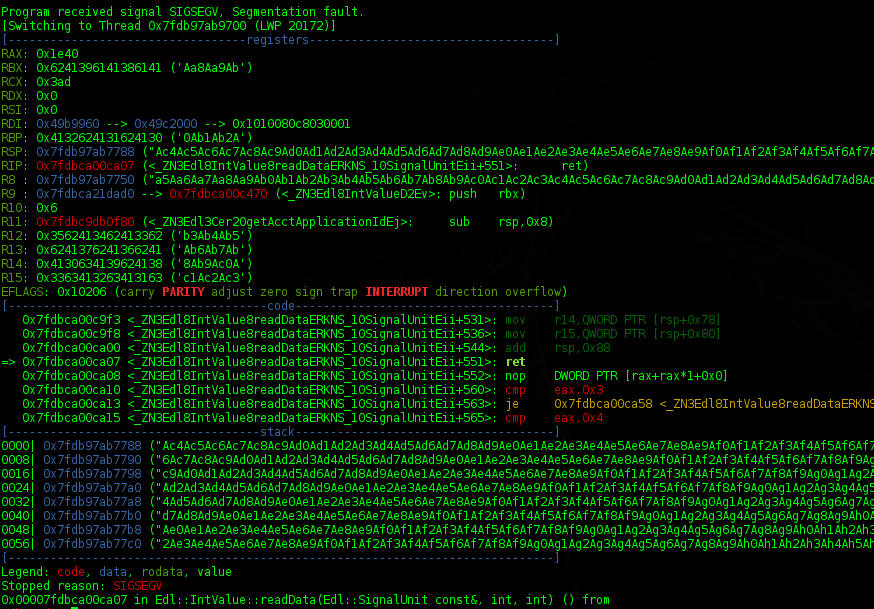 kpn-ciso/dra_writeup
Writeup of the Oracle DSR stack buffer overflow vulnerability (DRA) CVE-2014-6598
 ut-security/cve-2023-5217-poc
A PoC to trigger CVE-2023-5217 from the Browser WebCodecs or MediaRecorder interface.
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 mohammadalimehri/cve-2021-44790-lab
Dockerized Apache mod_lua lab with a Python PoC reproducing the CVE-2021-44790 multipart boundary buffer overflow for local defensive testing and…
 nexxus67/cve-2010-1938
A simple Python script to test an off-by-one vulnerability in the OPIE library (CVE-2010-1938). This vulnerability affects certain FTP servers and…
 bobfuzzer/cve-2019-18885
Proof-of-concept for a null pointer dereference in the Linux kernel BTRFS filesystem (CVE-2019-18885), including a crafted image, reproduction steps,…