

http-terminator
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
ai-securityexploitationfuzzing+8
129
portswigger/http-terminatorAI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…

 malqr/malqr.github.io
MalQR is a collection of malicious QR Codes and Barcodes you can use to test the security of your scanners.

 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
 chenaotian/cve-2023-0386
Local privilege escalation exploit for CVE-2023-0386 targeting Linux kernel overlayfs. Includes detailed vulnerability analysis, PoC code, and…
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 seungsoo-lee/delta
PROJECT DELTA: SDN SECURITY EVALUATION FRAMEWORK
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
 nccgroup/memscan
Searches for strings, regex, credit card numbers of magnetic stripe card tracks in a Windows process's memory space
 ethicalhackingplayground/wordlistgen
Generates target specific word lists for Fuzzing with fuff
 ikkisoft/bradamsa
Burp Suite extension to generate Intruder payloads using Radamsa
 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
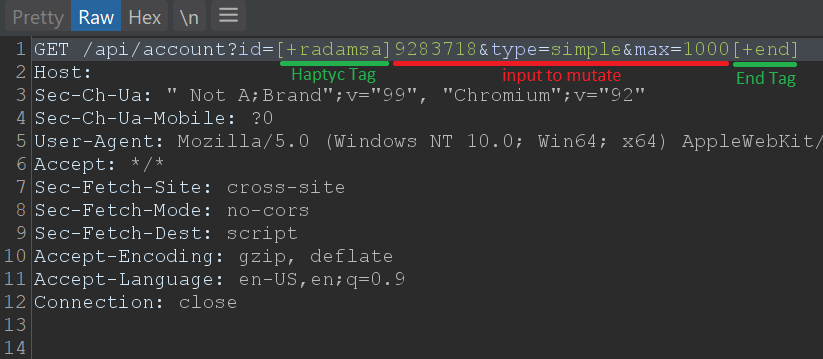 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…