
CVE-2025-5548
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
binary-exploitationdebuggerseducation+6
raulsineiro/cve-2025-5548Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 spiralbl0ck/cve-2020-11097-poc
POC TO CRASH FREERDP USING CVE-2020-11097
 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…
 rafaelbicas/cve-2019-11395
Proof of concept with the academic purpose to understand the Buffer Overflow vulnerability using as background the CVE-2019-11395
 syaifulandy/cve-2024-38475
CVE-2024-38475 Scanner using FFUF + Seclists

 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
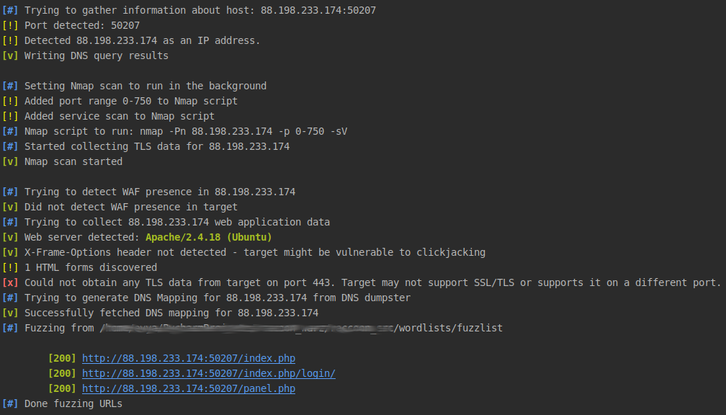 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
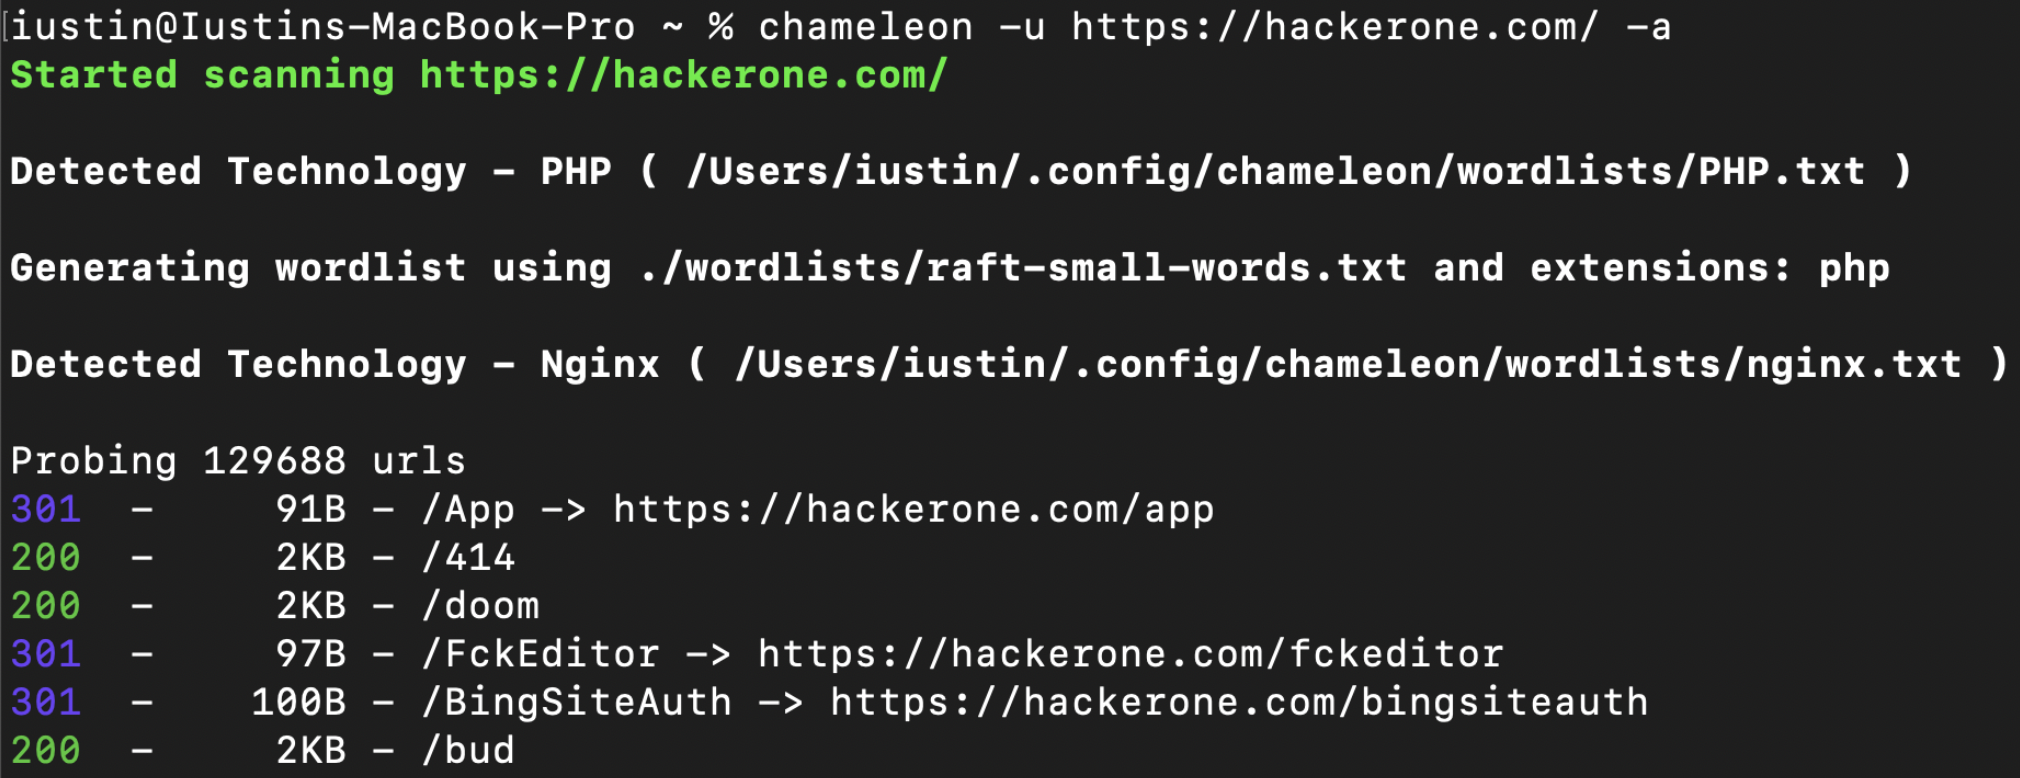 iustin24/chameleon
Technology-aware web content discovery scanner: detects Wappalyzer fingerprints, adapts wordlists/extensions, and performs fast directory bruteforce…
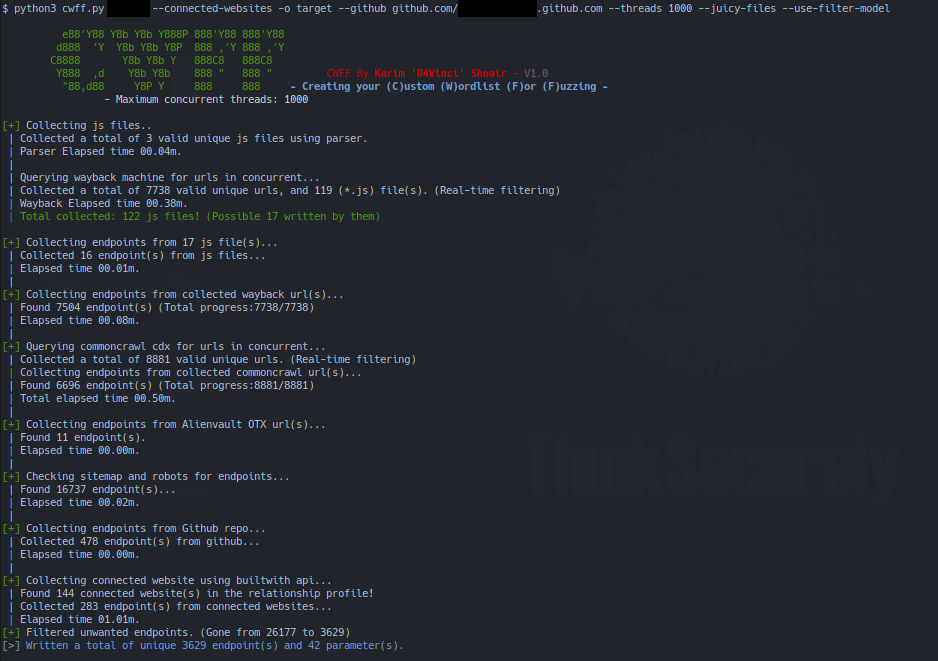 d4vinci/cwff
Create your Custom Wordlist For Fuzzing
 qualcomm/afltriage
Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
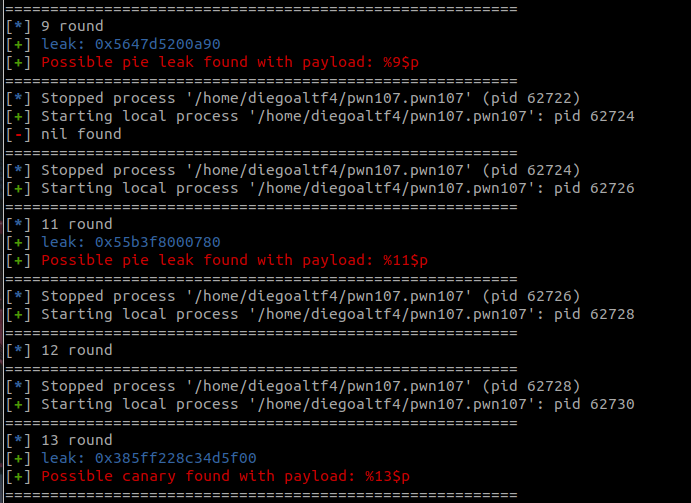 diego-altf4/glufs
Automated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…
 mk219533/cve-2010-1205
sample exploit of buffer overflow in libpng
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 0linear/cve-2026-62958
Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.