
ioctlance
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4733 months ago
zeze-zeze/ioctlanceA tool that is used to hunt vulnerabilities in x64 WDM drivers
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 ihebski/angryfuzzer
Tools for information gathering
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
 libnet/nemesis
A command-line network packet crafting and injection utility
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 uds-se/formatfuzzer
Template-driven binary format fuzzer that generates and parses valid test inputs at high speed, with AFL++ integration for coverage-guided fuzzing.
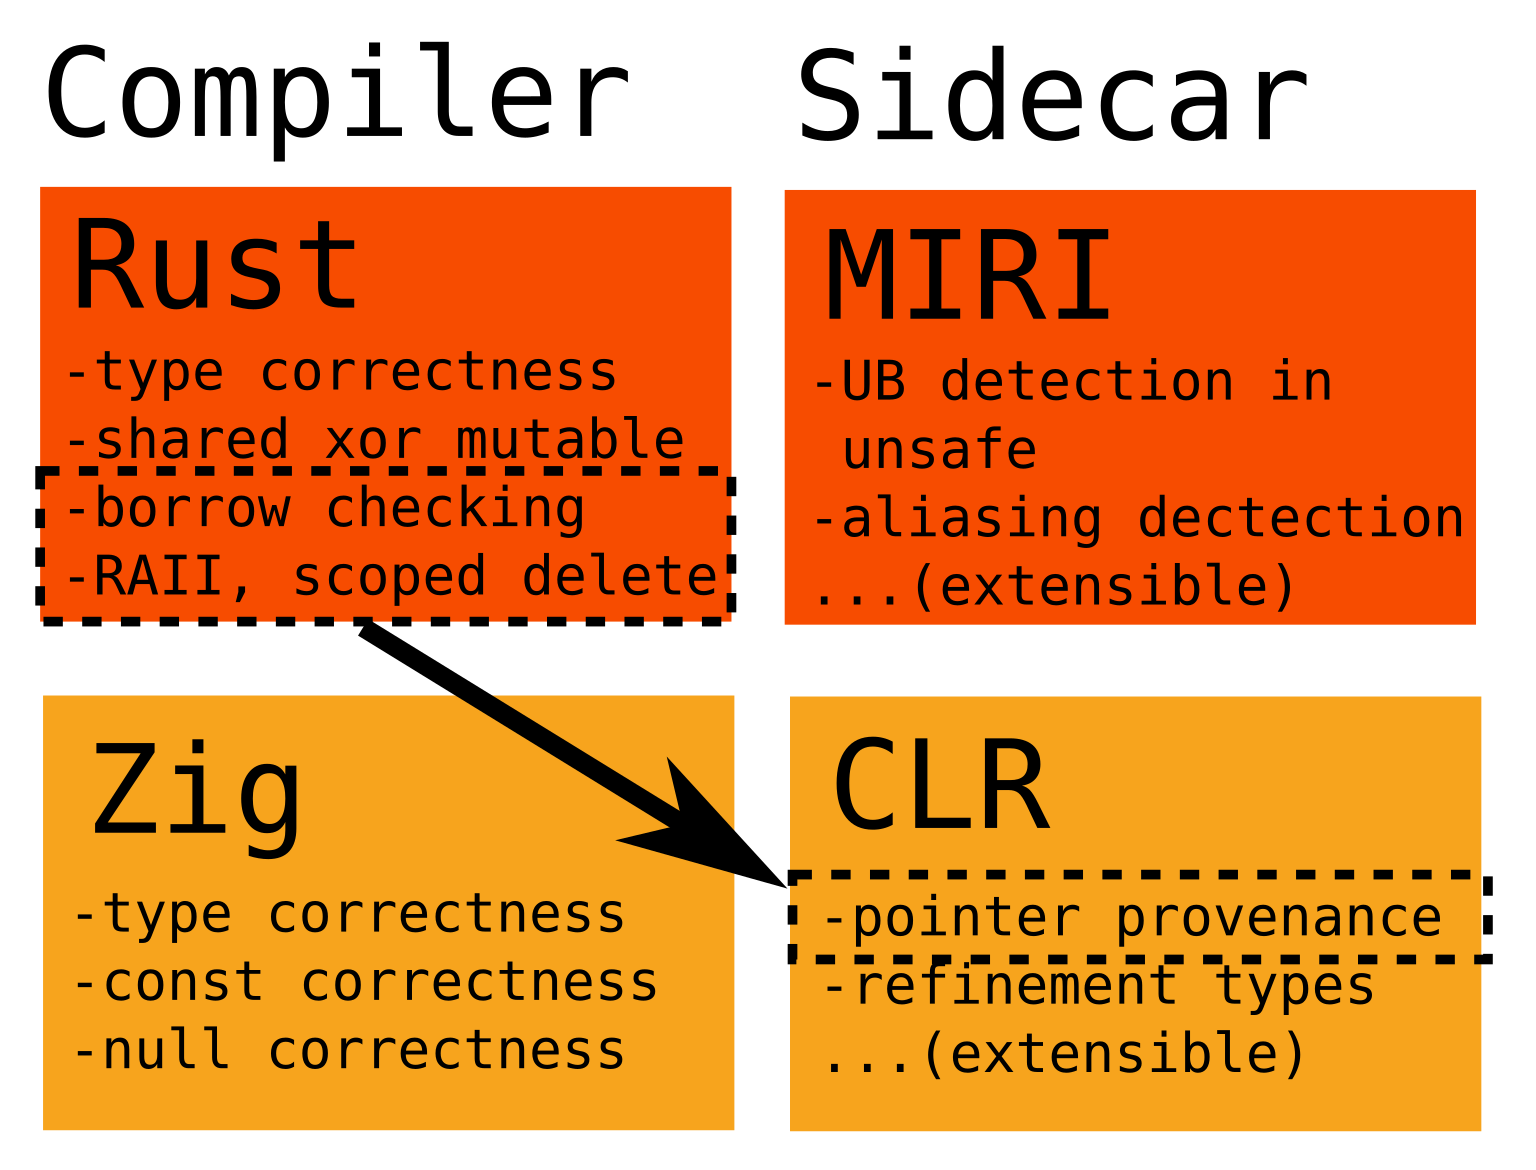 ityonemo/clr
Checker for Lifetimes and other Refinement types
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer

 gitlab-org/security-products/protocol-fuzzer-ce
This is the community edition of GitLab's protocol fuzzing framework. This framework is based on Peach Fuzzer Professional with some features removed.
 ffmancera/pentesting-multitool
Different utility scripts for pentesting and hacking.
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 bobfuzzer/cve-2019-18885
Proof-of-concept for a null pointer dereference in the Linux kernel BTRFS filesystem (CVE-2019-18885), including a crafted image, reproduction steps,…
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 horkimhab/cve-2026-442_
CVE-2026-44289, CVE-2026-44290, CVE-2026-44291, CVE-2026-44292, CVE-2026-44294, CVE-2026-44295 - protobuf.js
 elrajiii/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0
 thephykon/cve-2025-53367-poc
A simple POC of the CVE-2025-53367, creating a .djvu-file which triggers an OOB-write in the heap