

cve-2010-1938
 nexxus67/cve-2010-1938
A simple Python script to test an off-by-one vulnerability in the OPIE library (CVE-2010-1938). This vulnerability affects certain FTP servers and…
binary-exploitationeducationexploitation+3
4
nexxus67/cve-2010-1938A simple Python script to test an off-by-one vulnerability in the OPIE library (CVE-2010-1938). This vulnerability affects certain FTP servers and…
 dantsco/cve-2025-64720-poc
Proof-of-concept exploit for CVE-2025-64720, a libpng buffer overflow in palette premultiplication. Includes exploit generator, test harness with…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
 brum3ns/firefly
High-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…
 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 esentire/cve-2015-7547-public
PoC attack server for CVE-2015-7547 buffer overflow vulnerability in glibc DNS stub resolver (public version)
 praetorian-inc/augustus
LLM security testing framework for detecting prompt injection, jailbreaks, and adversarial attacks — 190+ probes, 28 providers, single Go binary
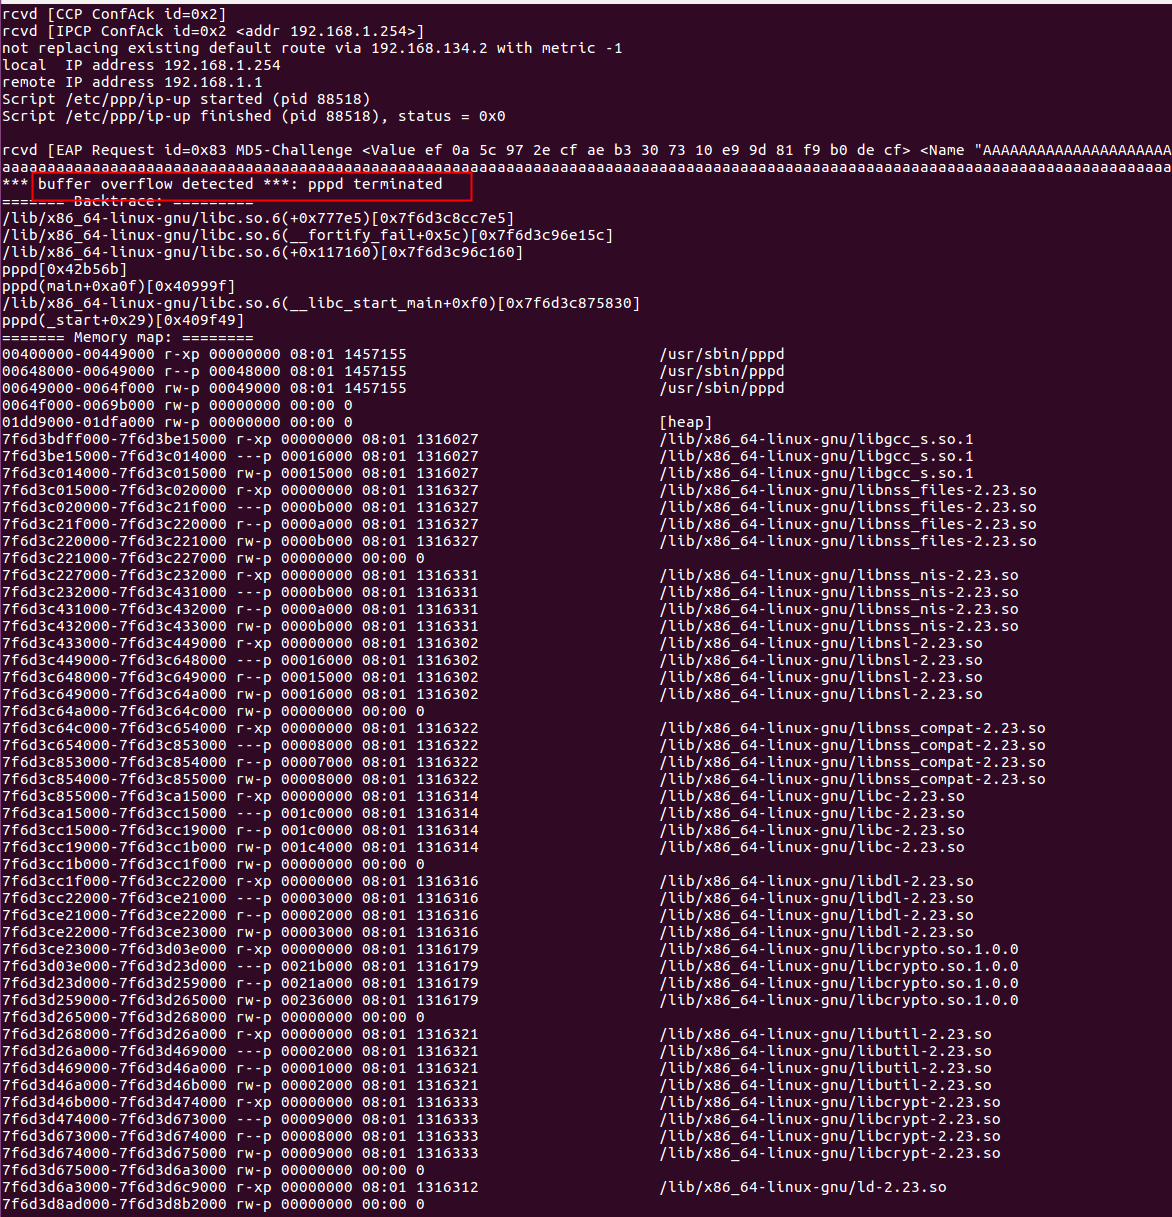 winmin/cve-2020-8597
CVE-2020-8597 pppd buffer overflow poc
 danielbohannon/invoke-dosfuscation
Cmd.exe Command Obfuscation Generator & Detection Test Harness
 dzonerzy/gowapt
Go Web Application Penetration Test
 nccgroup/blesuite
BLESuite is a Python package that provides an easier way to test Bluetooth Low Energy (BLE) device
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
 0xricksanchez/fisy-fuzz
This is the full file system fuzzing framework that I presented at the Hack in the Box 2020 Lockdown Edition conference in April.