
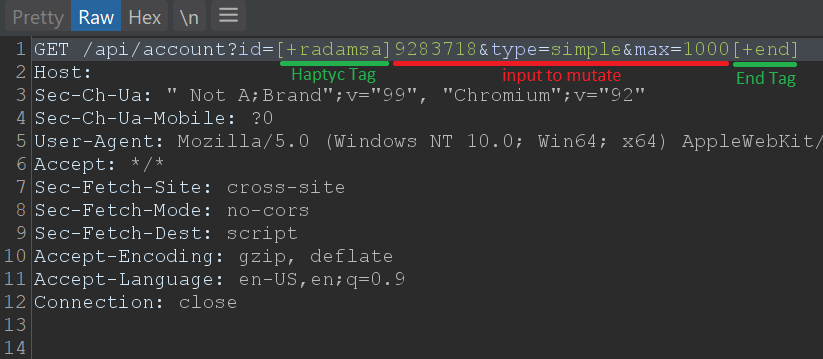
haptyc
 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
fuzzingpayload-generationpenetration-testing+1
93
defparam/haptycPython library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 ethicalhackingplayground/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 bishopfox/cve-2022-22274_cve-2023-0656
Proof-of-concept exploit for SonicWall SonicOS stack-based buffer overflows (CVE-2022-22274, CVE-2023-0656) that tests and triggers crashes via…
 fatmo666/cve-2023-38545-libcurl-socks5-heap-buffer-overflow
Proof-of-concept exploit for CVE-2023-38545, a heap buffer overflow in libcurl's SOCKS5 proxy handshake triggered via a malicious HTTP 301 redirect…
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 12lie20/cve-2026-23918-test
This repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 themalwareguardian/cve-2020-13768
Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 fzbacon/cve-2023-26976_tenda_ac6_stack_overflow
Proof-of-concept exploit for CVE-2023-26976, a stack overflow vulnerability in Tenda AC6 routers, enabling remote code execution via crafted HTTP…
 yang-shun-yu/cve-2023-38545
Proof-of-concept exploit for CVE-2023-38545, a curl heap buffer overflow. Includes SOCKS5 proxy and HTTP server to trigger the vulnerability and…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 sirredbeard/cve-2025-60876
Behavior-preserving fix for CVE-2025-60876 HTTP header injection in BusyBox wget, with proof-of-concept, percent-encoding patch, and upstream…
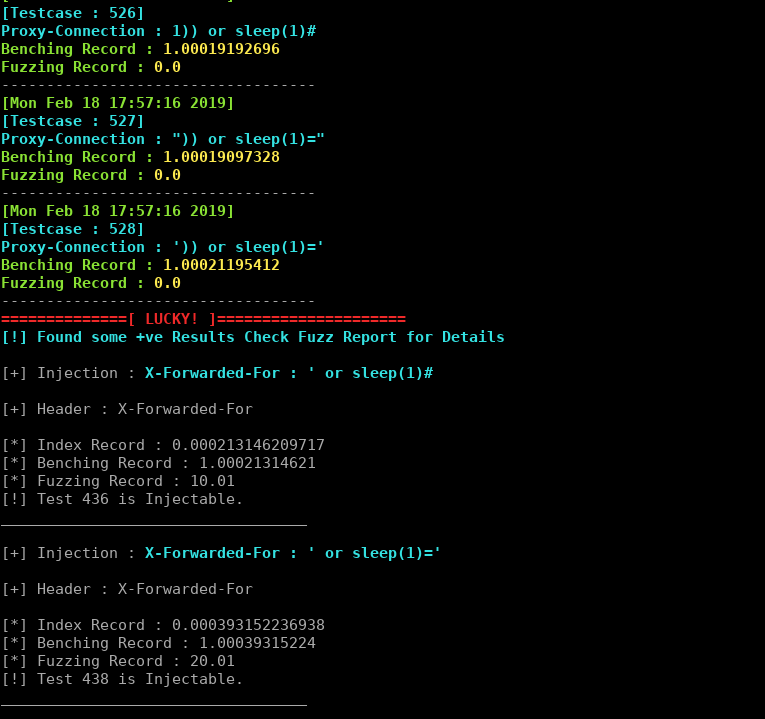 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 samsung/cotopaxi
Set of tools for security testing of Internet of Things devices using specific network IoT protocols
 bahruzjabiyev/t-reqs
Grammar-based HTTP/1 fuzzer with mutation ability
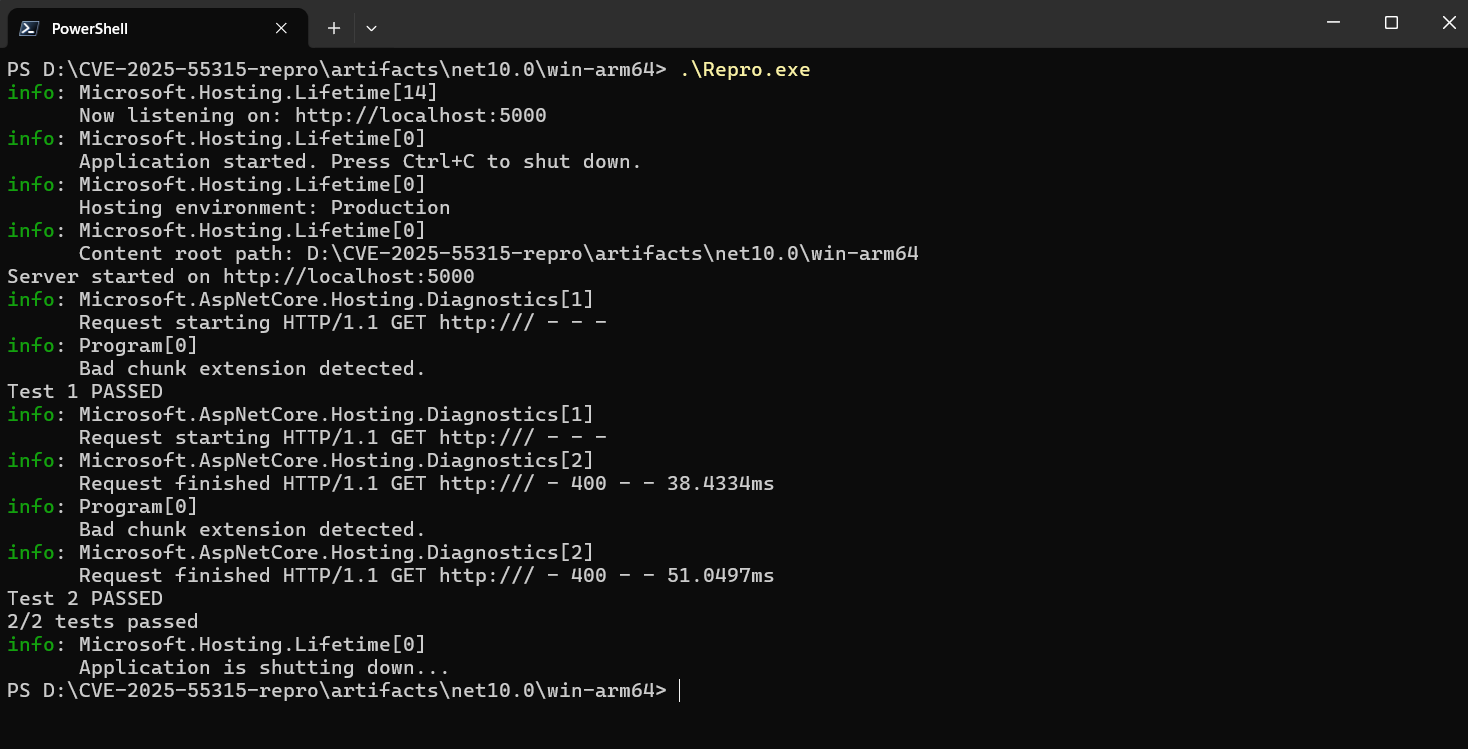 sirredbeard/cve-2025-55315-repro
Tool that reproduces CVE-2025-55315 in ASP.NET Core.