
CVE-2025-51495
 cainiao159357/cve-2025-51495
Proof-of-concept exploit for CVE-2025-51495, an integer overflow in Mongoose WebSocket's mg_ws_cb function leading to out-of-bounds memory access and…
binary-exploitationexploitationfuzzing+3
cainiao159357/cve-2025-51495Proof-of-concept exploit for CVE-2025-51495, an integer overflow in Mongoose WebSocket's mg_ws_cb function leading to out-of-bounds memory access and…
 trailofbits/umberto
Library and CLI for mutating structured data (JSON, XML, X.509) to support grammar-based fuzzing, with multiple mutation strategies and integration…
 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 narfindustries/http-garden
Differential testing framework for HTTP implementations
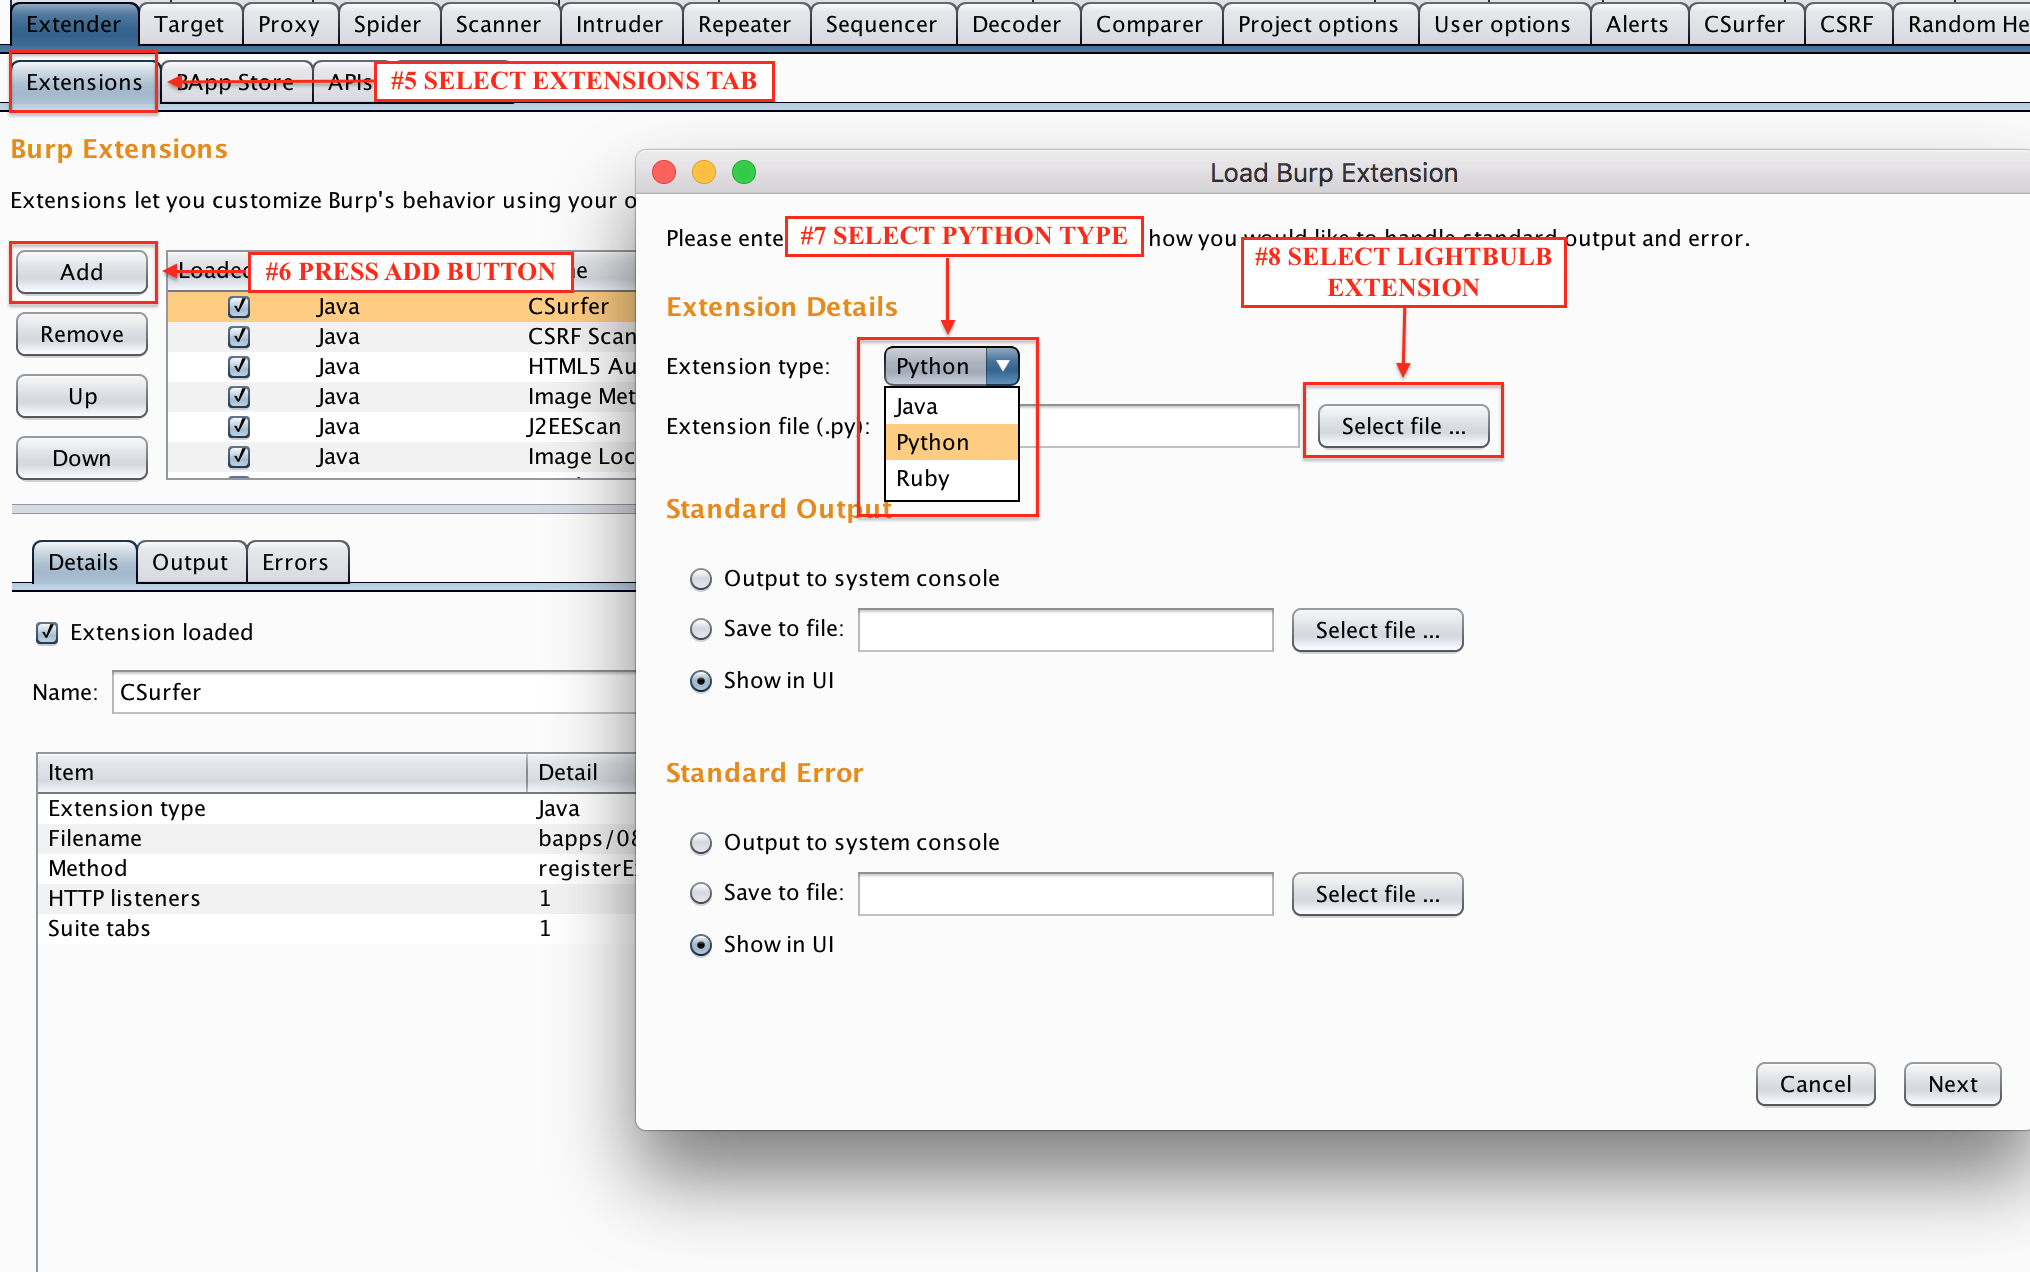 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 google/buzzer
eBPF fuzzer toolchain for generating random eBPF programs and validating kernel verifier/runtime behavior. Supports coverage-guided fuzzing and…
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 jakabakos/cve-2017-9096-itext-xxe
Proof-of-concept exploit for CVE-2017-9096 demonstrating XML External Entity (XXE) injection in iText PDF library via malicious XMP metadata and form…
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 therook/audiocaptchabypass-cve-2008-2019
Exploit for CVE-2008-2019 bypassing audio captcha in Simple Machines Forum 1.1.4 using hamming distance and levenshtein distance to compare PCM audio…
 jaf0rk/cve-2026-3909
Proof-of-concept exploit for CVE-2026-3909, a Chromium Skia out-of-bounds vulnerability, with patches and crash analysis for reliable triggering in…
 0xmid00/cve-2022-46364-poc
CVE-2022-46364 Apache CXF XOP:Include SSRF / LFI
 ubuntustrike/struts_rest_rce_fuzz-cve-2017-9805-
Simple python script to fuzz site for CVE-2017-9805
 s3mpr1linux/cve-2011-0762
Um script automatizado melhorando o exploit do cve-2011-0762 postado no exploit-db
 freefv/cve-2020-6308-mass-exploiter
Mass exploiter for CVE-2020-6308 with multi-worker support, enabling automated exploitation of vulnerable SAP NetWeaver systems.
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 nccgroup/wssip
Application for capturing, modifying and sending custom WebSocket data from client to server and vice versa.