
ci_fuzz
 mvdevnull/ci_fuzz
Command Injection Web Fuzzer Script for mitmproxy
fuzzingpenetration-testingvulnerability-analysis+1
mvdevnull/ci_fuzzCommand Injection Web Fuzzer Script for mitmproxy
 themalwareguardian/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0 illustrating how a single unsafe handler can generate multiple CVE entries across different commands.
 themalwareguardian/cve-2003-0264
Classic stack-based buffer overflow in SLMail 5.1 showing how early mail servers could be compromised through oversized SMTP and POP3 commands.
 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912

 asciimoo/exrex
Irregular methods on regular expressions
 cispa/trevex
Automated Vulnerability Detection Framework for Transient Execution Vulnerabilities (IEEE S&P '26)
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
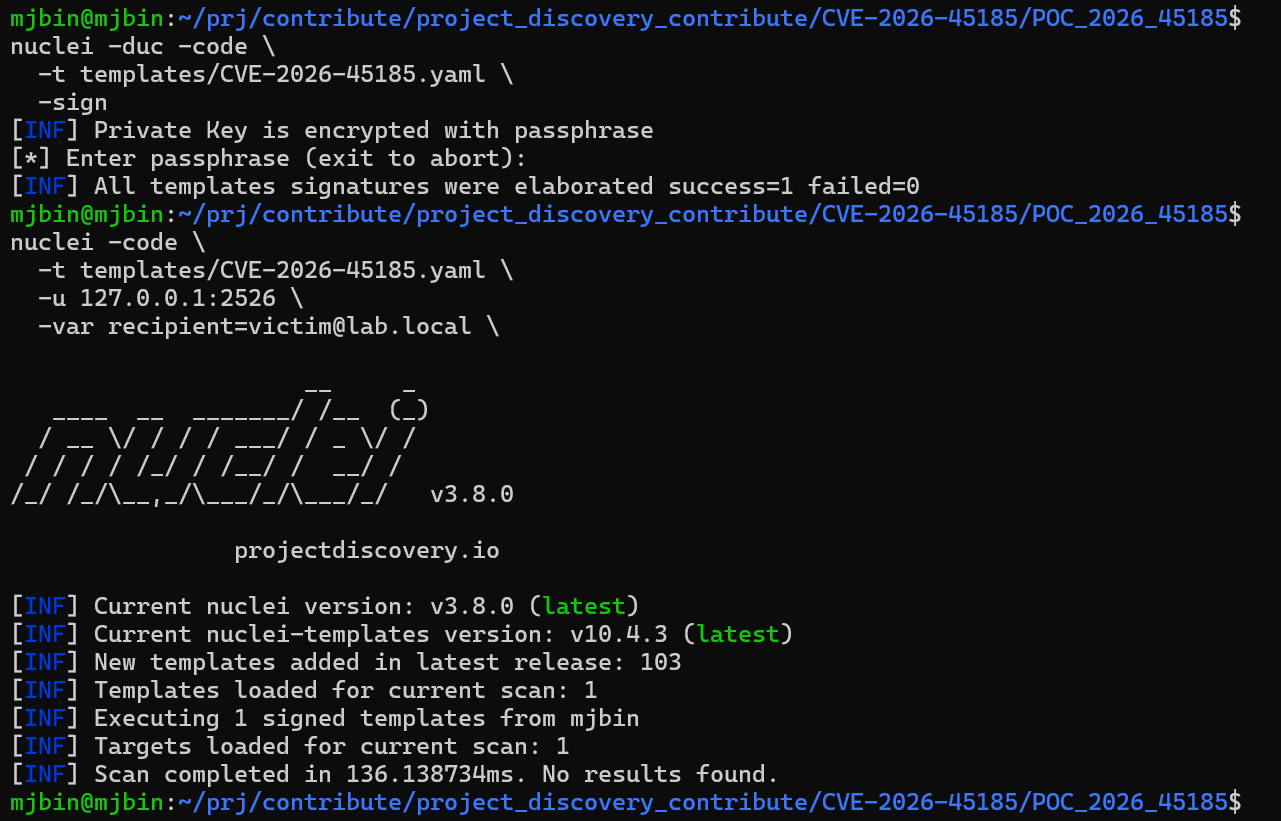 mj-bin/poc_cve-2026-45185
POC_CVE-2026-45185 for nuclei-templates
 mr-vill4in/log4j-fuzzer
Automated scanner for CVE-2021-44228 (Log4Shell) that tests single or multiple web targets for the vulnerability using remote callback servers.
 spiralbl0ck/cve-2020-11097-poc
POC TO CRASH FREERDP USING CVE-2020-11097
 s3mpr1linux/cve-2011-0762
Um script automatizado melhorando o exploit do cve-2011-0762 postado no exploit-db
 trailofbits/umberto
Library and CLI for mutating structured data (JSON, XML, X.509) to support grammar-based fuzzing, with multiple mutation strategies and integration…
 luisfontes19/xxexploiter
Tool to help exploit XXE vulnerabilities
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface