lorsrf
 mindpatch/lorsrf
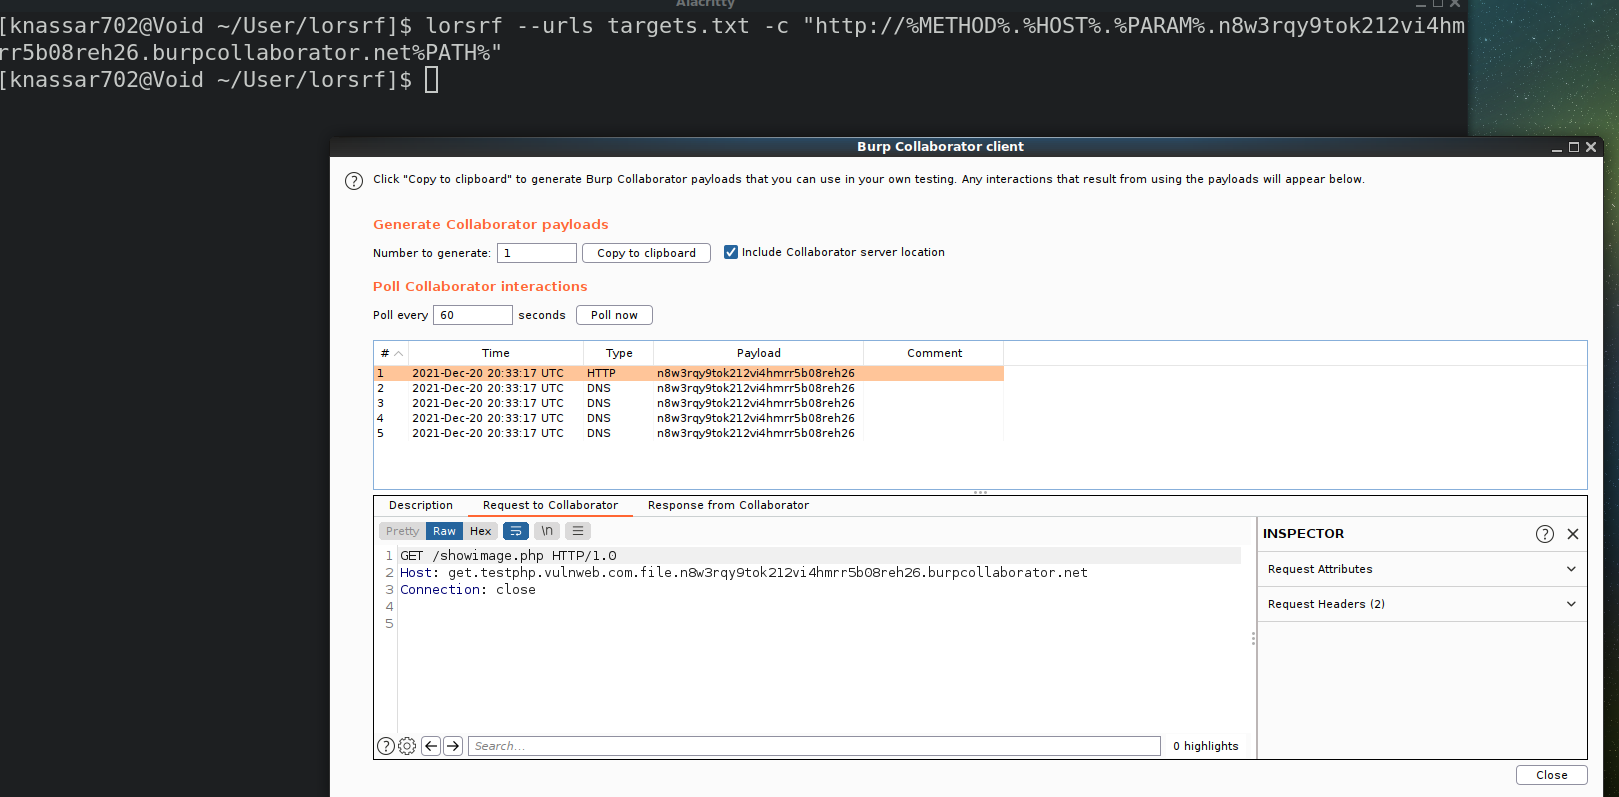
Fast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
fuzzingpenetration-testingvulnerability-scanners+1
297
mindpatch/lorsrfFast CLI tool to find the parameters that can be used to find SSRF or Out-of-band resource load :artificial_satellite: :crab:
 nescau-ufla/fuzzingtool
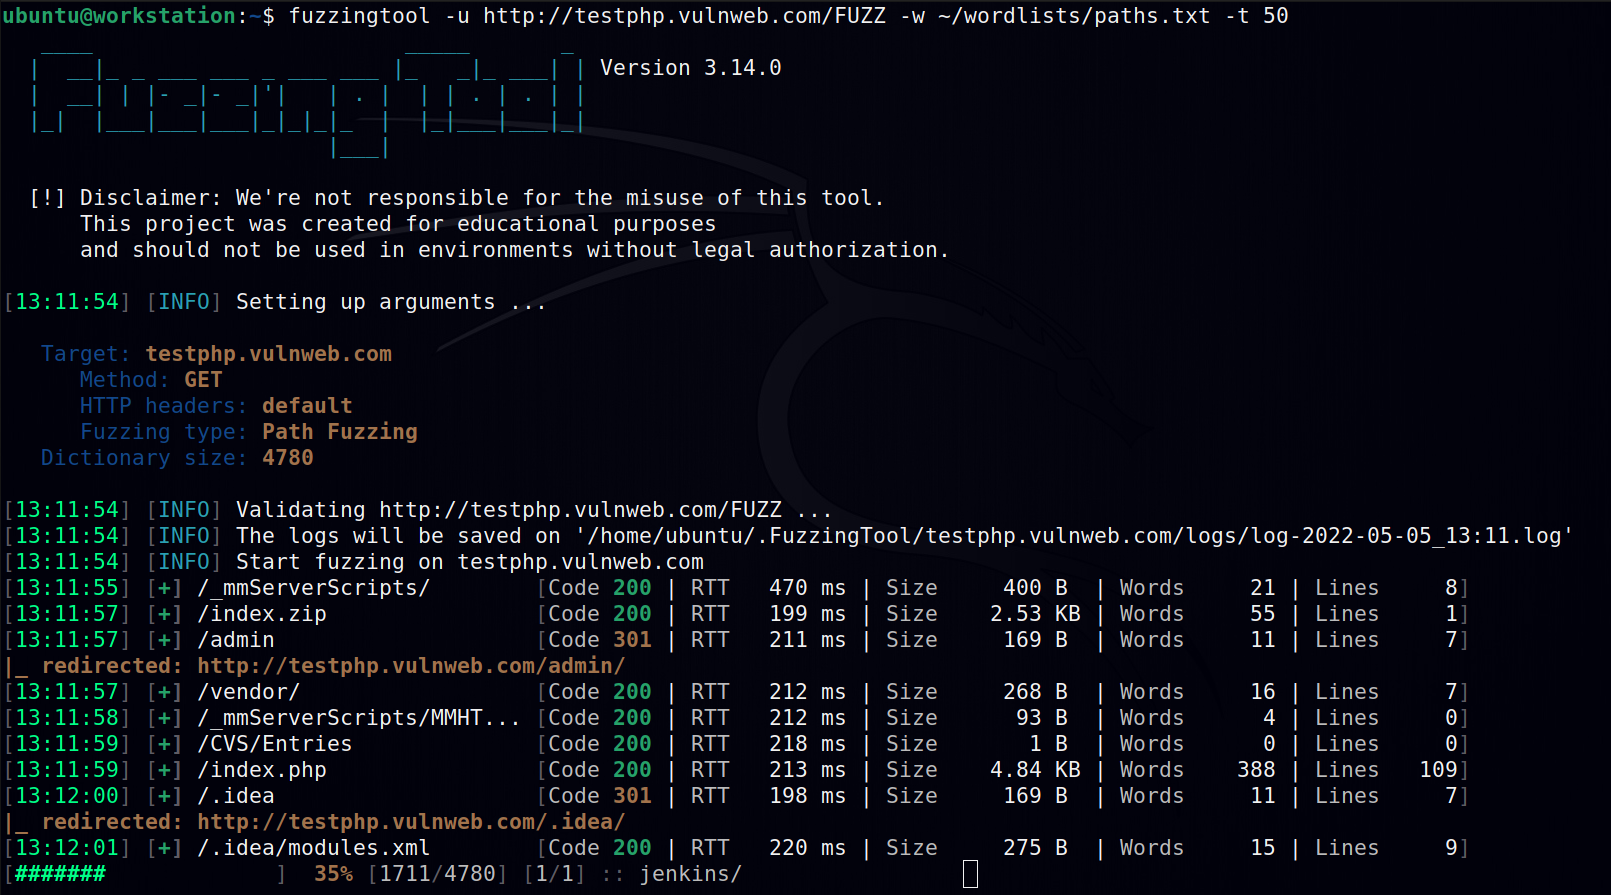
Software for fuzzing, used on web application pentestings.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 manishkanyal/log4j-scanner
A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
 damian89/extended-ssrf-search
Smart ssrf scanner using different methods like parameter brute forcing in post and get...
 brum3ns/firefly
High-performance black-box fuzzer for web applications with built-in payload engine, request verification, tampering, encoding, and advanced…
 andreiverse/vaf
Multi-threaded web fuzzer for URL path, HTTP header, and POST data brute-forcing with proxy support, status code filtering, and reflexive content…
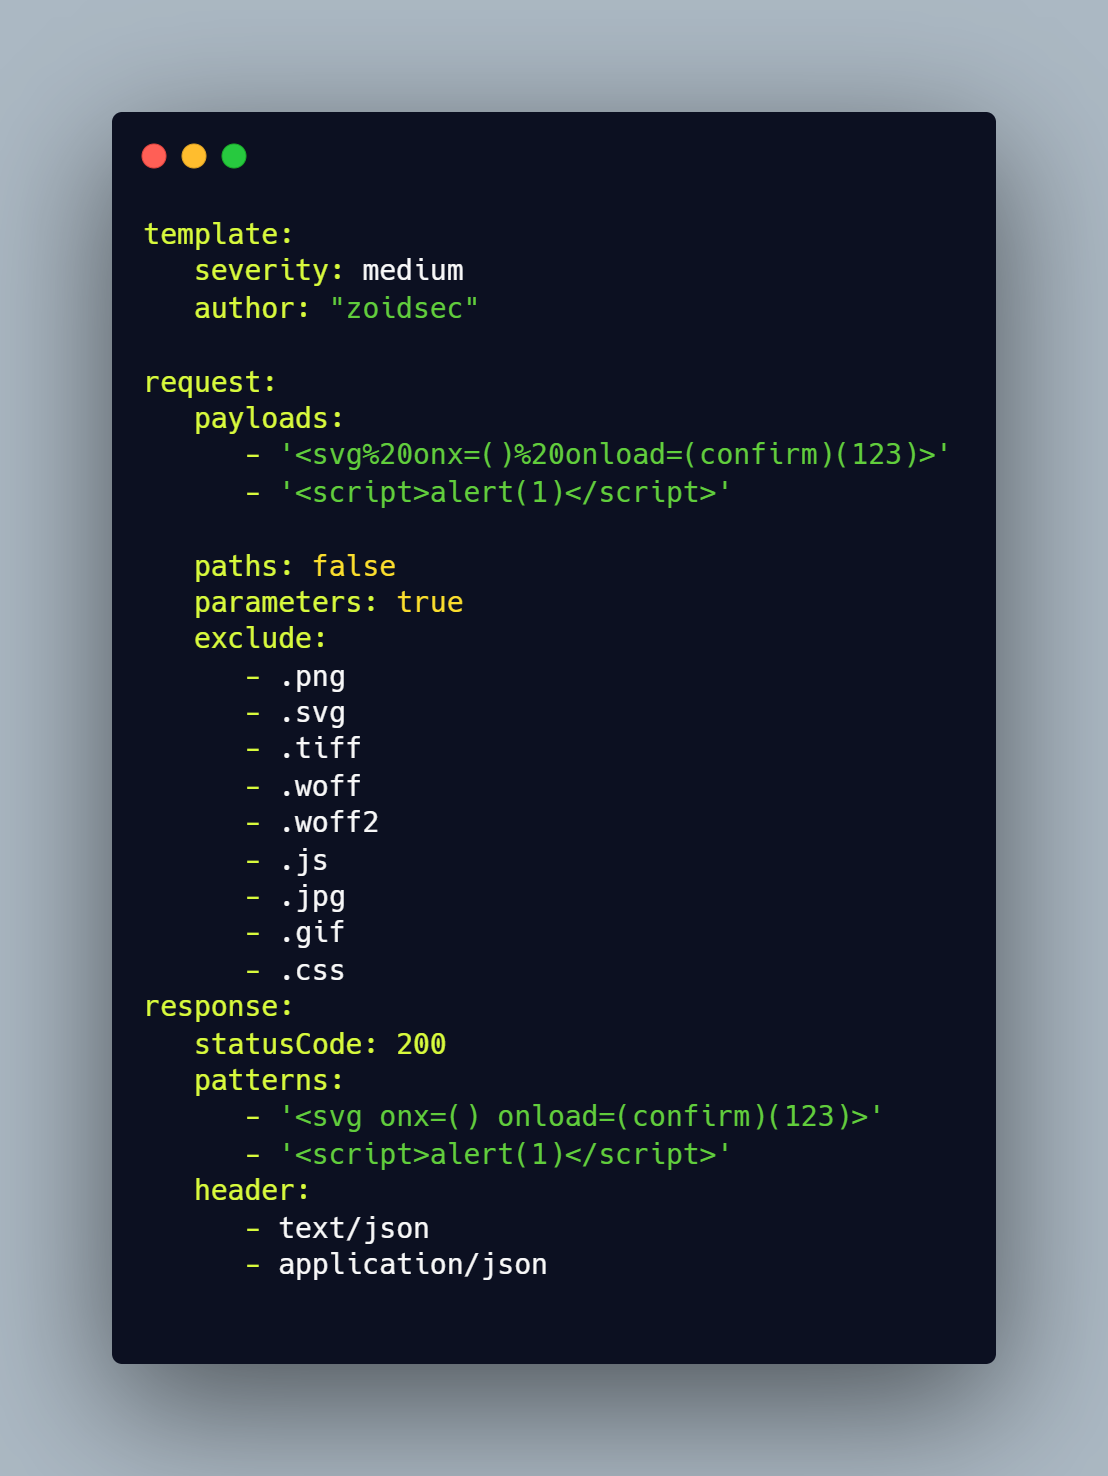 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 juanschallibaum/cve-2024-38473-nuclei-template
Nuclei template to detect Apache servers vulnerable to CVE-2024-38473
 vitaliy-grigoriev/protocol-analyzer
Fuzz testing framework for network protocols.
 soltanali0/cve-2024-40725
exploit CVE-2024-40725 (Apache httpd) with