
fuzzdb
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
curated-resourcesdns-fuzzingfuzzing+4
9.0k6 years ago
fuzzdb-project/fuzzdbDictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 portswigger/turbo-intruder
High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
 defparam/haptyc
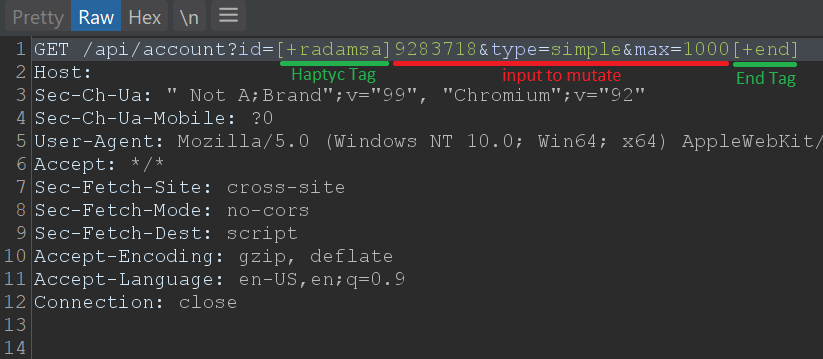
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 leviticus-triage/cerebro-red-v2
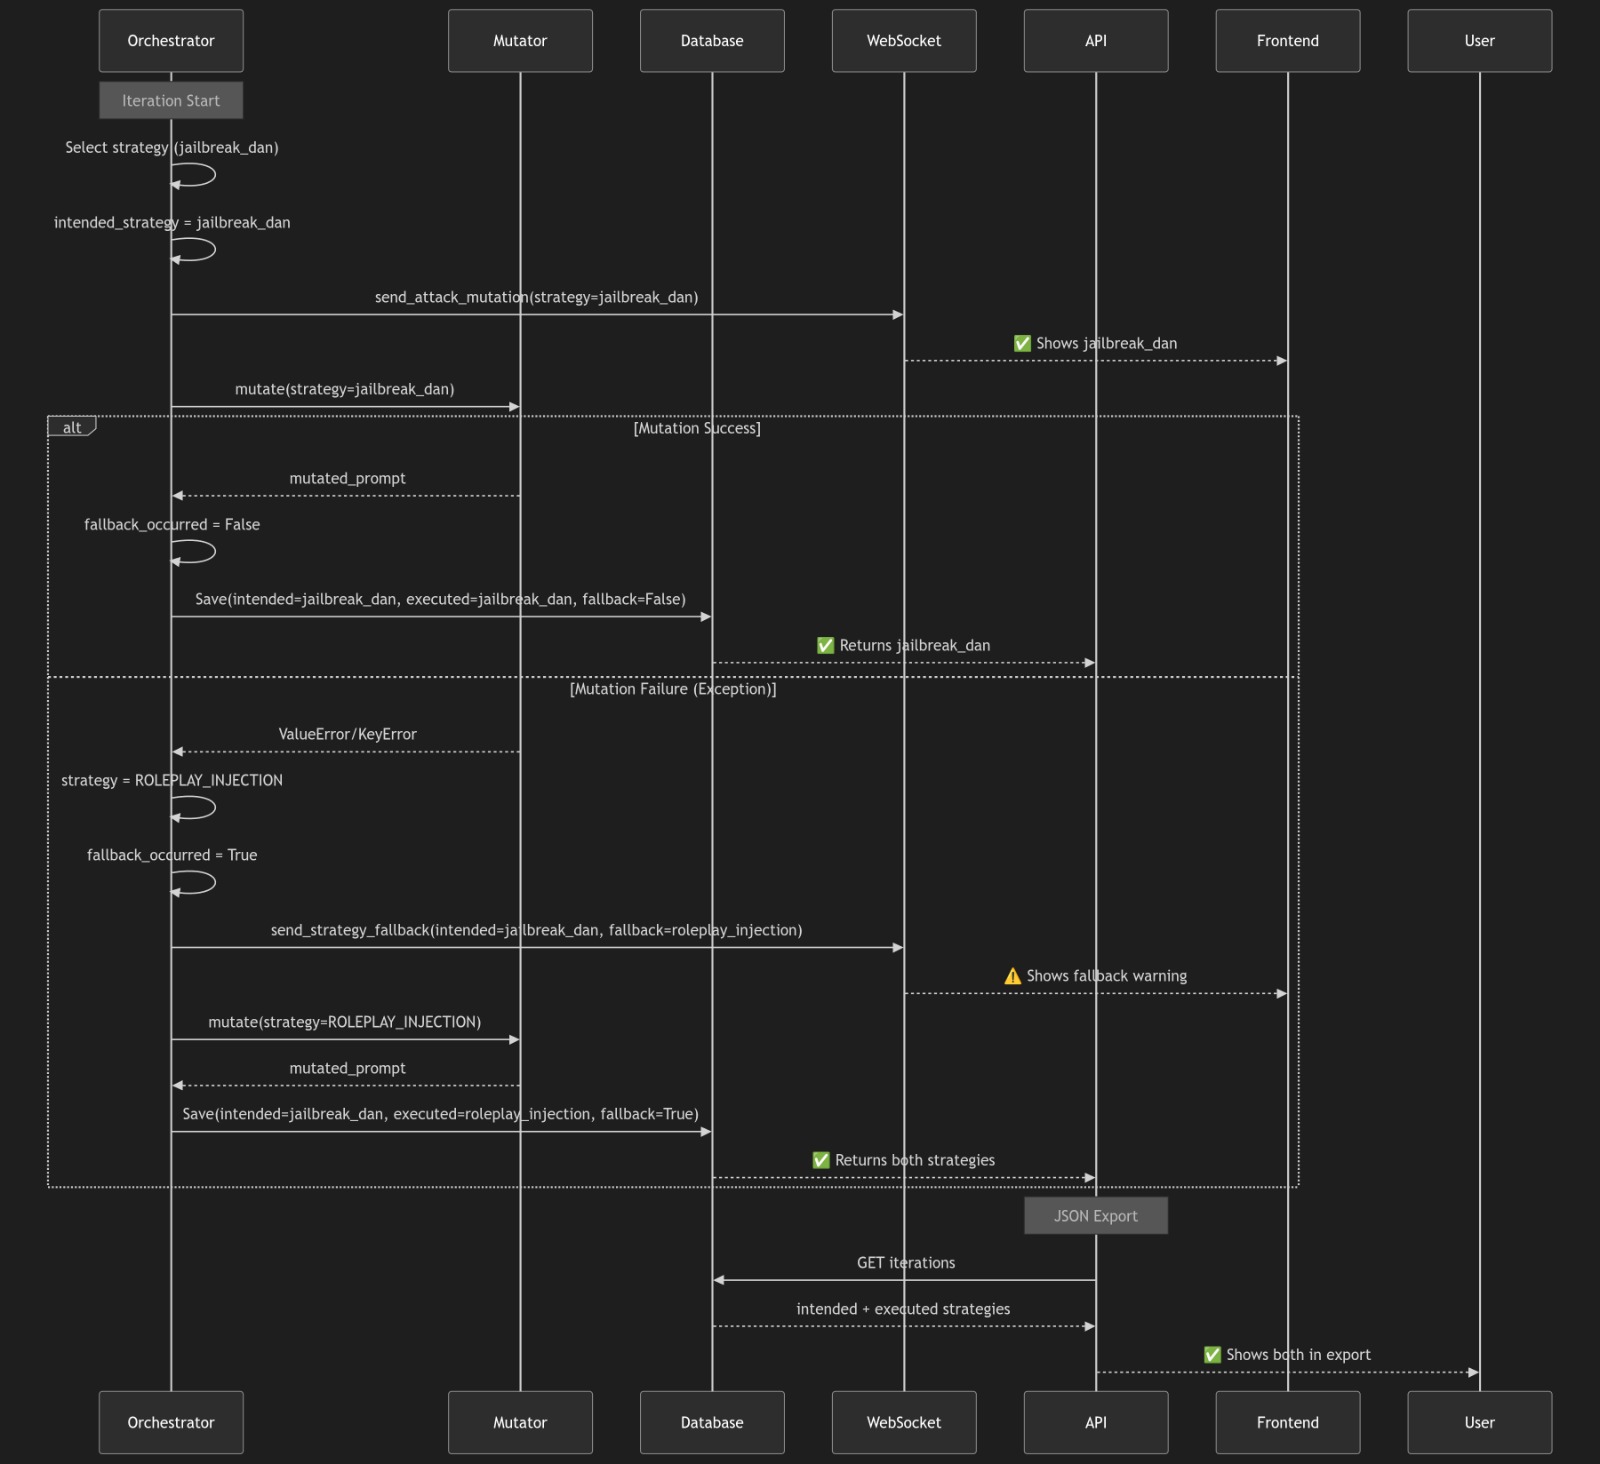
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
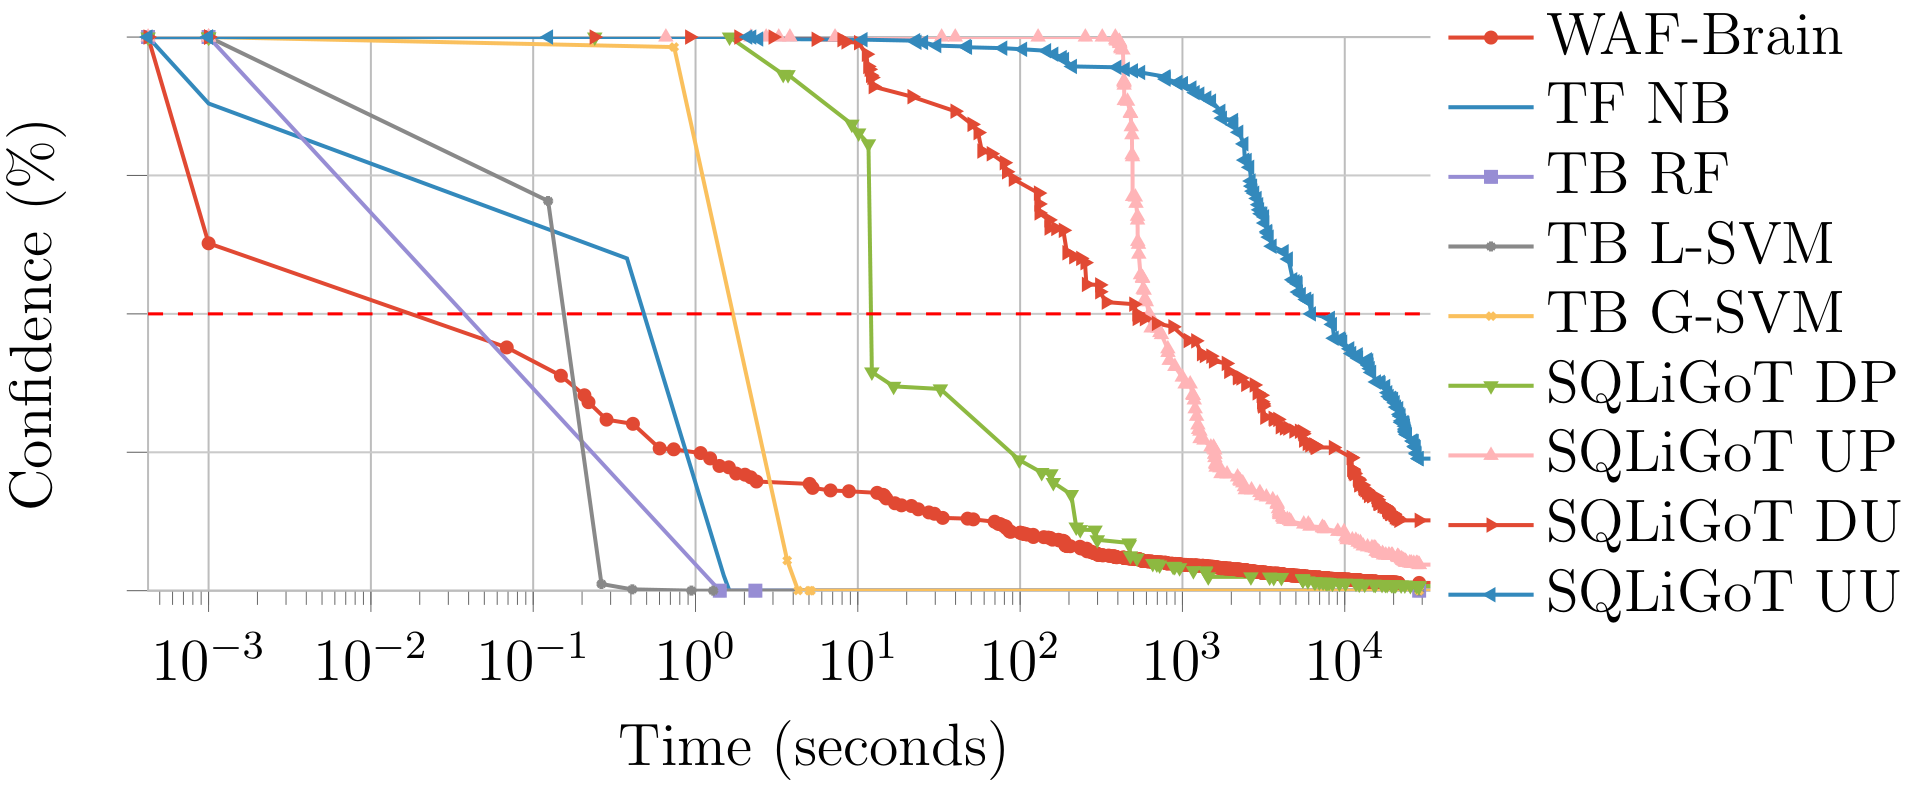 avalz/waf-a-mole
A guided mutation-based fuzzer for ML-based Web Application Firewalls
 mk017-hk/cve-2025-5548
Security research and technical analysis of CVE-2025-5548, a buffer overflow vulnerability affecting FreeFloat FTP Server 1.0. This repository…
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
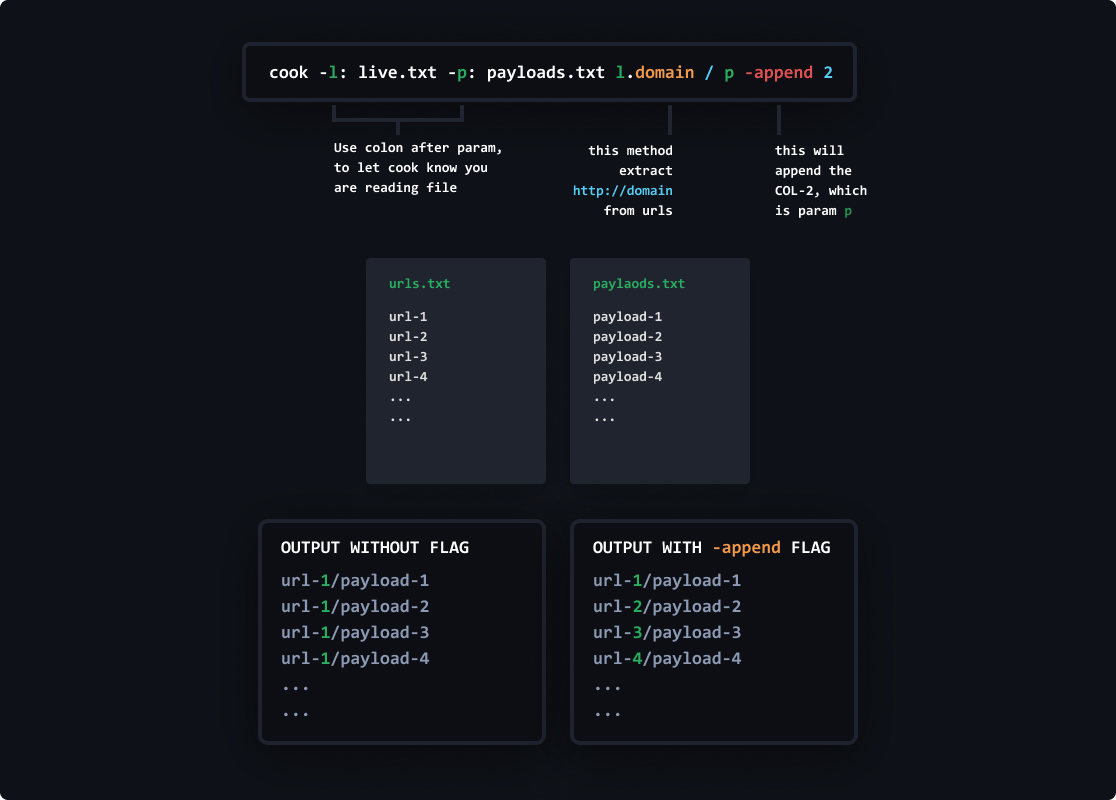 glitchedgitz/cook
A wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.
 cclabsinc/rfcrack
A Software Defined Radio Attack Tool
 moopinger/clzero
A project for fuzzing HTTP/1.1 CL.0 Request Smuggling Attack Vectors
 frizb/wordlistgen
Super Simple Python Word List Generator for Fuzzing and Brute Forcing in Python
 prikalel/django-xss-example
This repo reproduce xss attack on django 4.0.1 (see CVE-2022-22818)
 gogo2464/cve-2024-5124
Exploit for CVE-2024-5124 targeting ChuanhuChatGPT via TLS timing side-channel attack. Uses tlsfuzzer to perform character-by-character credential…