
exploits
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
binary-exploitationcurated-resourcesembedded-systems-security+7
470
hackerhouse-opensource/exploitsexploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 ya551n3/bug-bounty-wordlists
Curated collection of wordlists for bug bounty hunting, covering directories, subdomains, parameters, usernames, passwords, and web fuzzing payloads.
 phra/rustbuster
A Comprehensive Web Fuzzer and Content Discovery Tool
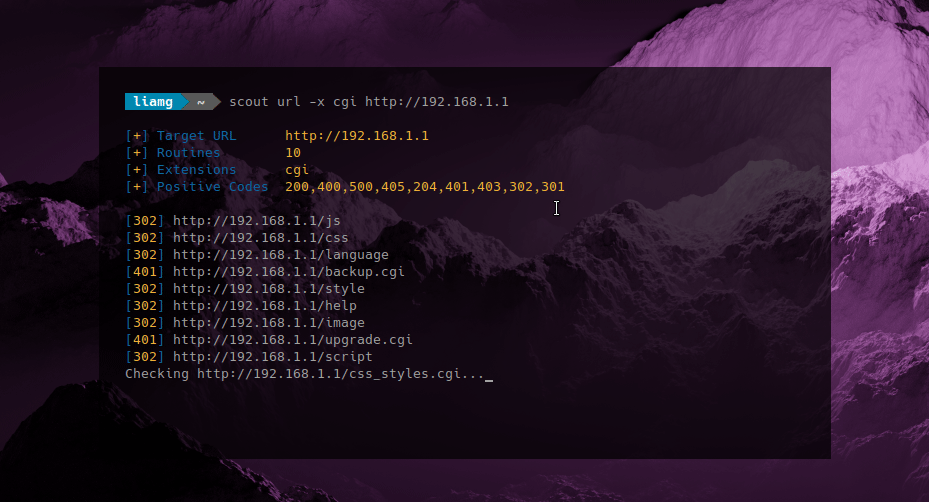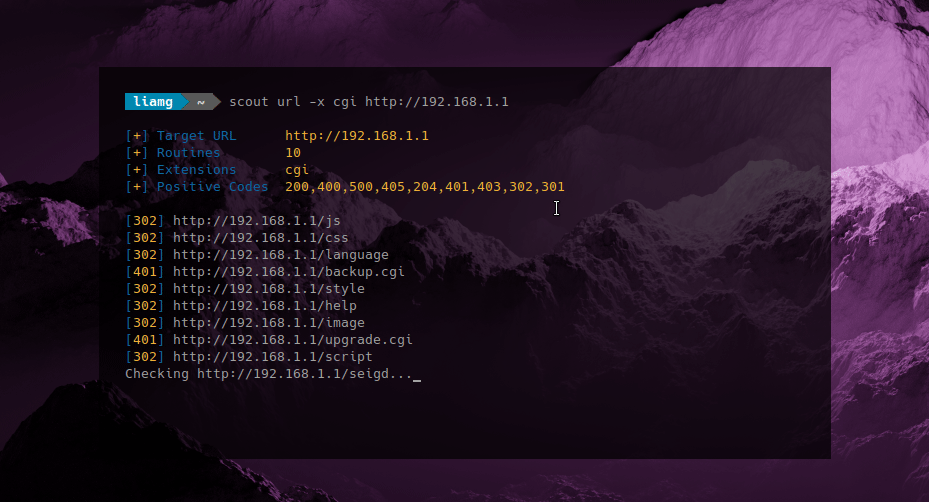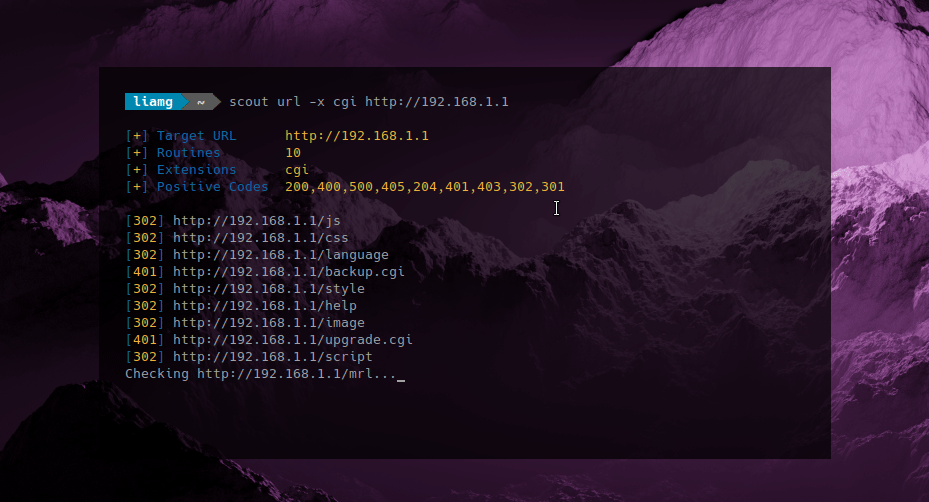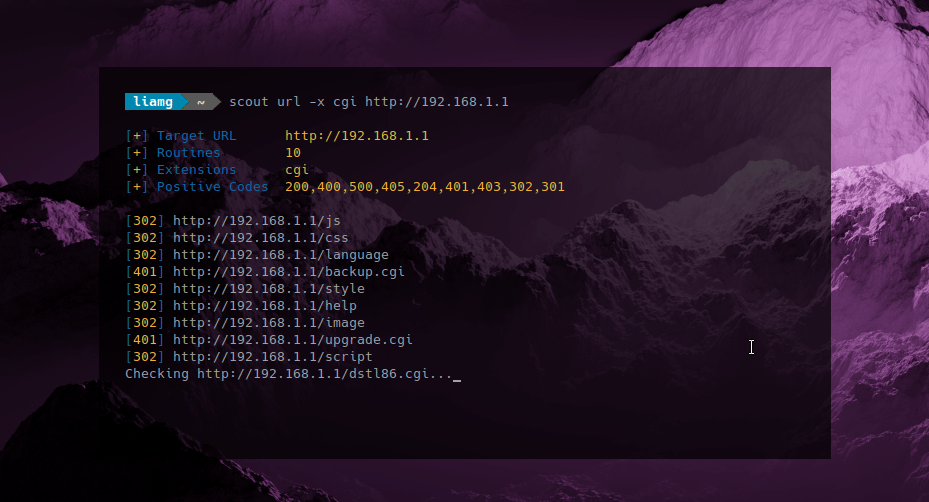 liamg/scout
🔭 Lightweight URL fuzzer and spider: Discover a web server's undisclosed files, directories and VHOSTs
 palindromelabs/awesome-websocket-security
Awesome information for WebSockets security research
 shenli/distributed-system-testing
AI-agent skills for distributed-systems testing
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 rootup/personalstuff
Research artifact repository containing fuzzing corpora (liblnk, tcpdump, vim), a Telegram privacy vulnerability report, and supporting scripts for…
 alphaseclab/all-my-collection-repos
All Security Resource Collections Repos That I Published.
 pwnwriter/kanha
🦚 A web-app pentesting suite written in rust .
 jonwiggins/xmloxide
A pure Rust reimplementation of libxml2
 emrekybs/draculaos
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.
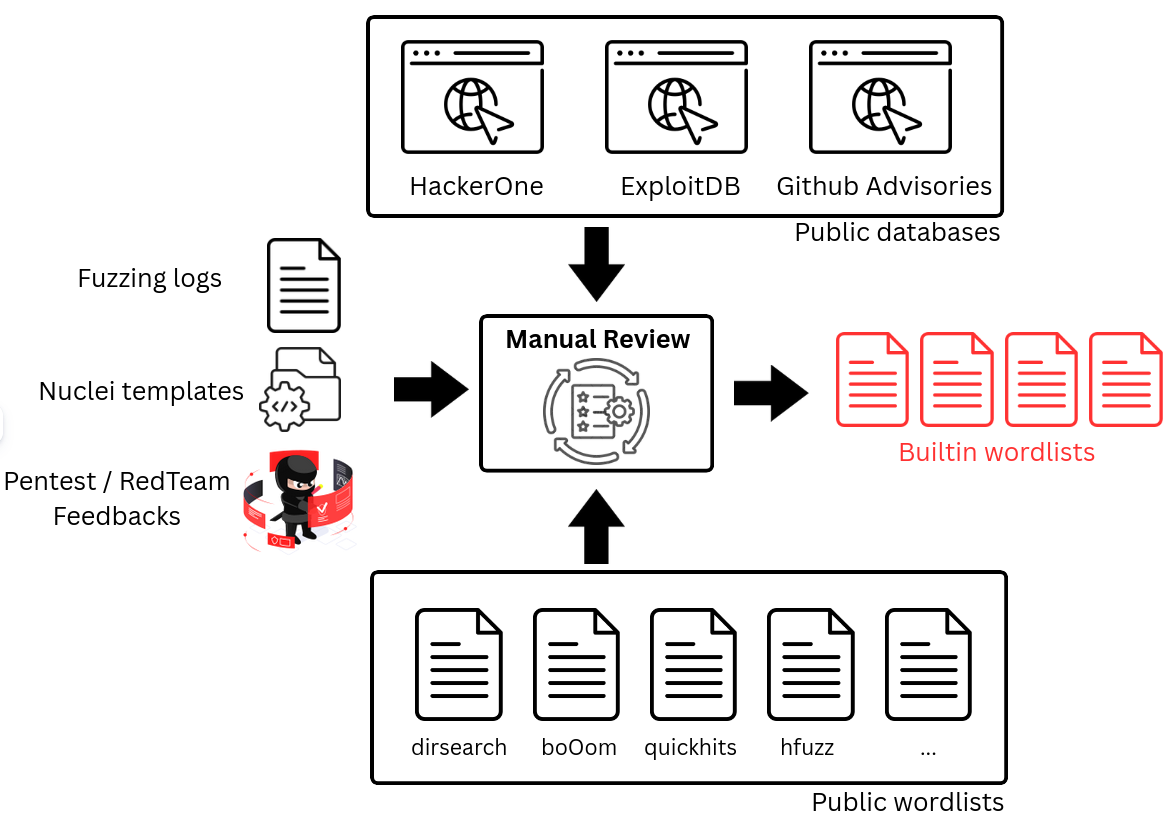 synacktiv/dicozorus
A tool to generate and maintain wordlists for Web fuzzing.
 rxerium/bug-bounty-tools
A BASH Script to automate the installation of the most popular bug bounty tools
 projectdiscovery/defcon32
Defcon 32 Workshop setup and info
 kihara-1/postgresql-cve-2026-14662
PostgreSQL の全文検索(tsvector/tsquery)に見つかった範囲外書き込み脆弱性 CVE-2026-14662 を、修正前(18.4)と修正後(18.6)を Docker で並べて動かして検証した記録と発表資料
 bozellqp/zk-xml-probe
Static XML fixtures for authorized bug bounty testing of XML parser behaviour (CVE-2026-45071).