
FuzzingBrain-Bench
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
ai-securitydynamic-analysis-sandboxingeducation+3
7
fuzzingbrain/fuzzingbrain-benchA benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
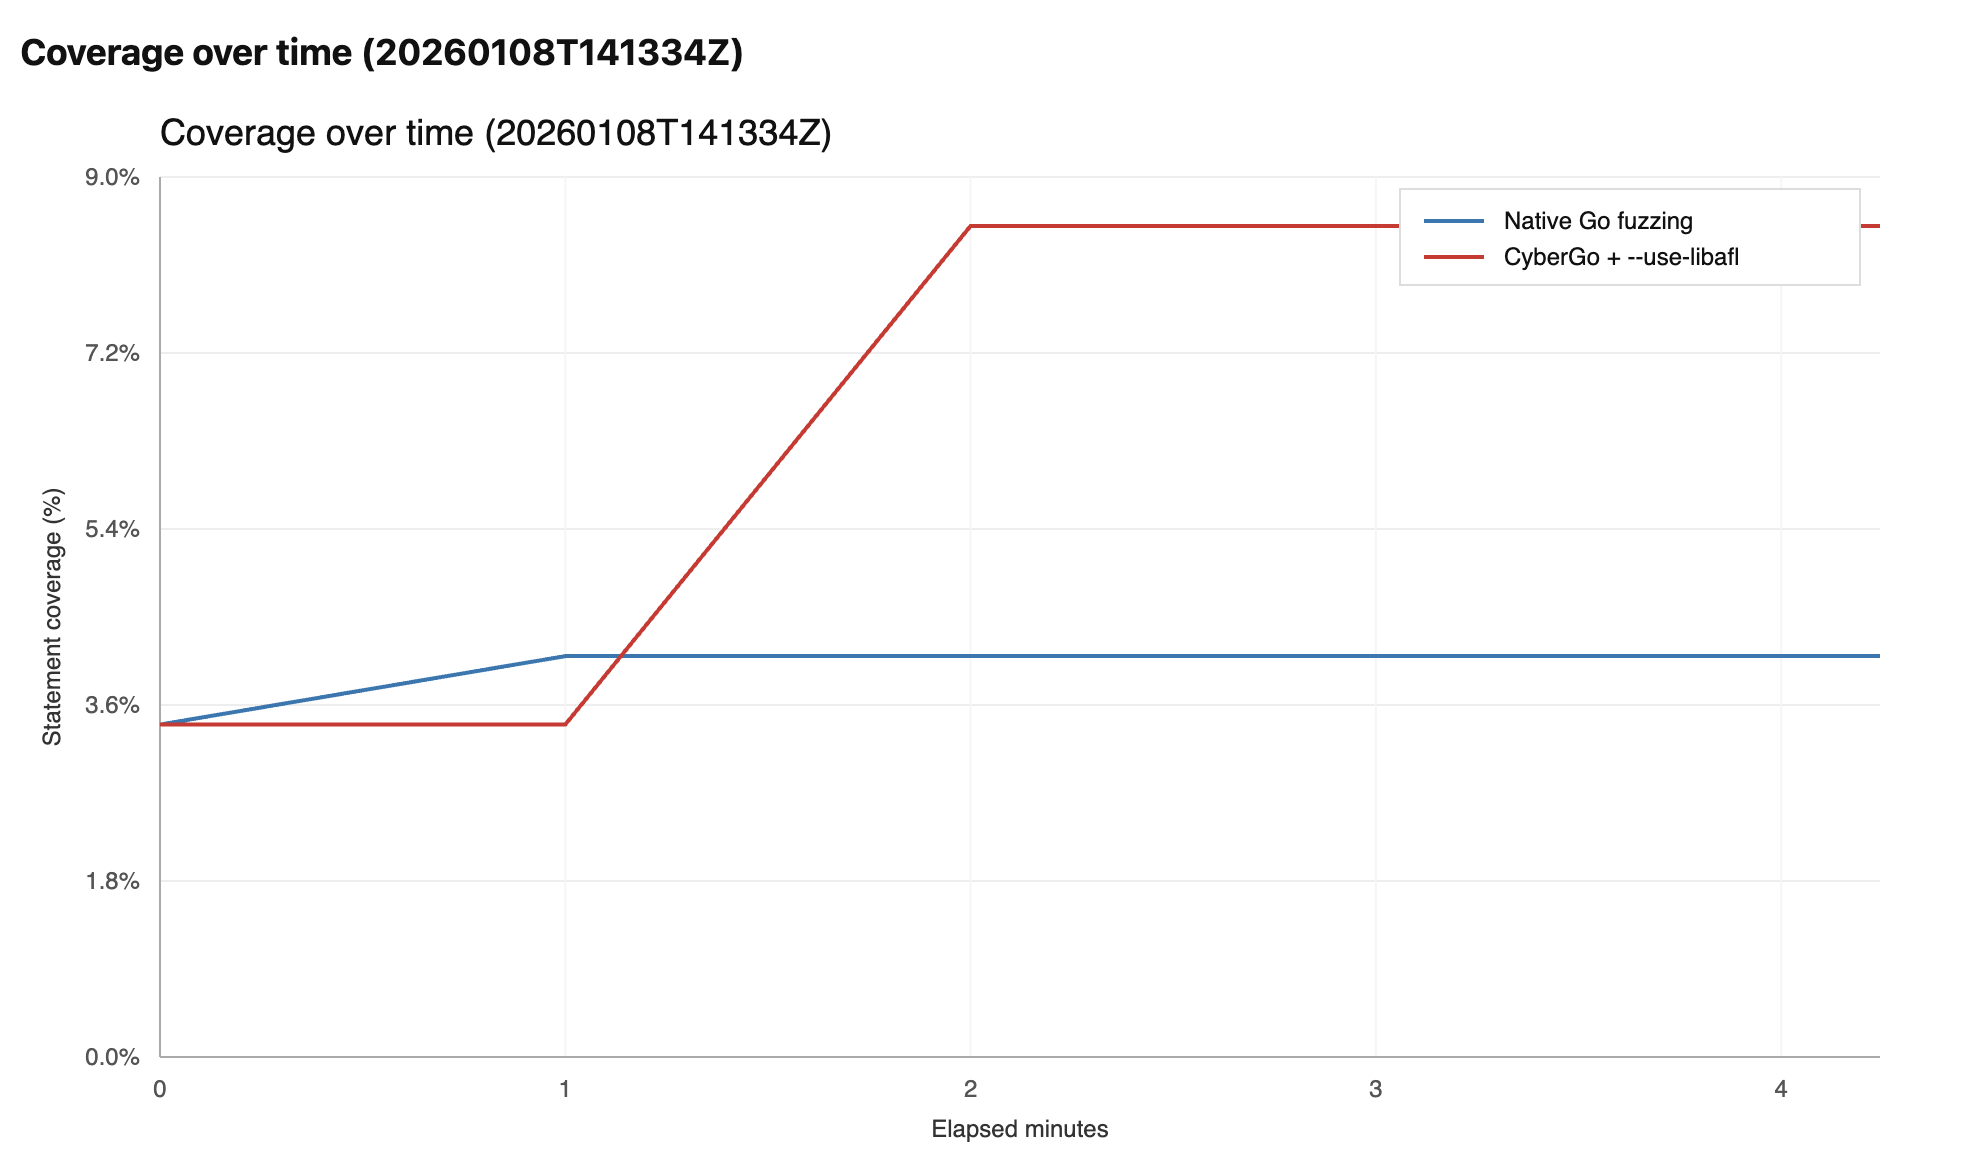 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 fraunhofer-aisec/gallia
Extendable pentesting framework for automotive UDS interfaces, enabling reproducible scans, diagnostic trouble code reading, and post-processing via…
 libssh/libssh-mirror
C library implementing the SSH protocol for secure remote access, authentication, and encrypted communication. Includes fuzzing support via OSS-Fuzz…
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 flock4h/freeway
WiFi Penetration Testing & Auditing Tool
 bikini/exploitarium
Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 abhinavagarwal07/gdcm-security-poc
Private end-to-end sanitizer reproduction package for six GDCM findings
 reversenseorg/dexcalibur
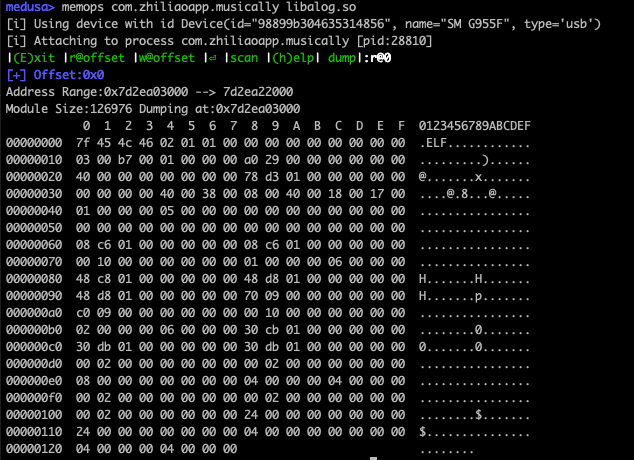
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis