
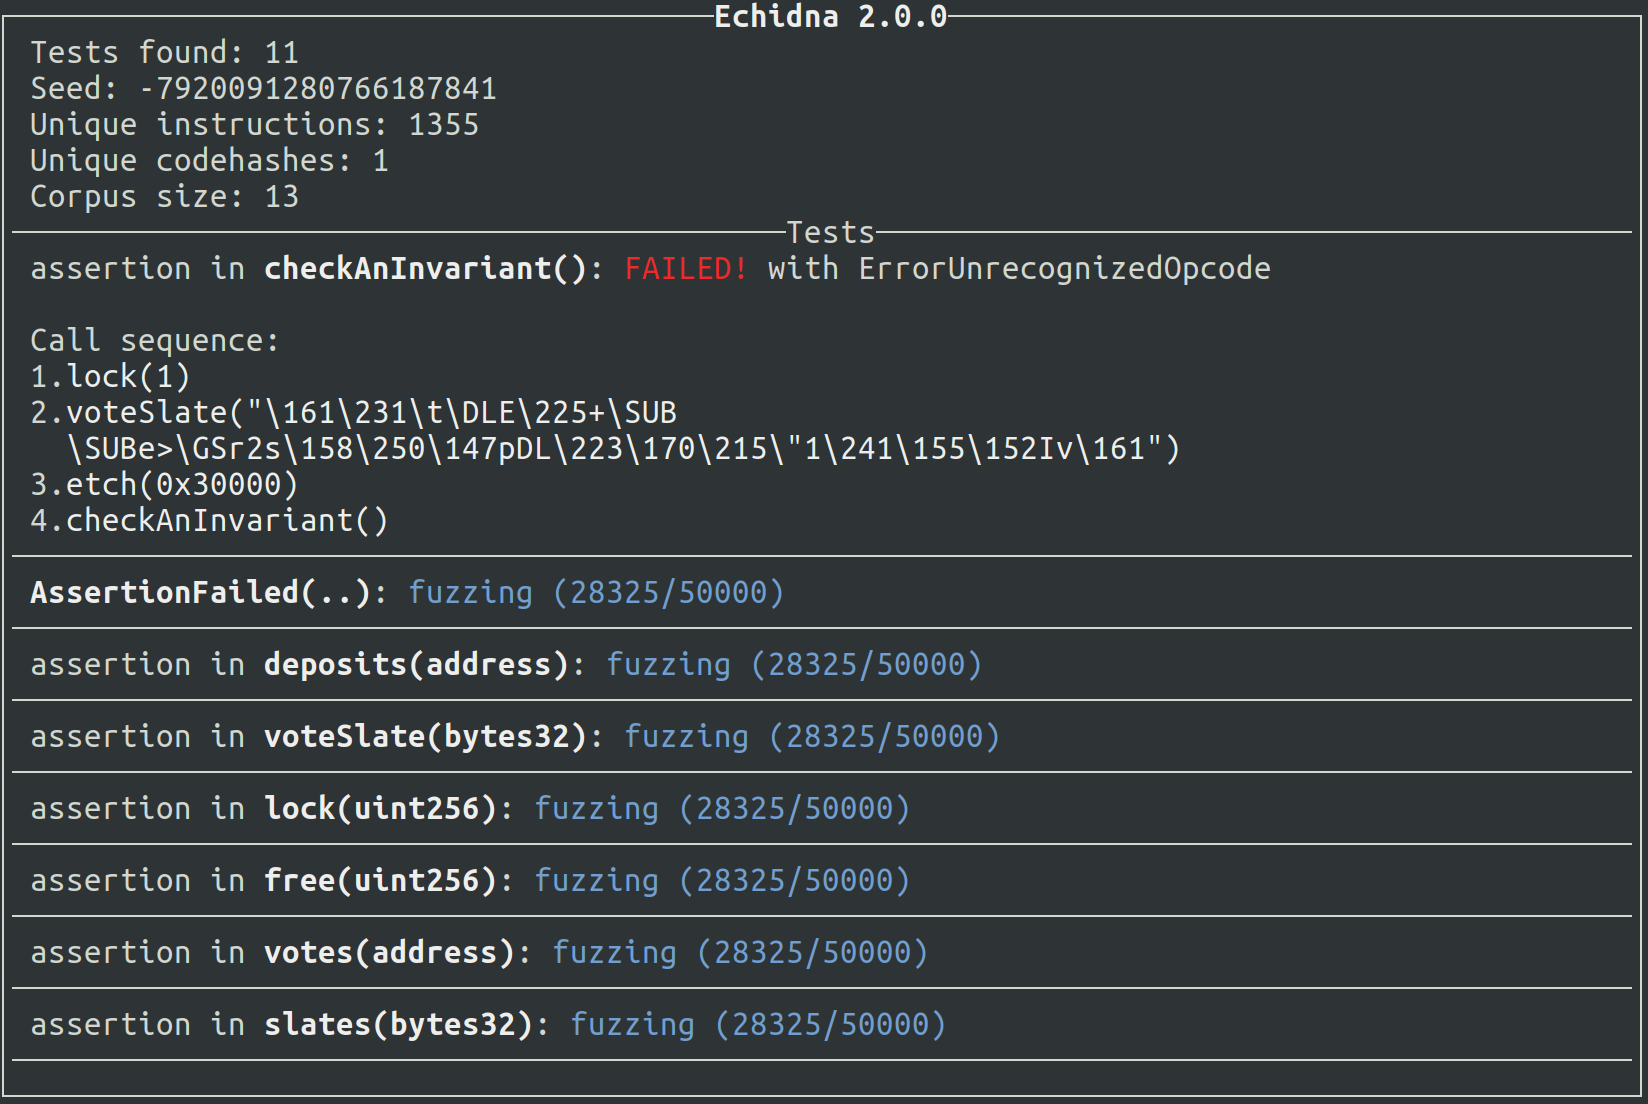

 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
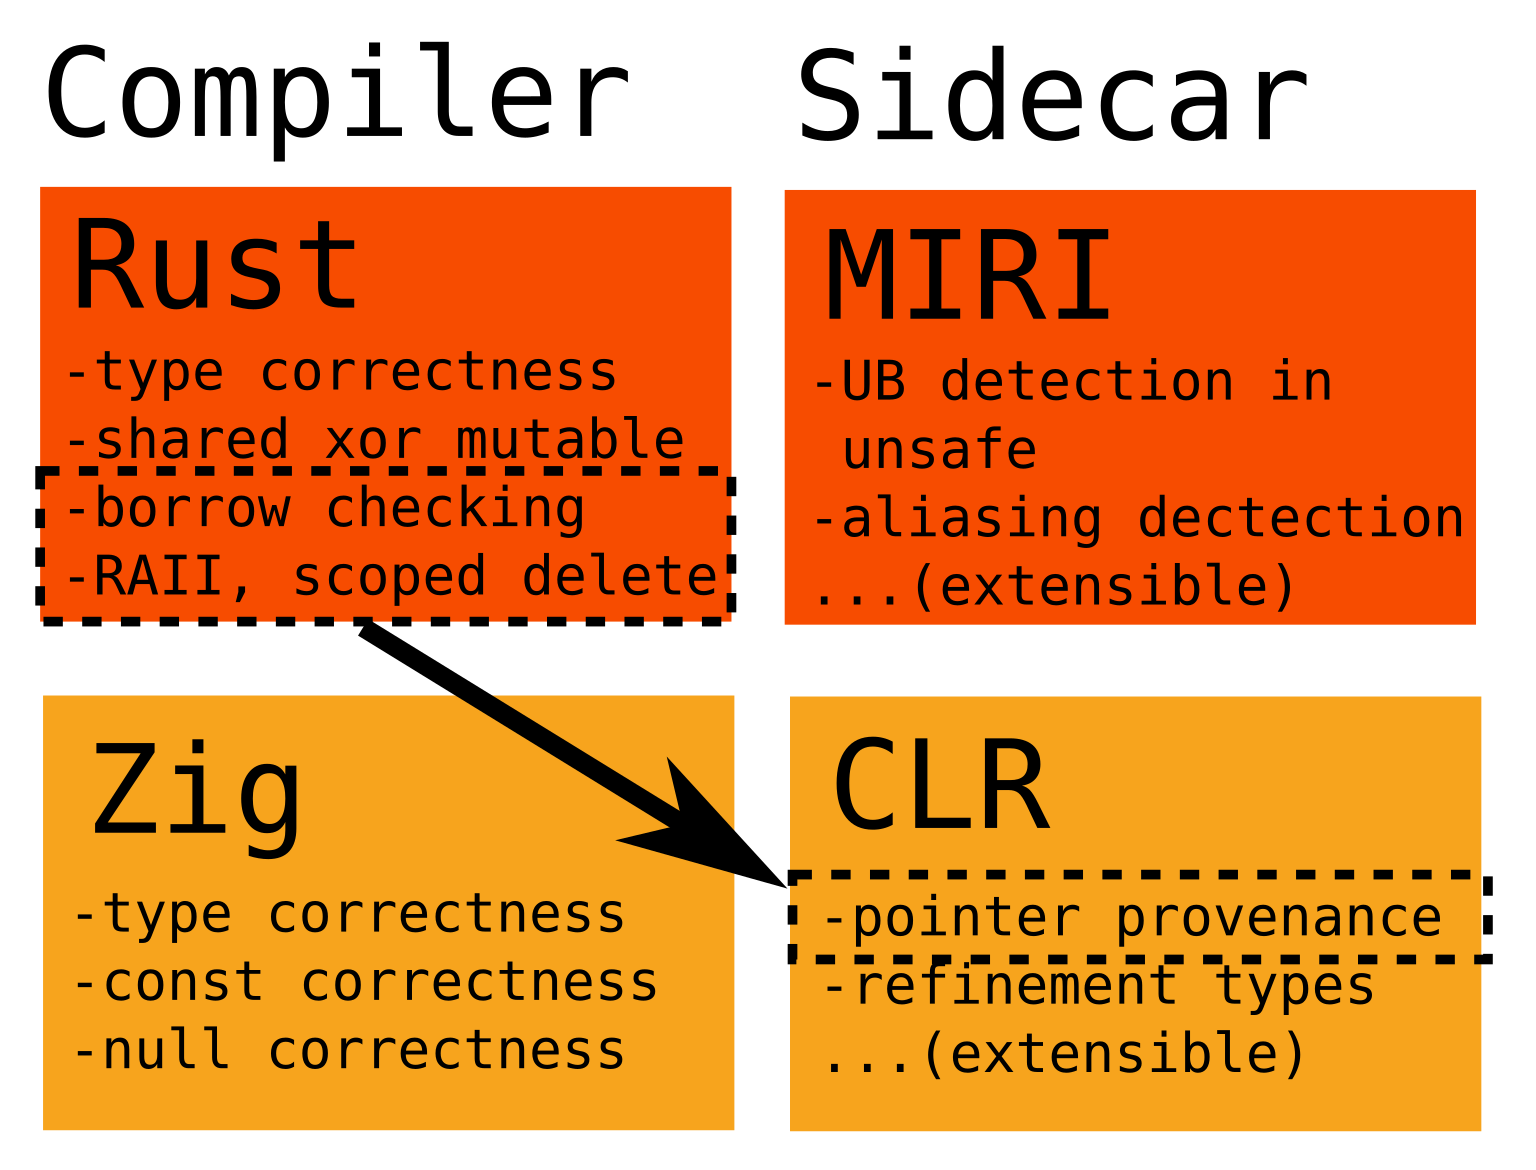 ityonemo/clr
Checker for Lifetimes and other Refinement types
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 kiyochii/cve-2026-29628
Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…
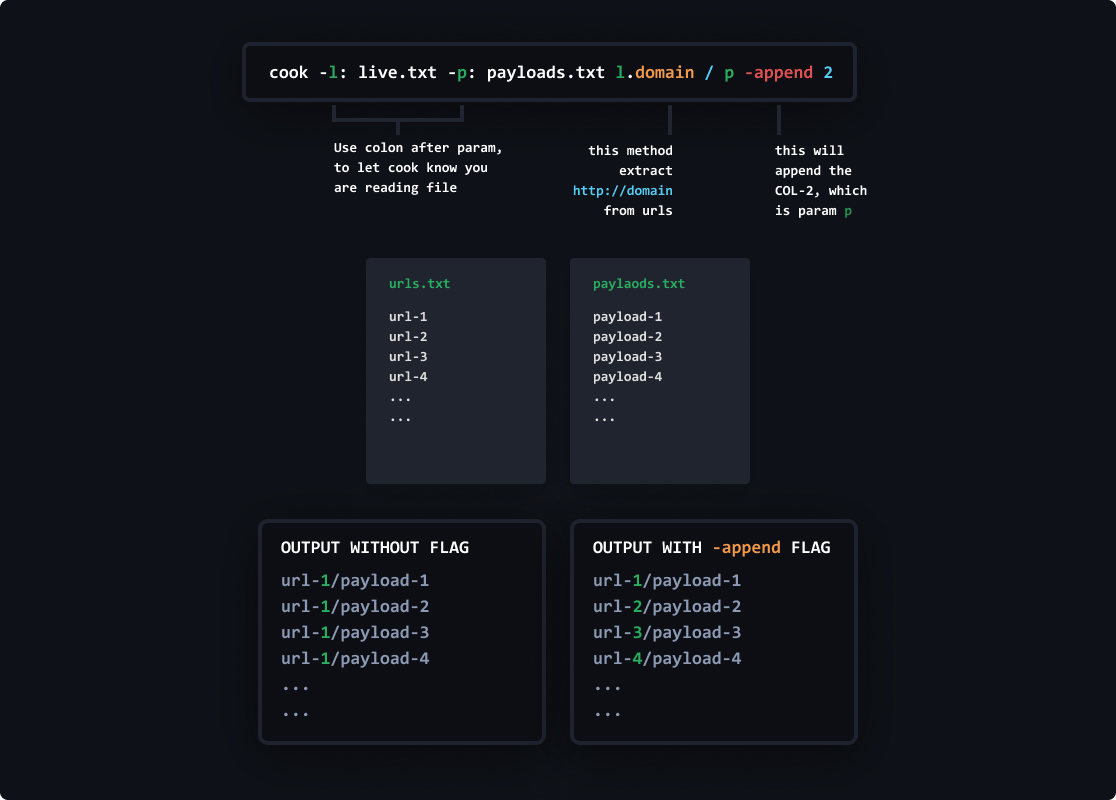 glitchedgitz/cook
A wordlist framework to fullfill your kinks with your wordlists. For security researchers, bug bounty and hackers.
 nikic/php-fuzzer
Edge-coverage-guided fuzzer for PHP libraries that detects bugs via crashes, timeouts, and warnings. Supports corpus management, crash minimization,…
 thephykon/cve-2025-53367-poc
A simple POC of the CVE-2025-53367, creating a .djvu-file which triggers an OOB-write in the heap
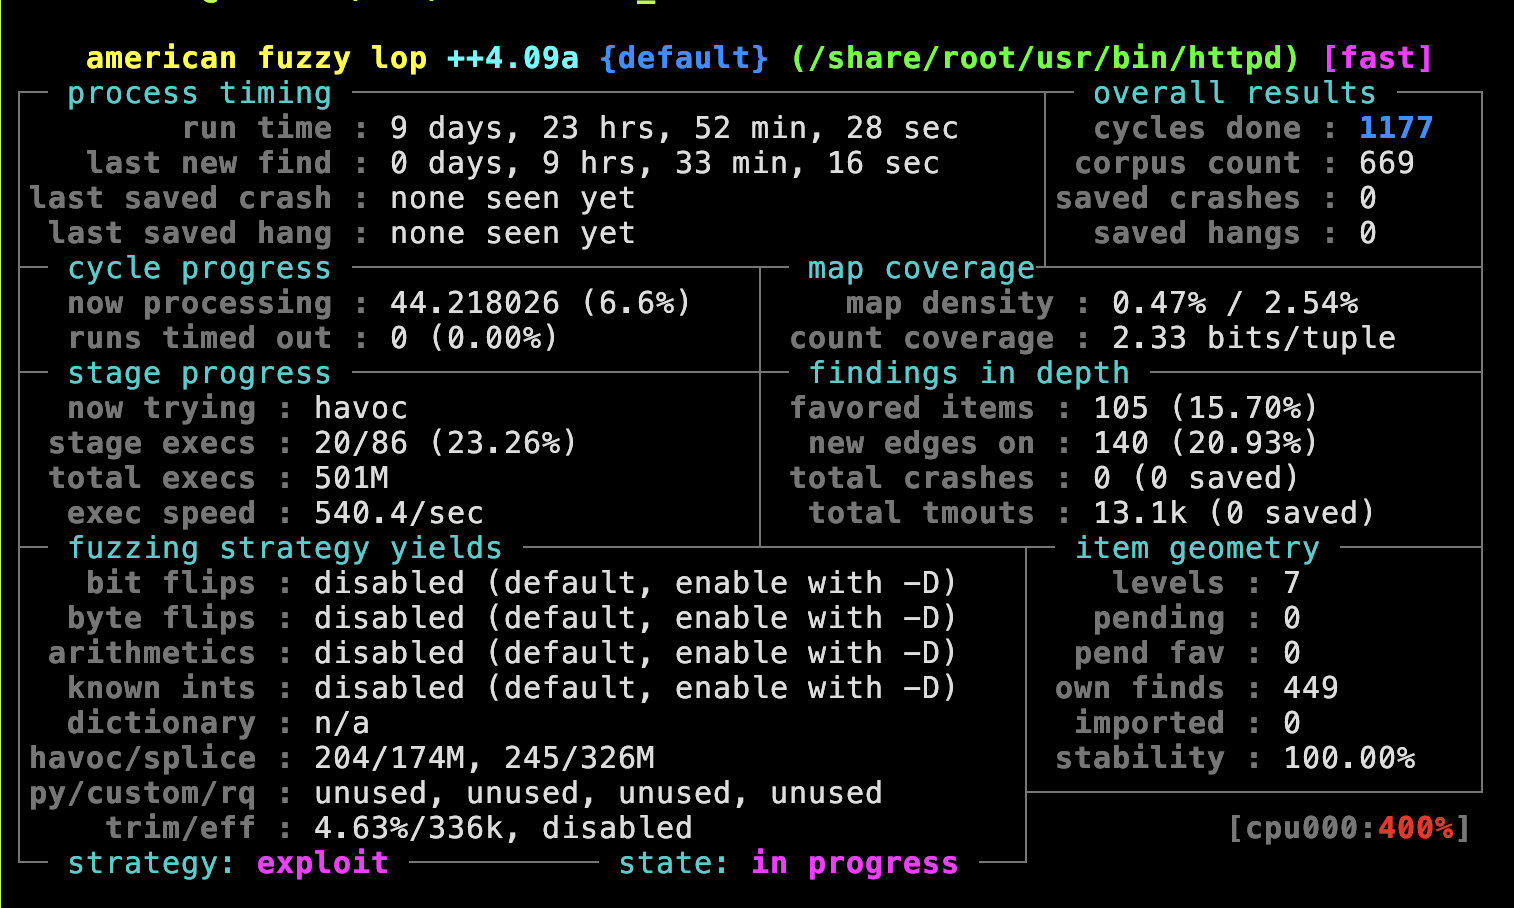 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
 shinigami-777/poc_cve-2025-11579
Proof-of-concept exploit for CVE-2025-11579, a denial-of-service vulnerability in rardecode that triggers an out-of-memory crash via a crafted RAR…
 bahruzjabiyev/t-reqs
Grammar-based HTTP/1 fuzzer with mutation ability
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 dsecuredcom/ffufpostprocessing
Golang tool which helps dropping the irrelevant entries from your ffuf result file.
 minimaxir/big-list-of-naughty-strings
Curated list of malicious and edge-case input strings (blns.txt/blns.json) for QA and security testing of user-input validation, injection, and…
 nccgroup/triforcelinuxsyscallfuzzer
A linux system call fuzzer using TriforceAFL