

libloong
 libriscv/libloong
The fastest LoongArch sandbox
binary-analysisembedded-systems-securityfuzzing+3
libriscv/libloongThe fastest LoongArch sandbox
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 harshrajsinghania/cve-2026-86547-mrubyc-op-enter
Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
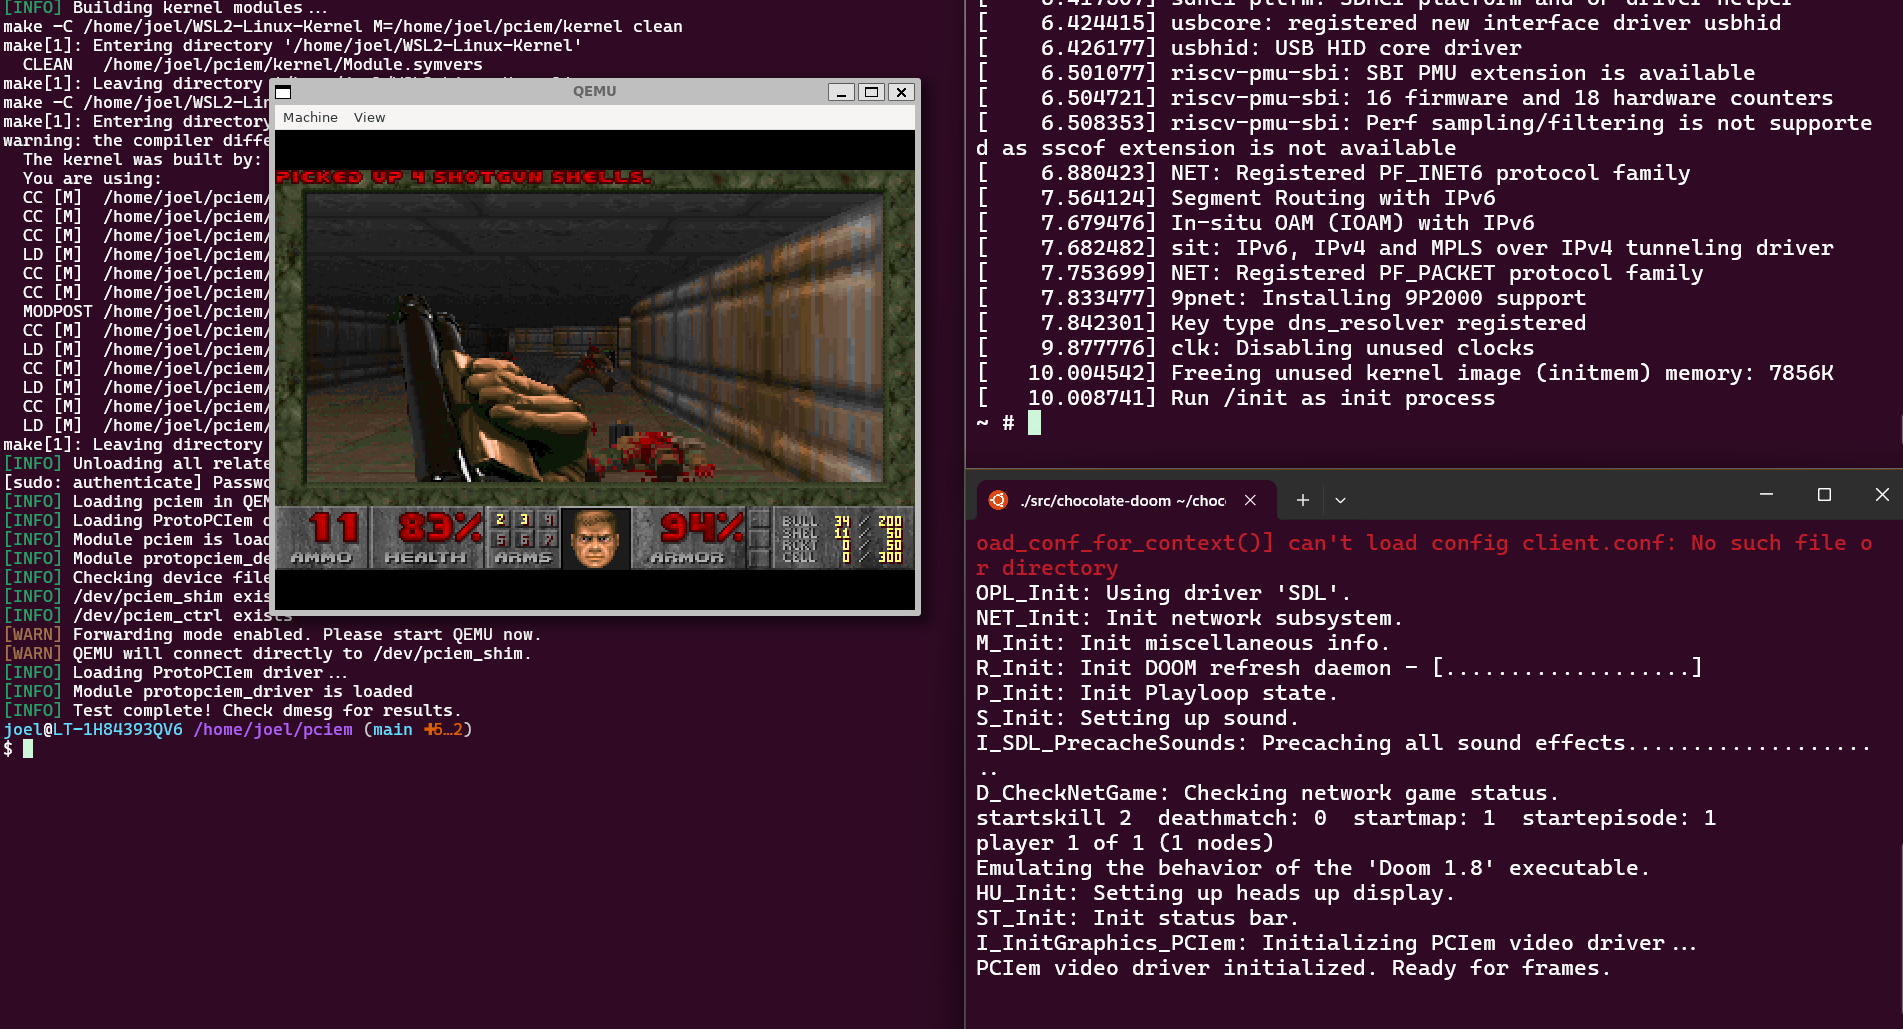 cakehonolulu/pciem
A Linux framework to enable userspace-defined "Virtual" PCIe card shims to enable in-host PCIe card driver development.
 brucedevices/firmware
Predatory ESP32 Firmware
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 0ldev/politician
Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…
 yeahhbean/cve-2026-45729
ThorVG NULL pointer dereference via malformed SVG — AFL++ fuzzing writeup
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
 j4ck3lsyn-gen2/cve-2026-39047
Epson Printer RAW Protocol Exploit Framework
 christbowel/cve-2026-56111
Proof-of-concept exploit for CVE-2026-56111, an out-of-bounds write in the M421 G-code handler of Marlin Firmware, demonstrating constrained memory…
 hunt-benito/lwip-snmpv3-stack-overflow-cve-2026-8836-critical-embedded-rce
CVE-2026-8836 — lwIP SNMPv3 stack-based buffer overflow PoC (CVSS 9.8)
 deepwoodssec/cve-2026-36522
Proof-of-concept exploit for CVE-2026-36522: unauthenticated NaN injection via MAVLink PARAM_SET in ArduPilot ArduPlane, causing DoS or silent…
 vital-information-resource-under-siege/cve-2026-38698-and-cve-2026-38699
Technical details and publication about CVE-2026-38698 and CVE-2026-38699
 jonathansalwan/triton
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification…
 0xbbdd/cve-2026-33317
Proof-of-concept for CVE-2026-33317, an out-of-bounds write in OP-TEE PKCS#11 TA, demonstrating Secure World heap corruption via a malformed…