

angr
 angr/angr
A powerful and user-friendly binary analysis platform!
ai-assisted-reversingbinary-analysisbinary-exploitation+12
9.1k8h 8m ago
angr/angrA powerful and user-friendly binary analysis platform!
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 mr-xn/penetration_testing_poc
渗透测试有关的POC、EXP、脚本、提权、小工具等---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss csrf-webshell cobub-razor…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 bishopfox/joro
A collaborative web exploitation framework.
 xairy/linux-kernel-exploitation
A collection of links related to Linux kernel security and exploitation
 hahwul/webhackersweapons
⚔️ Web Hacker's Weapons / A collection of cool tools used by Web hackers. Happy hacking , Happy bug-hunting
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
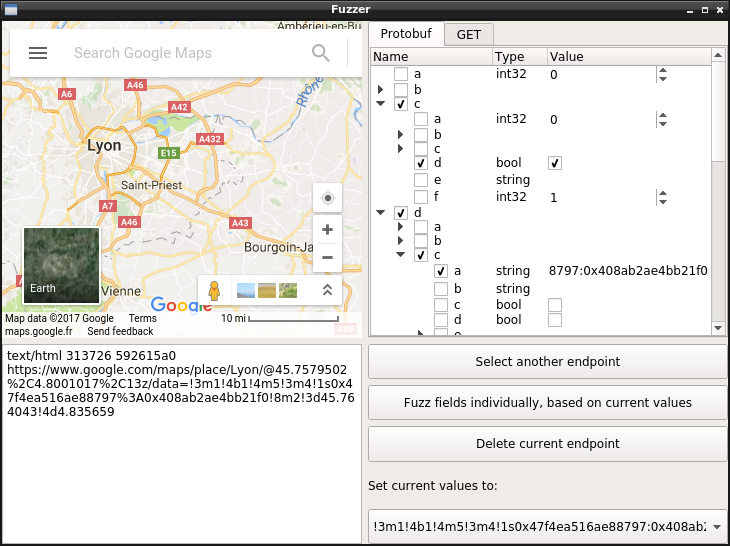 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 4minx/cve-2026-14266
CVE-2026-14266 - XZ Heap Buffer Overflow PoC Generator for 7-Zip
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 jvbotelho/cve-2026-69243-poc-aiohttp-smuggling
Reproduces aiohttp CWE-444 request smuggling via rejected WebSocket upgrades, with Python/Rust payloads and Docker lab demonstrating proxy…