
LFITester
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
crawlerexploitationfuzzing+7
112
kostas-pa/lfitesterPython3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
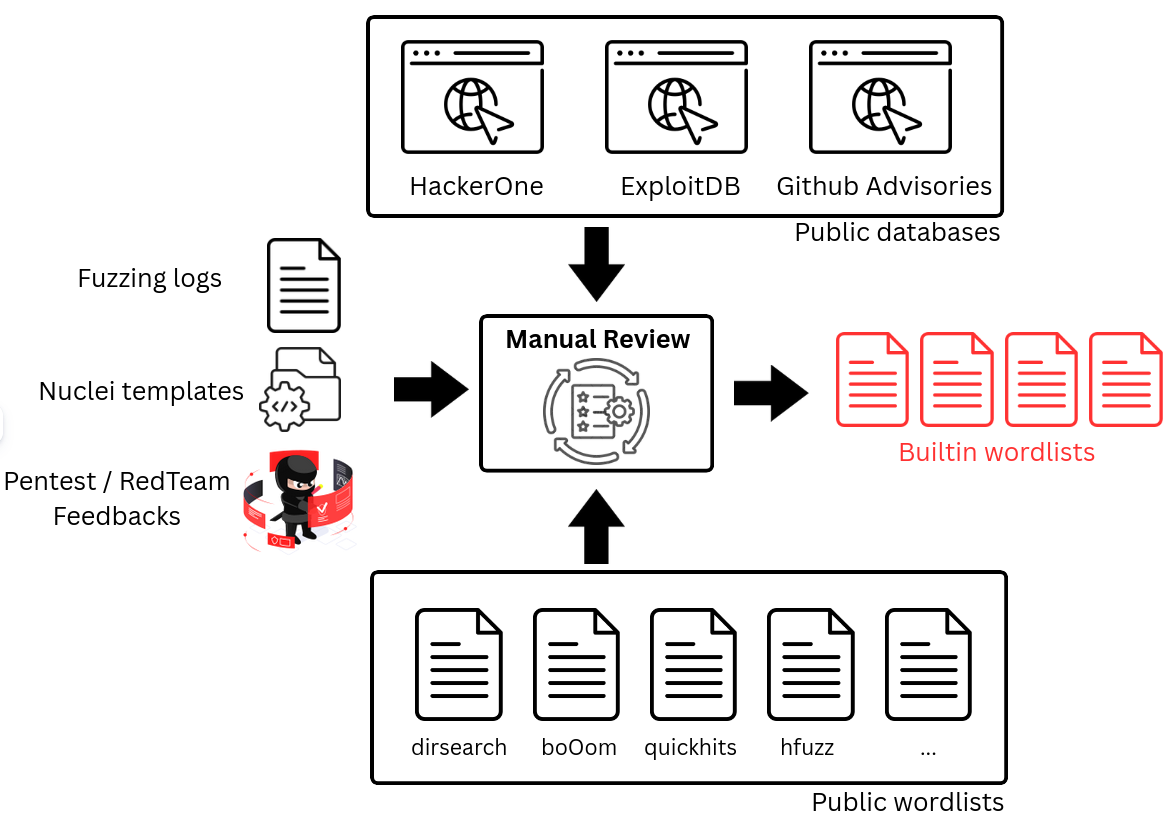 synacktiv/dicozorus
A tool to generate and maintain wordlists for Web fuzzing.
 alone/mutator
Generate mutations over a wordlist
 fantaghost/fgscanner
FGscanner is an advanced, opensource URL scanner.
 nccgroup/cecster
A GUI-based tool to perform security testing against the HDMI CEC (Consumer Electronics Control) and HEC (HDMI Ethernet Channel) protocols
 perplext/echteeteepee
Go tool and Nuclei template for testing James Kettle's (CVE-2025-32094) HTTP/1.1 must die: the desync endgame
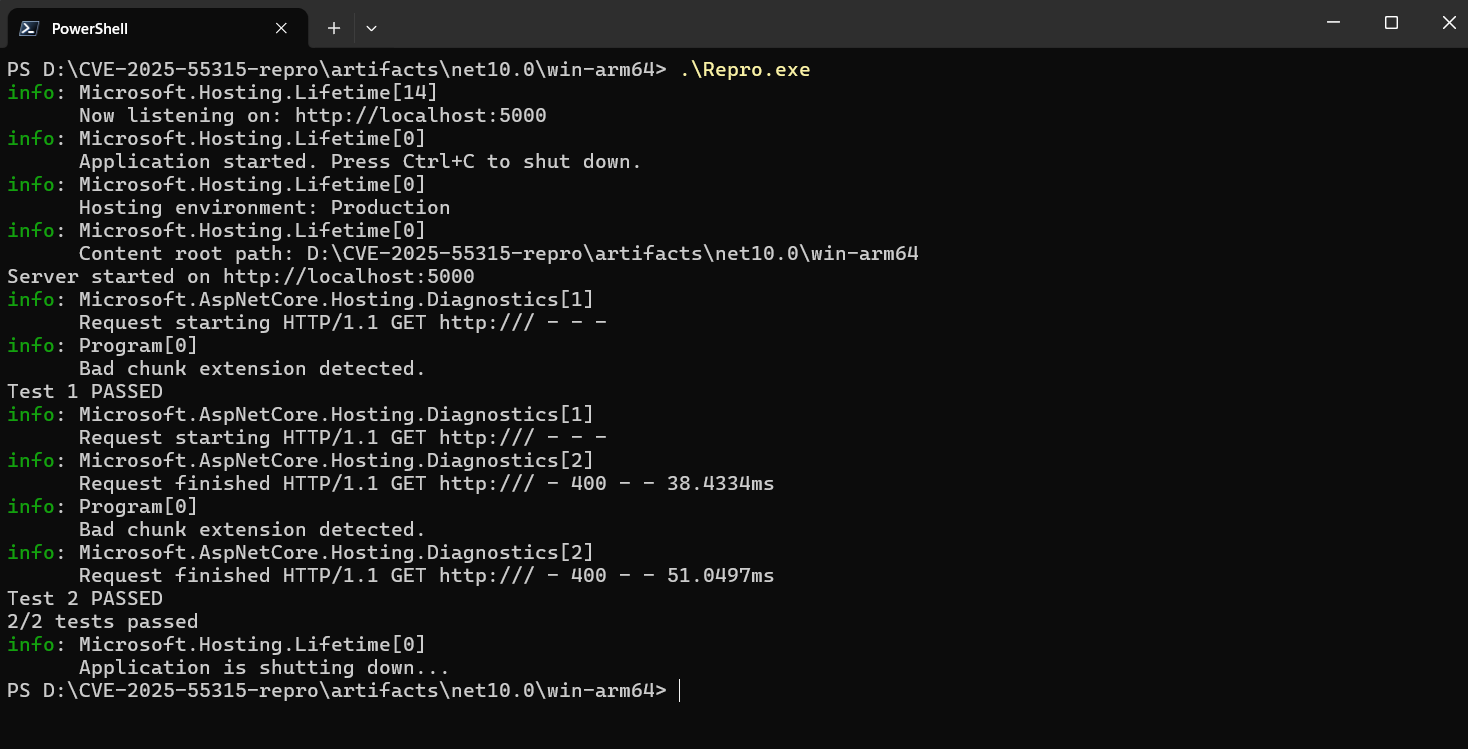 sirredbeard/cve-2025-55315-repro
Tool that reproduces CVE-2025-55315 in ASP.NET Core.
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface